

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 likaifeng0/cve-2018-9995_dvr_credentials-dev_tool
Exploit tool for CVE-2018-9995 that extracts credentials from exposed DVR devices via HTTP request with cookie bypass, targeting multiple vendor…
 omidsec/cve-2018-6389
PoC Exploit CVE-2018-6389
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 m3ssap0/wordpress_cve-2018-6389
Tries to exploit a WordPress vulnerability (CVE-2018-6389) which can be used to cause a Denial of Service.
 pradeepjairamani/wolfcms-xss-poc
WolfCMS-v0.8.3.1 Cross Site Scripting(XSS) Assigned CVE Number: CVE-2018-6890
 pradeepjairamani/typo3-xss-poc
Typo3 -v9.1.0 Persistent Cross Site Scripting(XSS) Assigned CVE Number: CVE-2018-6905
 rafaelcintralopes/swaggerui-cve-2018-25031
Exploit Swagger UI - User Interface (UI) Misrepresentation of Critical Information (CVE-2018-25031)
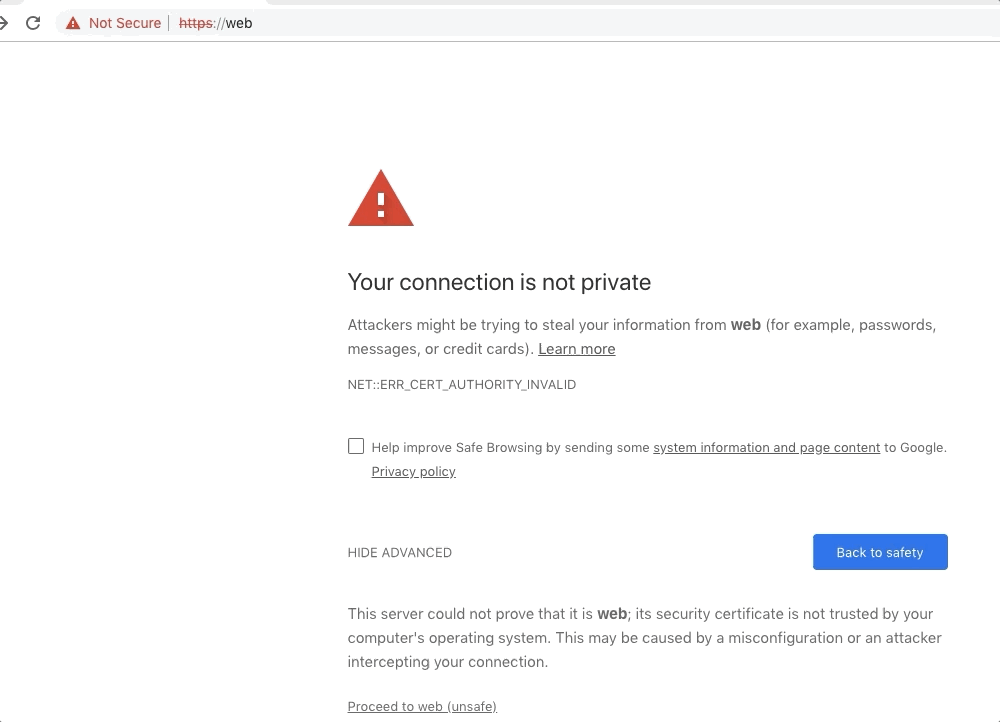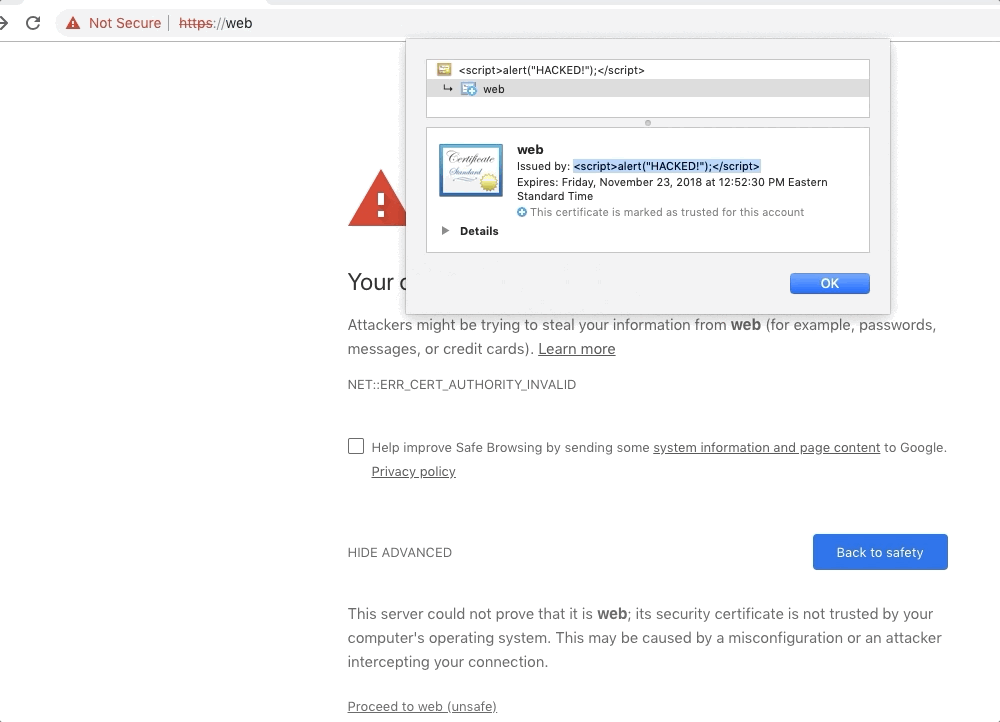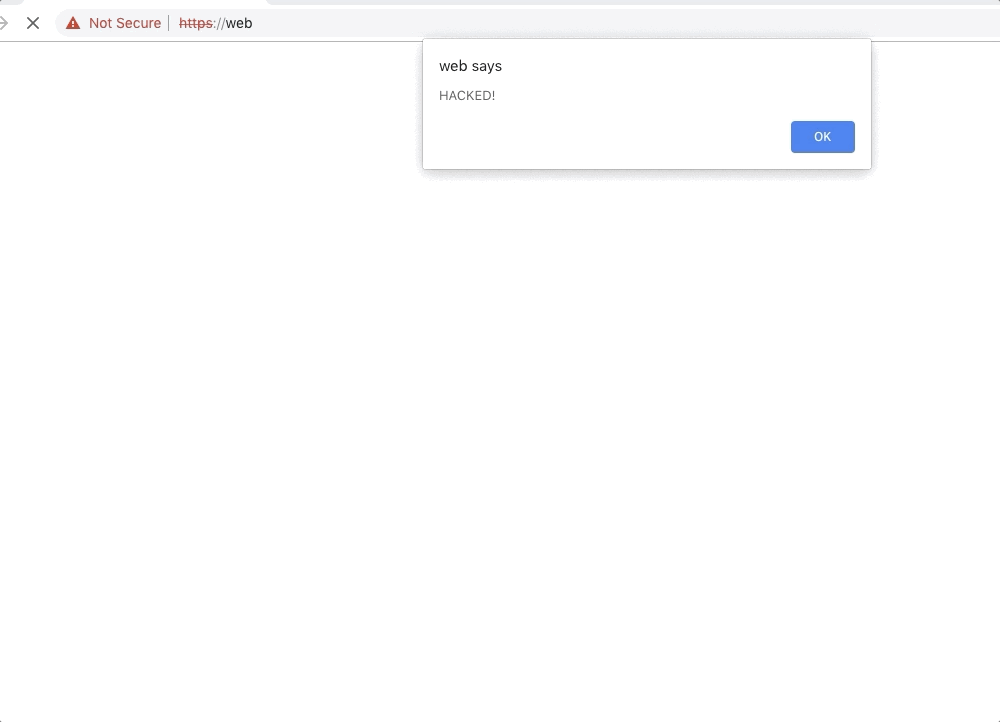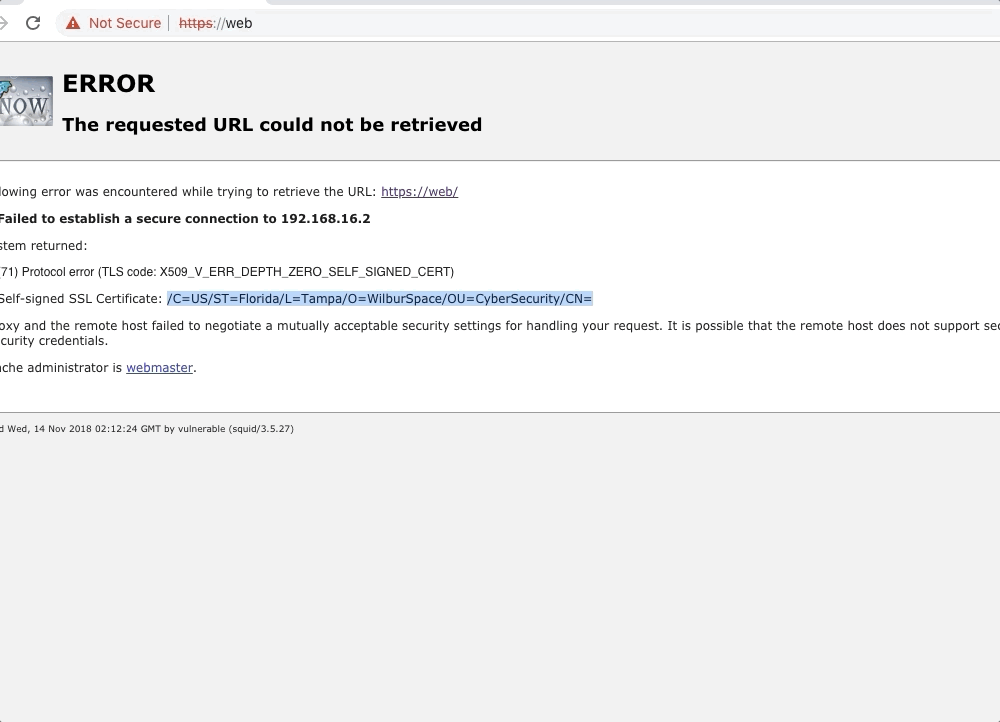 jonathanwilbur/cve-2018-19131
Proof-of-Concept exploit of CVE-2018-19131: Squid Proxy XSS via X.509 Certificate
 realbatuhan/jwt-bruteforcer
Jwt Bruteforcer with CVE-2018-1000531 Test
 wmasday/htc
Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995
 moon1705/easy_security
Project with sublist3r, massan, CVE-2018-15473, ssh bruteforce, ftp bruteforce and nikto.
 ynsmroztas/drupalhunter
CVE-2018-7600 0-Day Exploit (cyber-warrior.org)
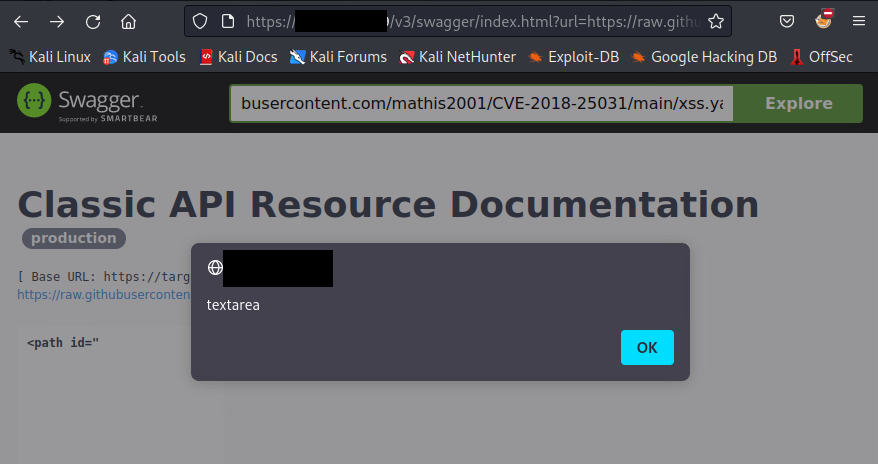 mathis2001/cve-2018-25031
CVE-2018-25031 tests
 egebalci/cve-2018-8065
Flexense HTTP Server <= 10.6.24 - Denial Of Service Exploit
 juliengadanho/cve-2018-6389-php-patcher
Patch Wordpress DOS breach (CVE-2018-6389) in PHP
 martinfrancois/cve-2018-1000529
Proof-of-concept for CVE-2018-1000529: stored XSS in Grails Fields plugin <=2.2.7. Demonstrates the vulnerability with a runnable Grails application…