

LBFH
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
educationexploitationhash-analysis+9
725 years ago
naimkowshik/lbfhAbout All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
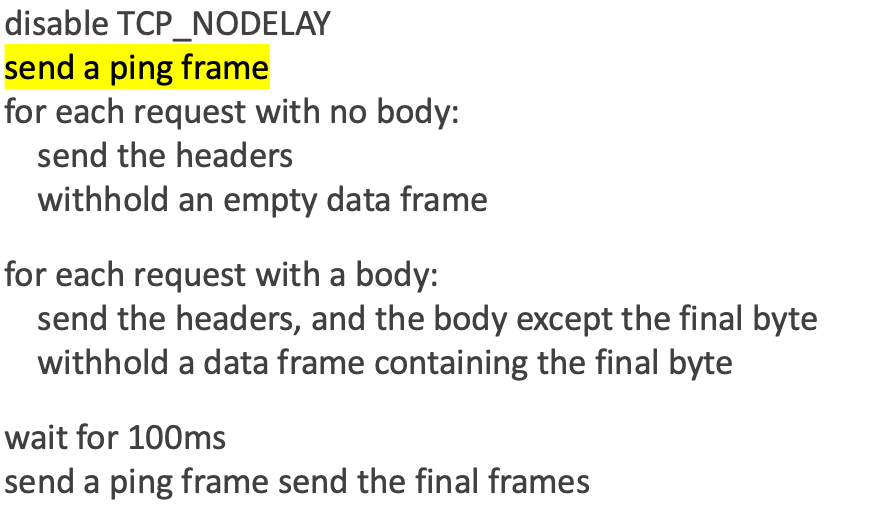 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 yora1928/papercut-cve-2026-81578-82078
Security research tool for PaperCut CVE-2026-81578 & CVE-2026-82078
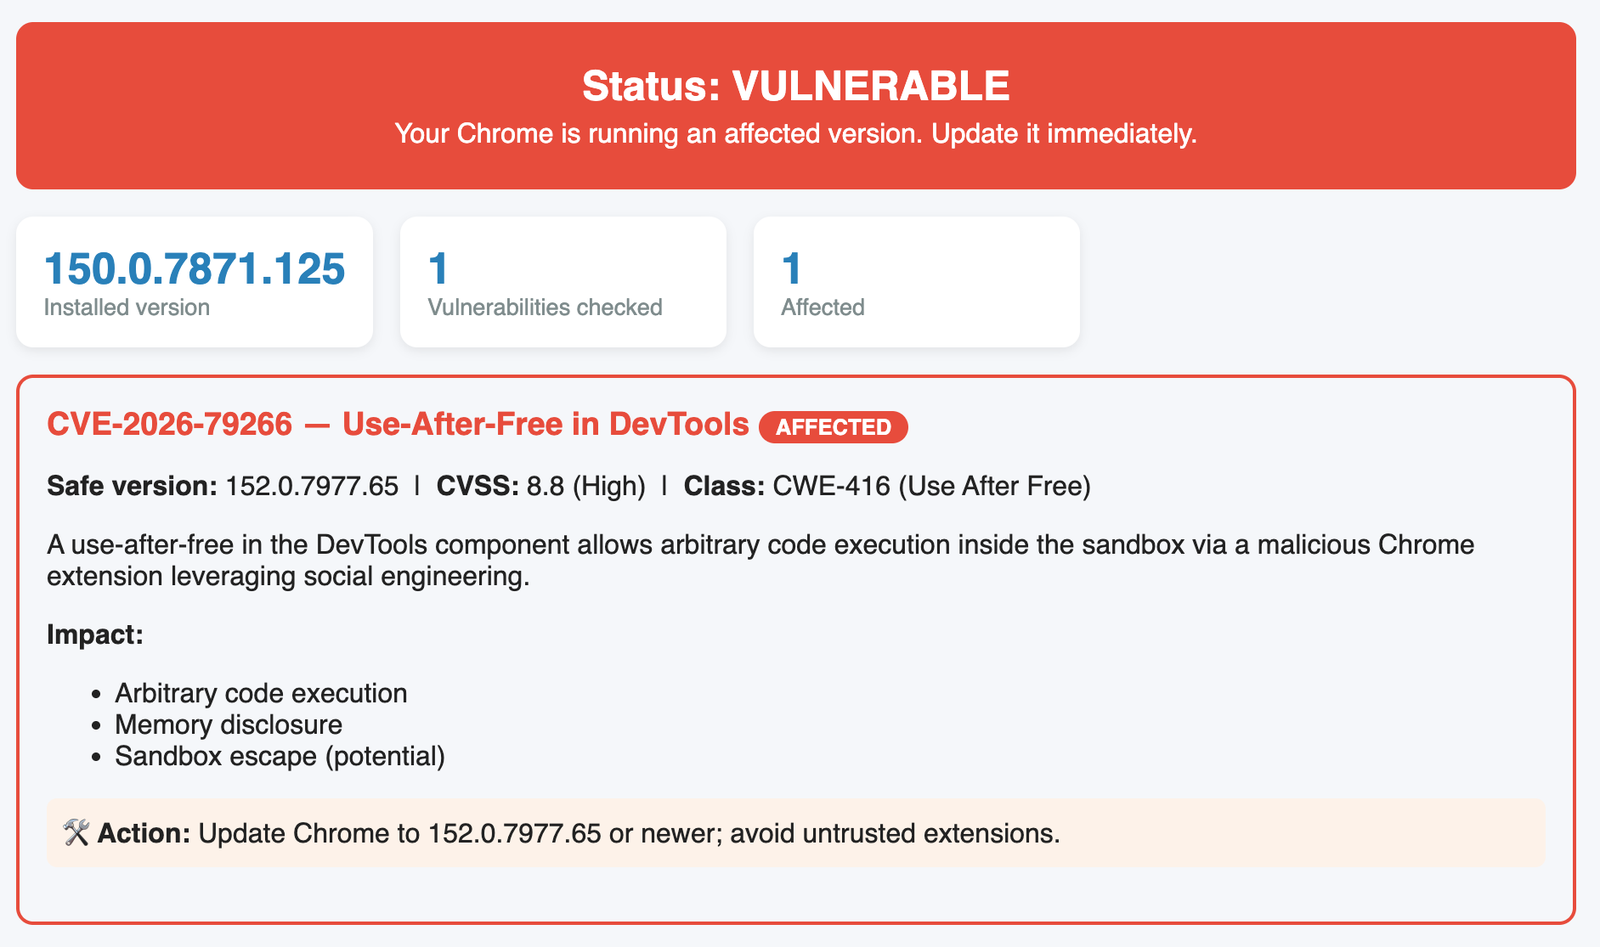 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
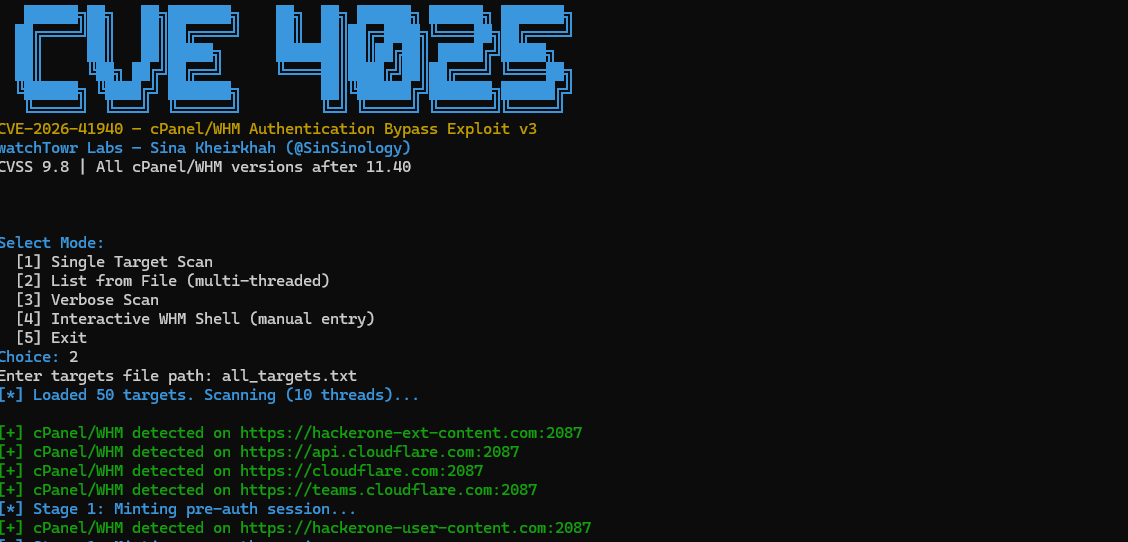 senyx122/cve-2026-41940
A security research tool for detecting and analyzing cPanel/WHM services and their authentication behavior. Designed for authorized testing and…
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
 cybrdude/cve-2026-1731-scanner
Passive vulnerability scanner for CVE-2026-1731 — BeyondTrust RS/PRA pre-auth RCE (CVSS 9.9). Educational & defensive use only.
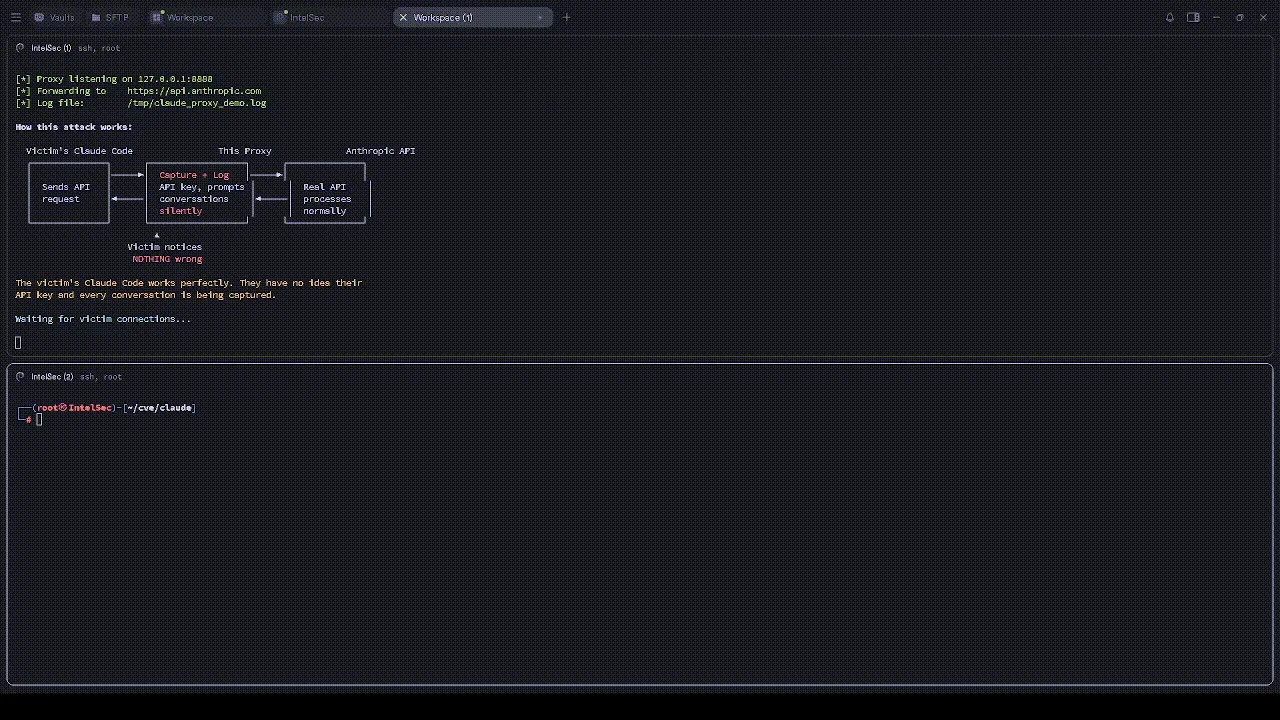 atiilla/cve-2026-21852-poc
Educational demo of three Claude Code vulnerabilities (hooks bypass, MCP injection, API key exfiltration) with attacker server, MITM proxy, and…
 deadexpl0it/wp2shell-poc
wp2shell — WordPress Core Pre-Auth RCE Chain poc for CVE-2026-63030 and CVE-2026-60137
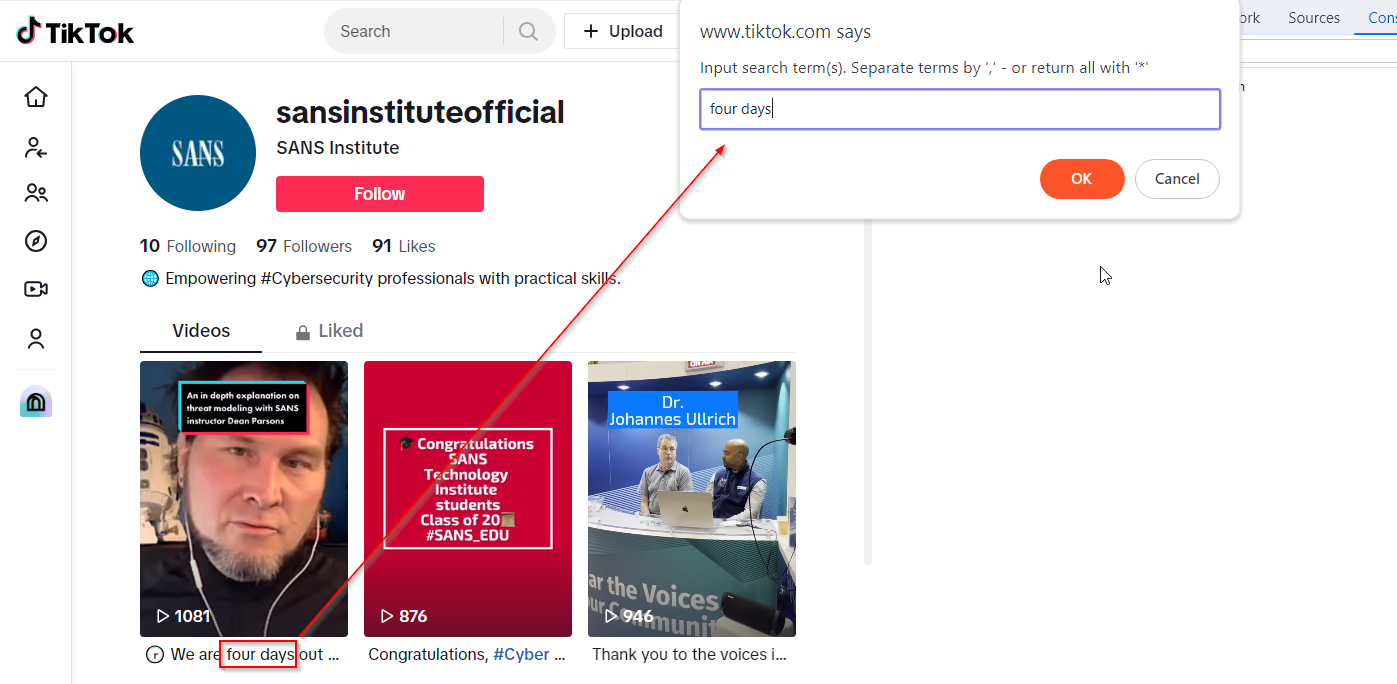 janhalendk/react
A OSINT project that explores how to dump data from React
 math-x-io/cve-2025-25296
Proof of Concept (POC) for the CVE-2025-25296 vulnerability affecting Label Studio versions prior to 1.16.0
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
 boredchilada/clickfix-simulator-2025
A lightweight, self-hosted simulation tool for "ClickFix" (ClearFake) social engineering training. Safely simulates clipboard-injection attacks with…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…