

WebGoat
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
ctfeducationlabs-practice+4
9.4k10 days ago
webgoat/webgoatDeliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
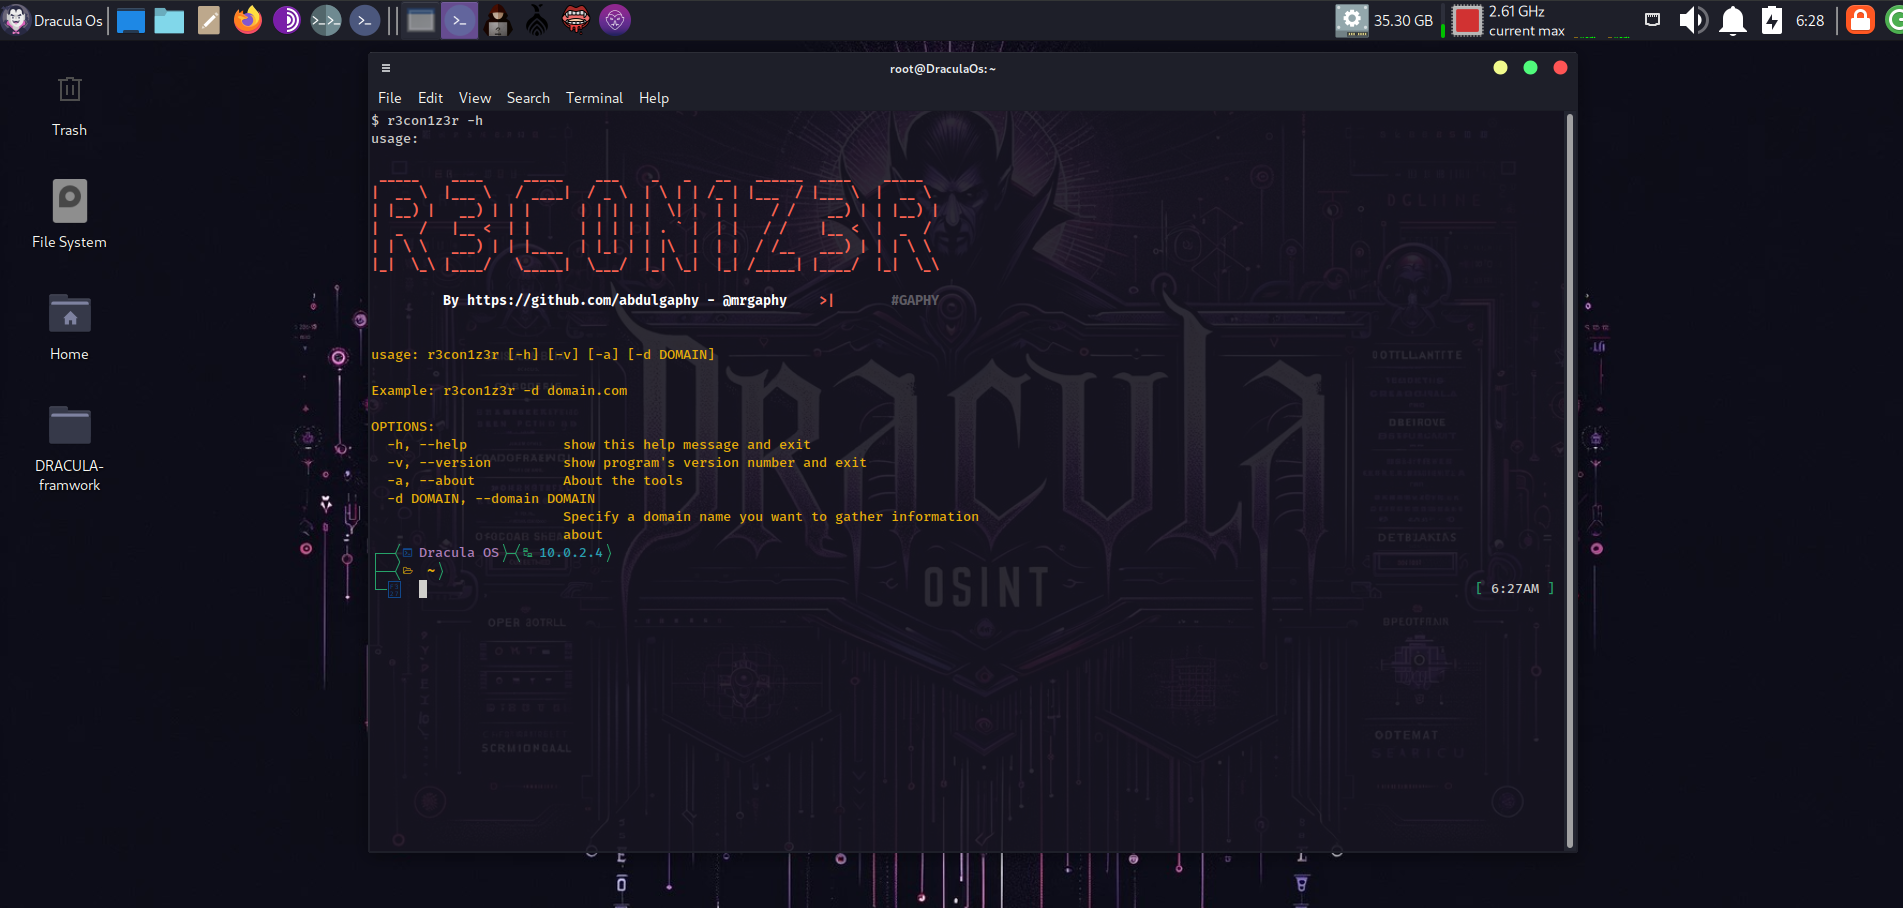 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 cumakurt/mudos
Command-line multi-vector DDoS test tool with 129 volumetric, protocol, application, and amplification attack vectors for authorized resilience…
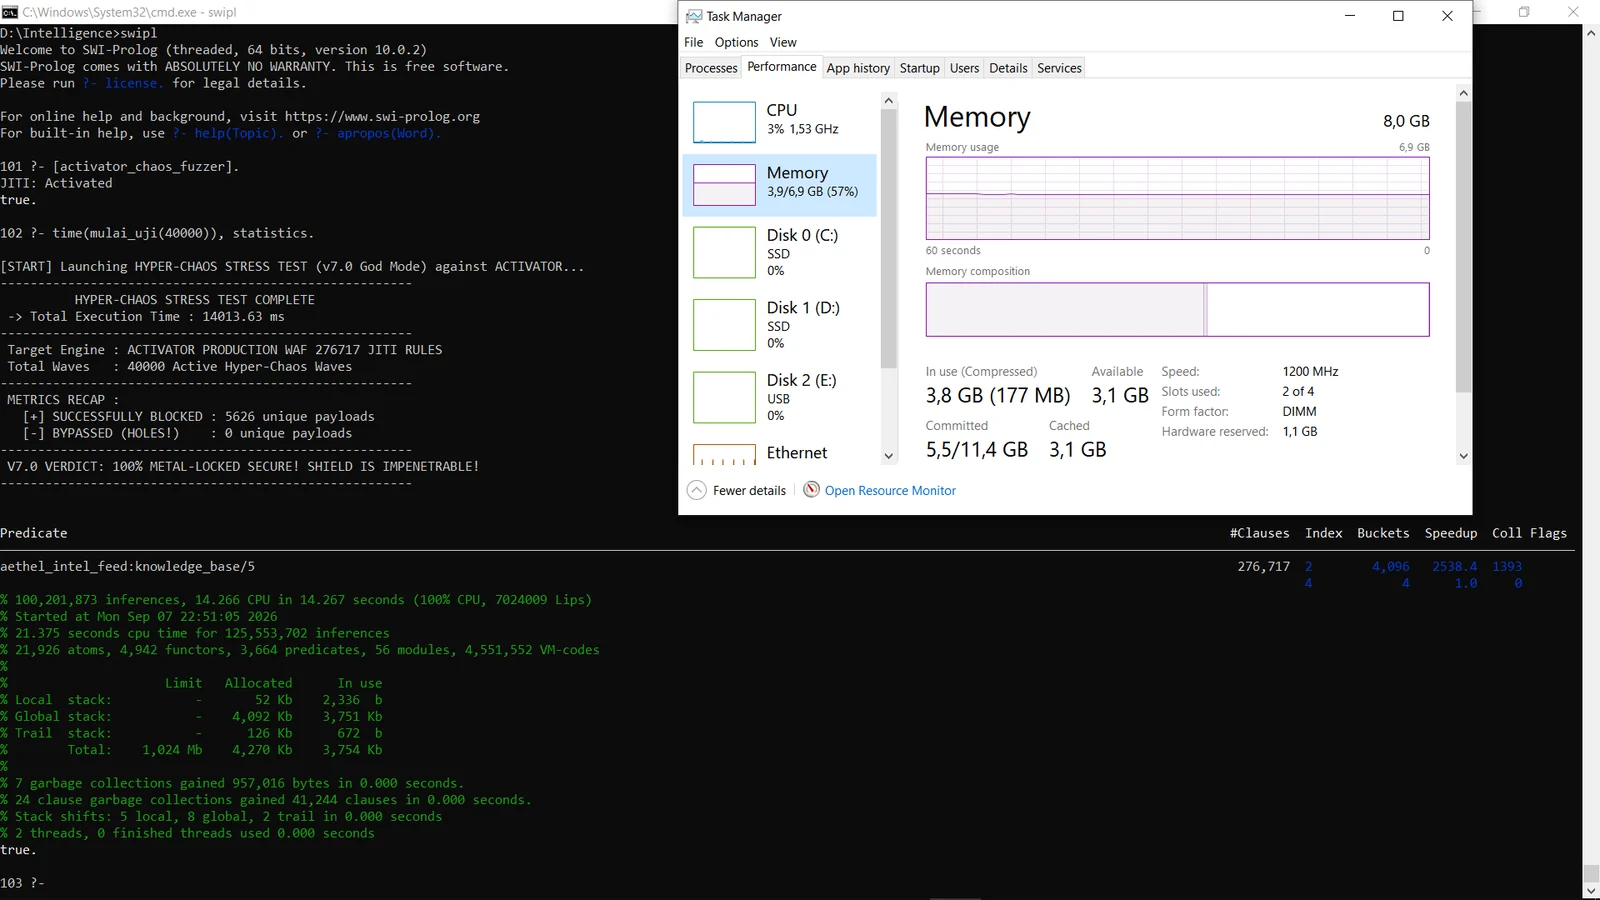 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 kac89/cve-2024-5961
Proof-of-concept exploit for reflected XSS vulnerability in 2ClickPortal versions 7.2.31 through 7.6.4, with a search parameter injection payload.
 bst04/cybersources
A curated list of cybersecurity tools and resources.
 ramadhanamizudin/lazyweb
LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 nccgroup/tracy
A tool designed to assist with finding all sinks and sources of a web application and display these results in a digestible manner.
 nu11secur1ty/python
Curated collection of Python scripts and tutorials for penetration testing, web security, and exploitation techniques, designed for security…
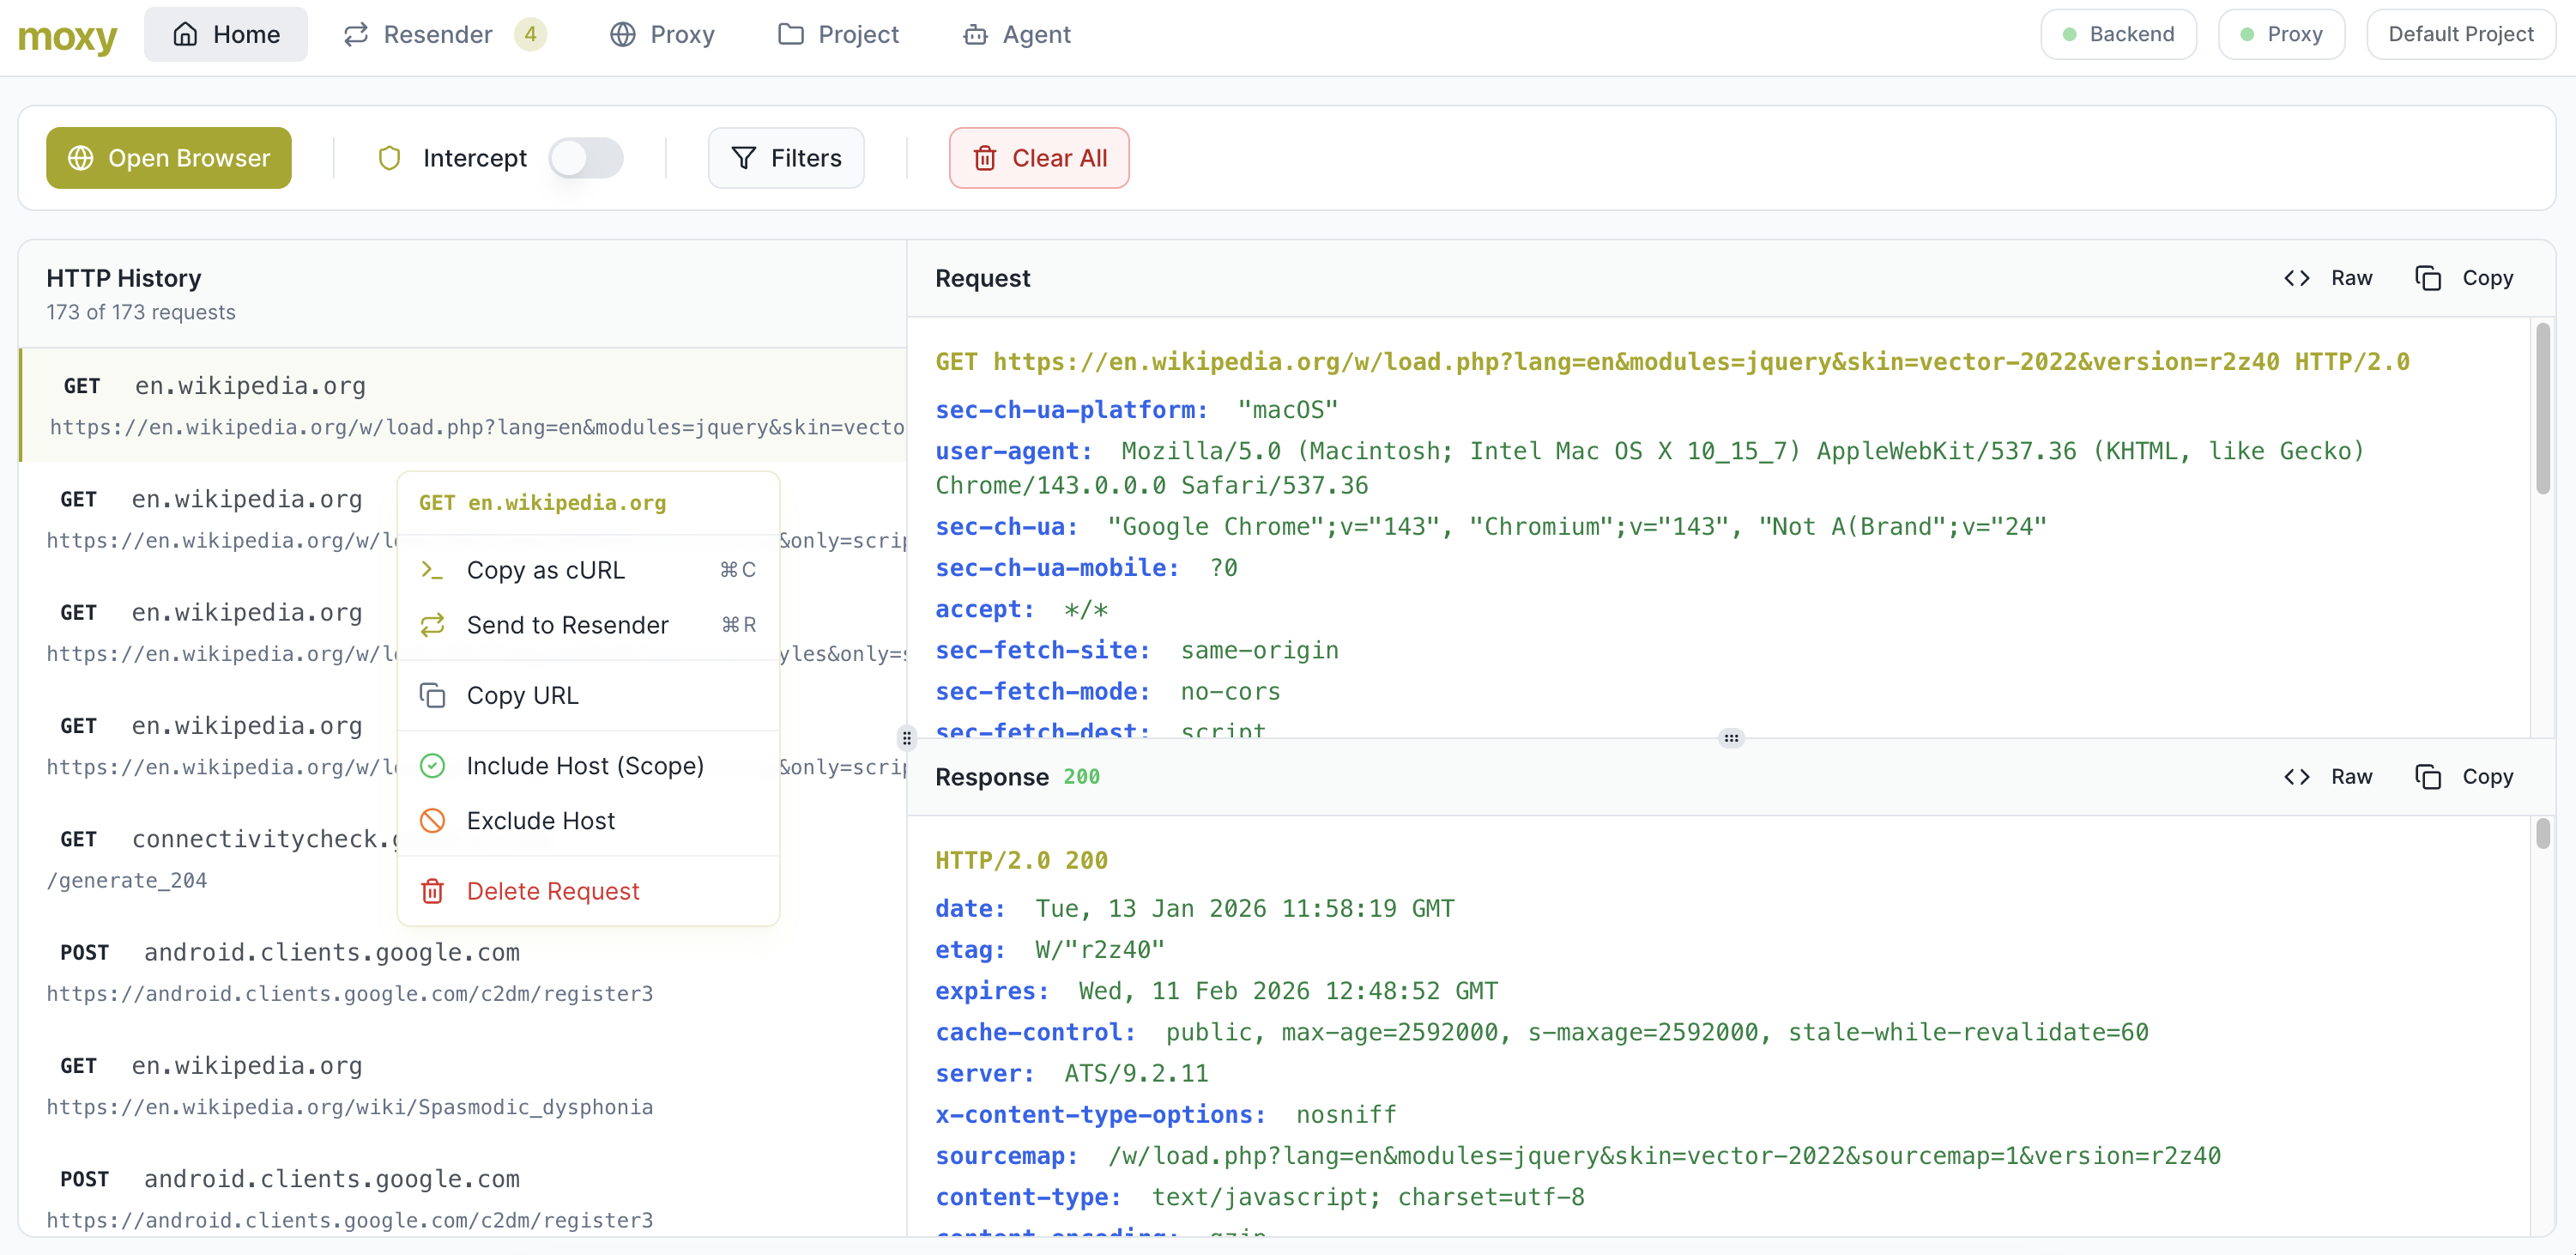 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.