

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool

 skyllpro/cve-2021-44026-poc
Bug Chain XSS (CVE-2020-35730 and CVE-2023-43770) to SQLi (CVE-2021-44026)

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 happynote3966/cve-2018-7600
Exploit for CVE-2018-7600, a critical remote code execution vulnerability in Drupal core. Enables automated exploitation of unpatched Drupal sites…
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
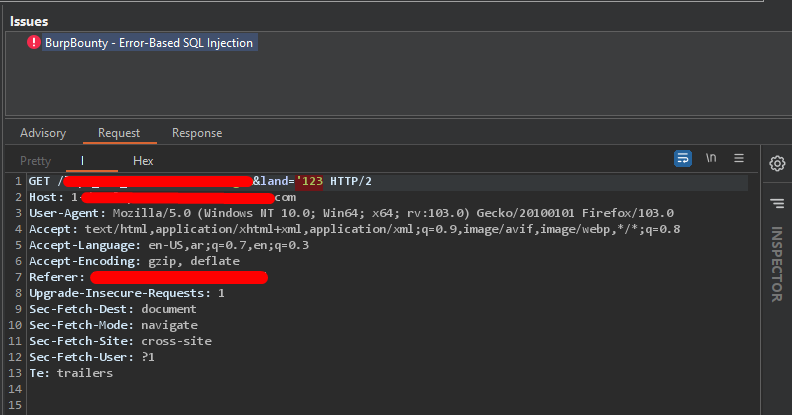 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
 neobee714/cve-2025-57819-poc
FreePBX 未认证SQL注入导致远程代码执行,FreePBX 15 (低于 15.0.66)、16 (低于 16.0.89)、17 (低于 17.0.3)。该漏洞位于商业化“endpoint”模块中,因对用户输入过滤不严,允许未认证的攻击者绕过管理员权限,执行SQL注入,并最终实现远程代码执行
 destr4ct/cve-2022-0739
Proof-of-Concept exploit (SQLI BookingPress before 1.0.11)
 ghostinexile/cve-2026-63030-wp2shell
WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
 gmh5225/cve-2024-6028-poc
CVE-2024-6028 Quiz Maker <= 6.5.8.3 - Unauthenticated SQL Injection via 'ays_questions' Parameter
 xsshk/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
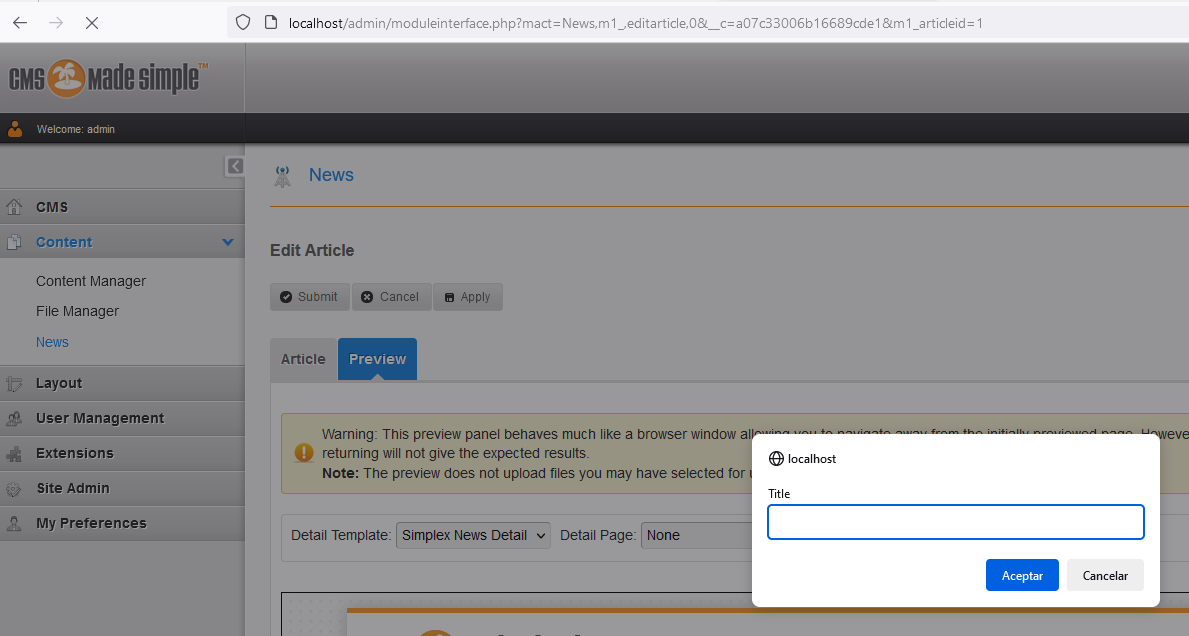 sromanhu/cve-2023-43358-cmsmadesimple-stored-xss---news
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Title in…