
CVE-2021-31166
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
exploitationexploit-frameworkspayload-development+4
6
mauricelambert/cve-2021-31166CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 0xbartita/cookie-swapper
Burp Suite extension that auto-replaces cookies and headers in requests using configurable rules. Eliminates manual copy-pasting of session tokens…
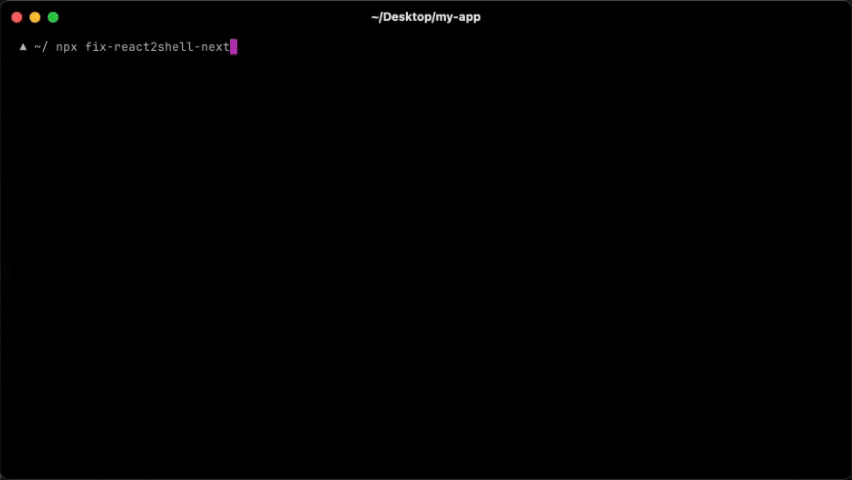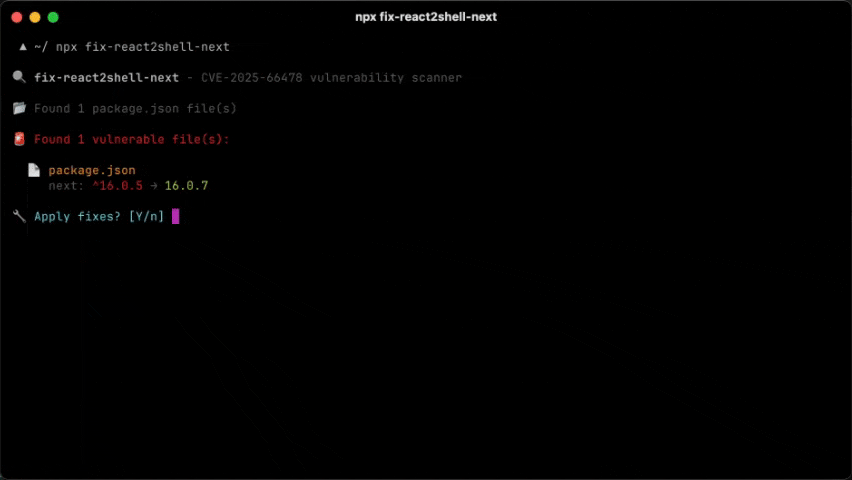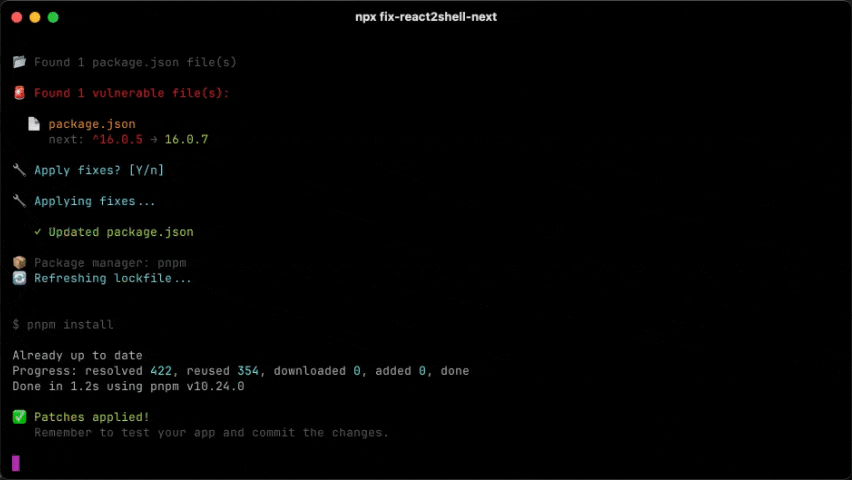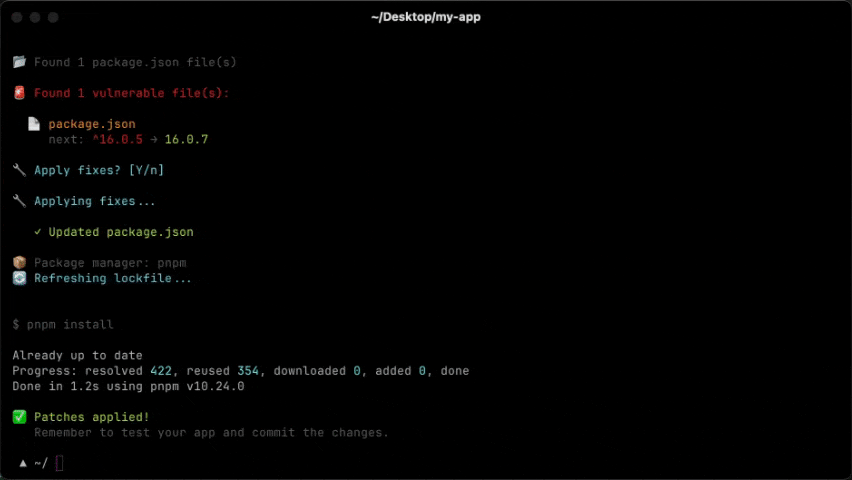 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 daryllundy/cve-2025-53770
Network-based vulnerability scanner for detecting systems vulnerable to CVE-2025-53770 (unsafe deserialization). Includes PowerShell and Python…
 theresafewconors/cve-2025-29927-testing
PowerShell script to test if a web app is vulnerable to CVE-2025-29927
 sarperavci/googlerecaptchabypass
Solve Google reCAPTCHA in less than 5 seconds! 🚀
 fzakaria/anubis-fetch
Like curl, but it gets past Anubis and Cloudflare bot-walls.
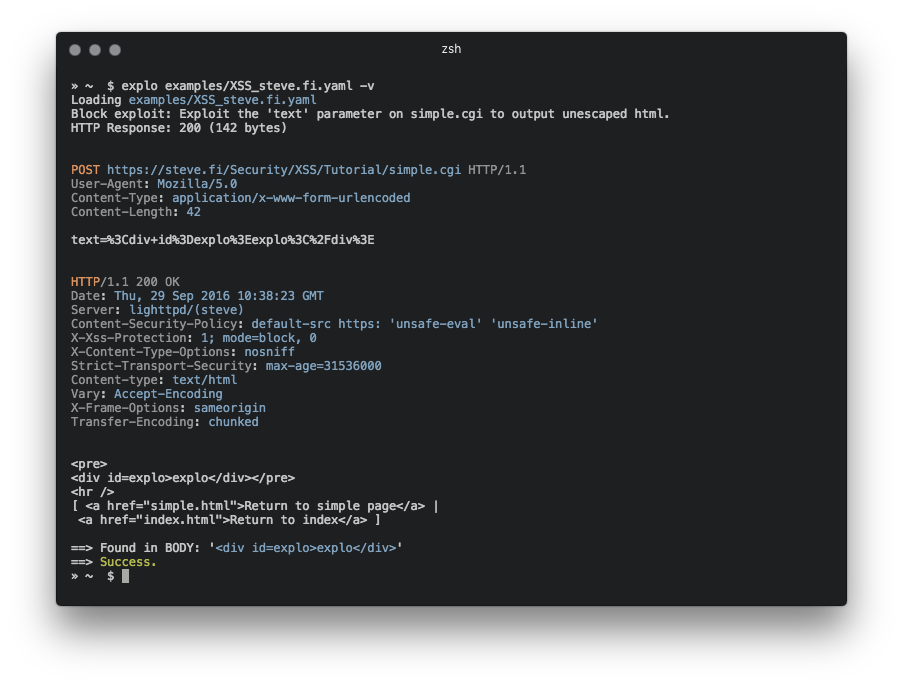 telekom-security/explo
Human and machine readable web vulnerability testing format
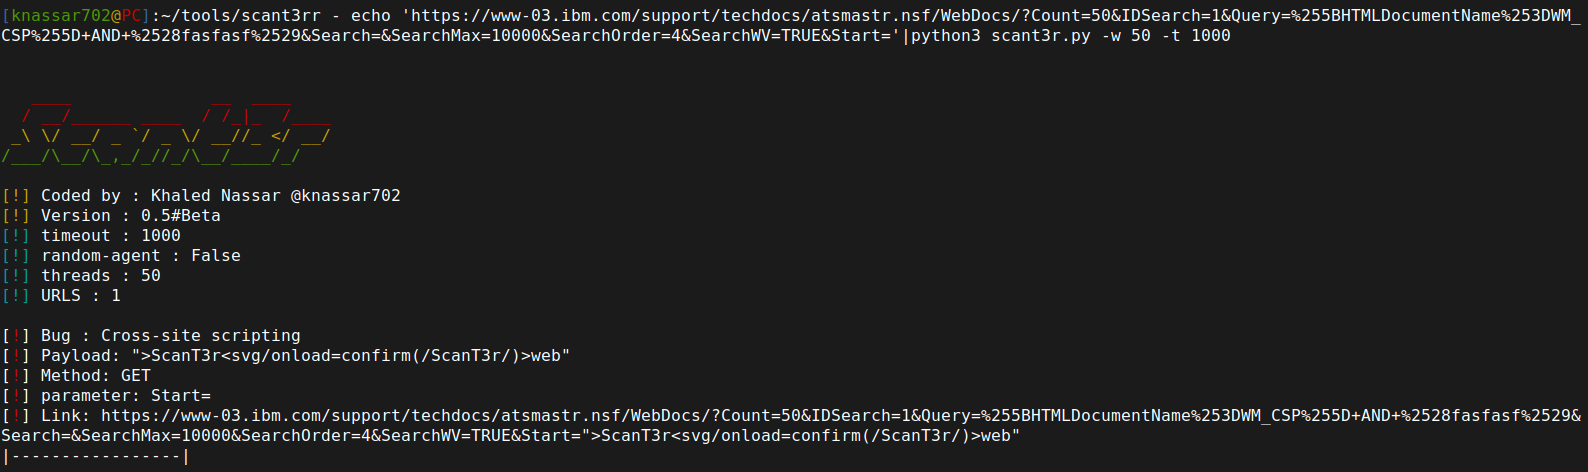 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 infiniroot/nginx-mitigate-log4shell
Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script
 adamrpostjr/cve-2021-27065
Quick One Line Powershell scripts to detect for webshells, possible zips, and logs.
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 google/safetext
Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.
 pratham220/cve-2026-17543-php-exposure-validator
Safe PowerShell validator for PHP CVE-2026-17543 exposure via HTTP headers and non-destructive login-form probes.
 logisek/huntcyberark
CyberArk Security Audit
 dzonerzy/gowapt
Go Web Application Penetration Test
 rsrdesarrollo/generator-burp-extension
Everything you need about Burp Extension Generation
 0sm0s1z/invoke-selfsignedwebrequest
This repo exists as a quick and dirty arsenal of methods and scripts to subvert .NET SSL/TLS certificate validation in PowerShell and press on with…