
http2smugl
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
penetration-testingvulnerability-analysisweb-application-exploitation+1
564
neex/http2smuglDetects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 cxosmo/cve-2021-42697
Proof of concept exploit for CVE-2021-42697: Akka HTTP 10.1.x before 10.1.15 and 10.2.x before 10.2.7 can encounter stack exhaustion while parsing…
 corelight/cve-2021-41773
Zeek package detecting Apache HTTP Server path traversal/RCE exploits (CVE-2021-41773, CVE-2021-42013) with payload capture and server header…
 theopaid/cve-2026-66752-http-request-smuggling-via-unparsed-transfer-encoding-values-tiny_http-
Security Advisory: HTTP Request Smuggling via Unparsed Transfer-Encoding Values (tiny_http)
 sirredbeard/cve-2025-60876
Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…
 w2hcorp/cve-2025-29927-poc
Here is a simple but effective exploit for CVE-2025-29927.
 liaoziqi-gzfls/cve-2026-42945
CVE-2026-42945 Nginx Rift
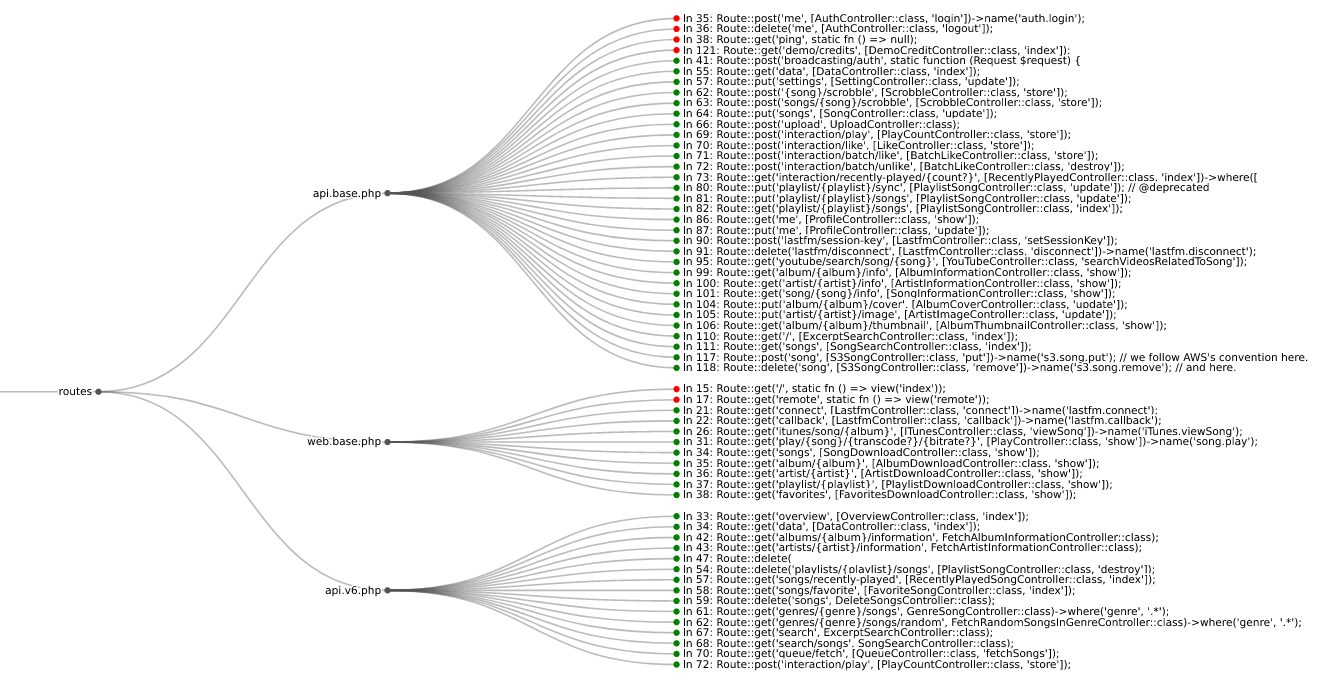 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 corelight/cve-2021-44228
Zeek package for detecting Log4j CVE-2021-44228 exploit attempts via HTTP header payloads, LDAP Java class downloads, and second-stage Java class…
 yuxblank/cve-2022-2466---request-context-not-terminated-with-graphql
Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…
 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
 theopaid/cve-2026-67182-http-request-smuggling-enables-front-end-access-control-bypass-rouille-
Security Advisory: HTTP Request Smuggling Enables Front-End Access Control Bypass (rouille)
 theopaid/cve-2026-66753-http-header-injection-via-unvalidated-cr-and-lf-in-header-values-tiny_http-
Security Advisory: HTTP Header Injection via Unvalidated CR and LF in Header Values (tiny_http)
 rubbxalc/cve-2025-29927
Functional exploit for CVE-2025-29927, a critical Next.js middleware authorization bypass. Sends crafted HTTP requests with the…
 renio-wow/cve-2026-51416
Analyzes a specific CVE in WeChat OAuth handler, identifying unbounded HTTP response reads leading to denial of service, with remediation guidance.
 thewhiteh4t/cve-2020-9375
TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
 knotsecurity/cve-2025-29927-nextjs-middleware-simulation
Simulates CVE-2025-29927, a critical Next.js vulnerability allowing attackers to bypass middleware authorization by exploiting the internal…