
CVE-2026-87902
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
2
bhideki/cve-2026-87902Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
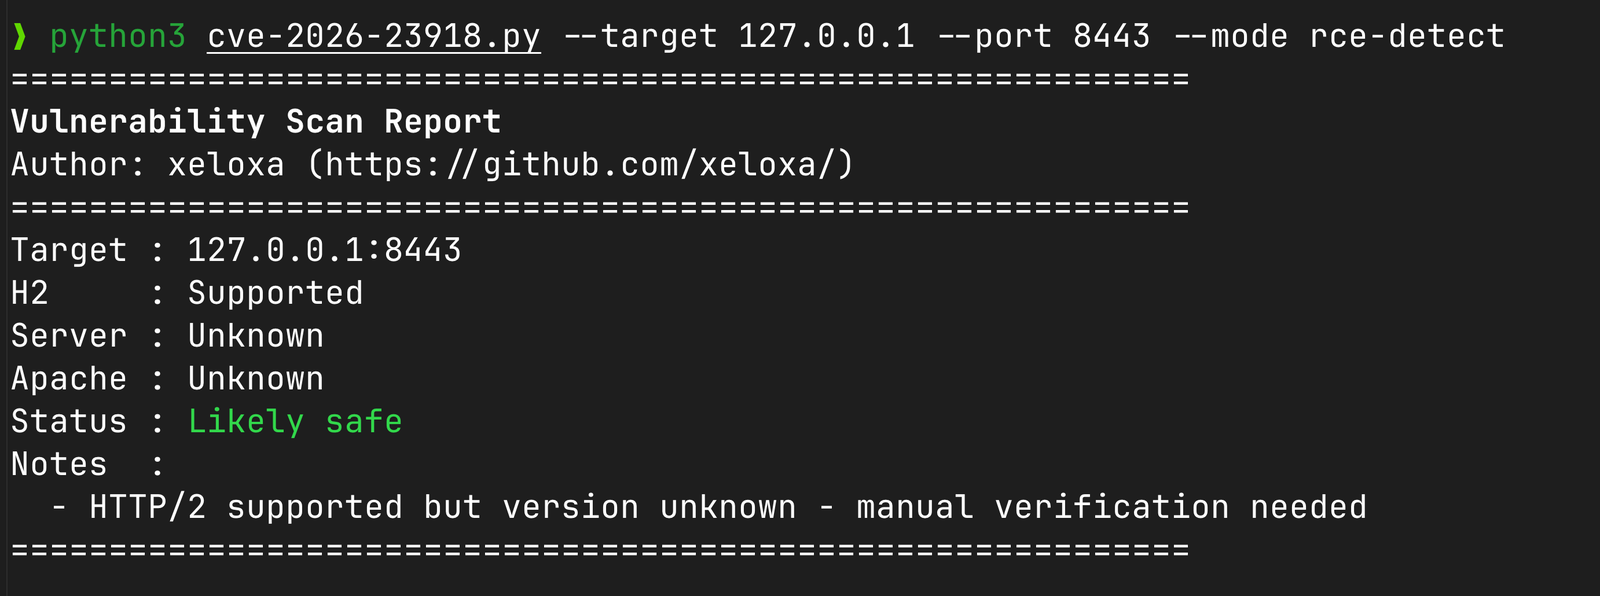 xeloxa/cve-2026-23918-apache-h2-poc
Proof-of-Concept exploit for CVE-2026-23918 (Apache mod_http2 double-free). Features multi-mode DoS (Rapid-RST, Slow-Drip) and passive…
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…
 r00tali/cve-2026-39200
The value of the produk request parameter is copied into the value of an HTML tag attribute which is encapsulated in double quotation marks. The…
 rshosting/apache-cve-2026-23918-fix
Upgrade to Apache 2.4.67 to fix CVE-2026-23918 vulneribility
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
 ubaydev/cve-2026-11551-poc
Proof-of-concept exploit for CVE-2026-11551, an unauthenticated privilege escalation vulnerability in the Branda White Label plugin for WordPress,…
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 rhasan-com/cve-2026-23918
Apache HTTP/2 double-free vulnerability PoC (CVE-2026-23918)
 halcy0nic/cve-2023-38434
Proof of Concept for CVE-2023-38434
 dotadrien/cve-2025-60656
Stored XSS vulnerability proof-of-concept for Script Pag's 'Recent Ads' module, exploiting unsanitized double quotes in image URL fields to execute…
 iveresk/cve-2022-21907-http.sys
An unauthenticated attacker can send an HTTP request with an "Accept-Encoding" HTTP request header triggering a double free in the unknown…