

 lascc/hacktools
The all-in-one browser extension for offensive security professionals 🛠
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
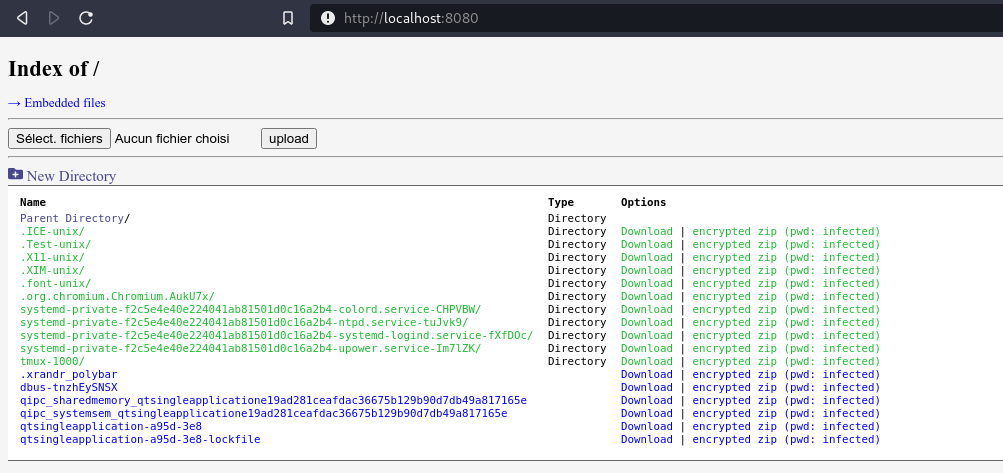 nodauf/swego
Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 digitalocean/nginxconfig.io
⚙️ NGINX config generator on steroids 💉
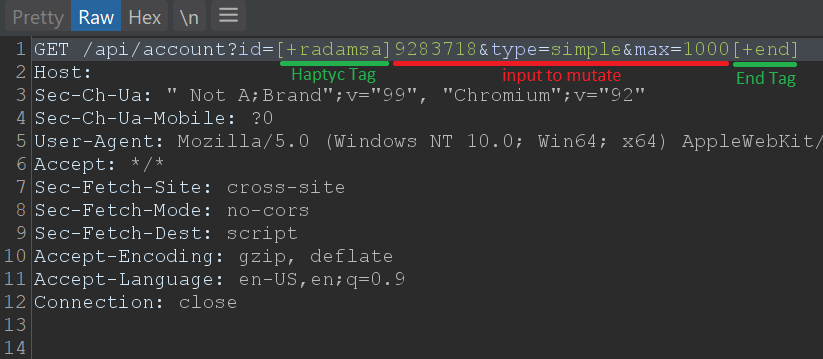 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 rsrdesarrollo/generator-burp-extension
Everything you need about Burp Extension Generation
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 watchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451
Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 jenderal92/cve-2026-49049
Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…
 thekawix/cve-2026-41940
Generates detection artifacts to verify cPanel/WHM authentication bypass vulnerability (CVE-2026-41940) and tests targets for exposure.