
CVE-2021-31166
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
exploitationexploit-frameworkspayload-development+4
6
mauricelambert/cve-2021-31166CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
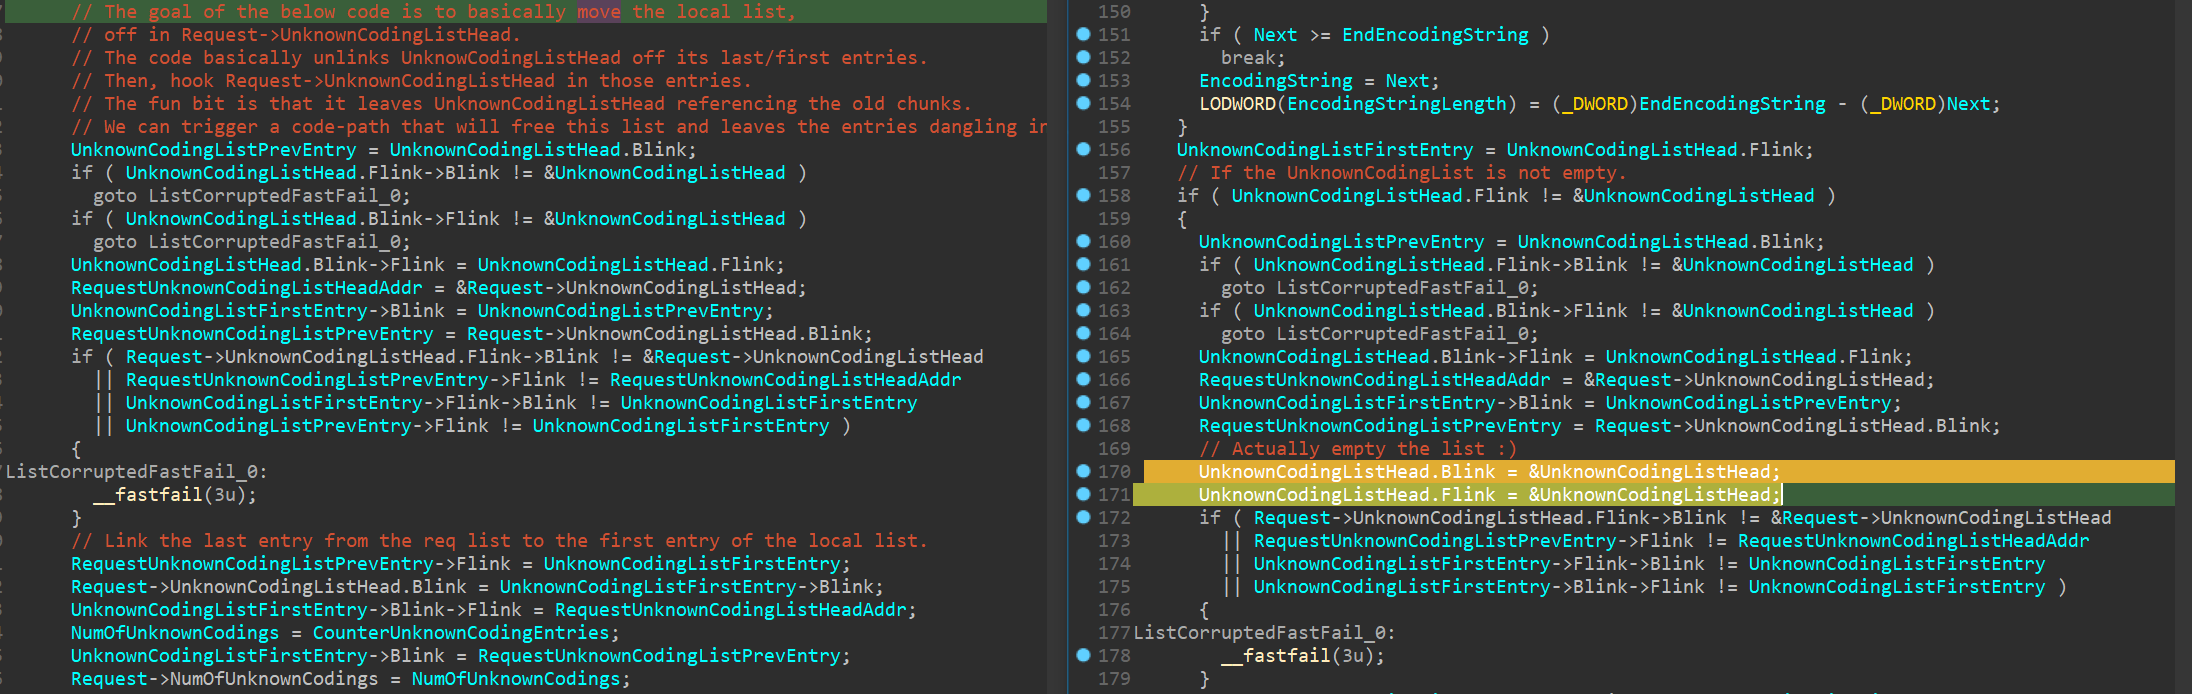 0vercl0k/cve-2021-31166
Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.
 corelight/cve-2021-41773
Zeek package detecting Apache HTTP Server path traversal/RCE exploits (CVE-2021-41773, CVE-2021-42013) with payload capture and server header…
 mehrzad1994/cve-2021-21193
Educational presentation analyzing CVE-2021-21193, a use-after-free vulnerability in Google Chrome's Blink engine, including exploitation details and…
 suniastar/scan-log4shell
A scanning suite to find servers affected by the log4shell flaw (CVE-2021-44228) with example to test it
 sanupl/cve-2021-46073
CVE-2021-46073 - A Stored Cross Site Scripting (XSS) vulnerability exists in Sourcecodester Vehicle Service Management System 1.0 via the User List…
 sakurasamuraii/derailed
CVE-2021-40875: Tools to Inspect Gurock Testrail Servers for Vulnerabilities related to CVE-2021-40875.
 athosgonzaga/cve-2021-3030
Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx
 grantbirki/redash-vulnerable
A Dockerized Redash instance that is vulnerable to CVE-2021-21239
 atnetws/fail2ban-log4j
fail2ban filter that catches attacks againts log4j CVE-2021-44228
 timborin0/log4j-dork-scanner
A script to search, scrape and scan for Apache Log4j CVE-2021-44228 affected files using Google dorks
 grey-master-a/metabase_nmap_script
It is a nmap script for metabase vulnerability (CVE-2021-41277)
 riptl/cve-2021-3449
CVE-2021-3449 OpenSSL denial-of-service exploit 👨🏻💻
 4jfinder/4jfinder.github.io
Searchable page for CISA Log4j (CVE-2021-44228) Affected Vendor & Software List
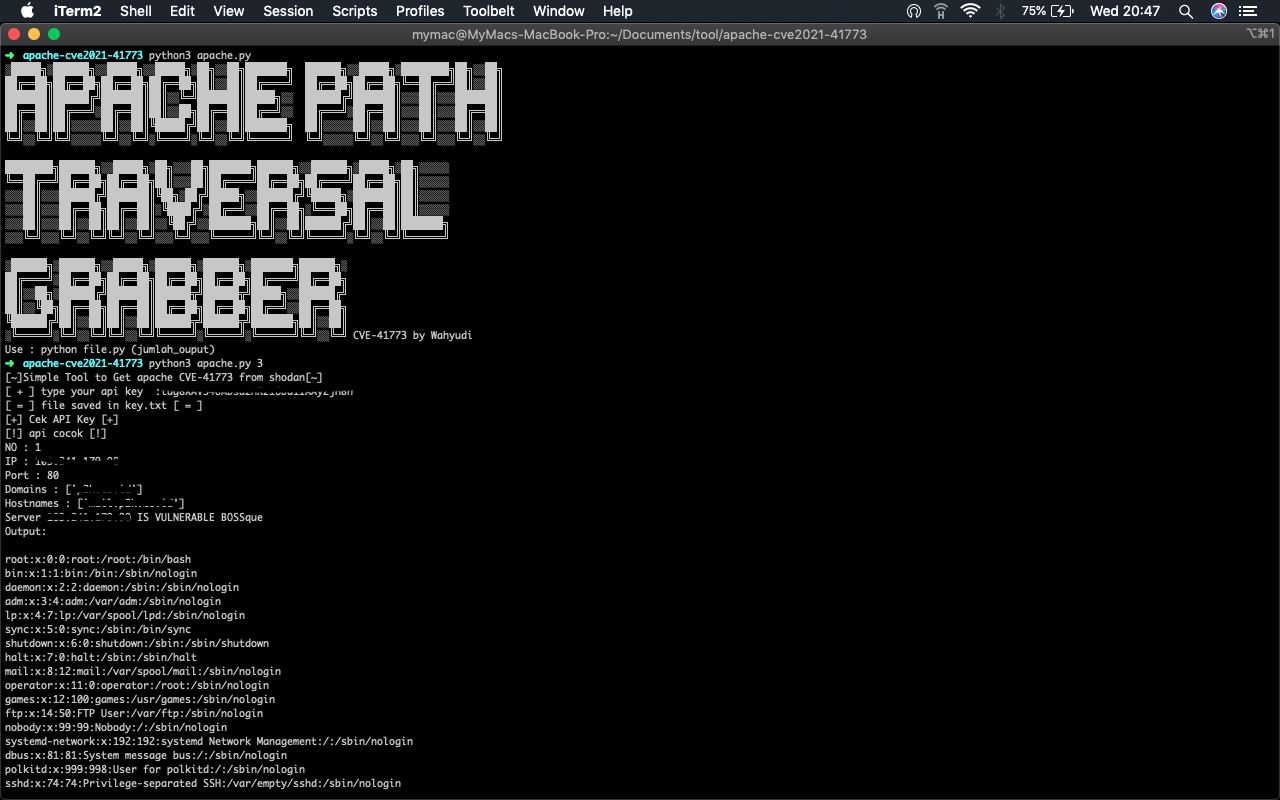 mohwahyudi/cve-2021-41773
Python script that uses Shodan to discover Apache HTTP Server 2.4.49 instances vulnerable to CVE-2021-41773 path traversal and file disclosure.
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 3ndg4me/adtran-personal-phone-manager-vulns
A repository hosting write ups for the 0 days CVE-2021-25679, CVE-2021-25680, and CVE-2021-25681
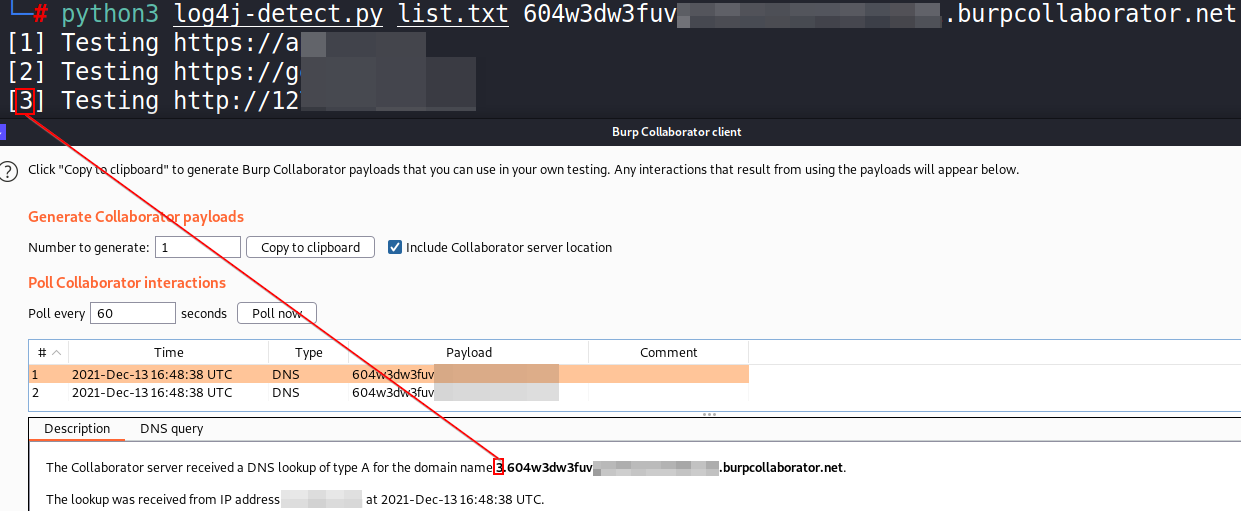 hassaanahmad813/log4j
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…