

wifipumpkin3
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
captcha-bypassdns-analysisphishing+5
p0cl4bs/wifipumpkin3Powerful framework for rogue access point attack.
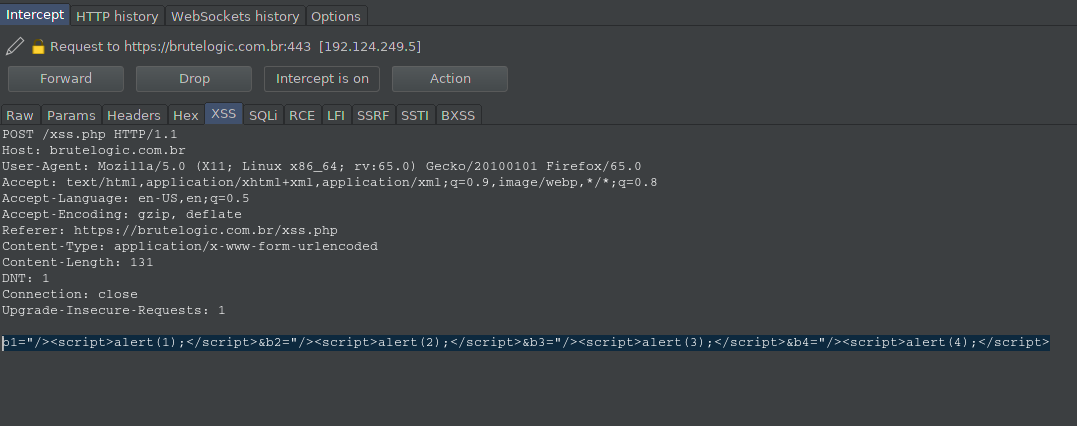 p3n73st3r/ghazi
Ghazi is a BurpSuite Plugins For Testing various PayLoads Like "XSS,SQLi,SSTI,SSRF,RCE and LFI" through Different tabs , Where Each Tab Will Replace…
 argos83/ritm
Ruby In The Middle (HTTP/HTTPS interception proxy)
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 ottimo/burp-alfresco-referer-proxy-cve-2014-9301
Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 secforce/tunna
Tunna is a set of tools which will wrap and tunnel any TCP communication over HTTP. It can be used to bypass network restrictions in fully firewalled…
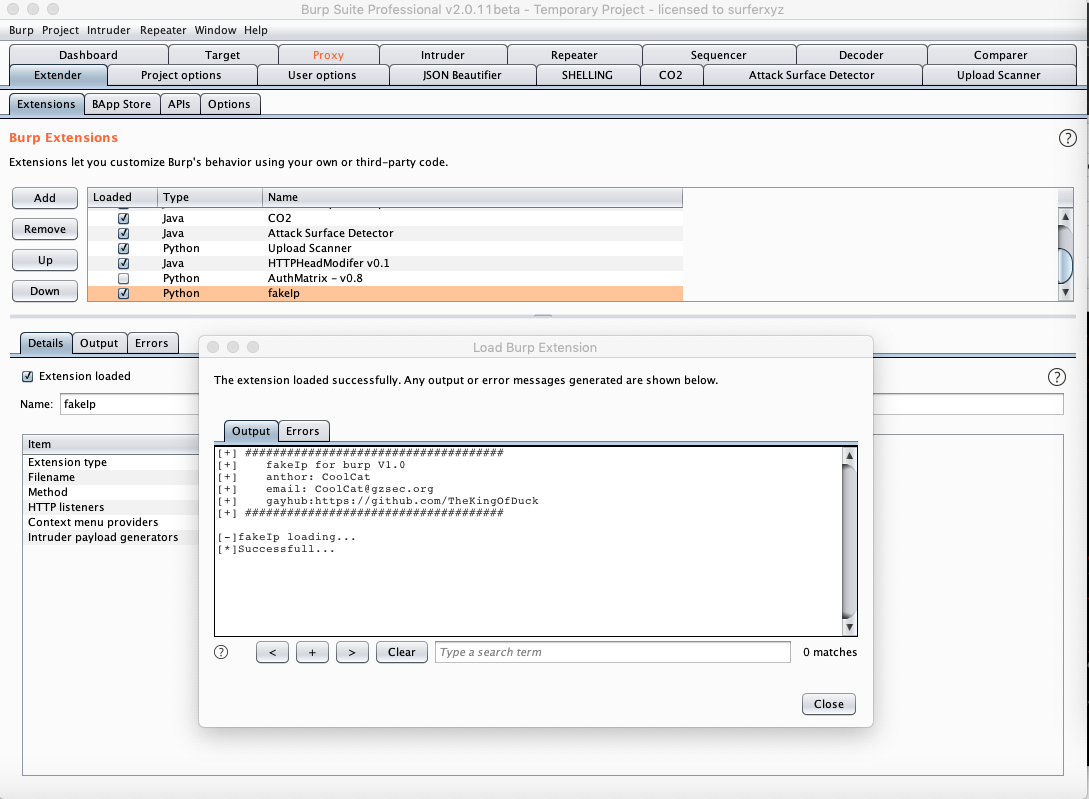 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
 inaz2/proxy2
HTTP/HTTPS proxy in a single python script
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
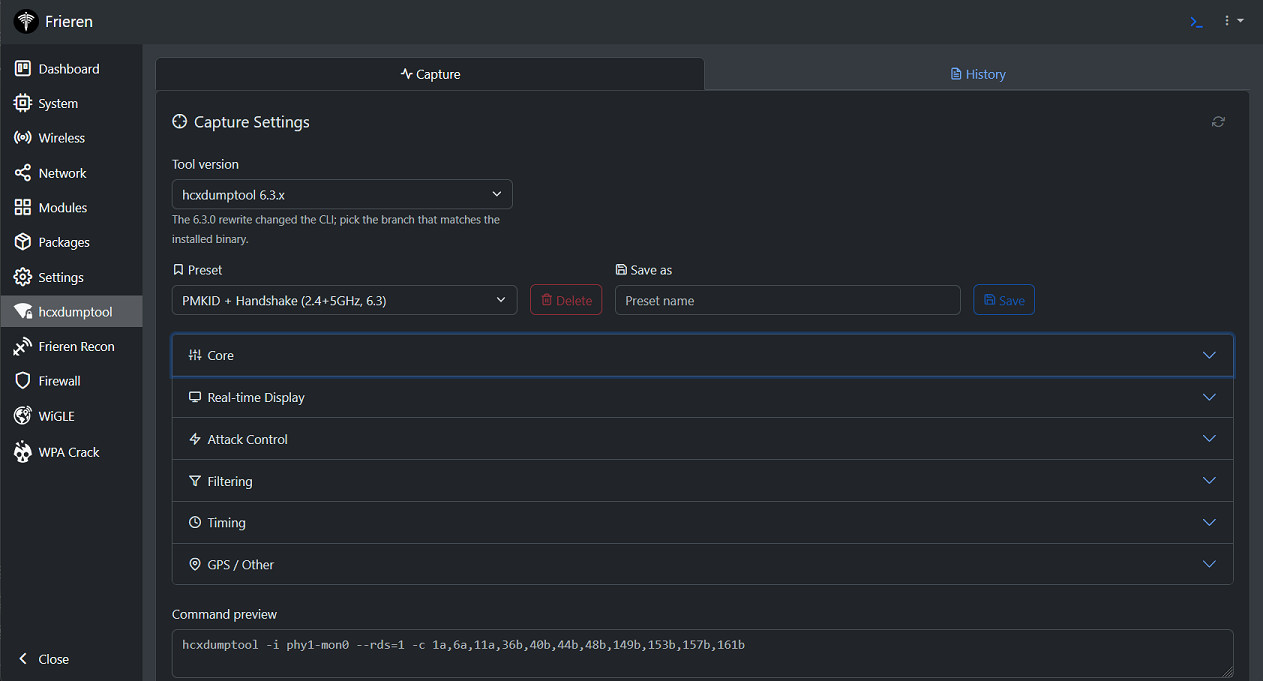 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
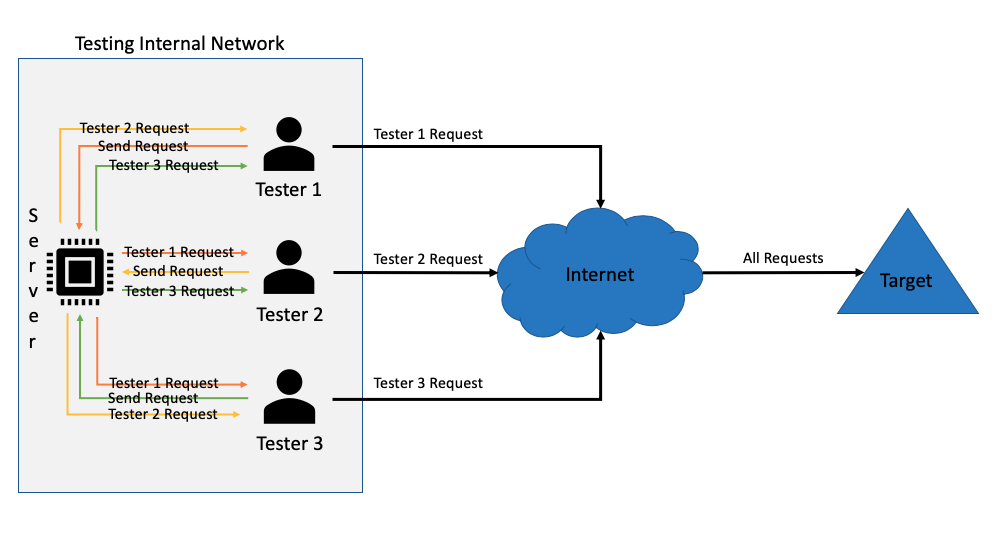 static-flow/burpsuite-team-extension
This Burpsuite plugin allows for multiple web app testers to share their proxy history with each other in real time. Requests that comes through your…
 nccgroup/datajackproxy
Datajack Proxy allows you to intercept TLS traffic in native x86 applications across platforms
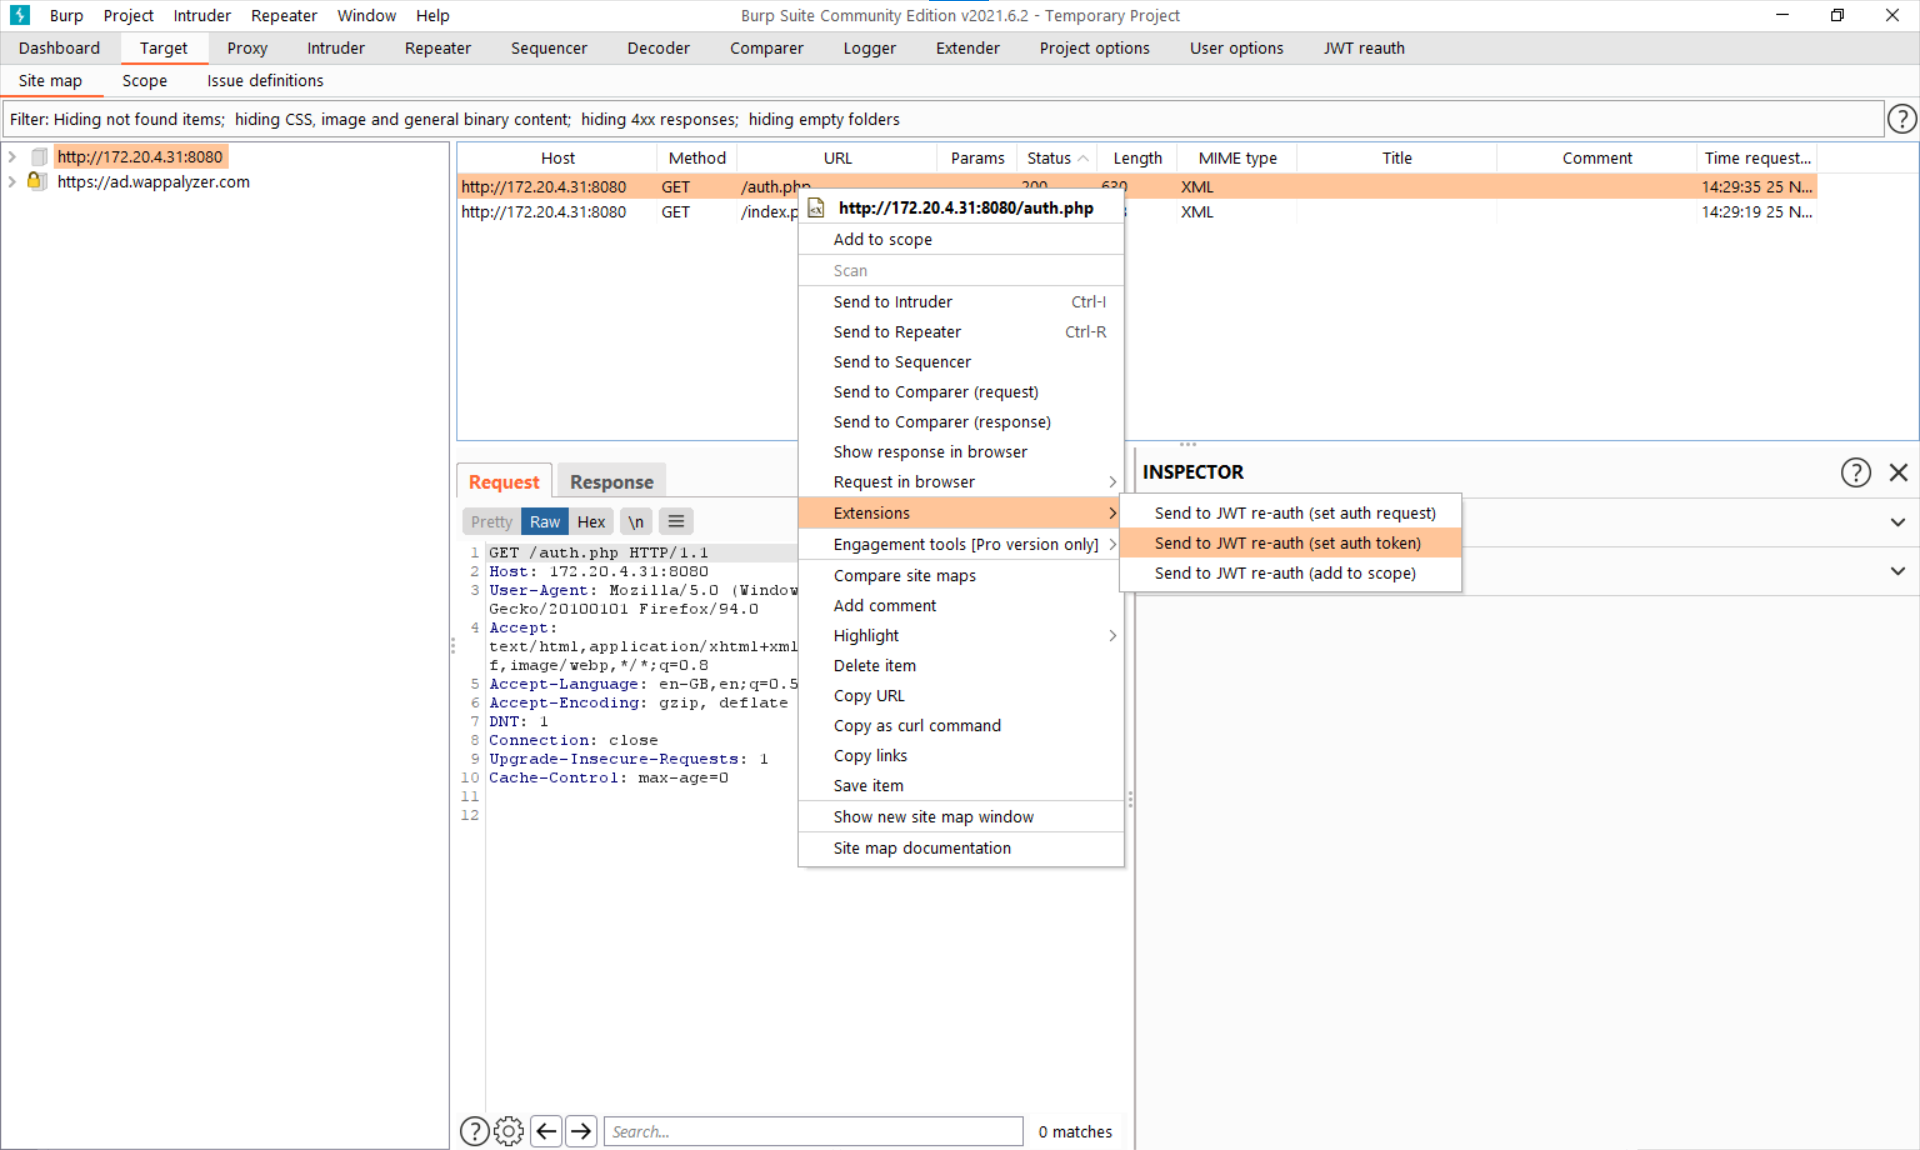 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 joanbono/gurp
Burp Commander written in Go
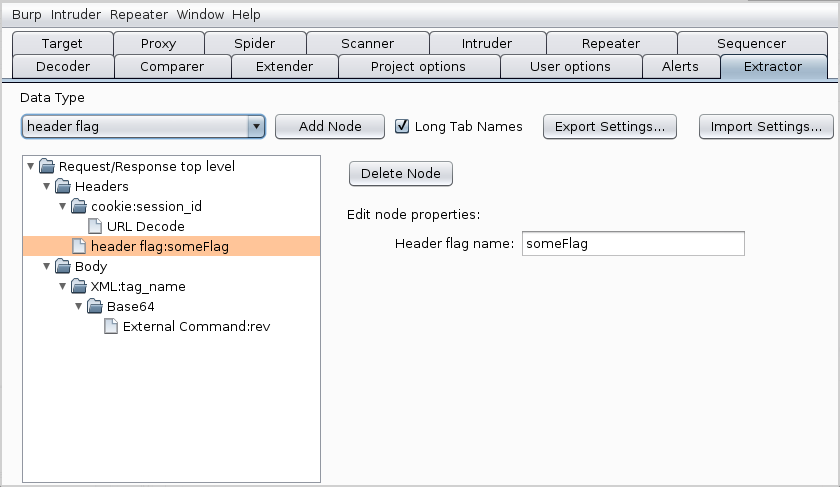 nccgroup/extractor
Extension adds a new tab in Burp Suite called Extractor
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.