 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
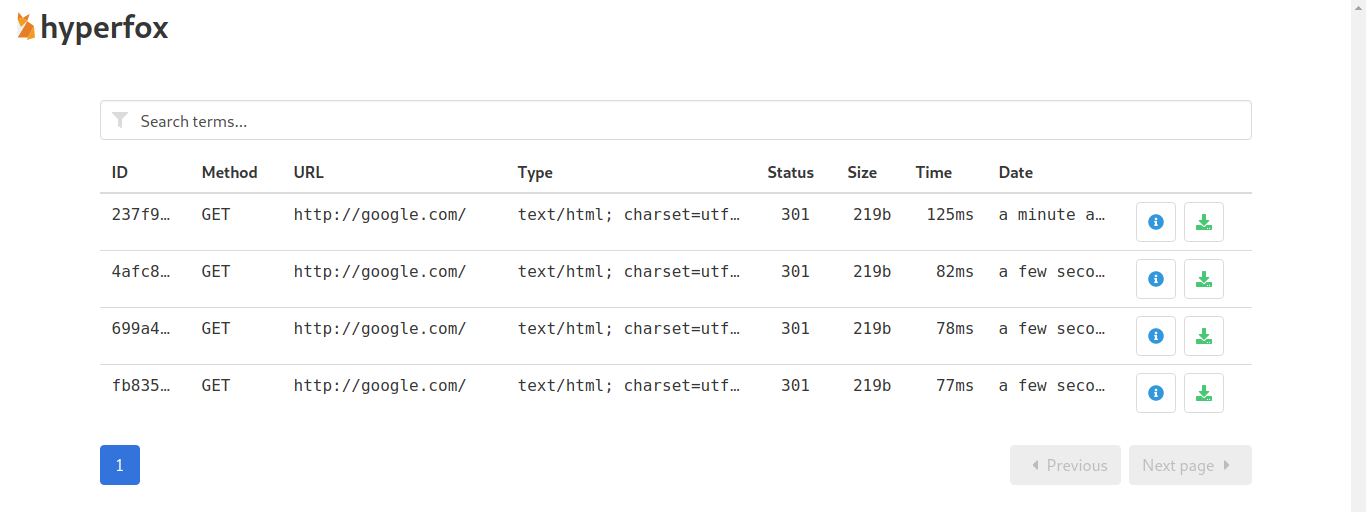 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.
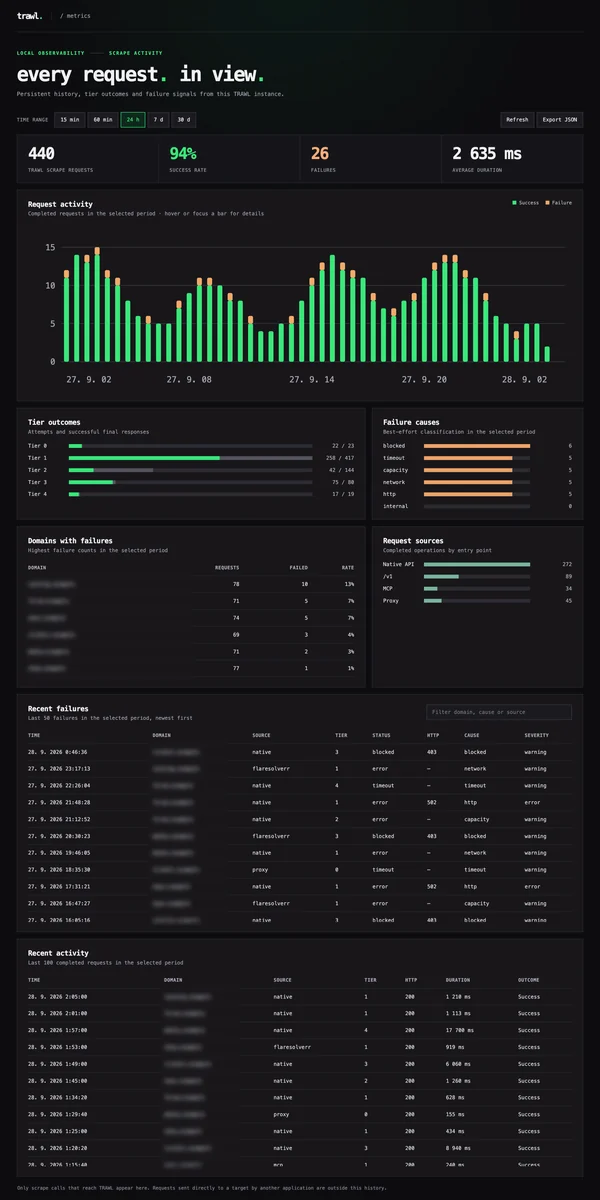 germondai/trawl
Self-hosted scraping engine — bypasses any JS challenge & captcha: Cloudflare, Turnstile, reCAPTCHA, hCaptcha, GeeTest. FlareSolverr & Byparr…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 splinters-io/blinder
Content-blind reverse proxy for exposure-protected security scanning
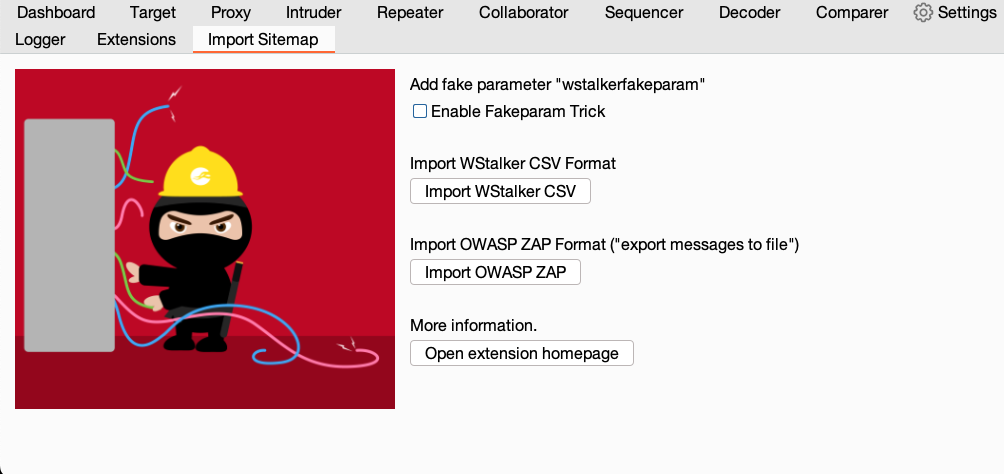 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap
 yukibtc/redknife
A Swiss Army knife for offensive security.
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…