MobileApp-Pentest-Cheatsheet

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic

Open-source MITM proxy to intercept, inspect, and mock network traffic.

Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…

The new bridge between Burp Suite and Frida!

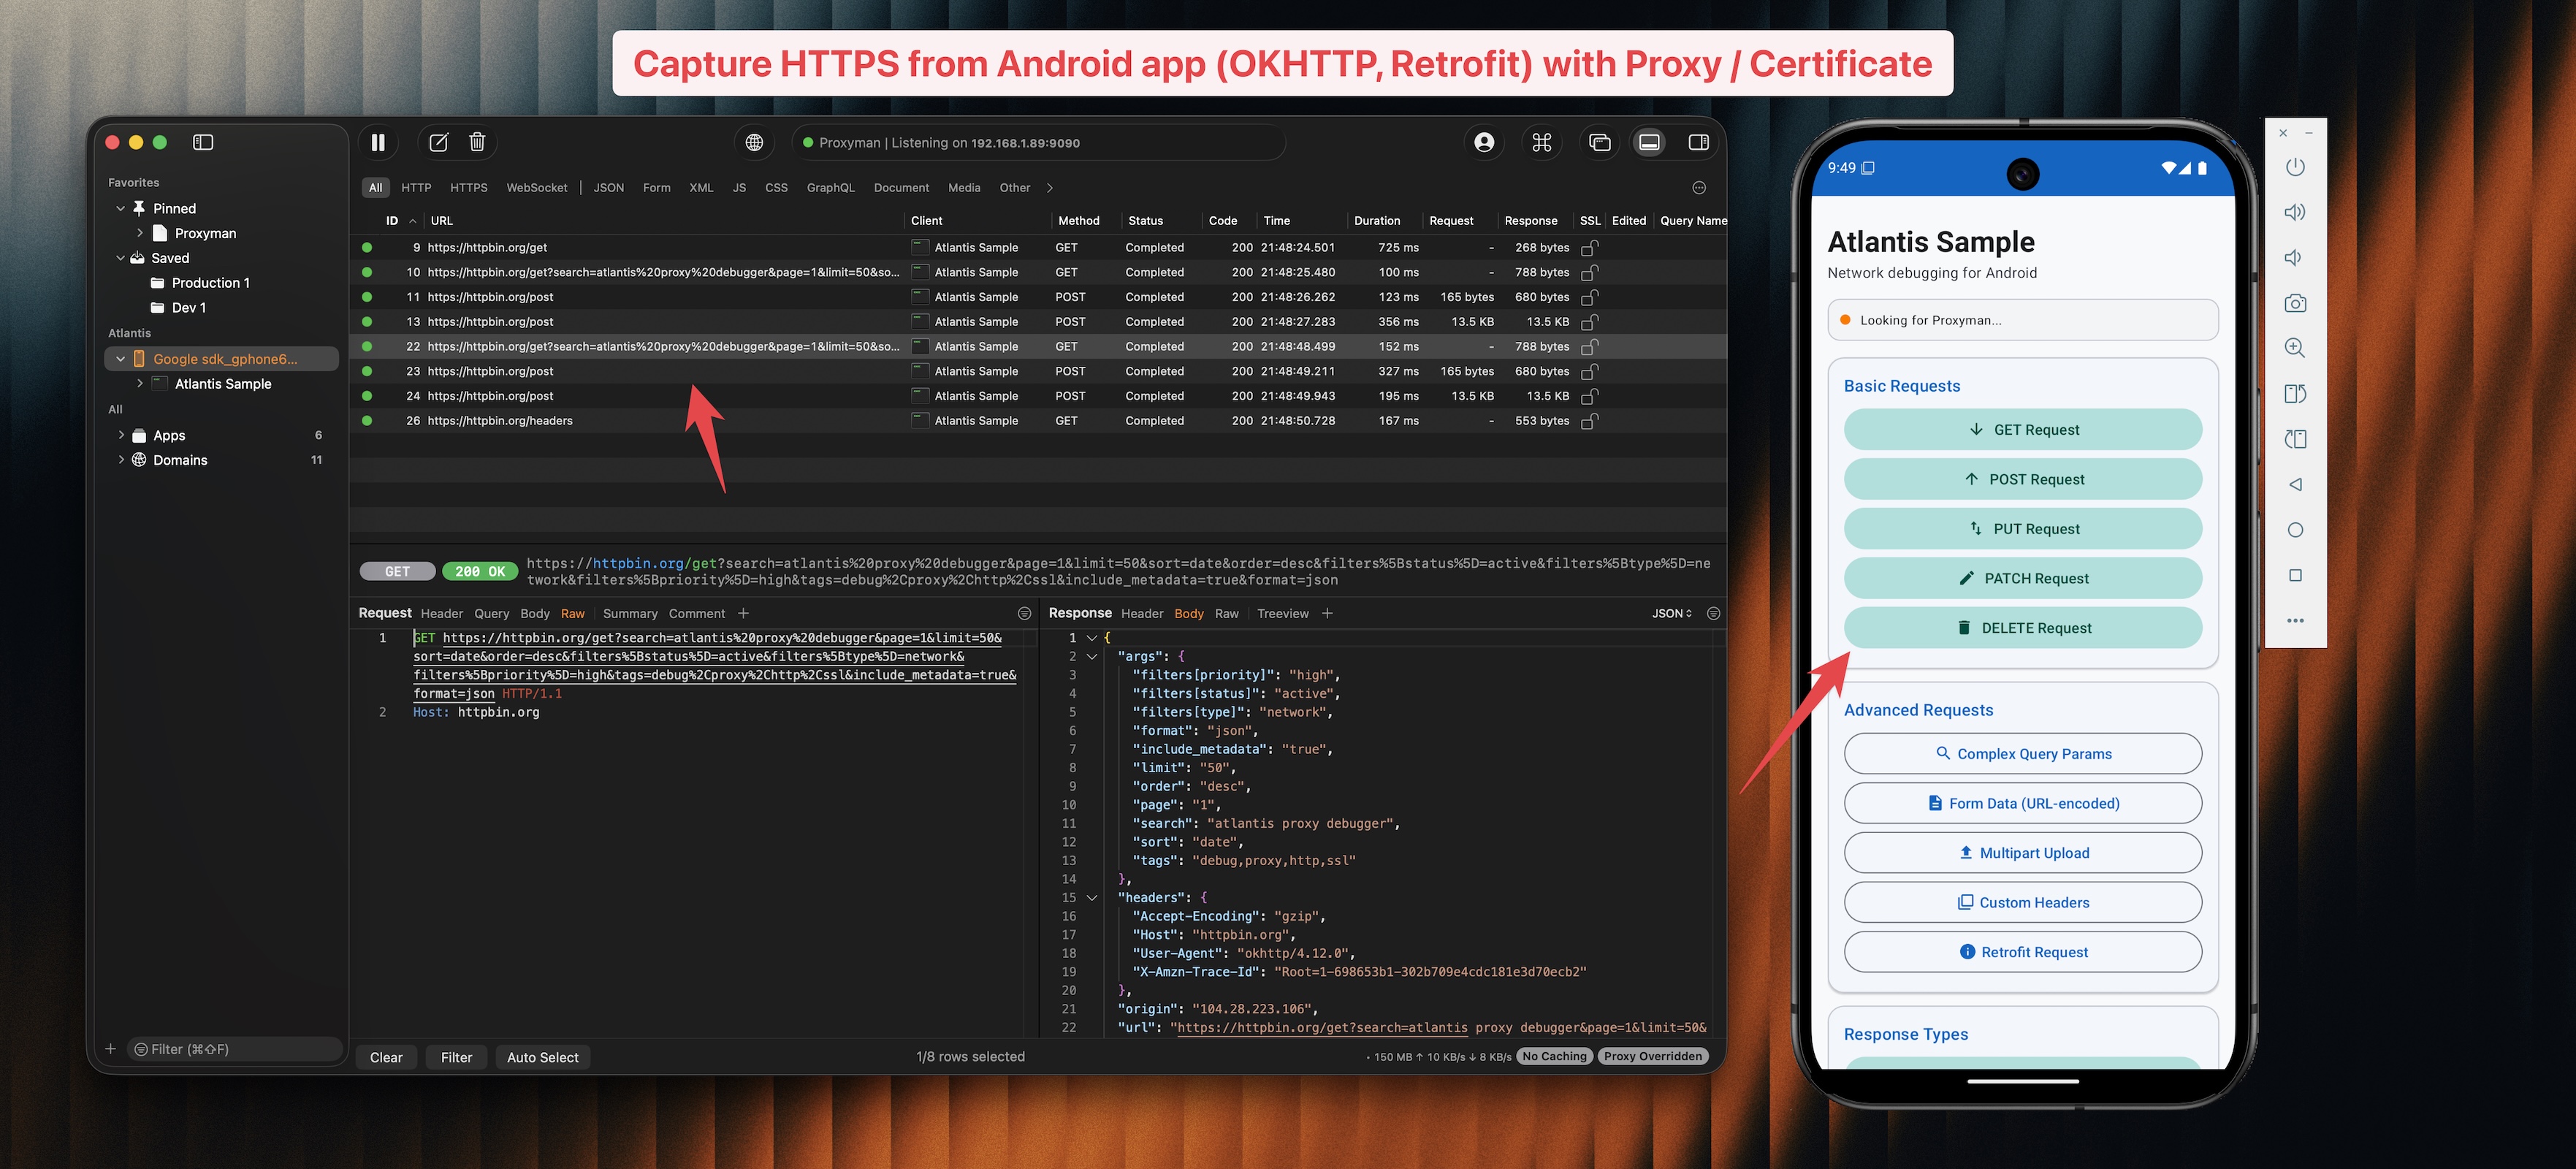
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.

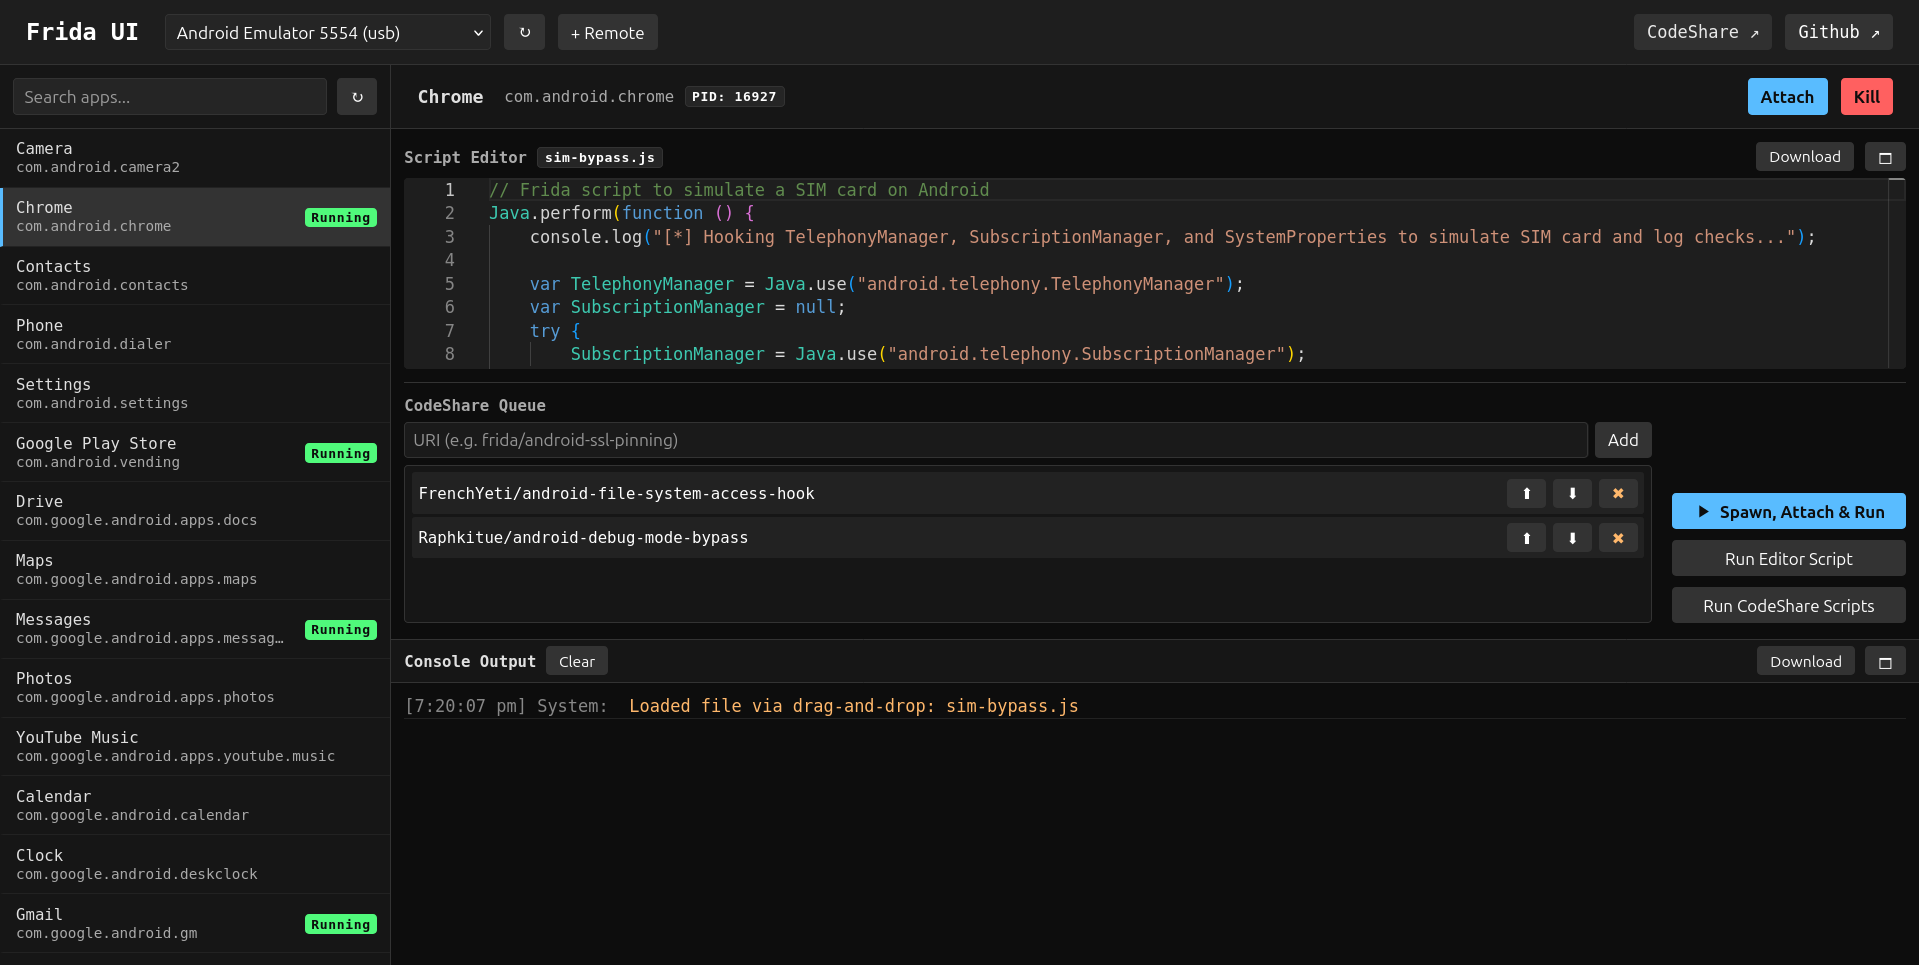
Interact with Frida devices, processes, and scripts directly from your browser.

Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…

Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.