
hoverfly
 spectolabs/hoverfly
Lightweight service virtualization/ API simulation / API mocking tool for developers and testers
api-security-testingweb-proxies-interception
spectolabs/hoverflyLightweight service virtualization/ API simulation / API mocking tool for developers and testers
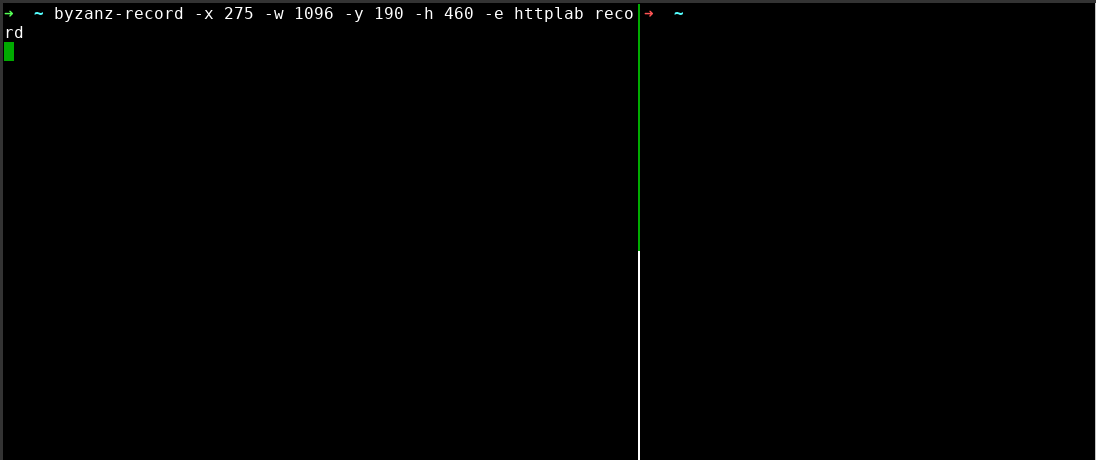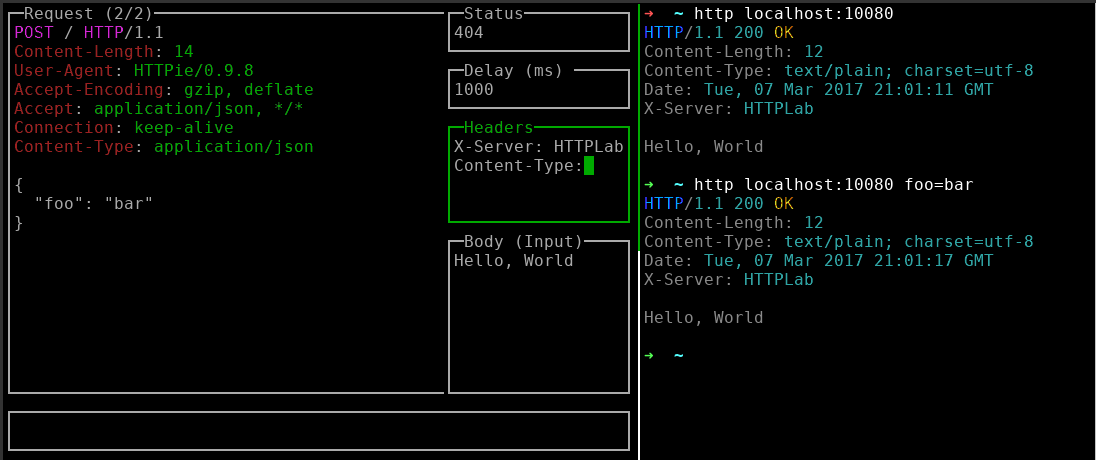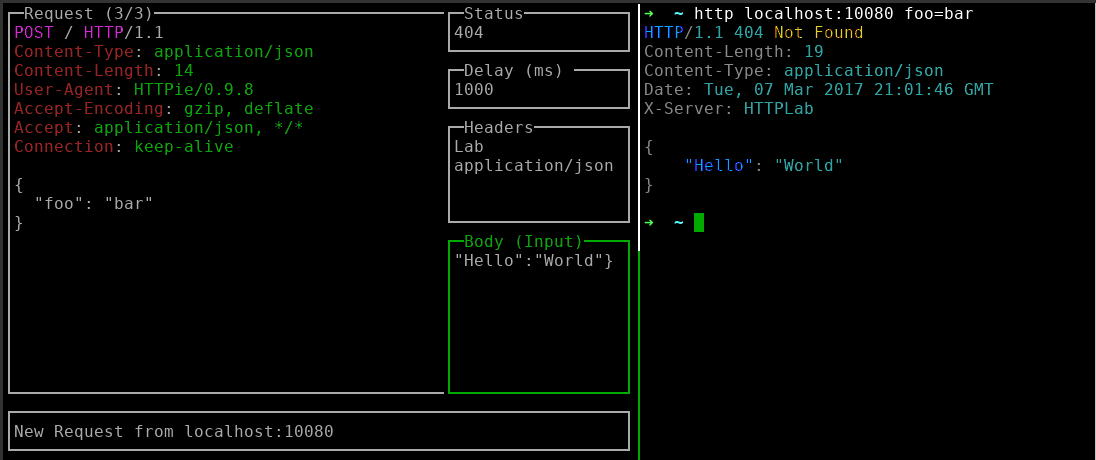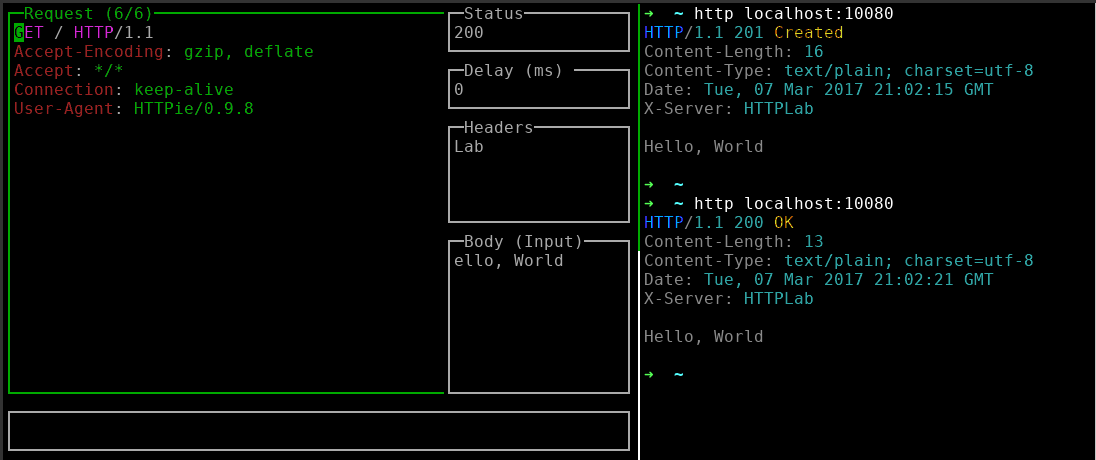 qustavo/httplab
Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.
 joanbono/gurp
Burp Commander written in Go
 google/martian
Martian is a library for building custom HTTP/S proxies
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
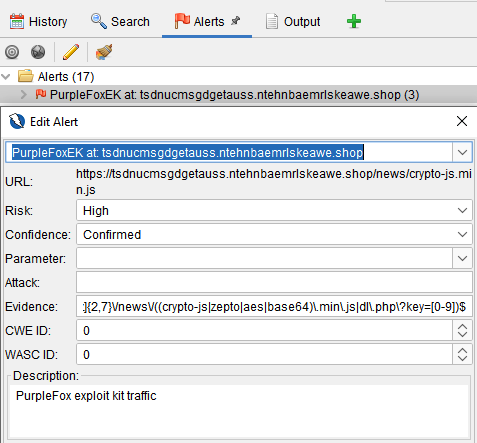 malwareinfosec/fiddlezap
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
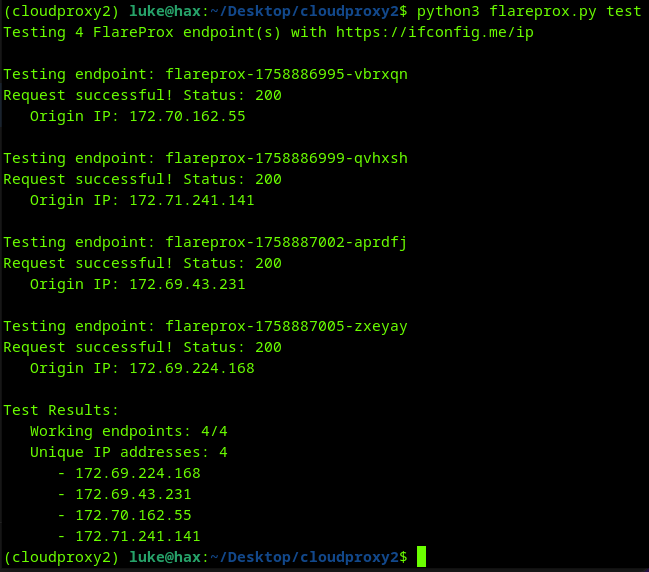 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
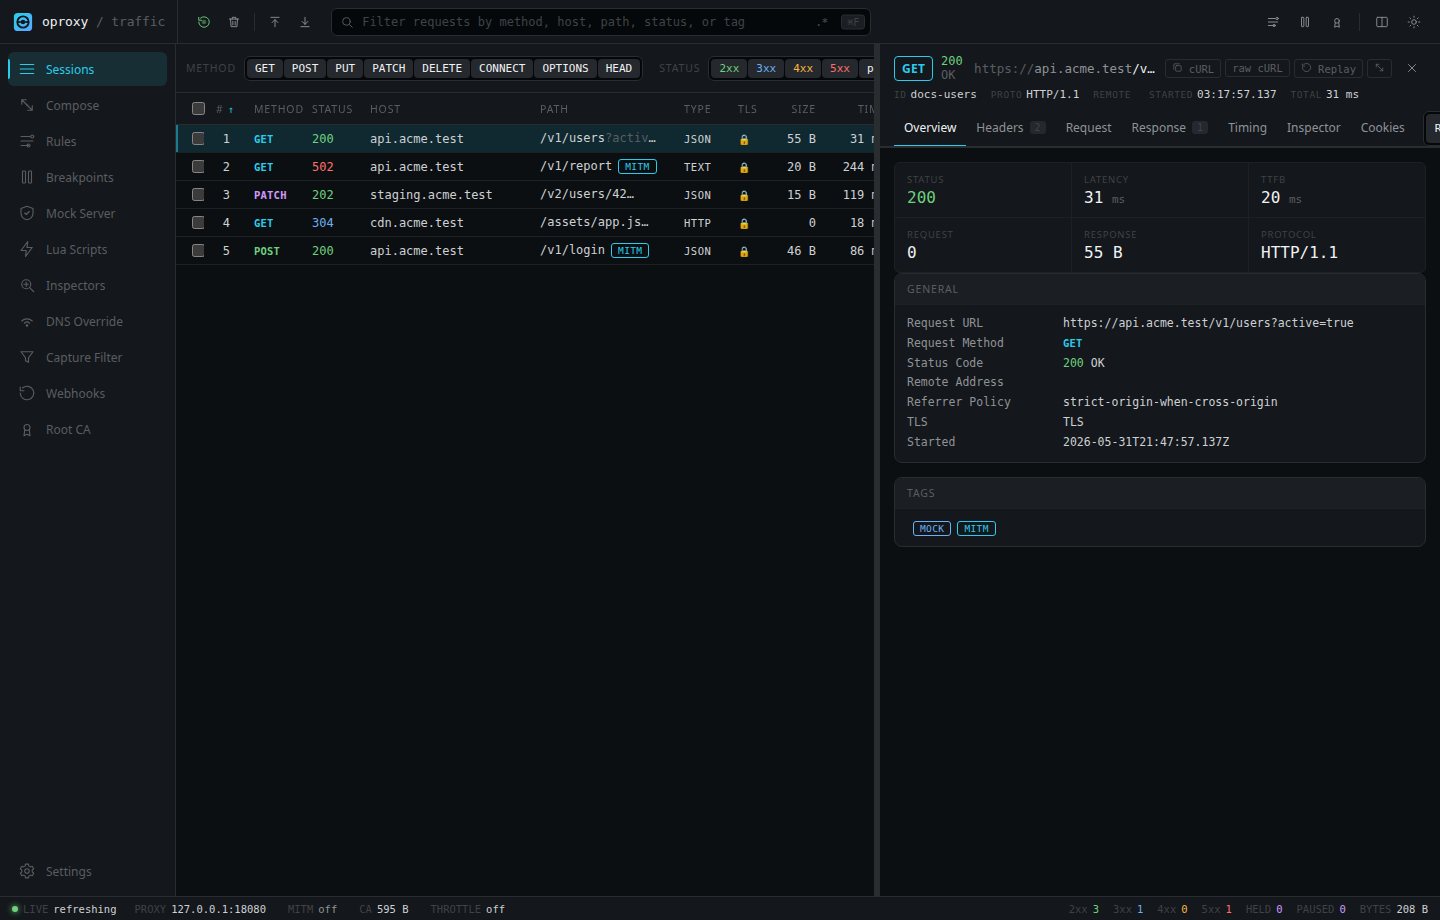 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
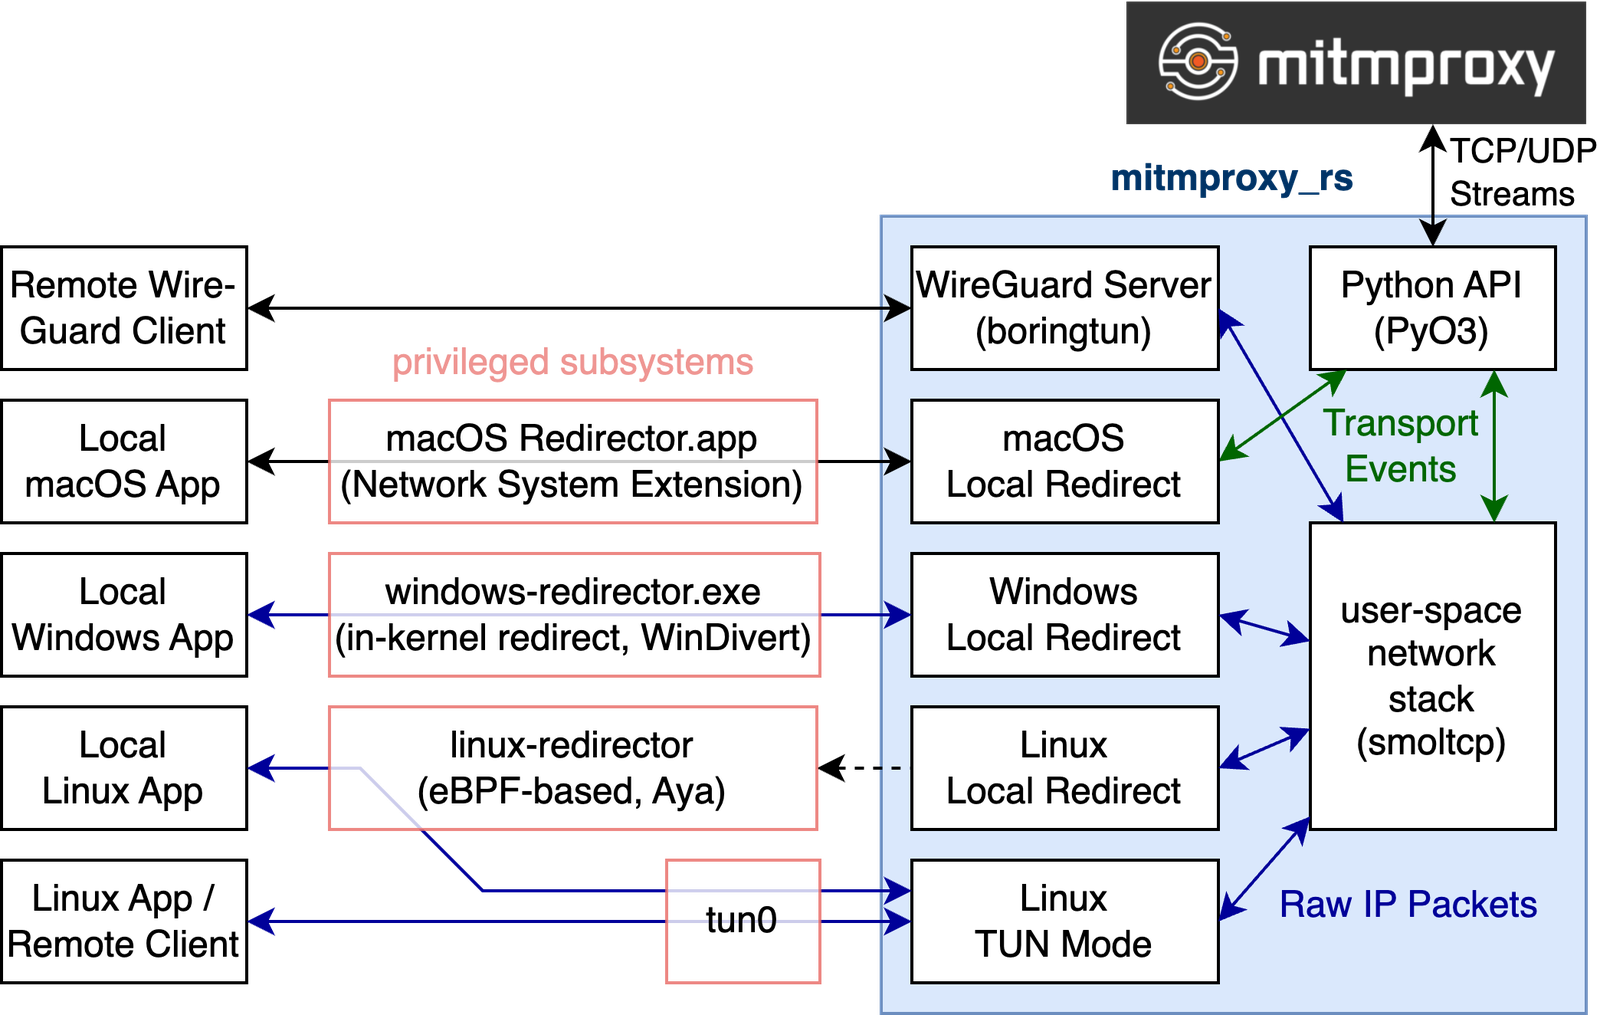 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 ebryx/aes-killer
Burp Plugin to decrypt AES encrypted traffic on the fly
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…