

Gurp
 joanbono/gurp
Burp Commander written in Go
api-security-testingpenetration-testingweb-proxies-interception
joanbono/gurpBurp Commander written in Go

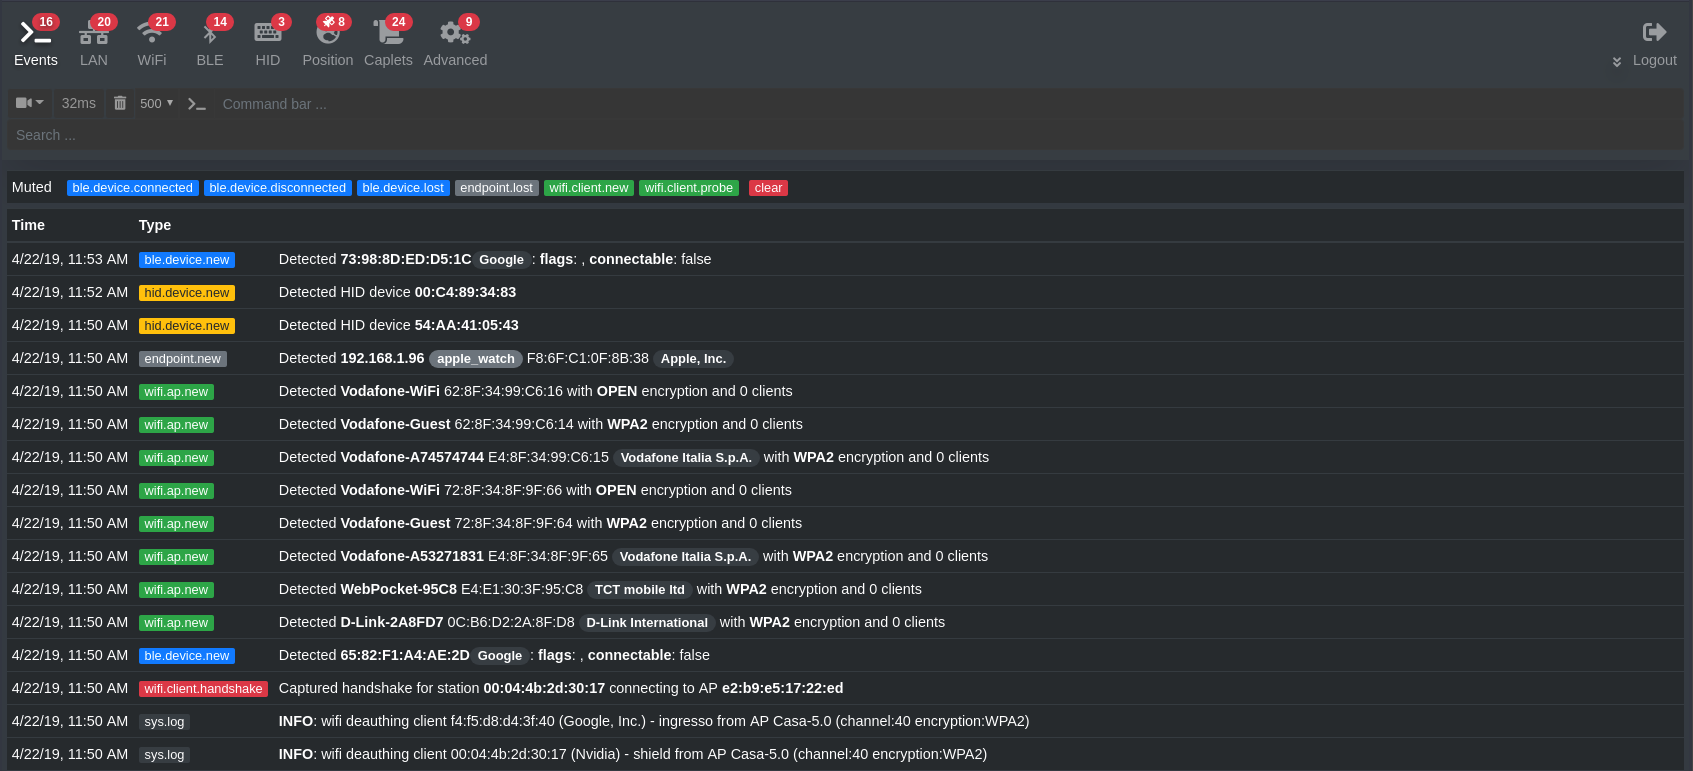 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 torxx666/propox
High-performance Rust HTTP/HTTPS proxy with active defense: rate limiting, reputation-based access, WAF (anti-bot, anti-injection, path protection),…