
ycsm
 infosecn1nja/ycsm
This is a quick script installation for resilient redirector using nginx reverse proxy and letsencrypt compatible with some popular Post-Ex Tools…
anti-botcommand-and-controlids-ips-evasion+2
86
infosecn1nja/ycsmThis is a quick script installation for resilient redirector using nginx reverse proxy and letsencrypt compatible with some popular Post-Ex Tools…
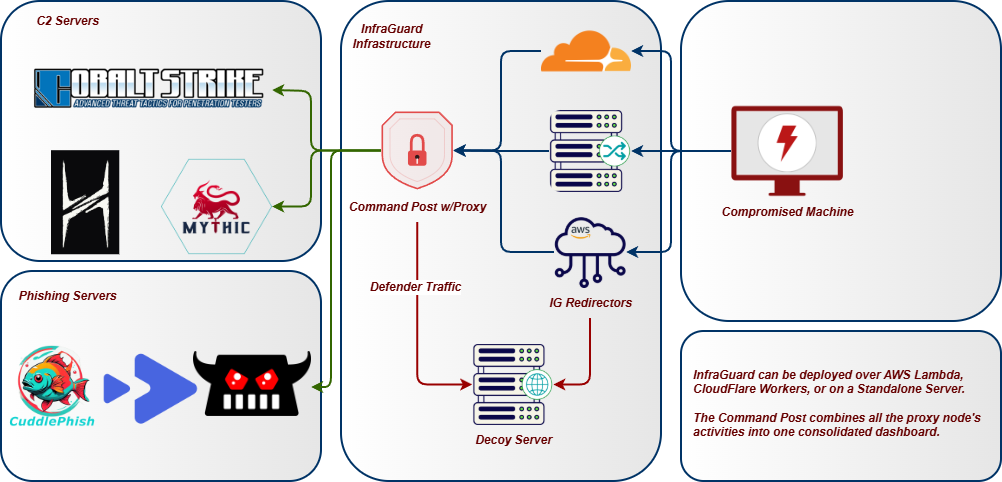 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.
 hahwul/webhackersweapons
⚔️ Web Hacker's Weapons / A collection of cool tools used by Web hackers. Happy hacking , Happy bug-hunting
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 synacktiv/hopla
HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite
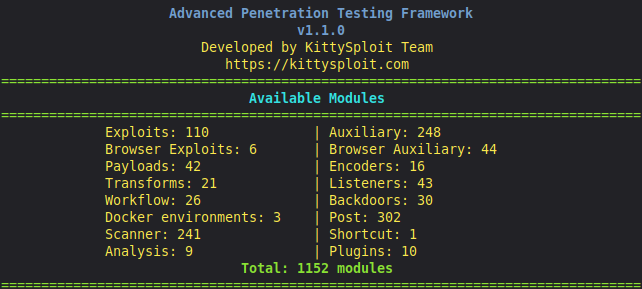 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 ryhanson/externalc2
A library for integrating communication channels with the Cobalt Strike External C2 server
 wofeiwo/webcgi-exploits
Multi-language web CGI interfaces exploits.
 xorrior/raven
CobaltStrike External C2 for Websockets
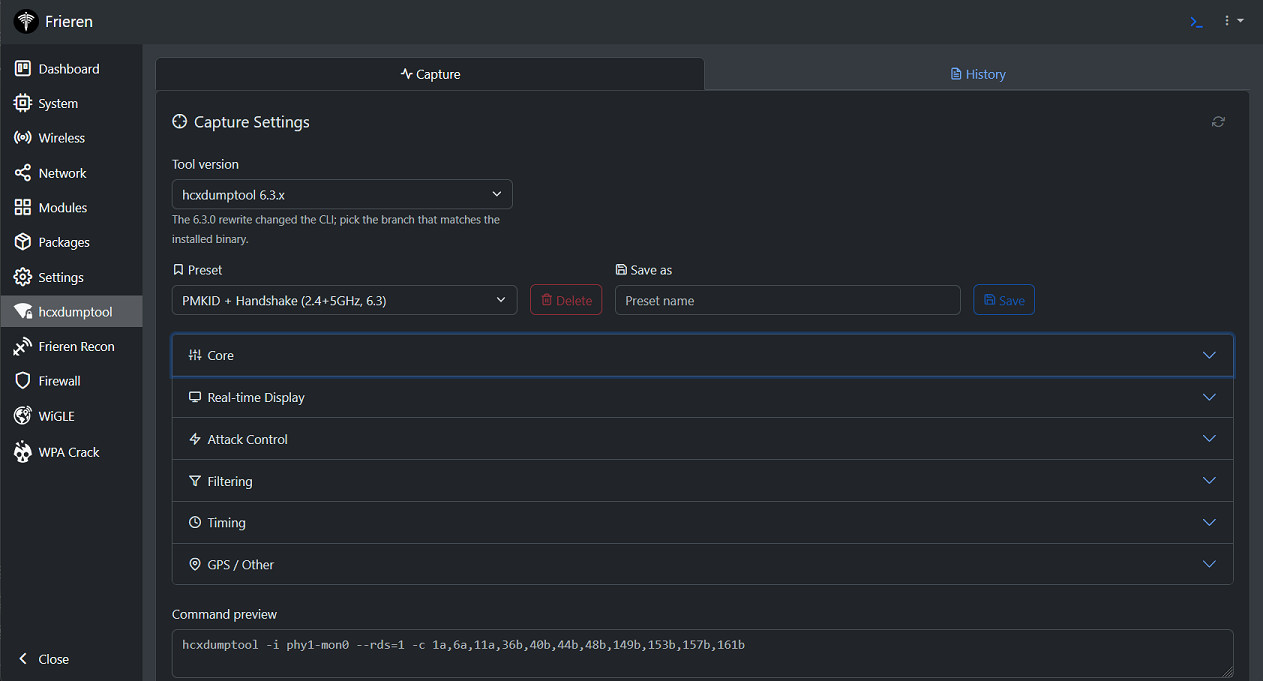 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
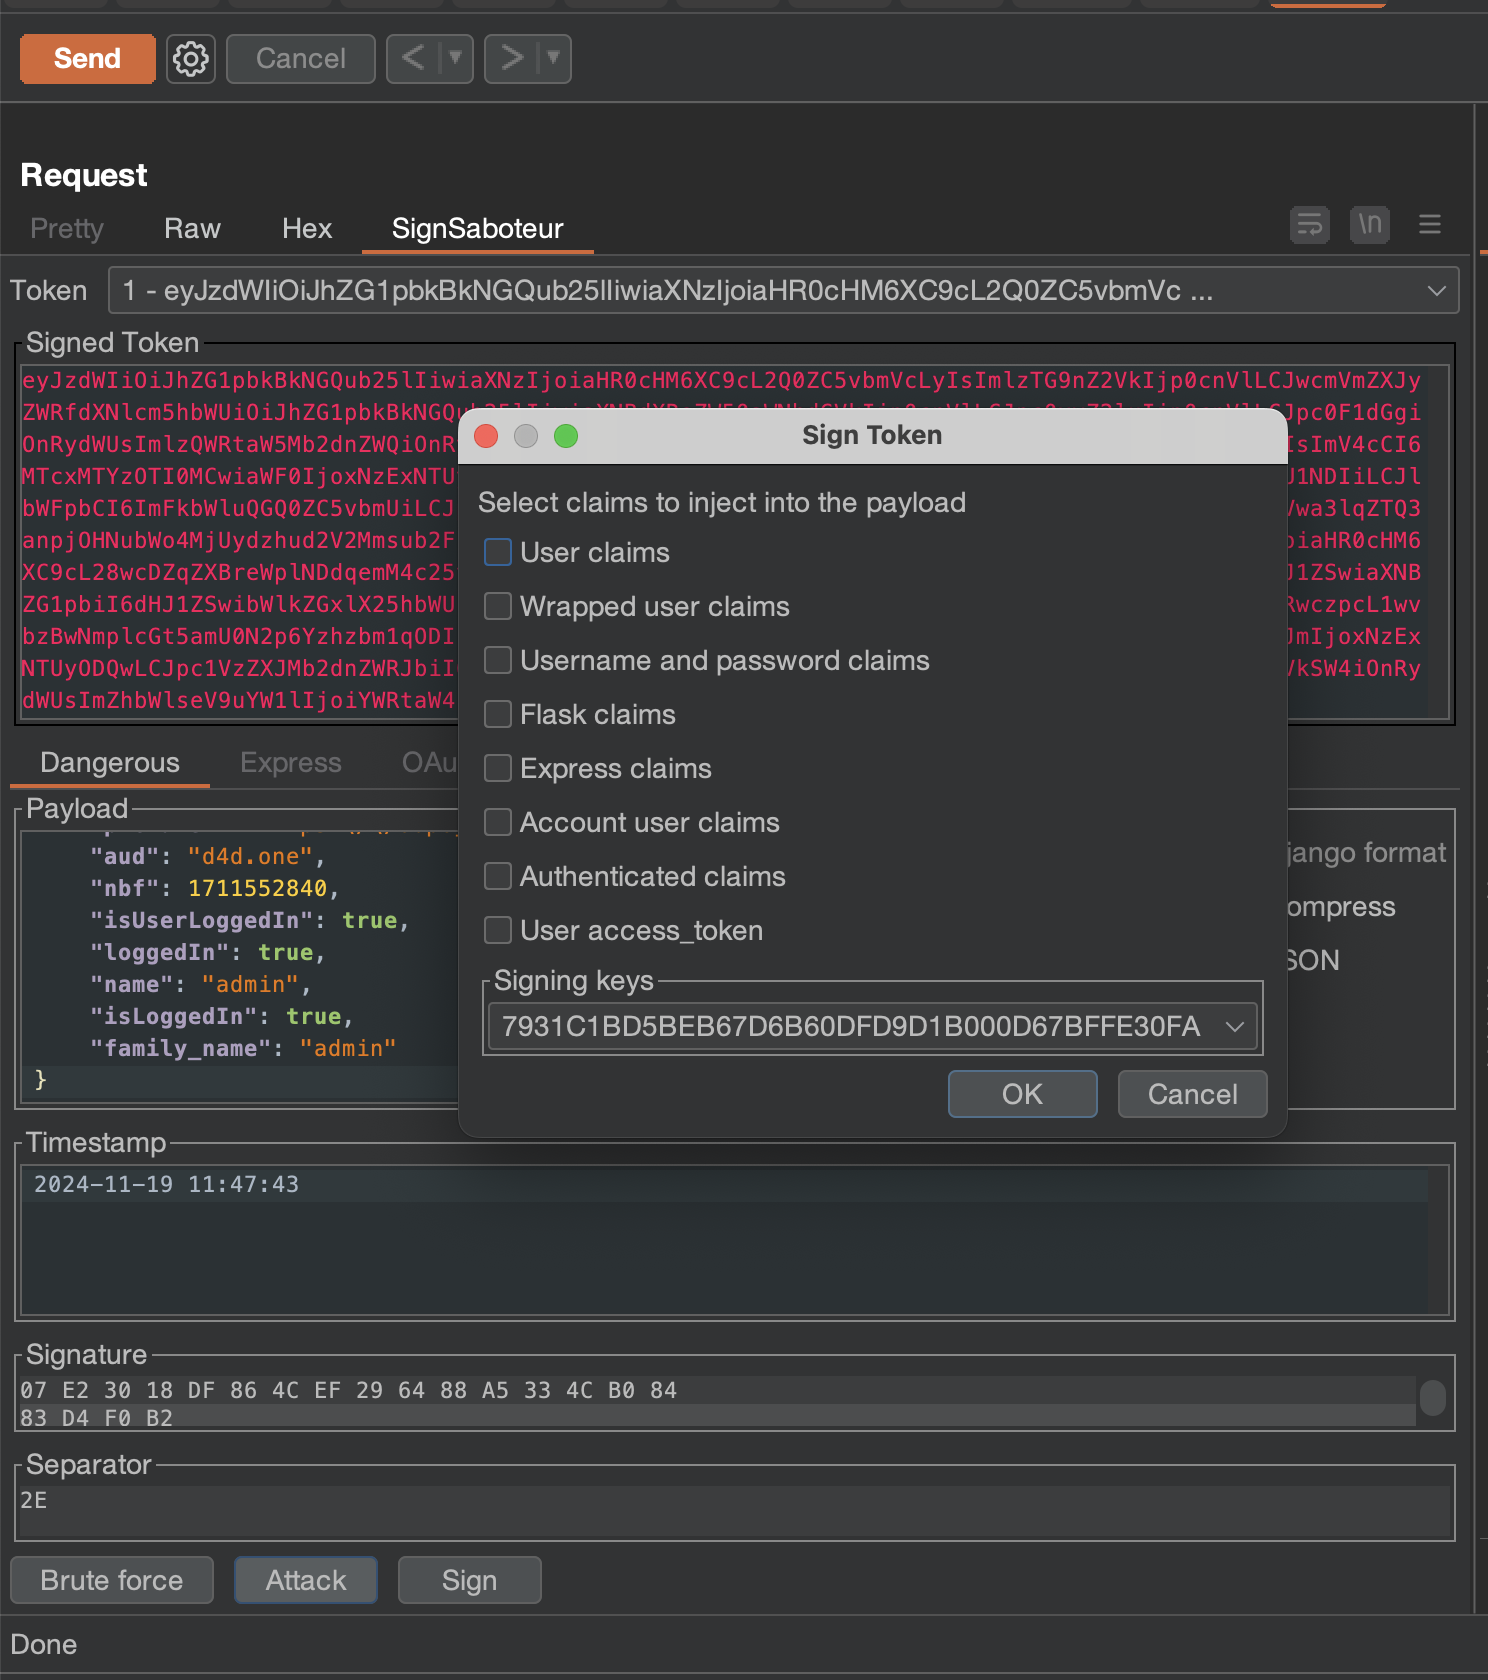 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens