
evilwaf
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
fingerprint-spoofinginformation-gatheringosint+6
894
matrixleons/evilwafevilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
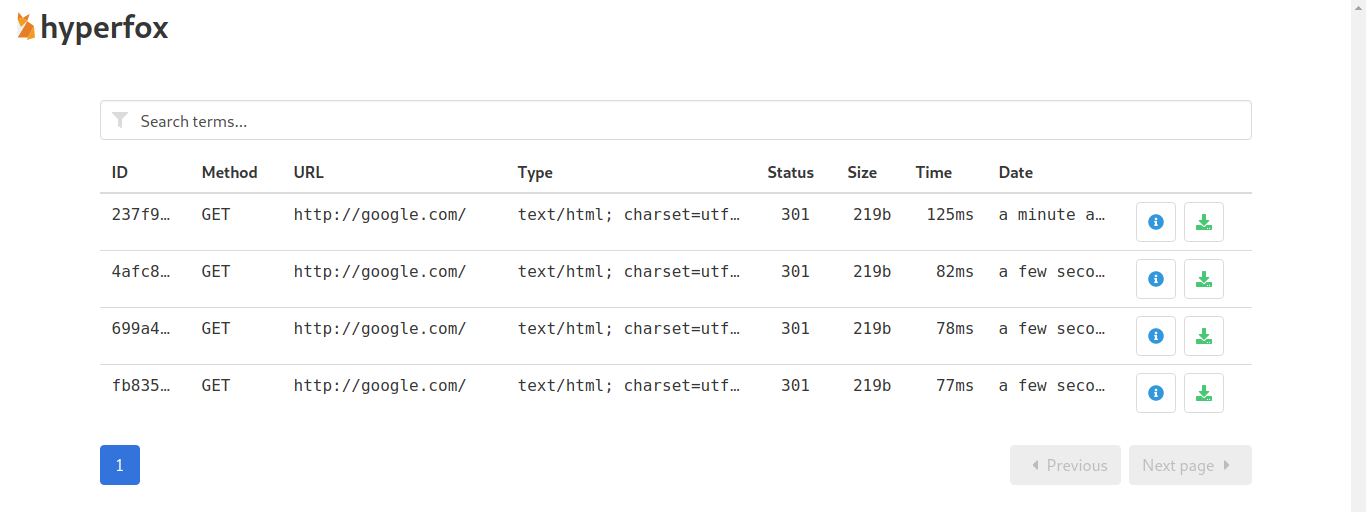 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua

 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
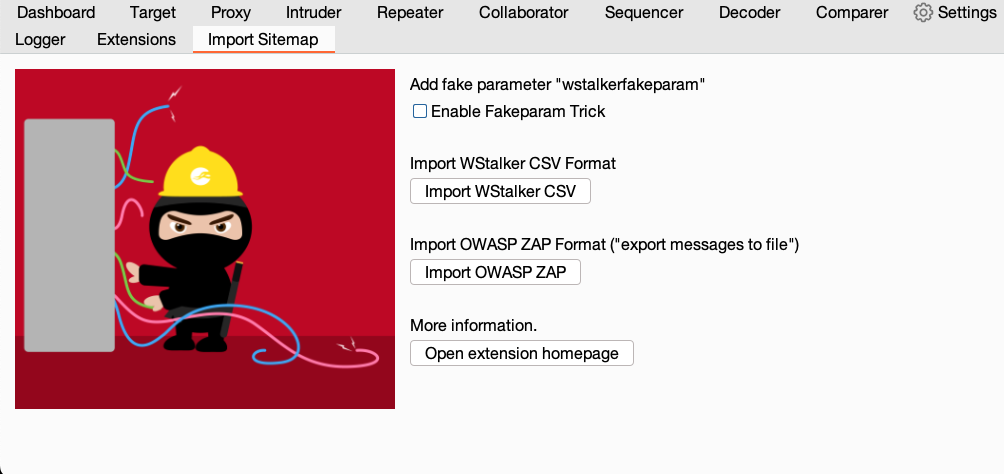 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…