
evilgrade
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
dns-analysisexploit-frameworkspayload-generation+4
1.3k
infobyte/evilgradeEvilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 justmao945/mallory
HTTP/HTTPS proxy over SSH
 inaz2/proxy2
HTTP/HTTPS proxy in a single python script
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
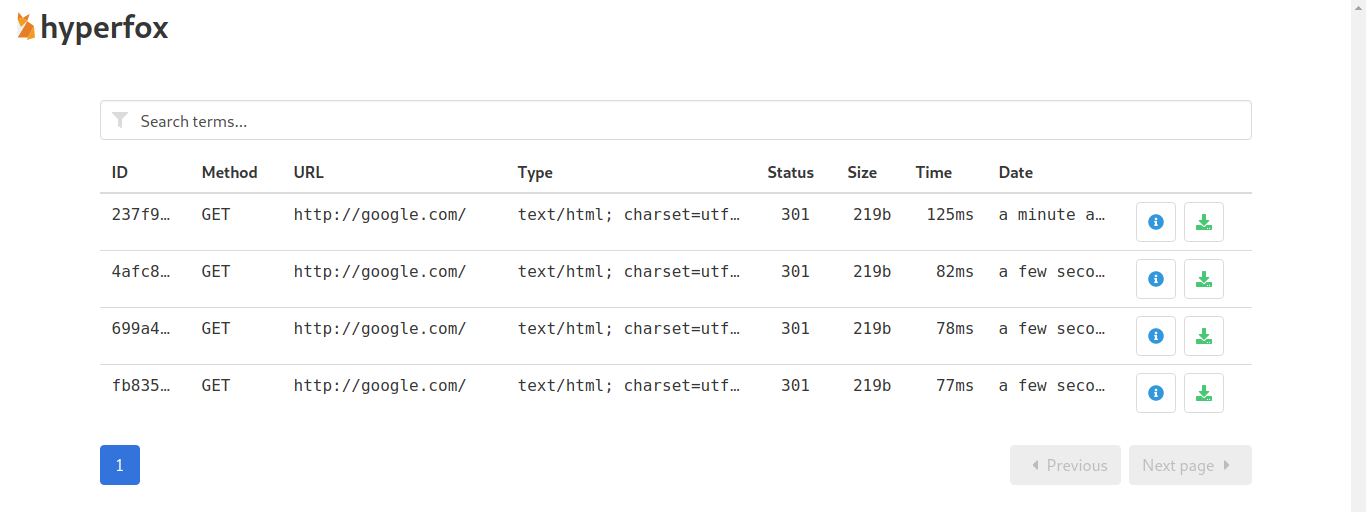 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.
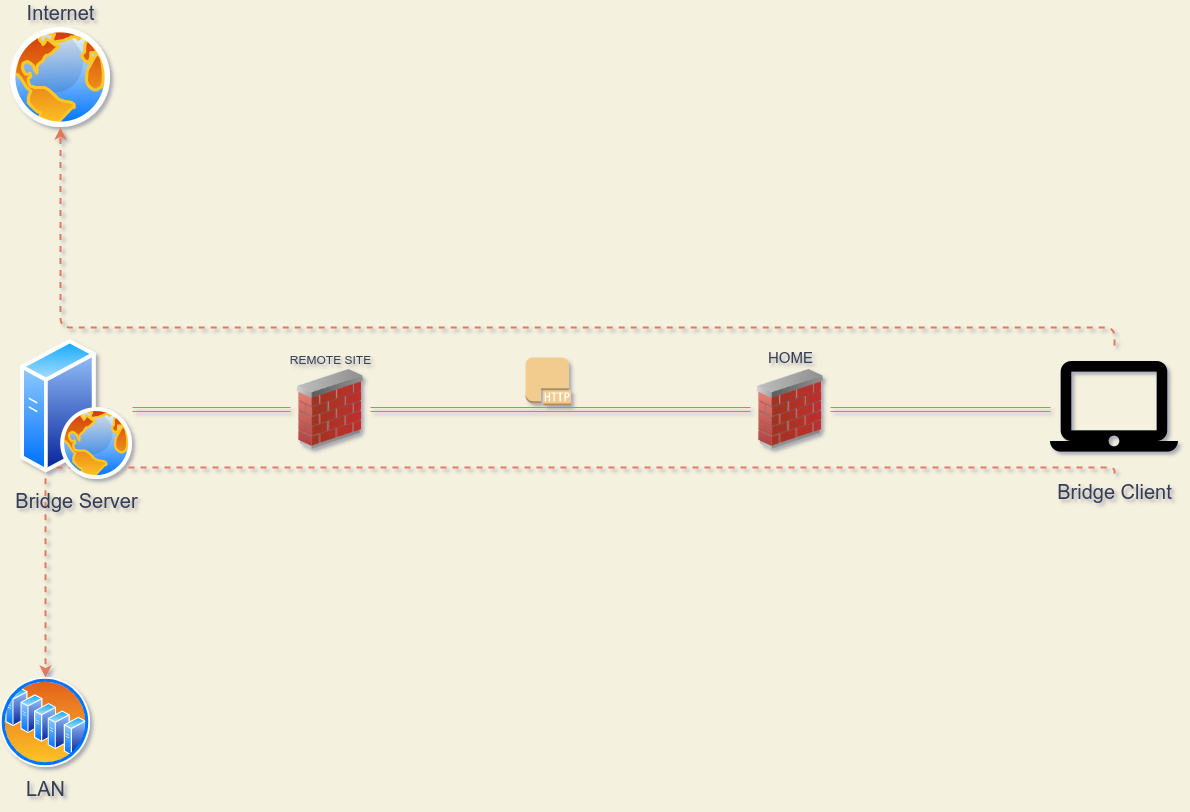 alejandro-llanes/http_bridge
SOCKS5-to-HTTP proxy bridge that tunnels arbitrary TCP streams (SSH, SMTP, TLS) through standard HTTP requests, enabling network traffic obfuscation…