
pentest-pivoting
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
ctfcurated-resourceseducation+5
228
t3l3machus/pentest-pivotingA compact guide to network pivoting for penetration testings / CTF challenges.
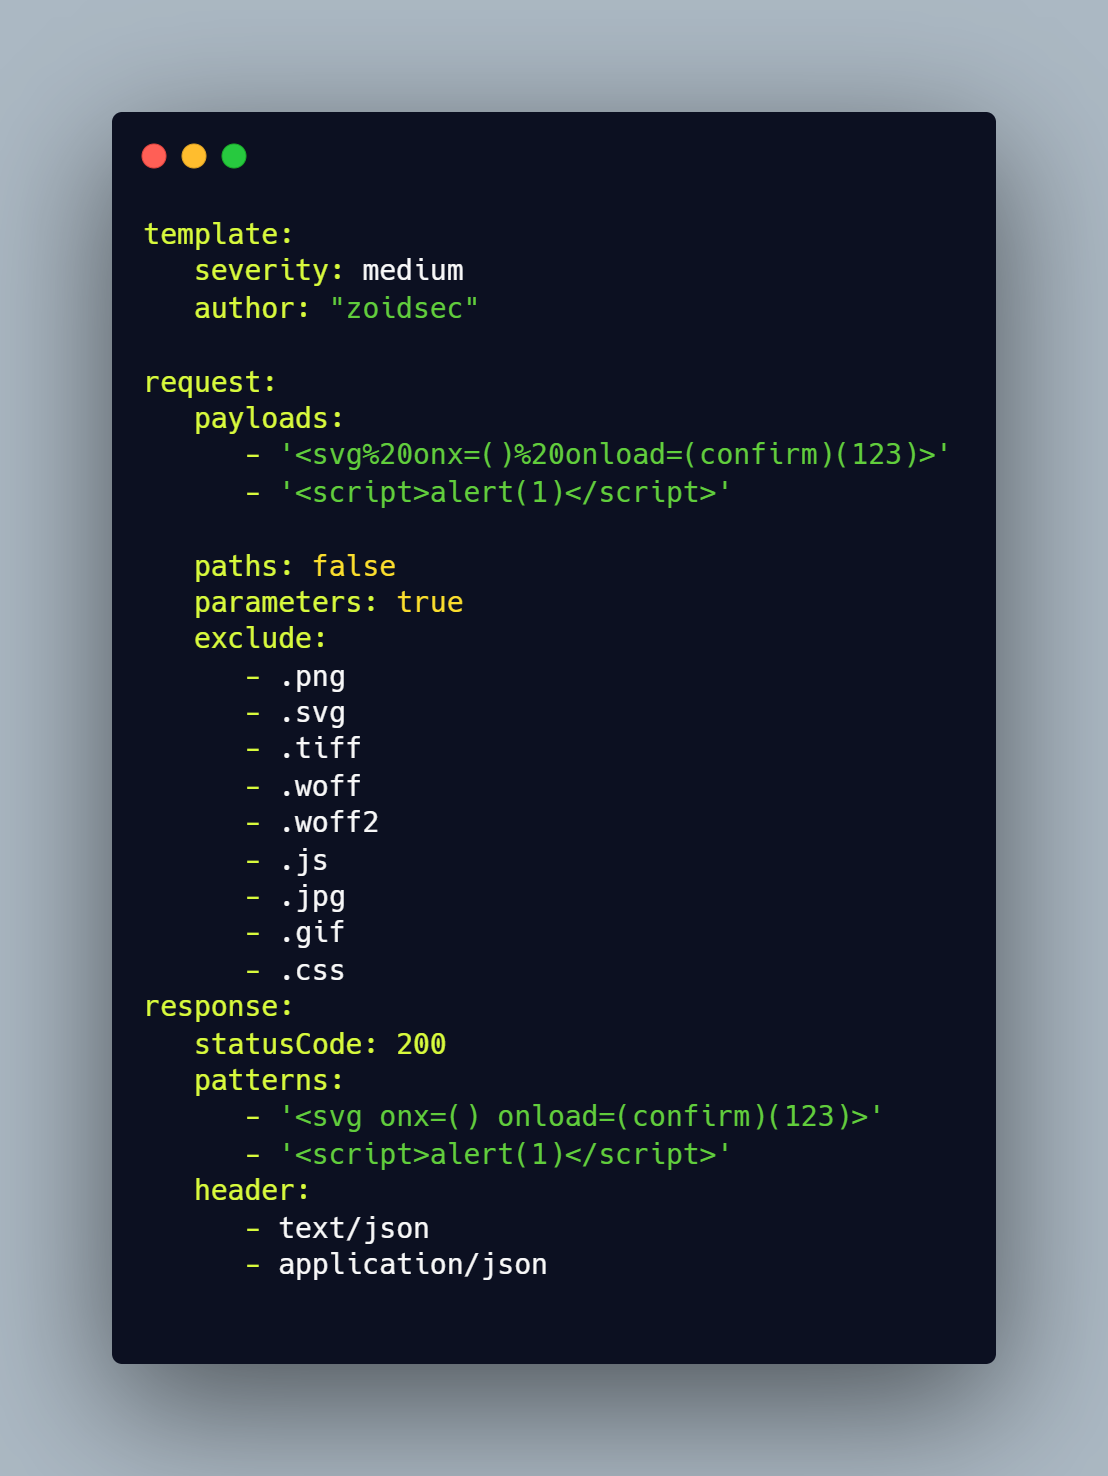 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 argos83/ritm
Ruby In The Middle (HTTP/HTTPS interception proxy)
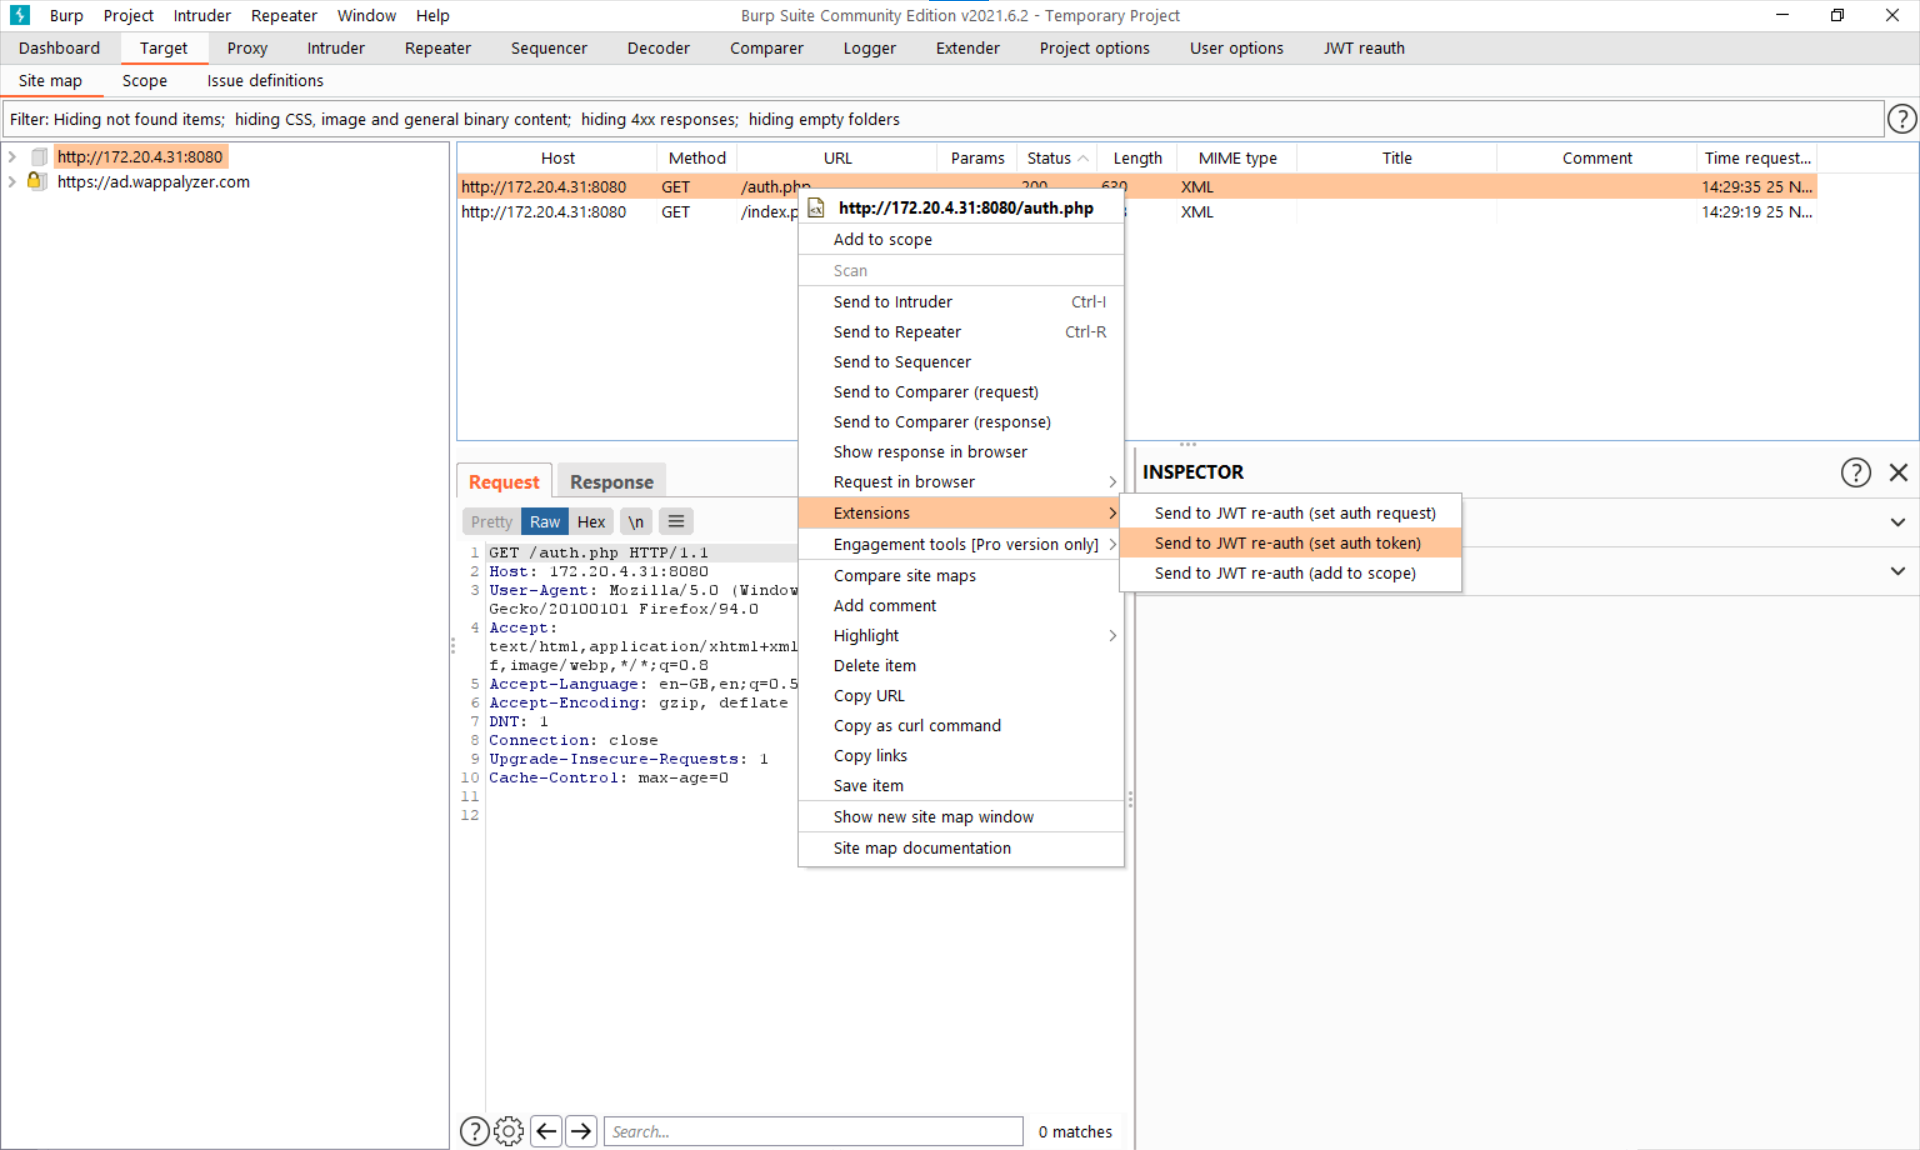 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 mthbernardes/houseproxy
Protect your parents from phishing
 mrschyte/socksmon
Monitor arbitrary TCP traffic using your HTTP interception proxy of choice
 michele0303/undetected-httpx
Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
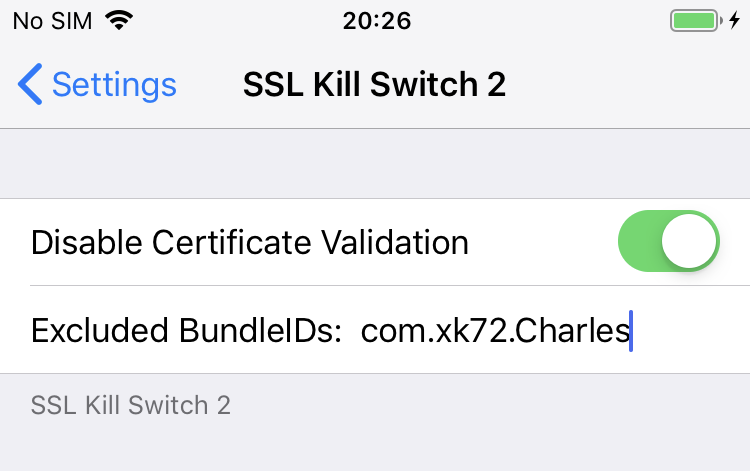 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 nyamisty/ssl-kill-switch3
Next Generation SSLKillSwitch with much more support!
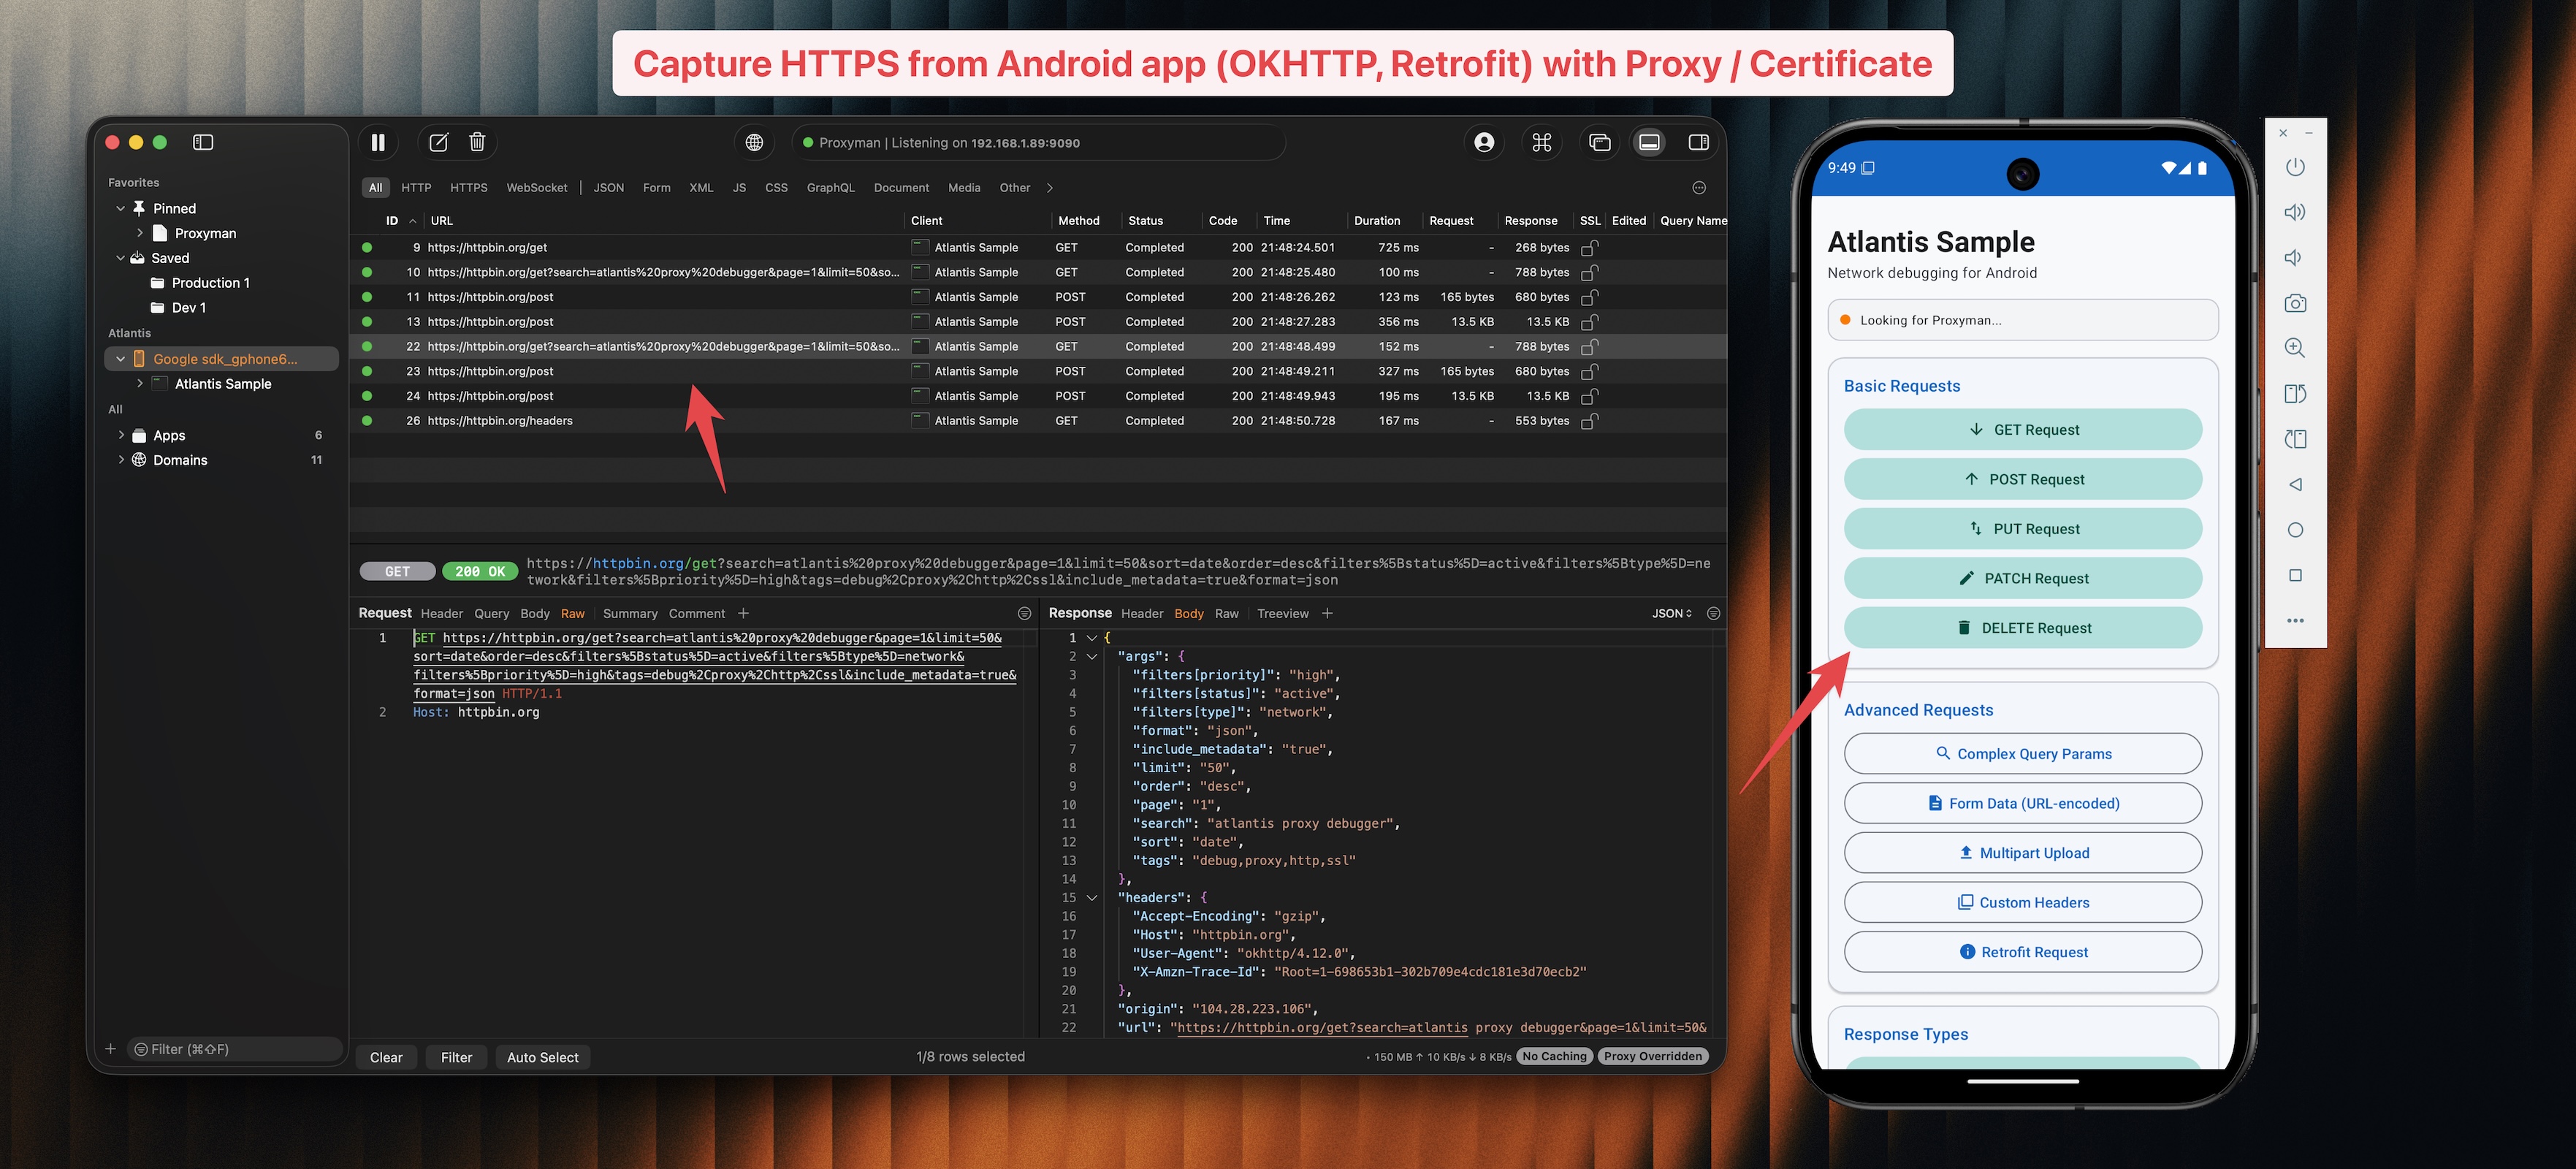 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
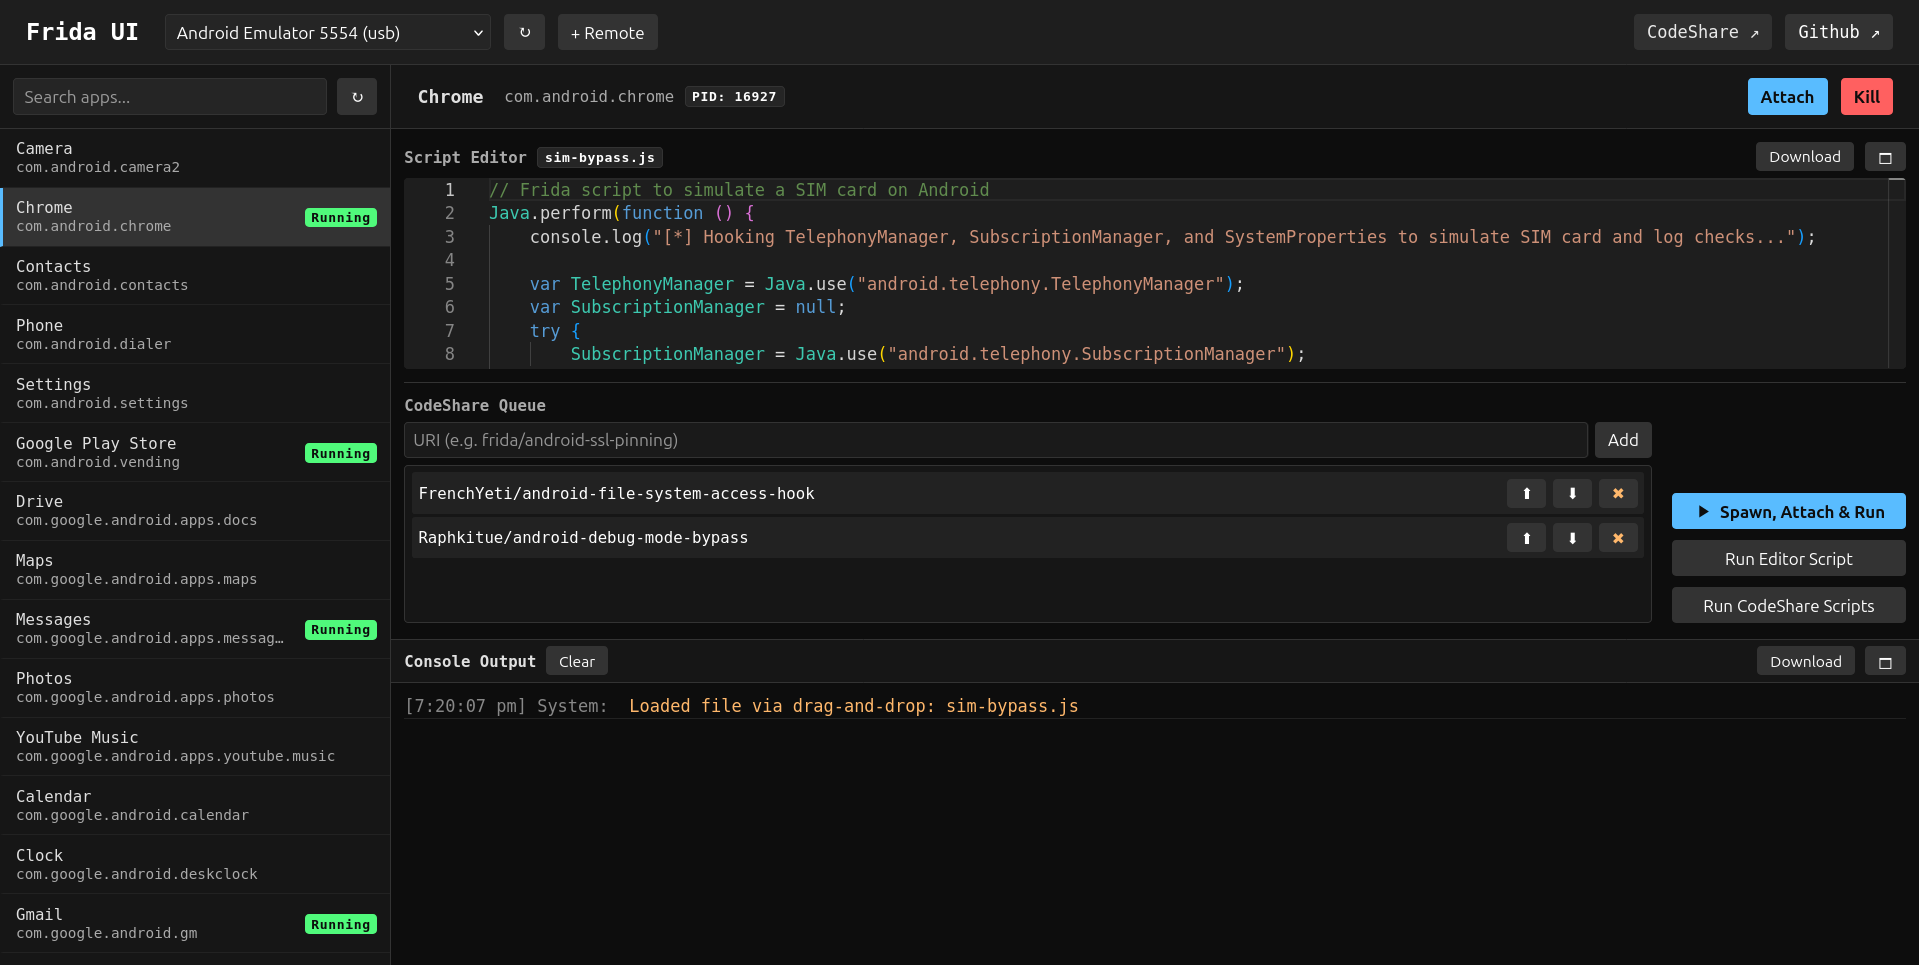 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.