

yakit
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.7k
yaklang/yakitAll-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
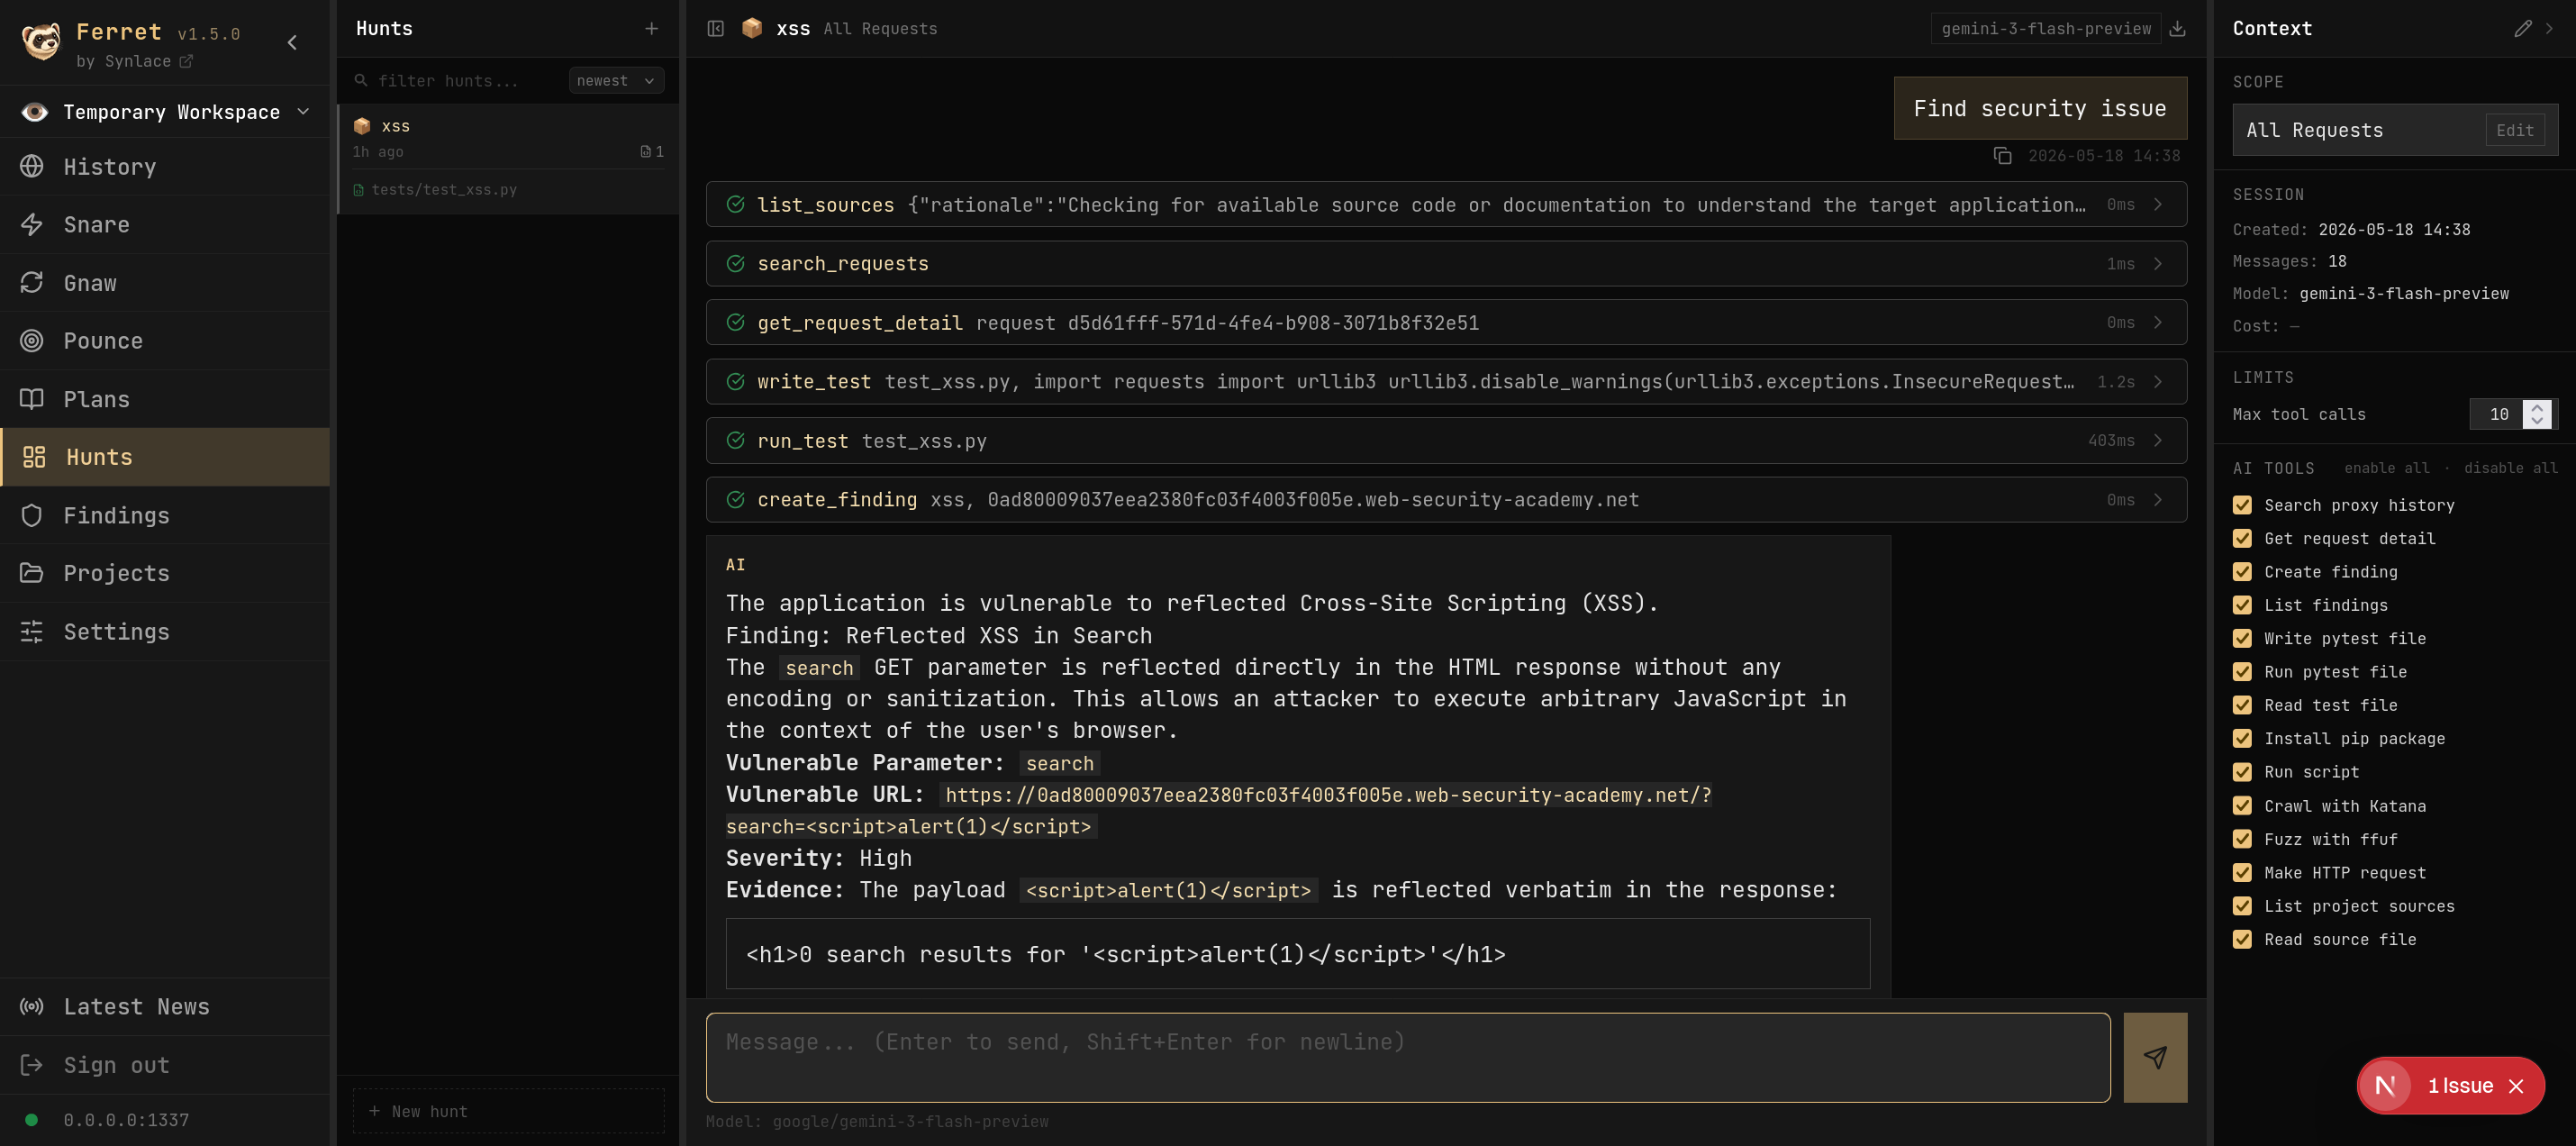 synlace/ferret
The collaborative web app pentest suite
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
 yeswehack/pwnfox
Firefox/Burp extension for security audits with single-click proxy, container profiles, postMessage logging, JS injection toolbox, and security…
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 johndoe31415/ratched
Ratched is a transparent Man-in-the-Middle TLS proxy intended for penetration testing
 joanbono/gurp
Burp Commander written in Go