

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.8k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 torxx666/propox
High-performance Rust HTTP/HTTPS proxy with active defense: rate limiting, reputation-based access, WAF (anti-bot, anti-injection, path protection),…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
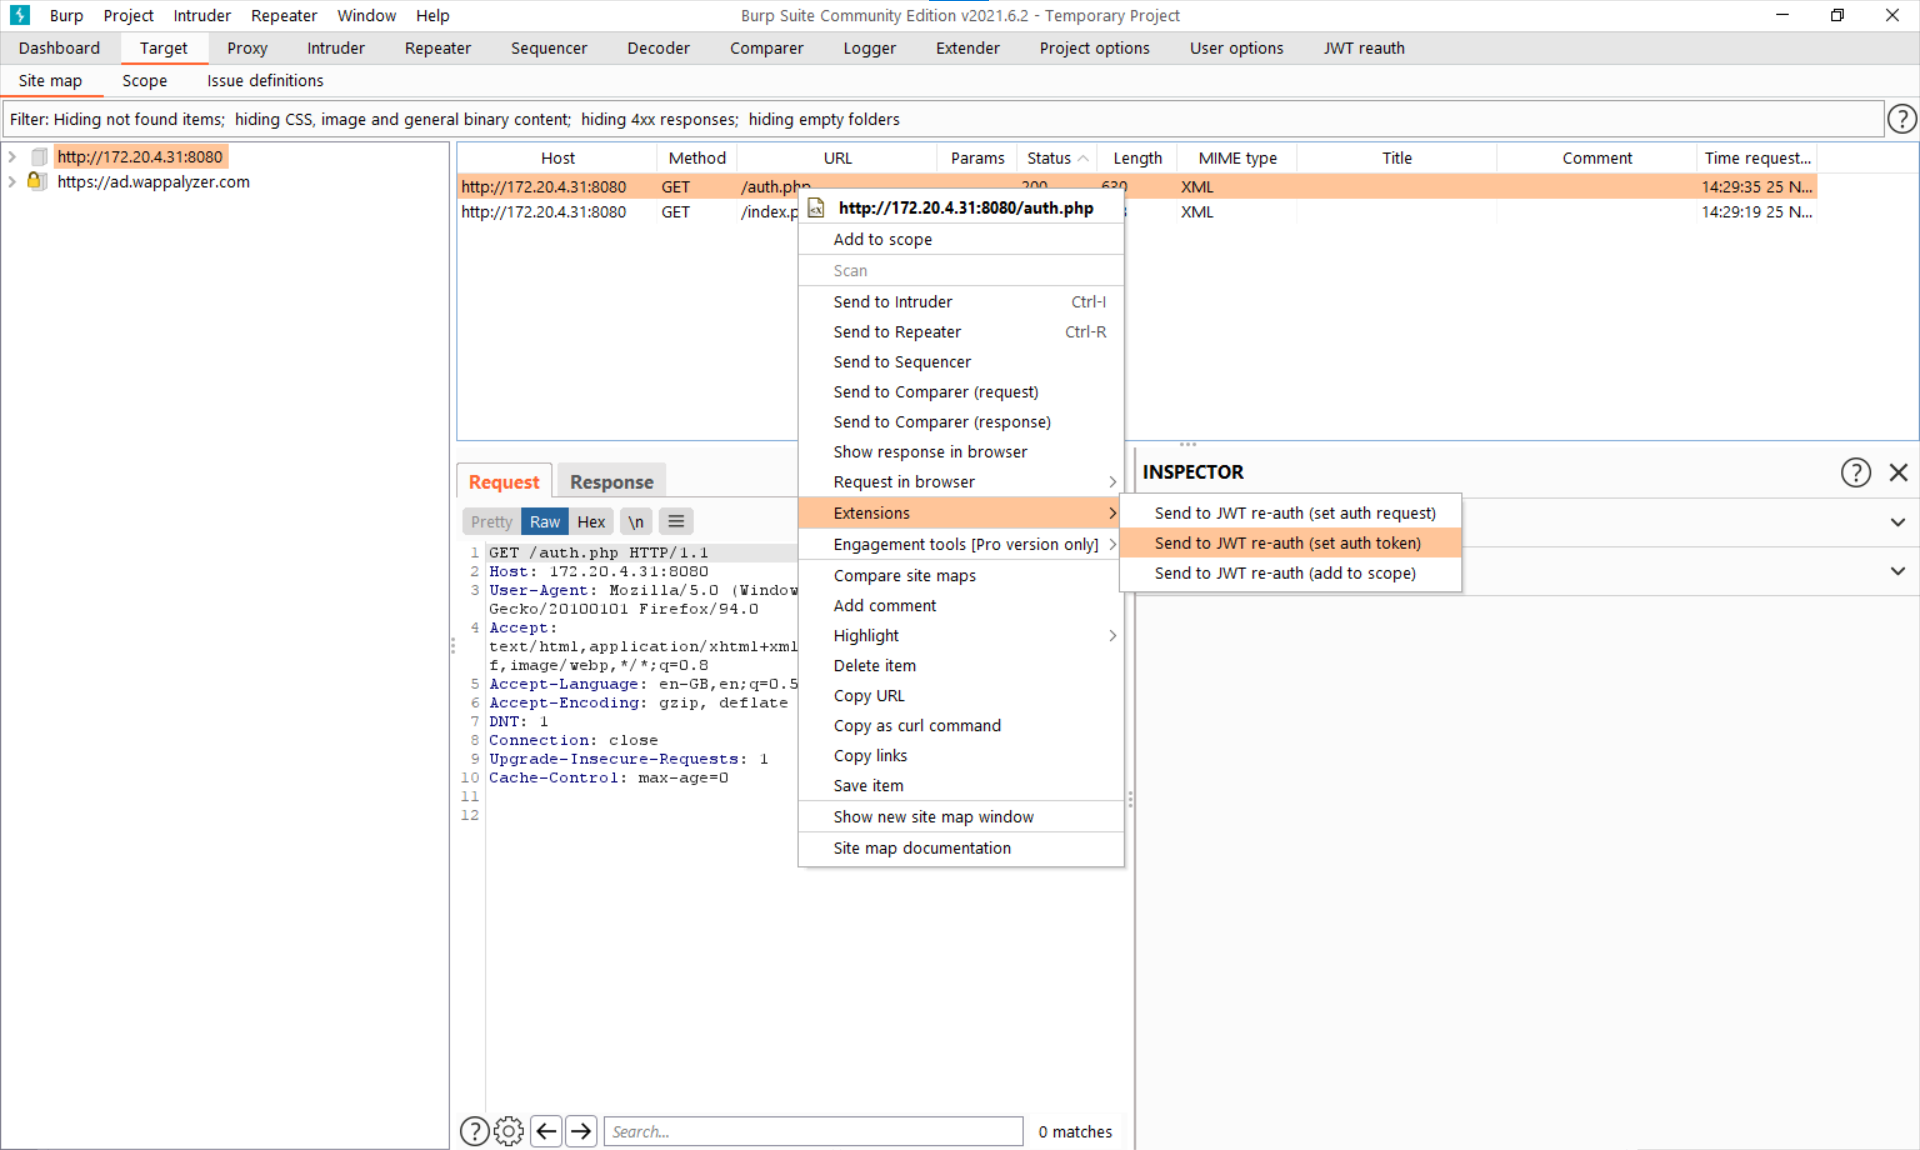 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
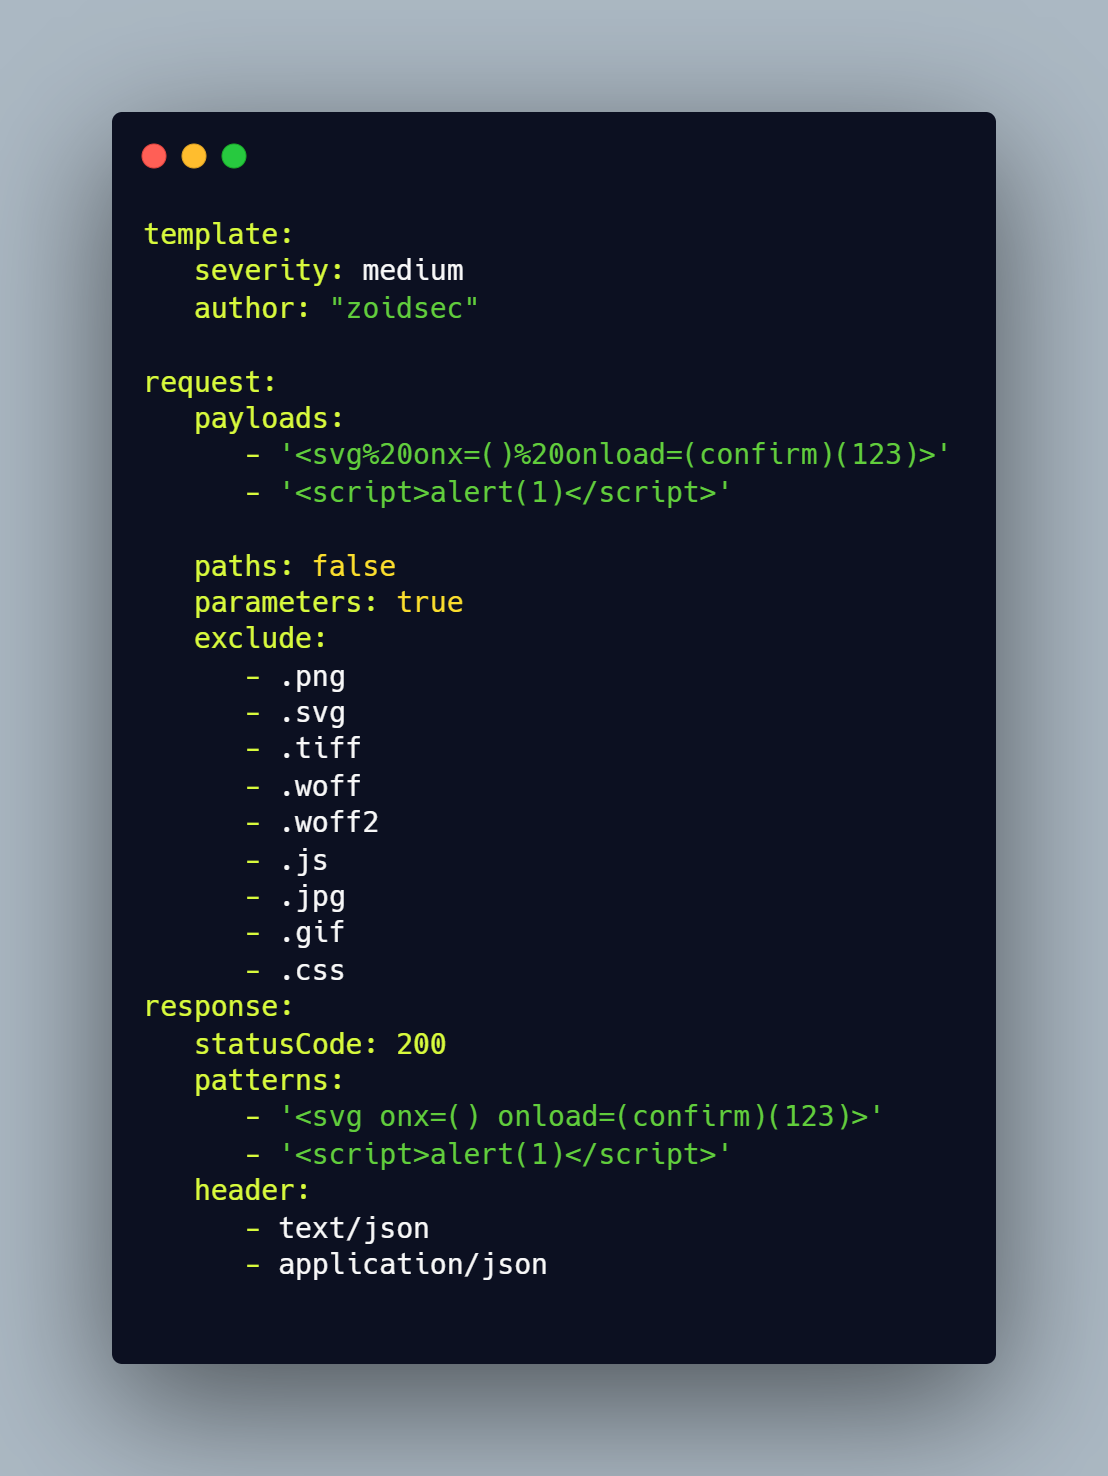 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 ianxtianxt/proxysqlmap
From Proxy to SqlMapApi
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
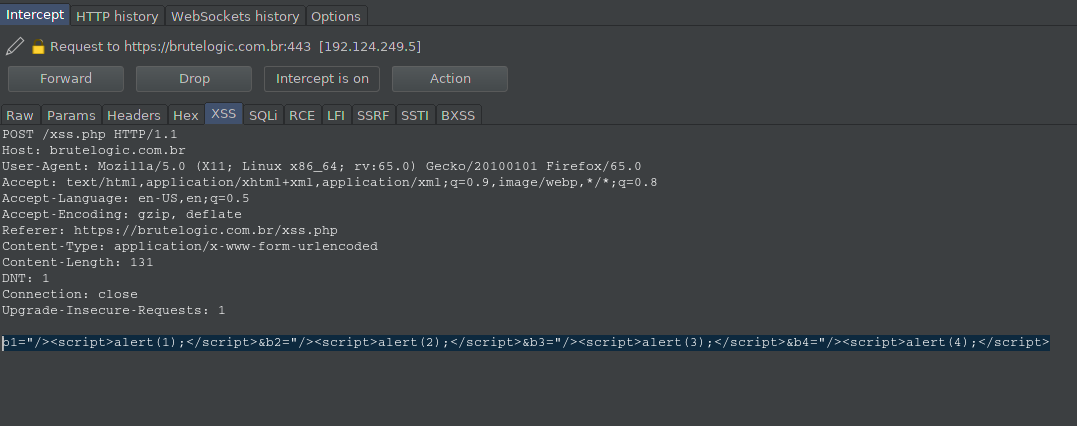 p3n73st3r/ghazi
Ghazi is a BurpSuite Plugins For Testing various PayLoads Like "XSS,SQLi,SSTI,SSRF,RCE and LFI" through Different tabs , Where Each Tab Will Replace…