
qyvora-toha3ee
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
exploitationnetwork-securityosint+9
4
qyvora/qyvora-toha3eeGo-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
 infosecn1nja/ycsm
This is a quick script installation for resilient redirector using nginx reverse proxy and letsencrypt compatible with some popular Post-Ex Tools…
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 v1v1/sleight
Empire HTTP(S) C2 redirector setup script
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
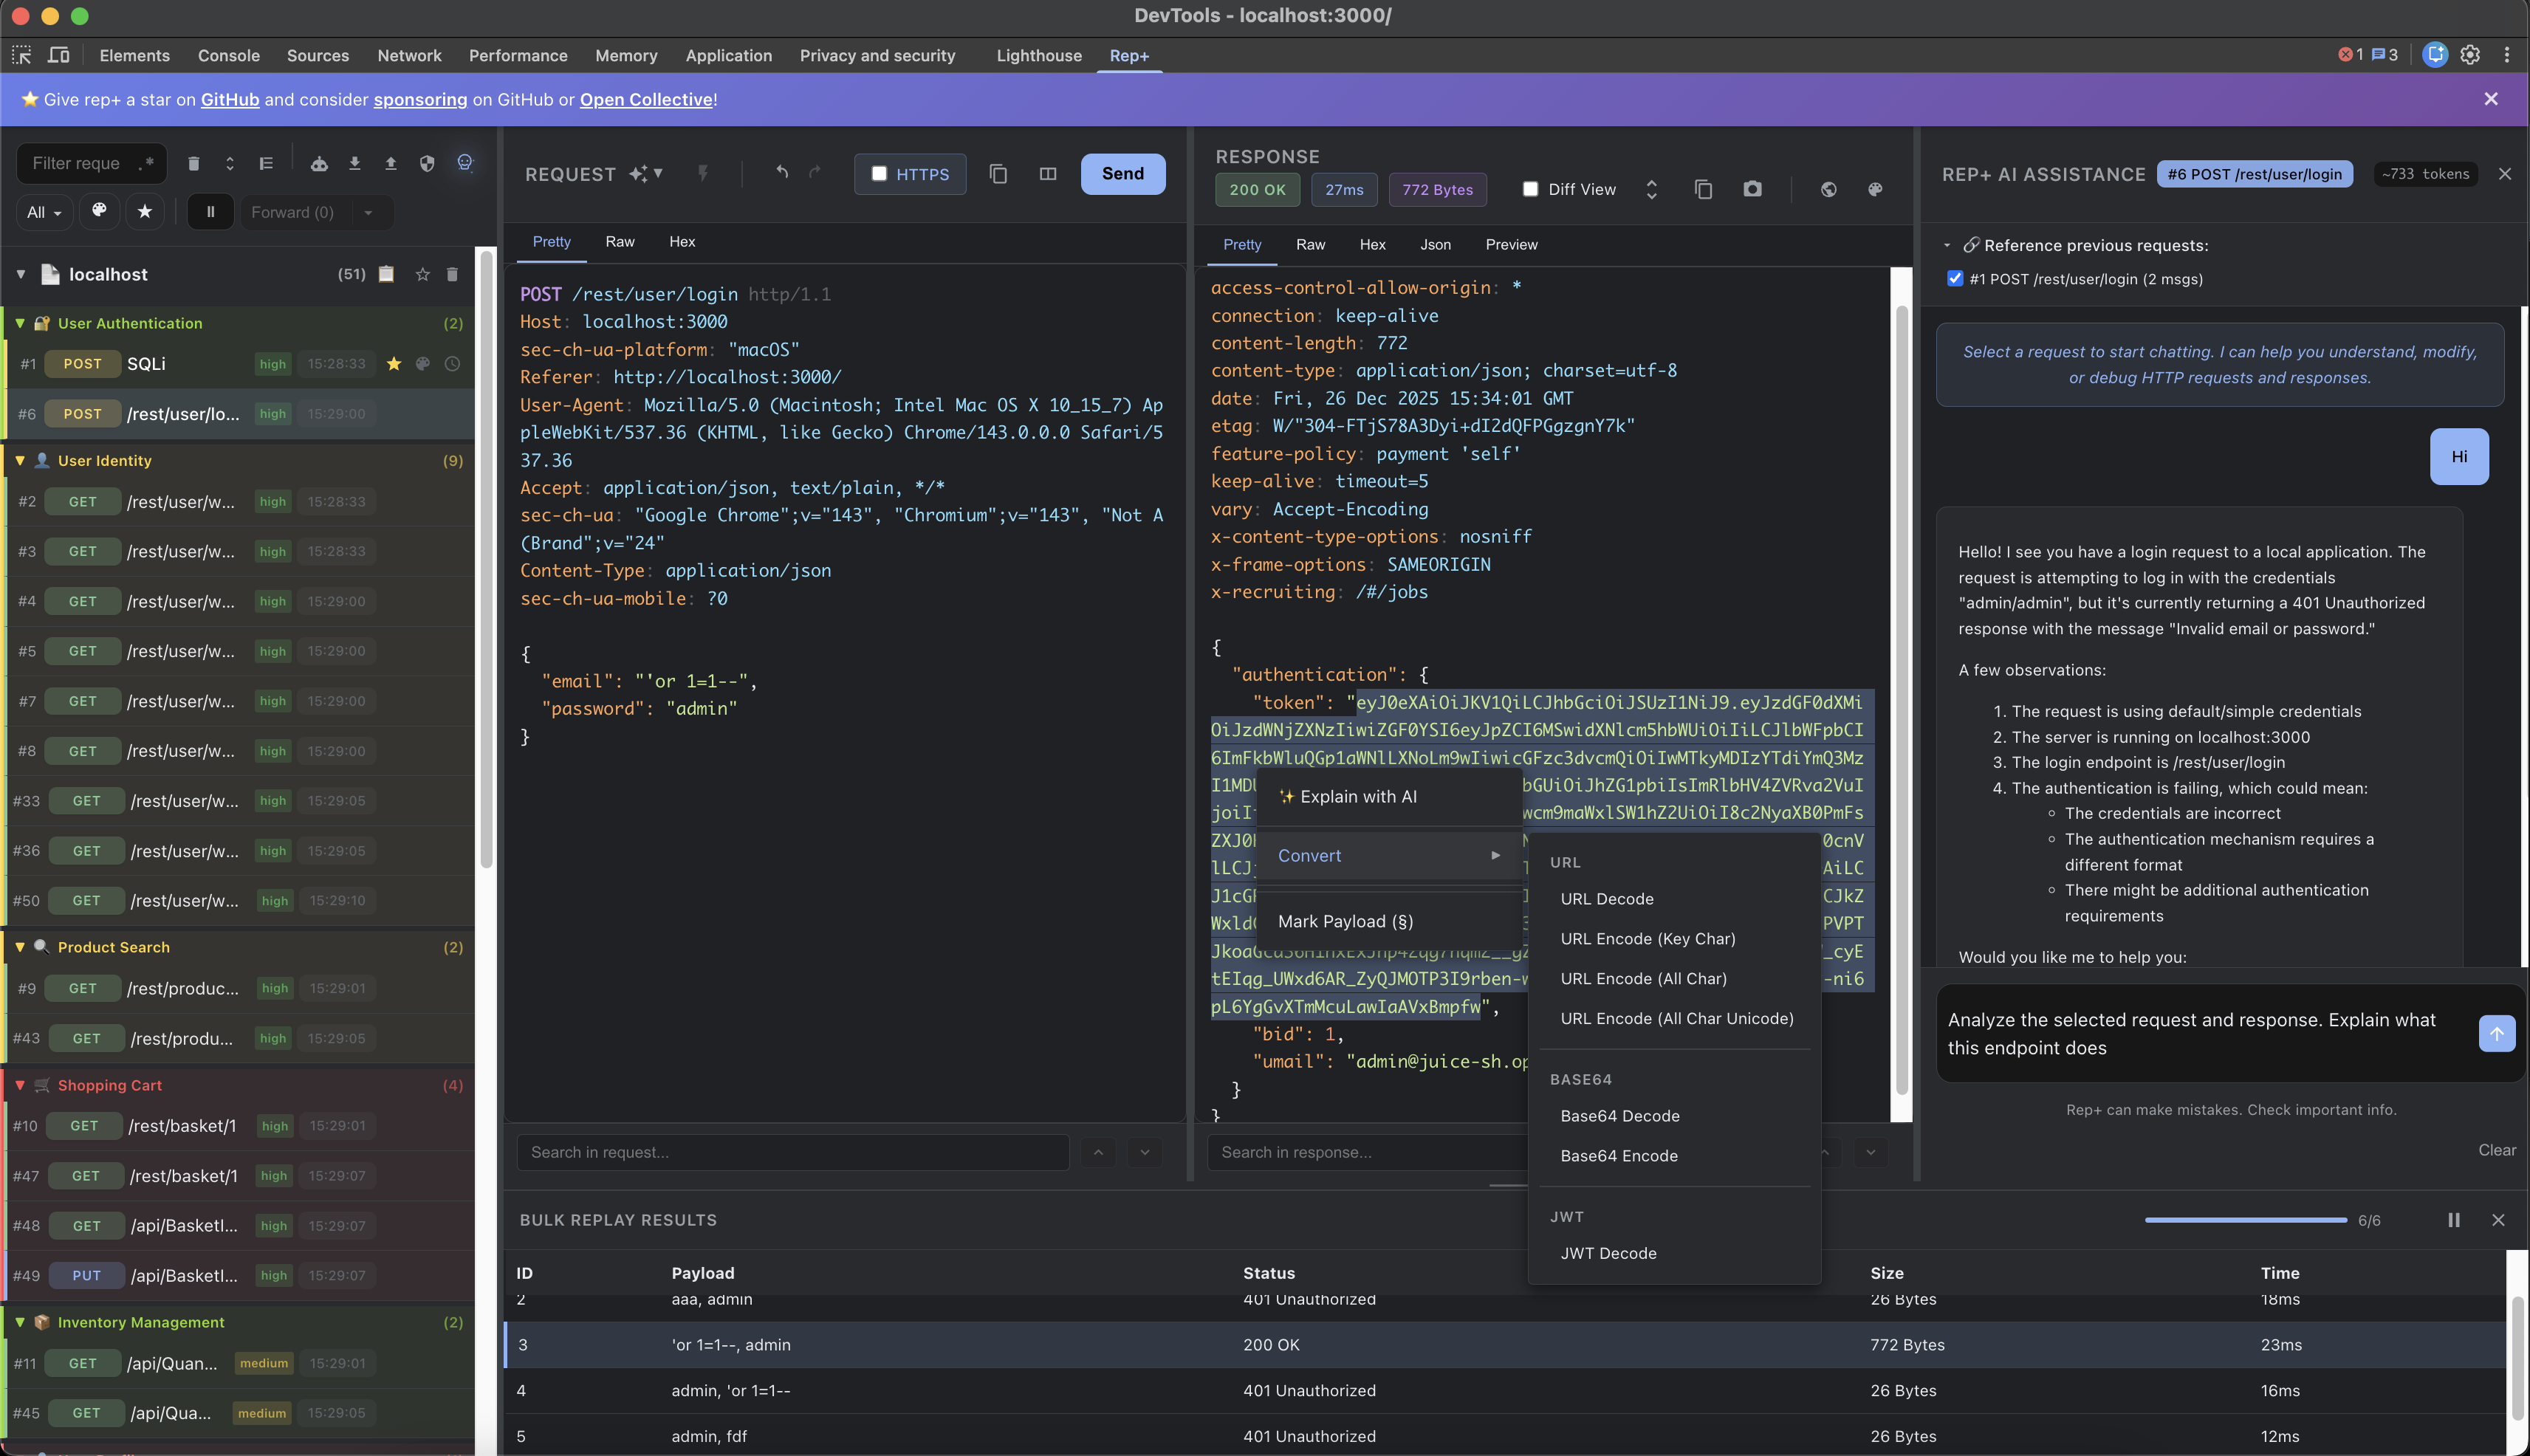 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
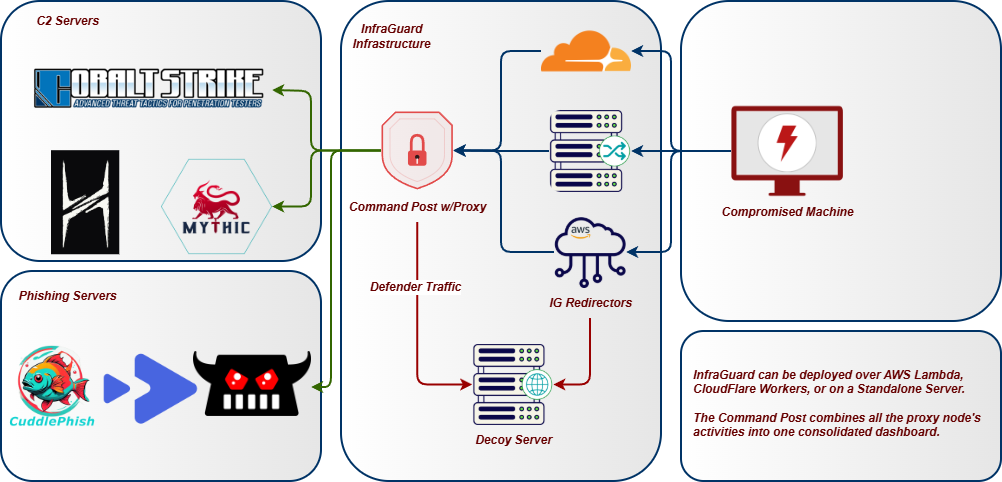 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
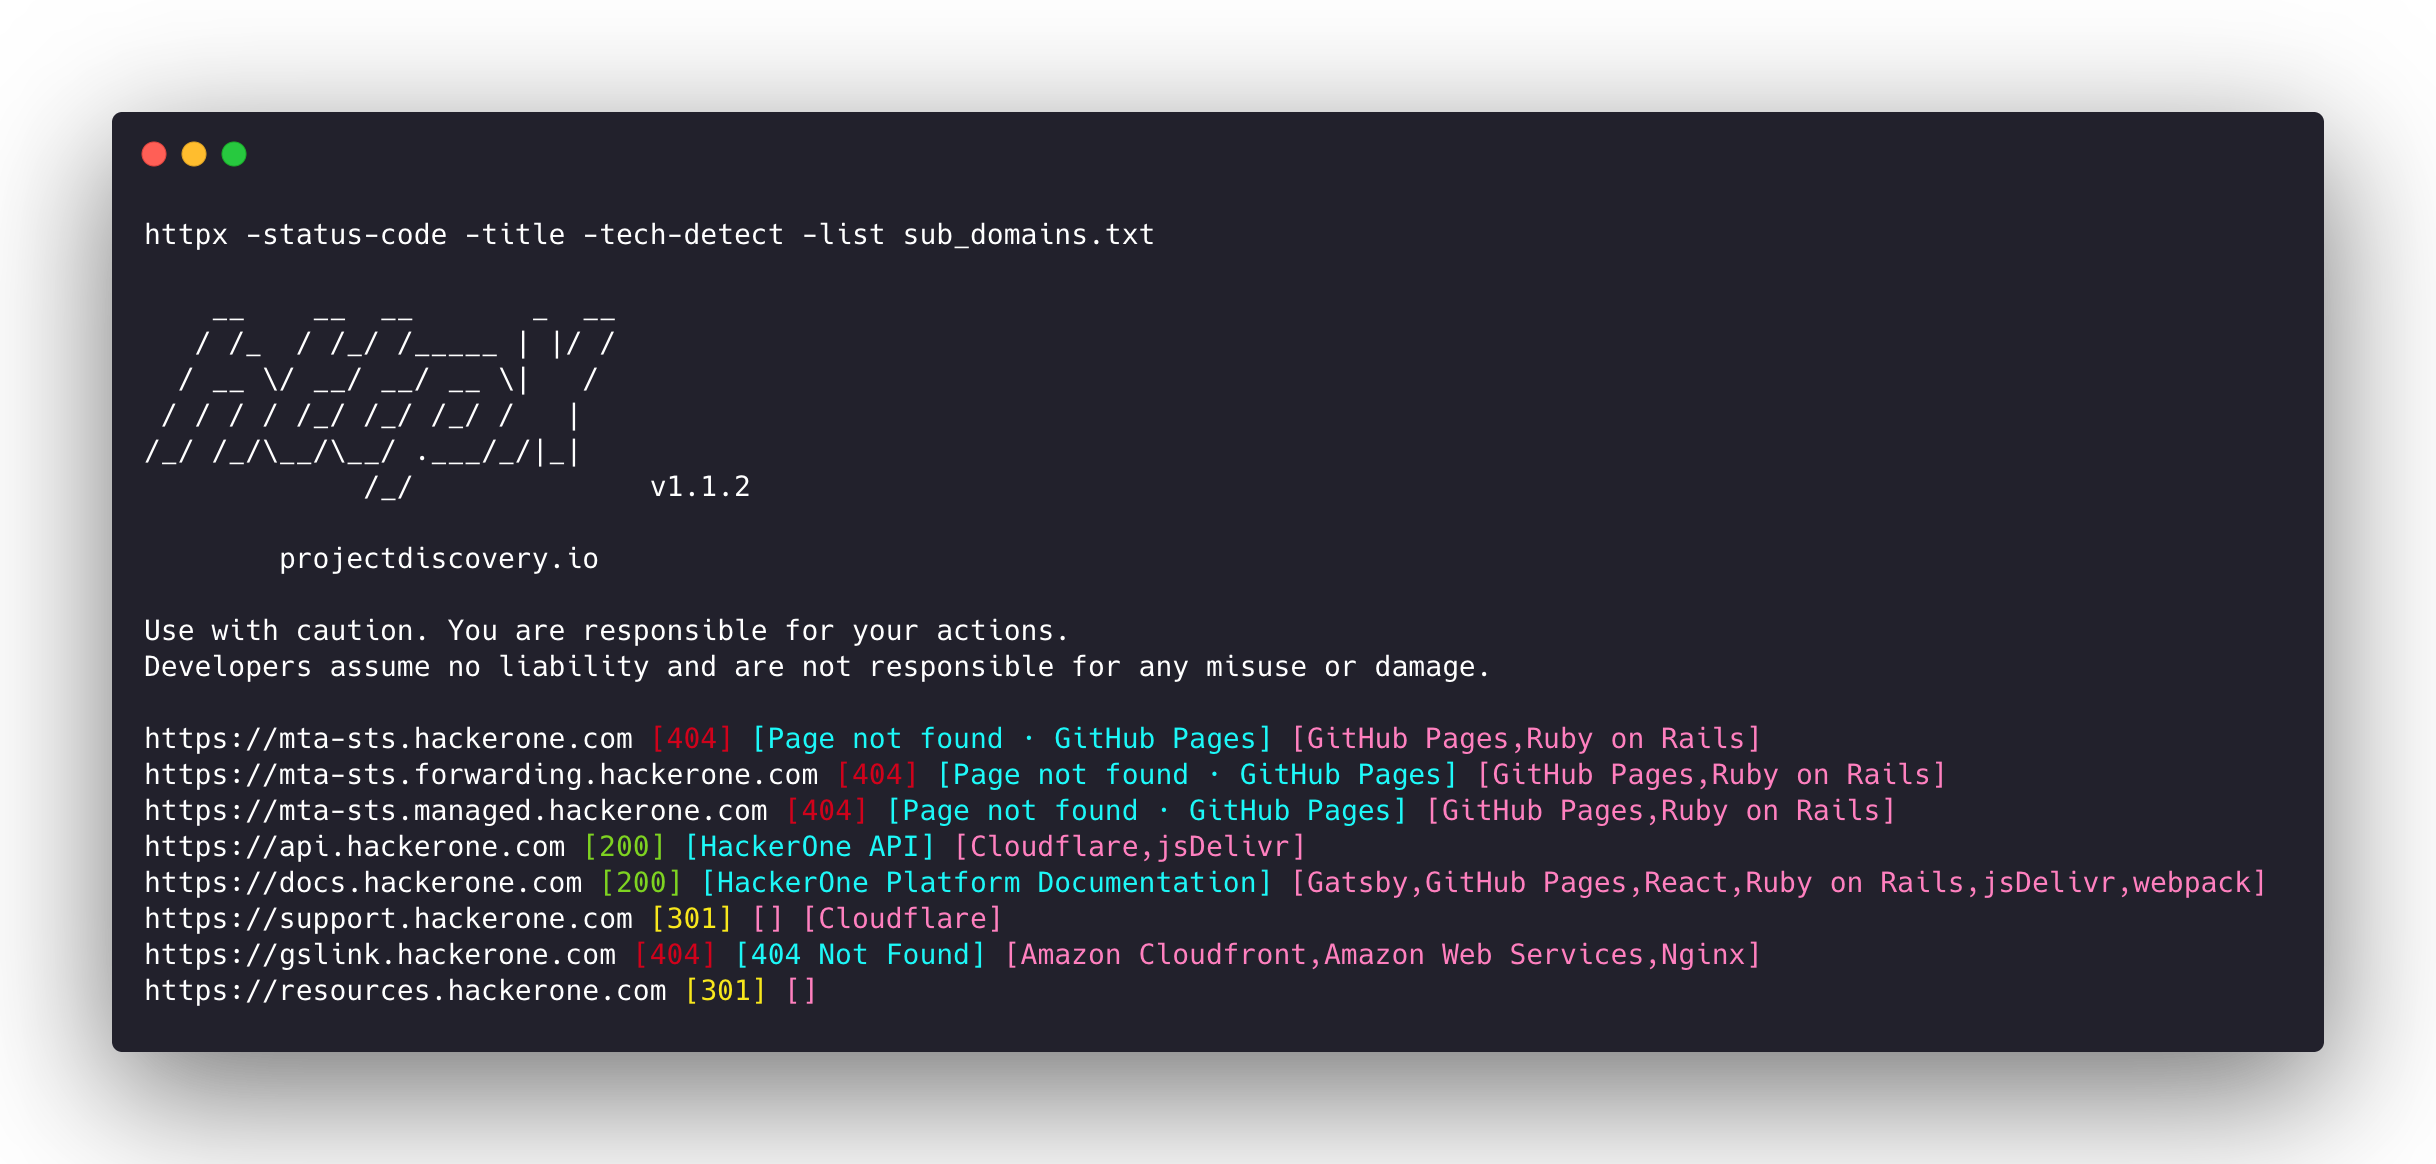 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 hahwul/webhackersweapons
⚔️ Web Hacker's Weapons / A collection of cool tools used by Web hackers. Happy hacking , Happy bug-hunting
 yeswehack/pwnfox
Firefox/Burp extension for security audits with single-click proxy, container profiles, postMessage logging, JS injection toolbox, and security…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 denuitt1/mhr-cfw
A Domain-Fronting Relay that routes traffic though GAS (Google Apps Script) and forwards it to Cloudflare Workers. Designed to bypass DPI.
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.