
evilwaf
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
fingerprint-spoofinginformation-gatheringosint+6
matrixleons/evilwafevilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 ianxtianxt/proxysqlmap
From Proxy to SqlMapApi
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 infobyte/faraday_addon
A browser extension for faradaysec platform https://faradaysec.com
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 keith-amateur/cve-2022-1040
Save the trouble to open the burpsuite...
 ottimo/burp-alfresco-referer-proxy-cve-2014-9301
Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
 dongpohezui/cve-2021-33045
Exploit for Dahua camera authentication bypass (CVE-2021-33045) using mitmproxy to intercept and modify login requests to /RPC2_Login.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
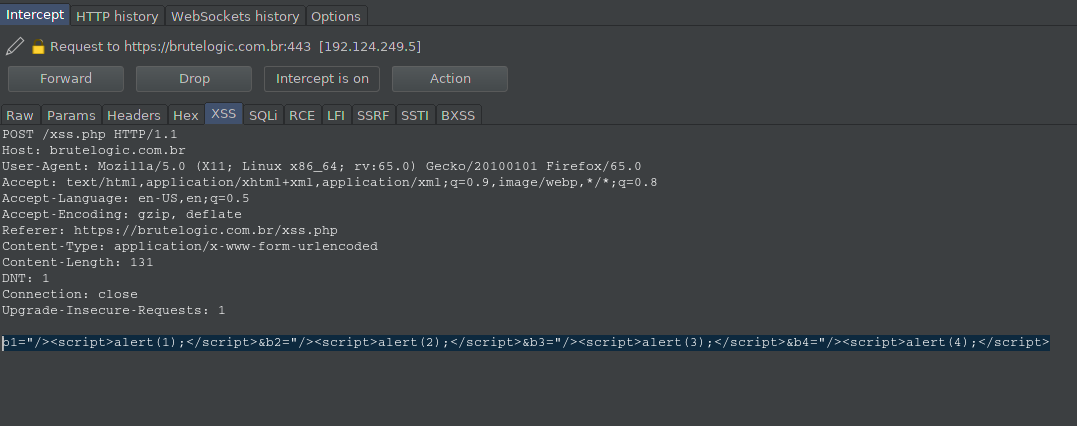 p3n73st3r/ghazi
Ghazi is a BurpSuite Plugins For Testing various PayLoads Like "XSS,SQLi,SSTI,SSRF,RCE and LFI" through Different tabs , Where Each Tab Will Replace…
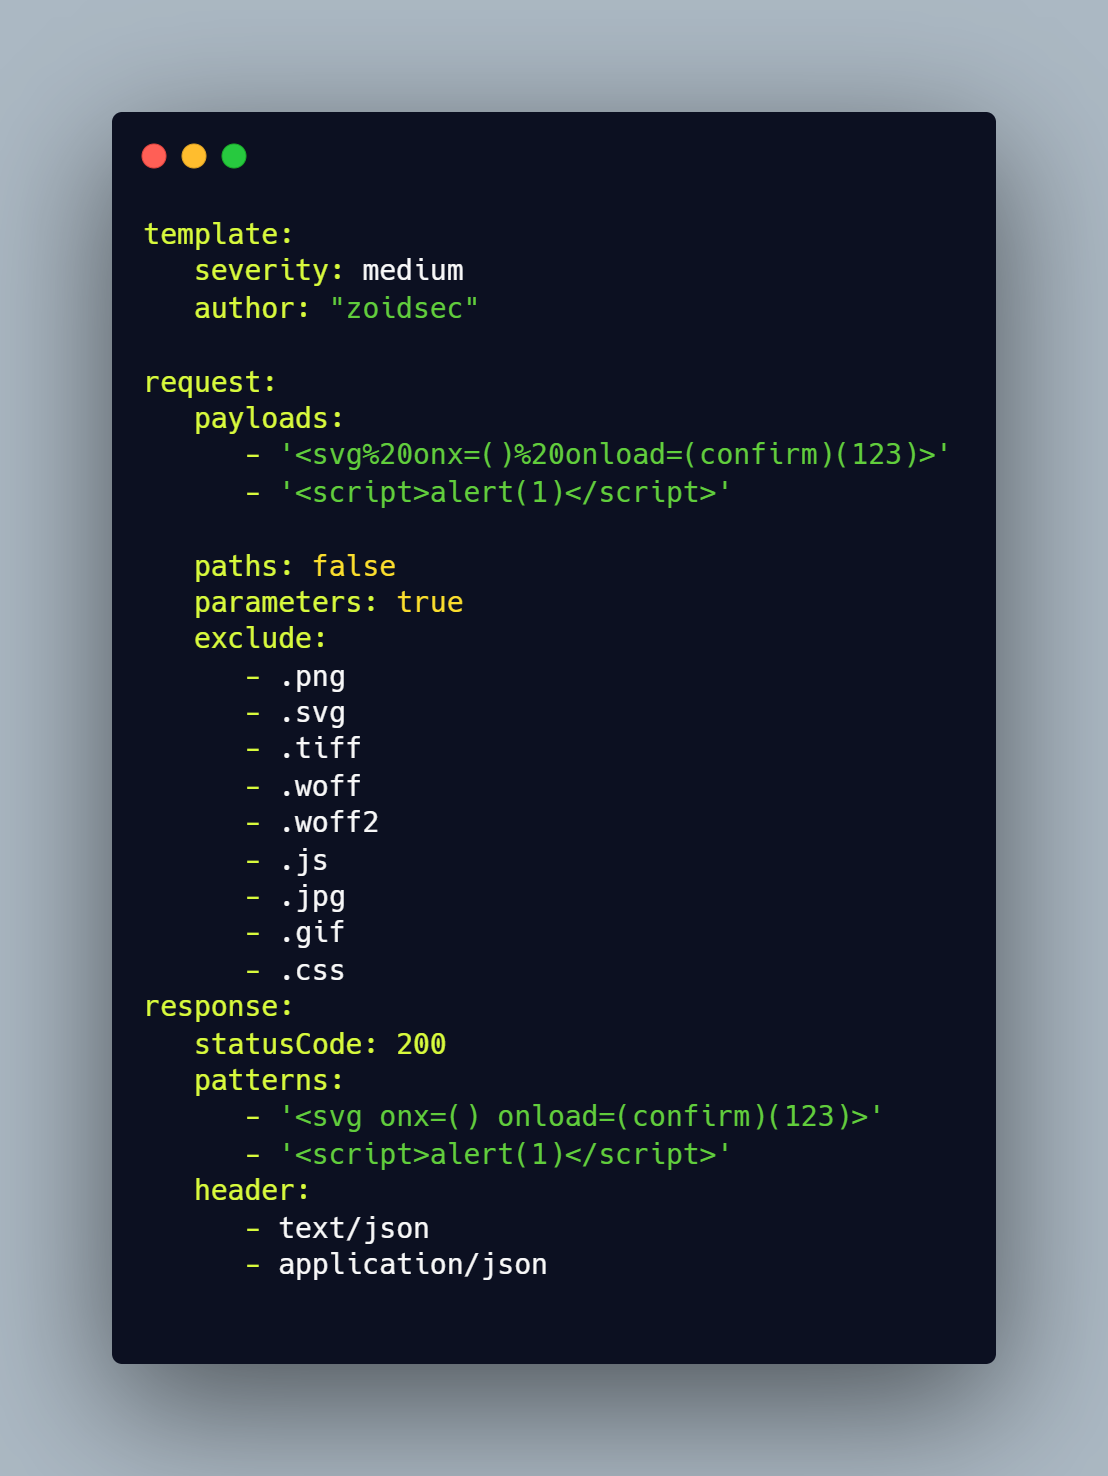 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.