
toxiproxy
 shopify/toxiproxy
:alarm_clock: :fire: A TCP proxy to simulate network and system conditions for chaos and resiliency testing
chaos-engineeringgeneral-purpose-utilitiesweb-proxies-interception
shopify/toxiproxy:alarm_clock: :fire: A TCP proxy to simulate network and system conditions for chaos and resiliency testing
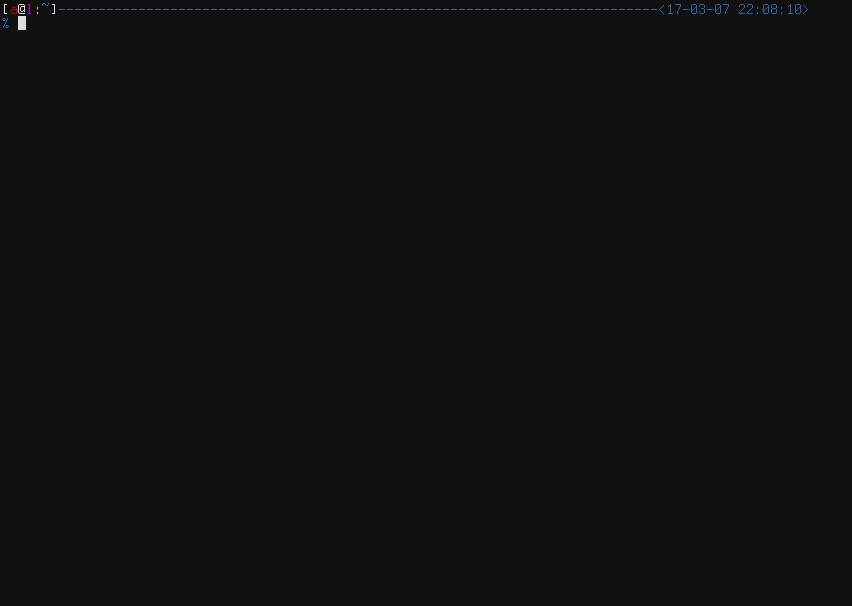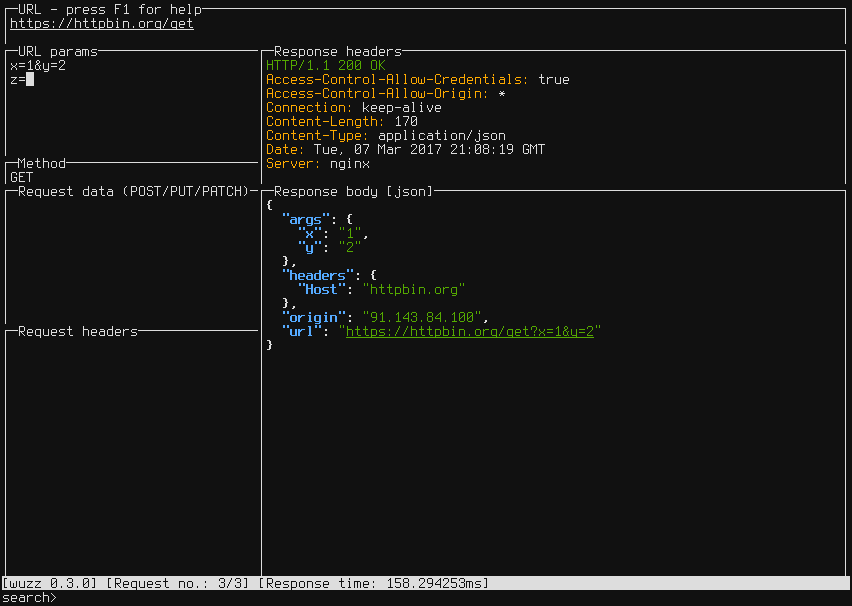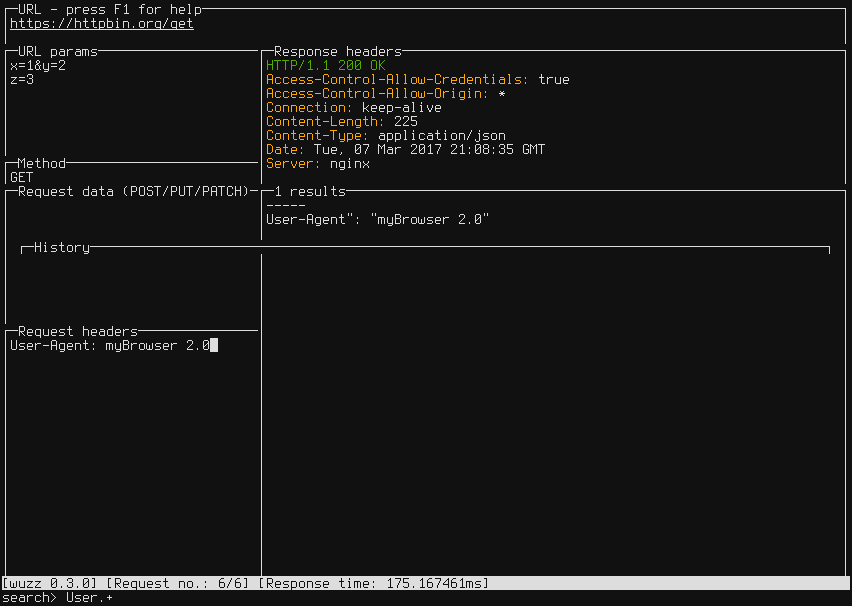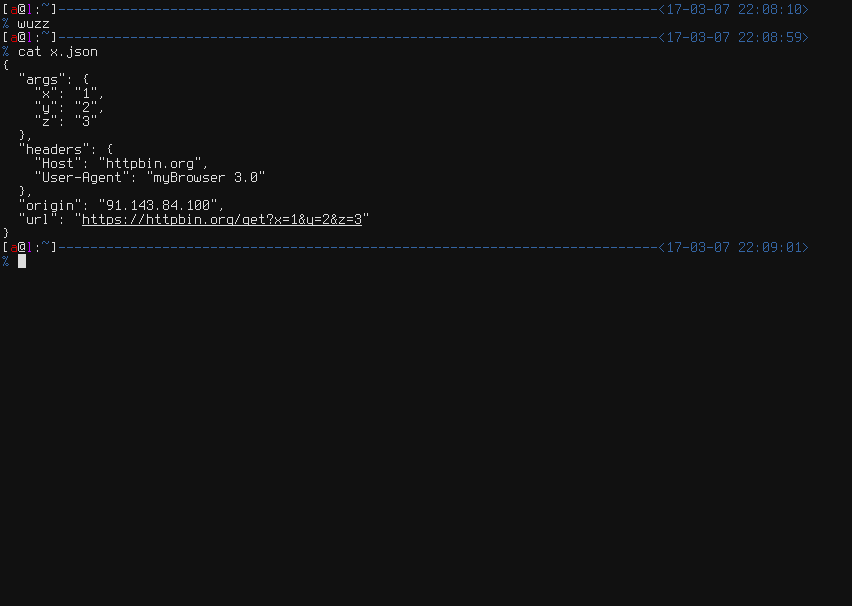 asciimoo/wuzz
Interactive cli tool for HTTP inspection
 kulikov0/whitelist-bypass
Tunneling data over webrtc to bypass censorship
 apify/crawlee
Node.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
 justmao945/mallory
HTTP/HTTPS proxy over SSH
 inaz2/proxy2
HTTP/HTTPS proxy in a single python script
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 caido/caido
Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
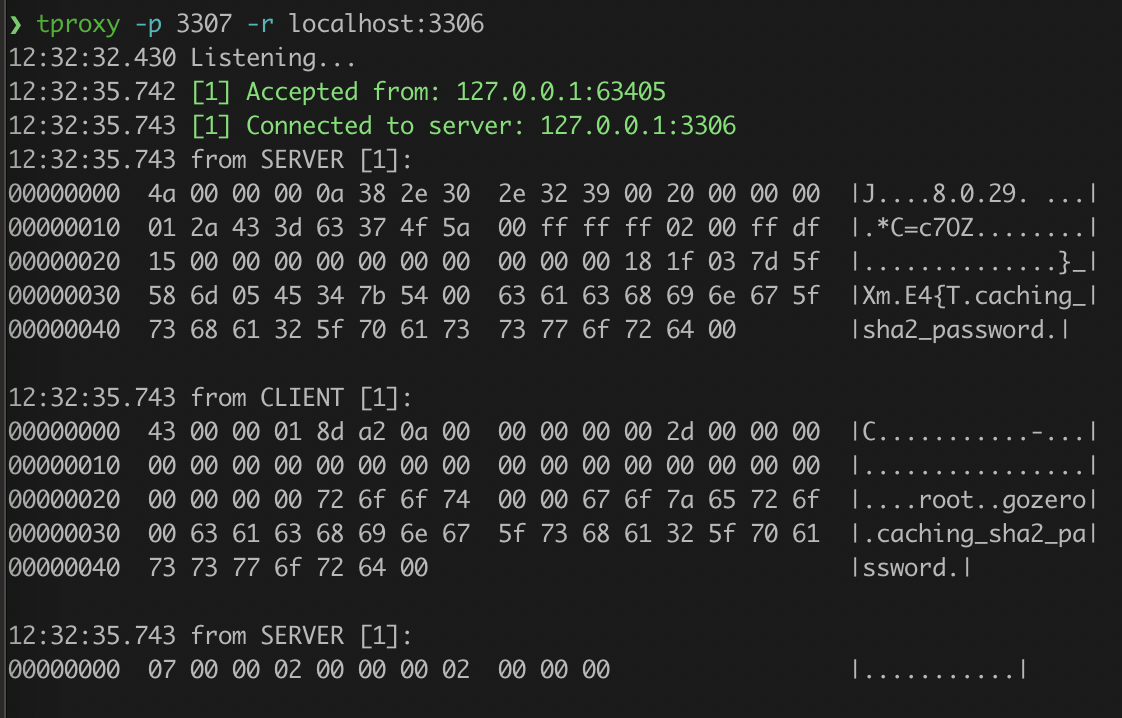 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
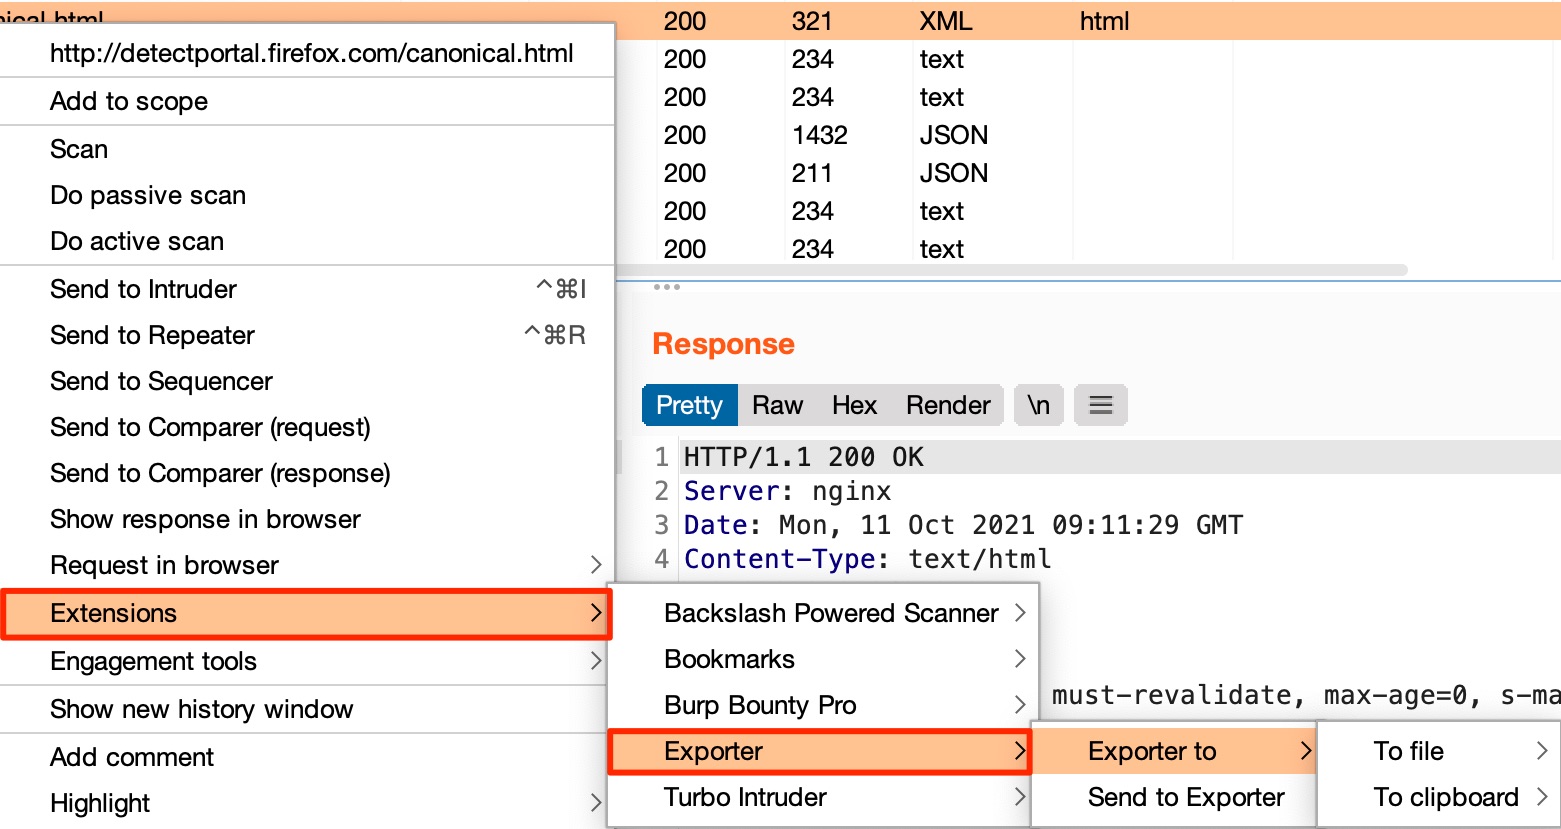 artssec/burp-exporter
Exporter is a Burp Suite extension to copy a request to a file or the clipboard as multiple programming languages functions.