

httpx
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
api-securityapi-security-testingcrawler+18
10.4k
projectdiscovery/httpxFast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 syhunt/sandcat
An open-source, pentest and developer-oriented web browser, using the power of Lua
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
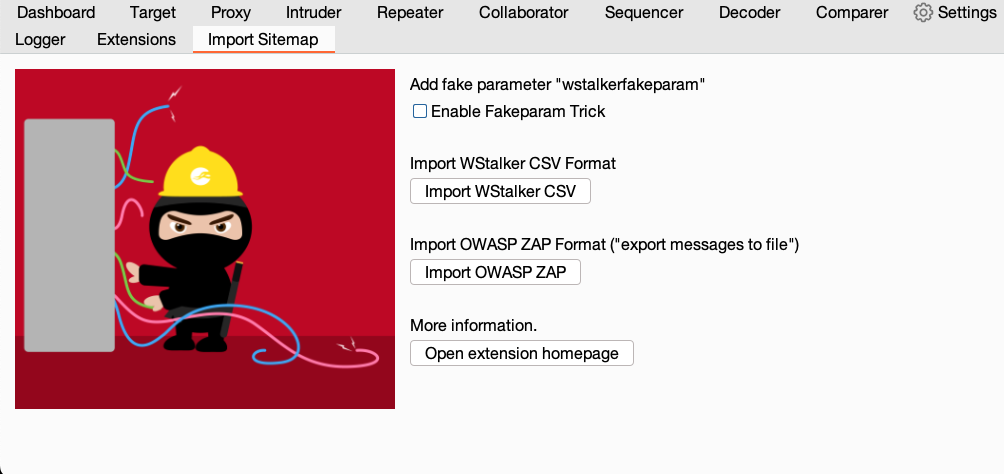 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
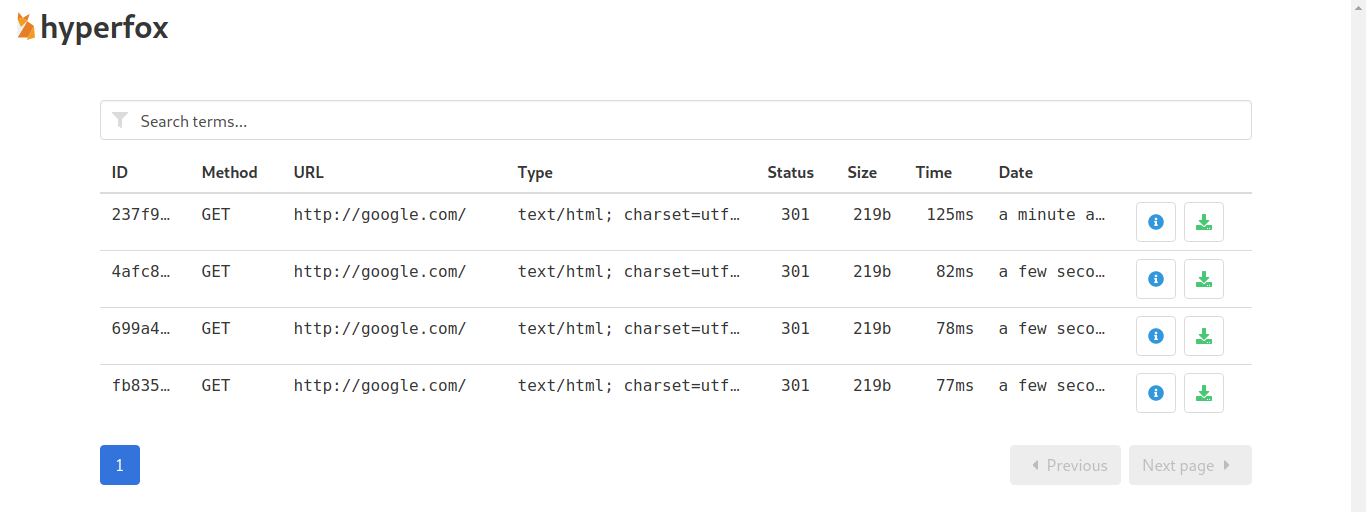 malfunkt/hyperfox
HTTP/HTTPS MITM proxy and recorder.
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…

 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…