
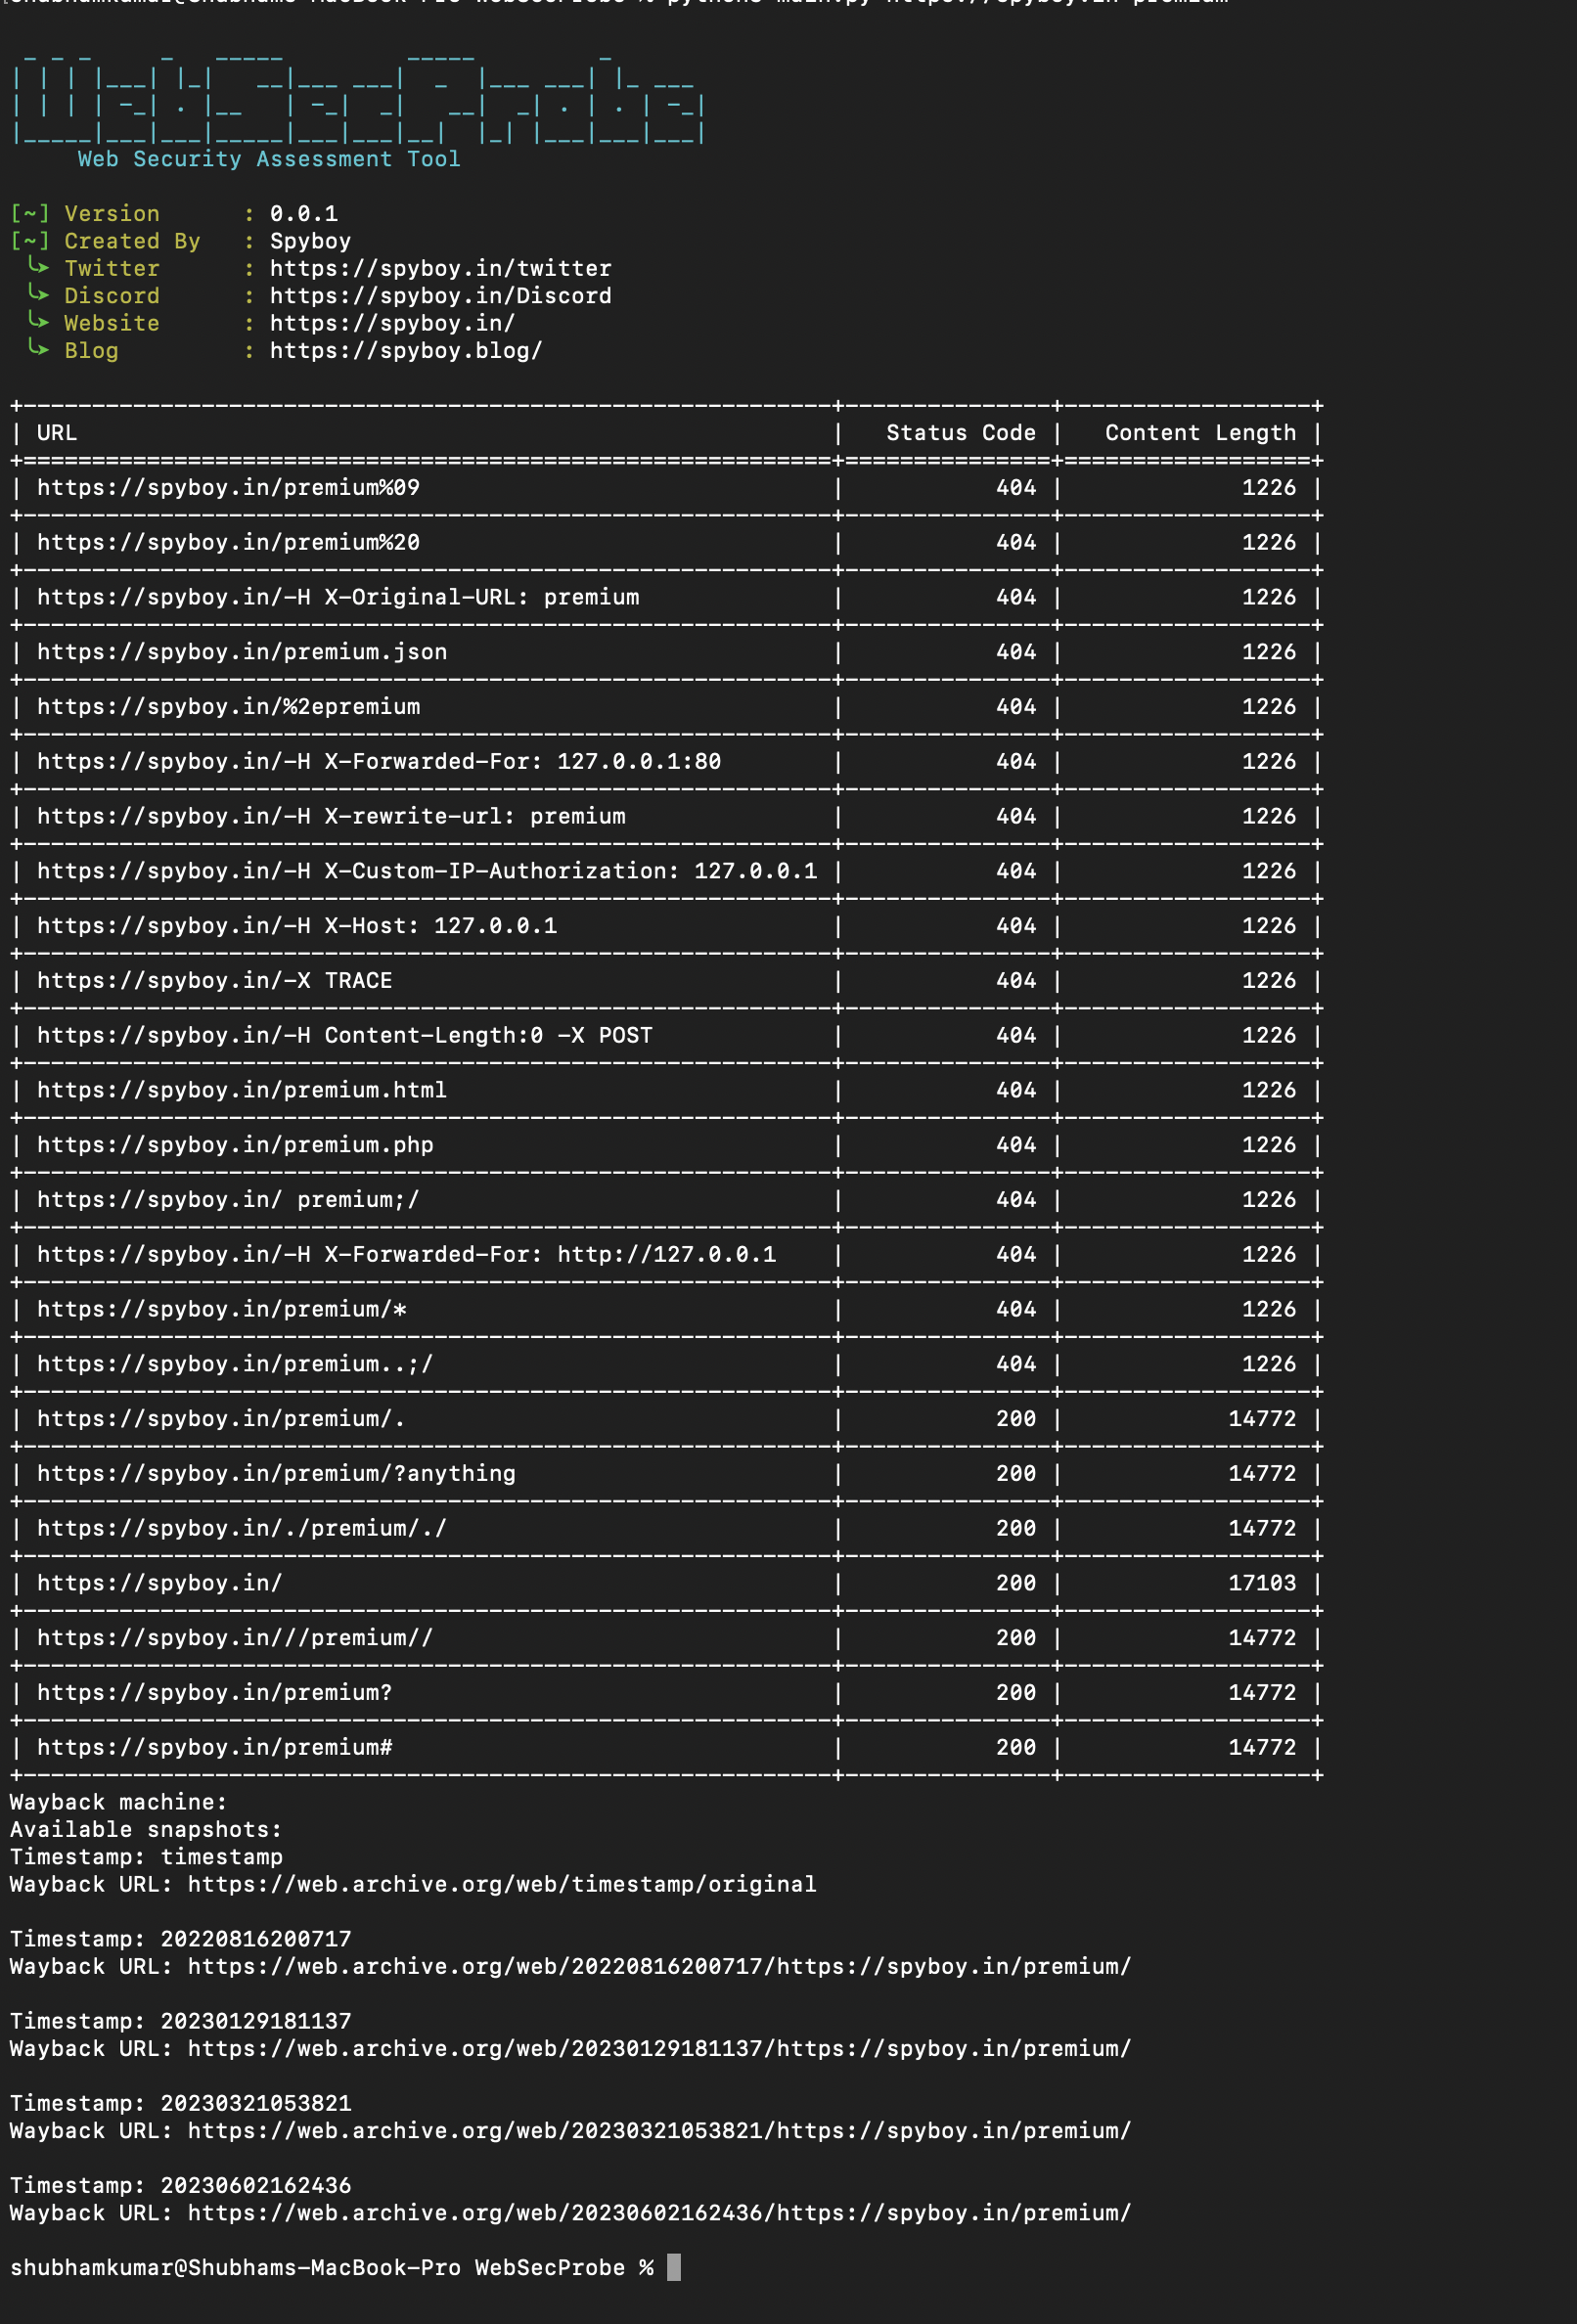
WebSecProbe
 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
misconfigurationpenetration-testingvulnerability-scanners+2
186
spyboy-productions/websecprobeSecurity testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 mbanyamer/cve-2026-27579-collabplatform-appwrite-cors-misconfiguration
Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…
 starkchristmas/cve-2020-1947
Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including…
 gquere/cve-2020-7931
Hacking Artifactory with server side template injection
 jet-pentest/cve-2022-24449
Solar Appscreener XXE
 mbadanoiu/cve-2019-12409
CVE-2019-12409: RCE Vulnerability Due to Bad Defalut Config in Apache Solr
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 vutiendat323/int14107_cve-2021-35042
Django-based CTF blog platform with integrated CVE-2021-35042 exploit tool for learning web application security and vulnerability exploitation.
 invicti-security/web-inf-path-trav
Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 vances25/cve-2024-44871
Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
 b374k/b374k
PHP Webshell with handy features
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 zerodayevil/cve-2026-41096-poc
Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and…
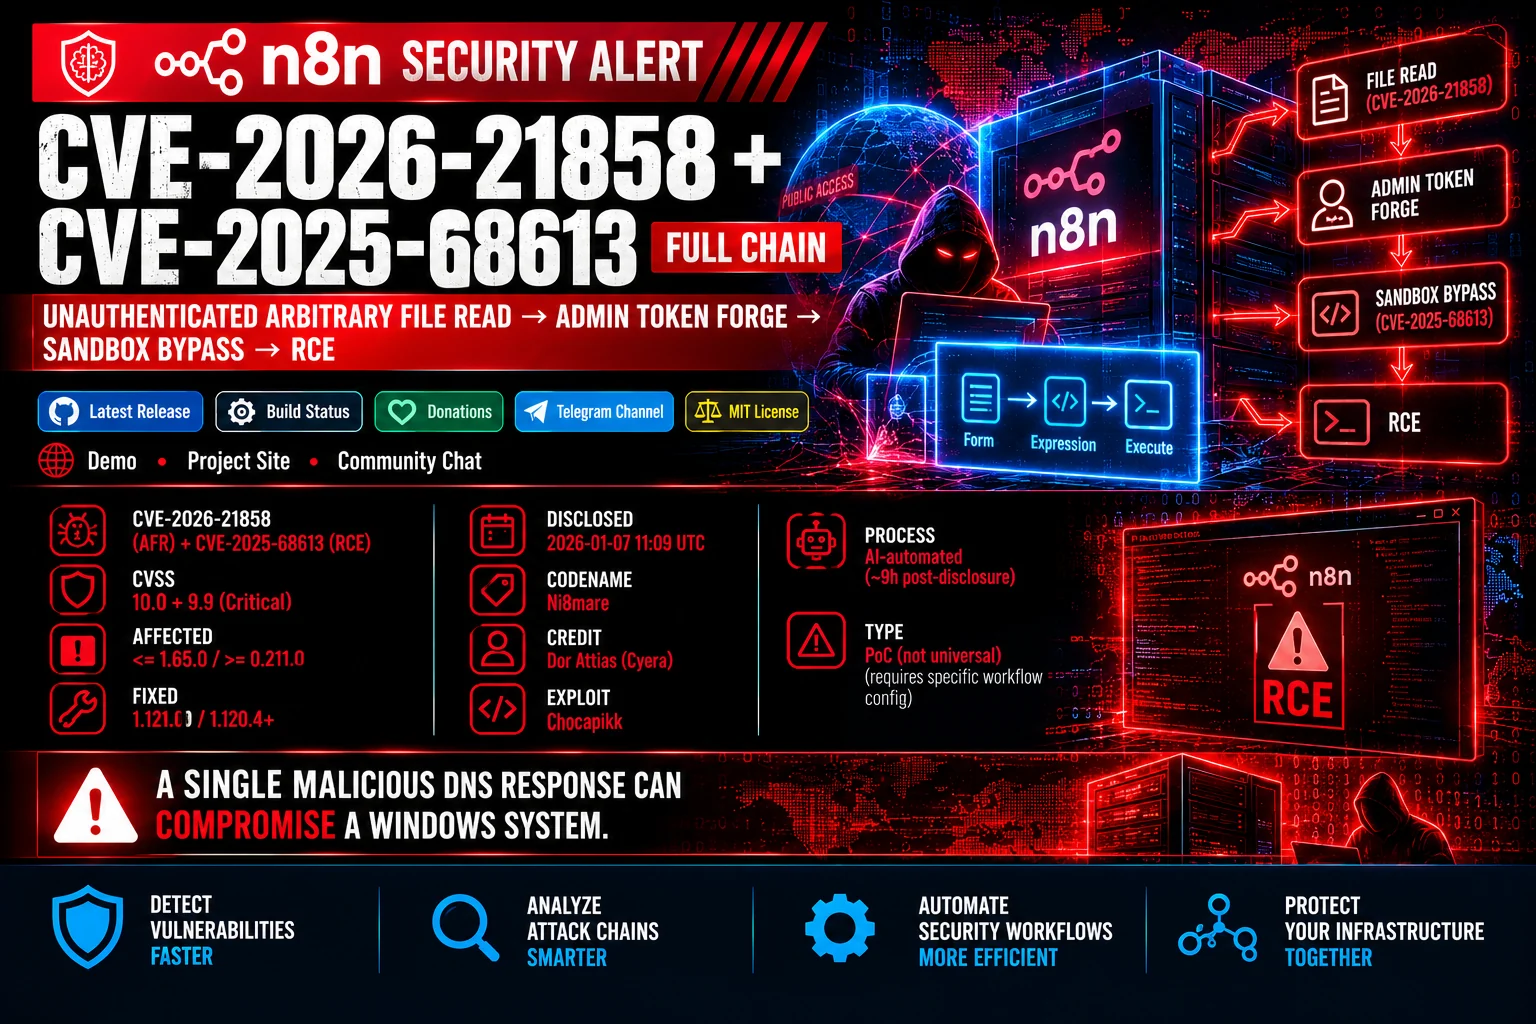 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 gagaltotal/cve-2026-57517-cwp
Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517
 la3b0z/cve-2025-24813-poc
CVE-2025-24813-POC JSP Web Shell Uploader
 sk1dr0wz/cve-2024-4358_mass_exploit
Mass exploitation tool for CVE-2024-4358, executing commands on multiple web targets concurrently with threading support.