

CVE-2024-3400
 h4x0r-dz/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, a Palo Alto OS command injection in GlobalProtect VPN. Demonstrates file creation and outbound command…
command-and-controlexploitationpenetration-testing+2
161
h4x0r-dz/cve-2024-3400Proof-of-concept exploit for CVE-2024-3400, a Palo Alto OS command injection in GlobalProtect VPN. Demonstrates file creation and outbound command…
 imjdl/cve-2019-11510-poc
Proof-of-concept exploit for CVE-2019-11510 targeting pre-authentication arbitrary file read in Pulse Secure SSL VPN. Enables extraction of sensitive…

 seed1337/cve-2024-24919-poc
Proof-of-concept exploit for CVE-2024-24919, an unauthenticated arbitrary file read vulnerability in Check Point SSL VPN appliances. Includes Nuclei…
 badboycxcc/netgear-ssl-vpn-20211222-cve-2022-29383
SQL injection exploit for CVE-2022-29383 in NETGEAR ProSafe SSL VPN, targeting scgi-bin/platform.cgi with sqlmap commands for FVS336Gv2 and FVS336Gv3…
 r00tpgp/http-pulse_ssl_vpn.nse
Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510
 aqhmal/pulsexploit
Automated script for Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API. You must have a Shodan account to use this…
 k4nfr3/cve-2018-13379-fortinet
Exploit for CVE-2018-13379 targeting Fortinet SSL VPN path traversal vulnerability. Enables automated exploitation and credential extraction for…
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
 c3rrberu5/cve-2024-24919
Nuclei template for detecting CVE-2024-24919, a path traversal vulnerability in CheckPoint SSL VPN appliances, enabling rapid security assessment.
 es0/cve-2019-11510_poc
PoC for CVE-2019-11510 | Pulse Secure 8.1R15.1/8.2/8.3/9.0 SSL VPN - Arbitrary File Disclosure vulnerability
 hcbt/cve-2026-9151
Authenticated OS command injection in the TP-Link Archer AX17 v1 VPN client import.
 mr-xn/cve-2023-43482
TP-Link ER7206 Omada Gigabit VPN Router uhttpd freeStrategy Command injection Vulnerability
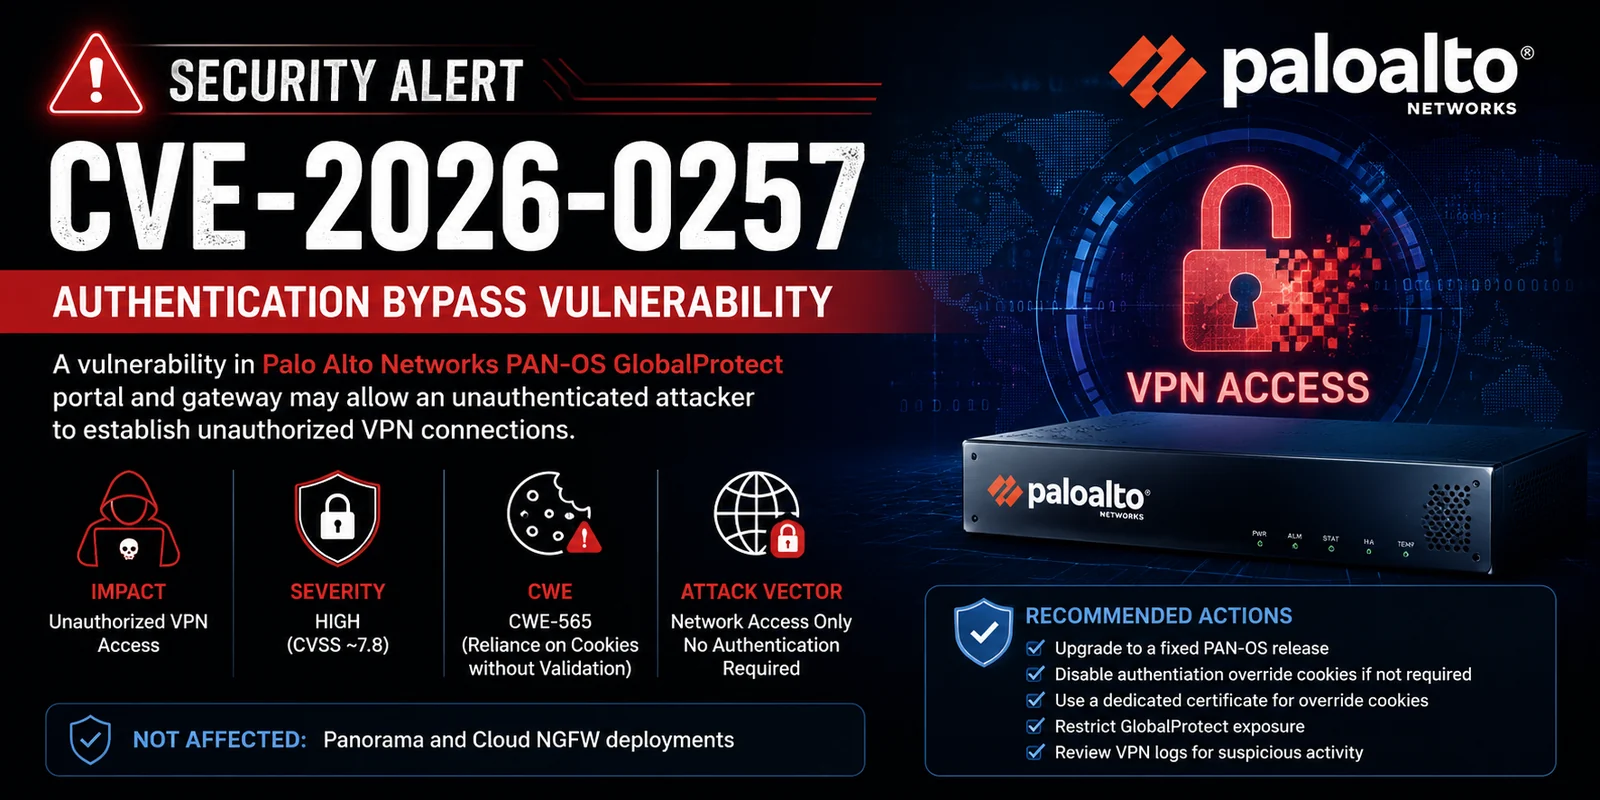 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
 tushargurav28/cve-2026-0257
Palo Alto Networks PAN-OS contains an authentication bypass caused by flaws in the GlobalProtect portal and gateway, letting attackers establish…
 slagzz/cve-2026-16348
TP-Link Archer BE800 V1 — VPN Key Injection RCE
 nocerainfosec/cve-2025-5777
Memory disclosure vulnerability in Citrix NetScaler ADC and Gateway when configured as a Gateway (VPN virtual server, ICA proxy, CVPN, RDP Proxy).
 rug4lo/cve-2024-24919-exploit
CVE-2024-24919 Exploit and PoC - Critical LFI for Remote Access VPN or Mobile Access.