
CVE-2025-44136
 mheranco/cve-2025-44136
Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…
exploitationpenetration-testingvulnerability-analysis+2
mheranco/cve-2025-44136Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…
 scap3sh4rk/cve-2025-66683
A Cross-Site Request Forgery (CSRF) vulnerability exists in the administrator profile update functionality of CarRentalMS v2.0. The affected endpoint…
 simoesctt/ctt-sovereign-vortex
Exploit for CVE-2026-2406 targeting Terrminus Authentication Gateways, using temporal dispersion to bypass fingerprinting and behavioral AI,…
 ahrixia/cve-2024-57428
CVE-2024-57428: PHPJabbers Cinema Booking System v2.0 suffers from stored XSS, enabling persistent JavaScript injection for phishing and malware…
 armaansidana2003/cve-2025-25614
Proof-of-concept exploit for CVE-2025-25614, an incorrect access control vulnerability in Unifiedtransform v2.0 allowing teachers to modify fellow…
 ahrixia/cve-2024-57429
CVE-2024-57429: PHPJabbers Cinema Booking System v2.0 is vulnerable to CSRF, allowing attackers to escalate privileges by forging requests on behalf…
 ghostwirez/cve-2024-9326-poc
Automated PoC exploit for CVE-2024-9326, a SQL injection vulnerability in PHPGurukul Online Shopping Portal v2.0, enabling security professionals to…
 armaansidana2003/cve-2025-25616
Proof-of-concept demonstrating incorrect access control in Unifiedtransform v2.0, allowing students to modify exam rules via the /exams/edit-rule…
 ahrixia/cve-2024-57427
CVE-2024-57427: PHPJabbers Cinema Booking System v2.0 is vulnerable to reflected XSS, allowing session hijacking and phishing attacks.
 armaansidana2003/cve-2025-25620
Proof-of-concept for stored XSS in Unifiedtransform v2.0's Create Assignment function, demonstrating remote code execution via malicious PDF upload…
 spbavarva/cve-2025-46203
PoC of CVE-2025-46203
 n1shant-sinha/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
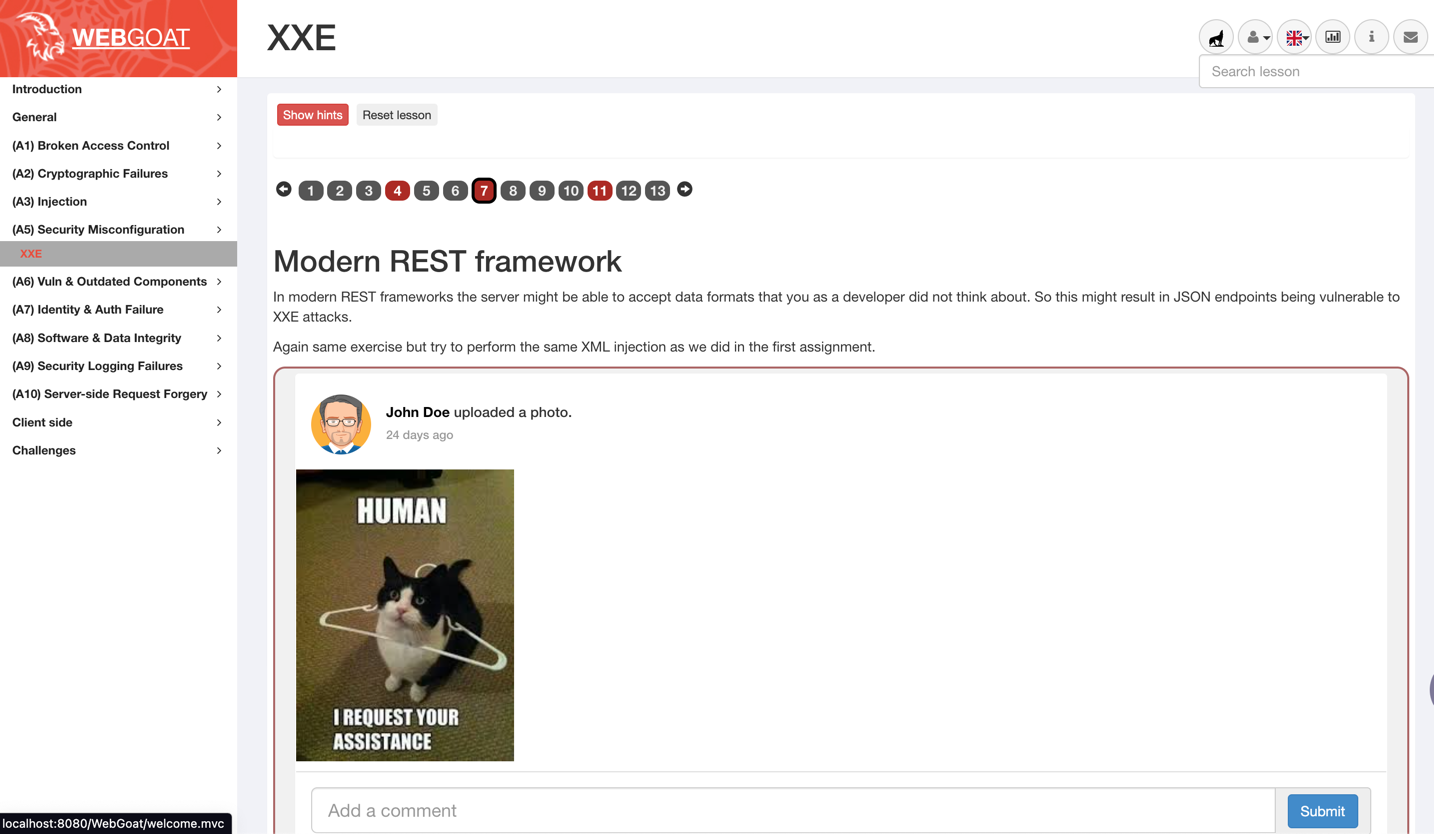 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
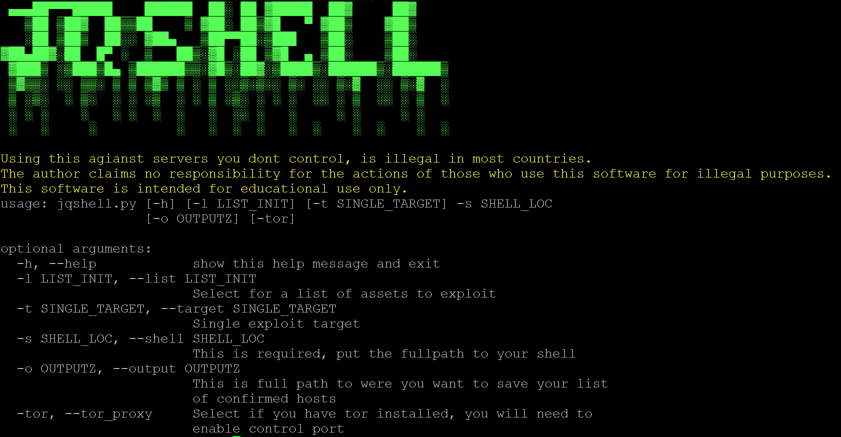 stahlz/jqshell
Automated exploit tool for CVE-2018-9206 (jQuery File Upload) with single/multi-target scanning, Tor proxy support, and output logging for…