

CVE-2025-63406-PoC
 nxvh1337/cve-2025-63406-poc
Small PoC to automate exploitation of CVE-2025-63406.
command-and-controlexploitationpenetration-testing+2
4
nxvh1337/cve-2025-63406-pocSmall PoC to automate exploitation of CVE-2025-63406.
 kaktus5454/cve-2018-15473
SSH username enumeration exploit for CVE-2018-15473 (OpenSSH 2.3-7.7). Sends malformed authentication packets to identify valid users on vulnerable…
 d34dun1c02n/cve-2023-30458
Username enumeration exploit for Medicine Tracker System 1.0 leveraging response timing discrepancies in the login functionality to identify valid…
 jfriedli/cve-2023-3897
Exploit for CVE-2023-3897 enabling username enumeration via CAPTCHA bypass in On-premise SureMDM on Windows. Includes PoC script for local user…
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 triple-octopus/bludit-cve-2019-17240-fork
Better version of rastating.github.io/bludit-brute-force-mitigation-bypass/
 xryptoh/cve-2025-63498
Stored XSS proof-of-concept for SOGo groupware, exploiting the 'Remember Username' cookie to inject JavaScript payloads via the login endpoint.
 dhananjayasj/cve-2024-1698-notificationx-wordpress-plugin-sql-injection-to-admin-credential-extraction
Unauthenticated time-based blind SQL injection exploit for NotificationX WordPress plugin (CVE-2024-1698) that extracts admin username and password…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 philippedixon/cve-2018-15473
Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…
 r3dston3/cve-2023-23752
Proof-of-concept exploit for CVE-2023-23752 (Joomla 4.0.0-4.2.8) that extracts usernames and passwords via an information disclosure vulnerability.
 snizi/cve-2026-18963-exploit
Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
 jweny/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980, a remote code execution vulnerability in Spring Data MongoDB via SpEL injection in the username…
 estebanzarate/cve-2025-47812-wing-ftp-server-7.4.3-unauthenticated-rce-poc
Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
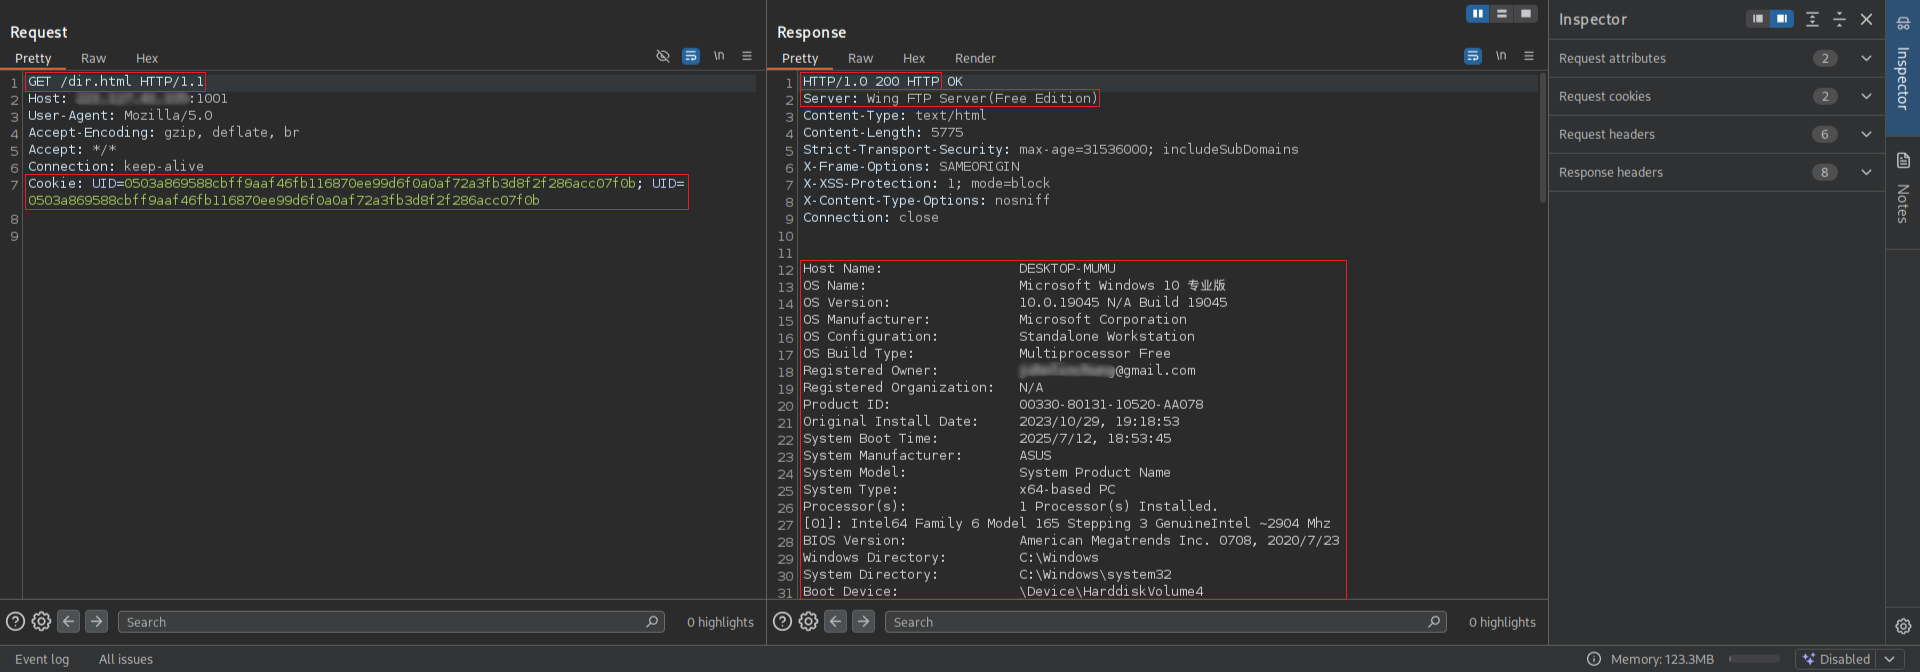 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 overgrowncarrot1/cve-2021-22911
Python exploit script for CVE-2021-22911 targeting Rocket.Chat admin password reset via unauthenticated user registration. Automates exploitation…