

CVE-2023-32243
 randomrobbiebf/cve-2023-32243
CVE-2023-32243 - Essential Addons for Elementor 5.4.0-5.7.1 - Unauthenticated Privilege Escalation
exploitationpassword-attackspenetration-testing+3
86
randomrobbiebf/cve-2023-32243CVE-2023-32243 - Essential Addons for Elementor 5.4.0-5.7.1 - Unauthenticated Privilege Escalation
 jas502n/cve-2020-10199
PoC exploit collection for Nexus Repository Manager 3 vulnerabilities (CVE-2020-10199, CVE-2020-10204, CVE-2020-11444) enabling remote code execution…
 godylockz/cve-2024-42327
POC for CVE-2024-42327: Zabbix Privilege Escalation -> RCE
 im-hanzou/msaper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2023-3076 - MStore API < 3.9.9 - Unauthenticated Privilege Escalation (Mass Add…
 ly1g3/mailcow-cve-2022-31245
CVE-2022-31245: RCE and domain admin privilege escalation for Mailcow
 its-arun/cve-2020-35682
Proof-of-concept exploit for CVE-2020-35682: SAML authentication bypass in ManageEngine ServiceDesk Plus, enabling privilege escalation to…
 murrez/cve-2026-14281
Unauthenticated privilege escalation in WordPress WAWP (Automation Web Platform) ≤ 4.8.6 via public REST signup and unsanitized wawp_custom_fields →…
 im-hanzou/mass-cve-2023-28121
CVE-2023-28121 - WooCommerce Payments < 5.6.2 - Unauthenticated Privilege Escalation [ Mass Add Admin User ]
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 pysectools/cve-2026-3629
WordPress Privilege Escalation Checker
 theeblind/cve-2018-18387
playSMS < = 1.4.2 - Privilege escalation
 chrisbarack/cve-2025-55182
Technical penetration testing writeup demonstrating exploitation of CVE-2025-55182 in Next.js, credential harvesting from SQLite, and privilege…
 r3vpwnx/cve-2025-8110
Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…
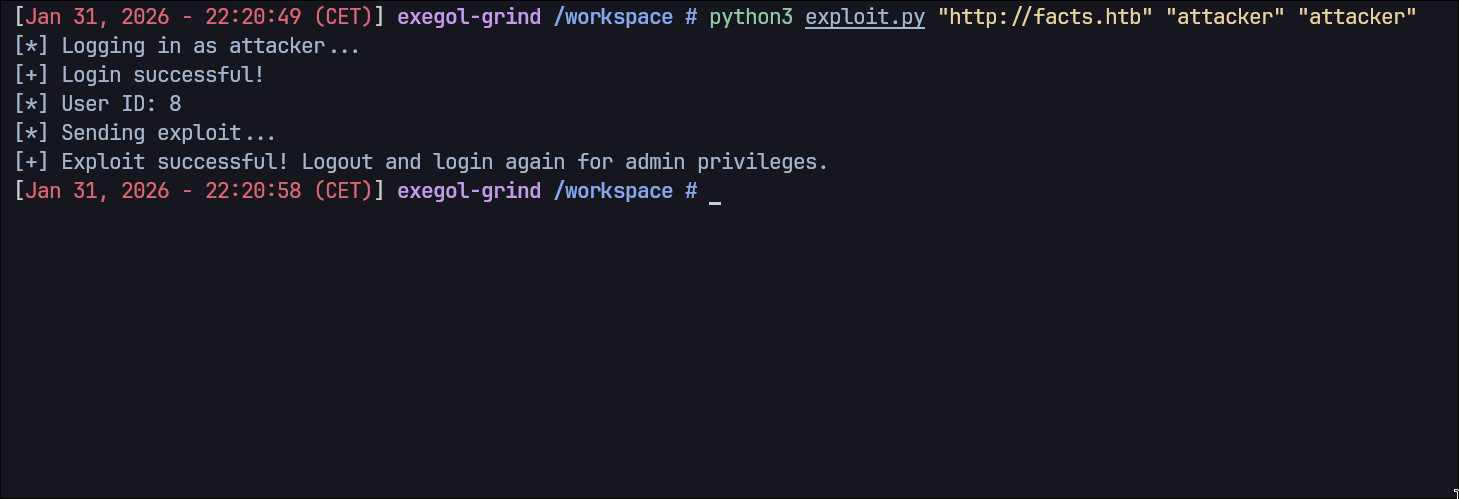 whiteov3rflow/cve-2025-2304-poc
Proof-of-concept exploit for CVE-2025-2304, a mass assignment vulnerability in Camaleon CMS < 2.9.1 allowing authenticated privilege escalation to…
 randomrobbiebf/cve-2024-49328
WP REST API FNS <= 1.0.0 - Privilege Escalation
 drkim-dev/cve-2026-30862
Proof-of-concept demonstrating stored XSS in Appsmith Table Widget leading to vertical privilege escalation and full admin takeover via XSS-to-CSRF…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 zycoder0day/cve-2026-8732
Automated 8-phase exploit for CVE-2026-8732, an unauthenticated privilege escalation in WP Maps Pro ≤ 6.1.0. Uses multiprocessing and asyncio to scan…