
CVE-2019-0708-POC
 closethe/cve-2019-0708-poc
Proof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting RDP services on Windows systems. Detects vulnerability and triggers remote code…
exploitationpenetration-testingremote-access-tool+2
13
closethe/cve-2019-0708-pocProof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting RDP services on Windows systems. Detects vulnerability and triggers remote code…
 watchtowrlabs/watchtowr-vs-fortisiem-cve-2025-25256
Detection artifact generator for FortiSIEM CVE-2025-25256 unauthenticated remote command execution vulnerability. Sends crafted packets to verify…
 haingn/lohongcam-cve-2021-33044
Python exploit for Dahua device authentication bypass (CVE-2021-33044). Sends crafted malicious data packets to bypass login and gain unauthorized…
 mattgsys/cve-2026-0834
Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 bhanunamikaze/activemq-cve-2023-46604
Non-destructive validator for Apache ActiveMQ CVE-2023-46604. Sends crafted OpenWire packets, uses HTTP callback server to confirm RCE or XML…
 kaktus5454/cve-2018-15473
SSH username enumeration exploit for CVE-2018-15473 (OpenSSH 2.3-7.7). Sends malformed authentication packets to identify valid users on vulnerable…
 gumerzzzindo/cve-2024-47176
Python exploit for CVE-2024-47176 achieving remote command execution in CUPS cups-browsed via crafted UDP packets. Includes reverse shell payload…
 benjaminhays/cve-2023-28771-poc
PoC for CVE-2023-28771 based on Rapid7's excellent writeup
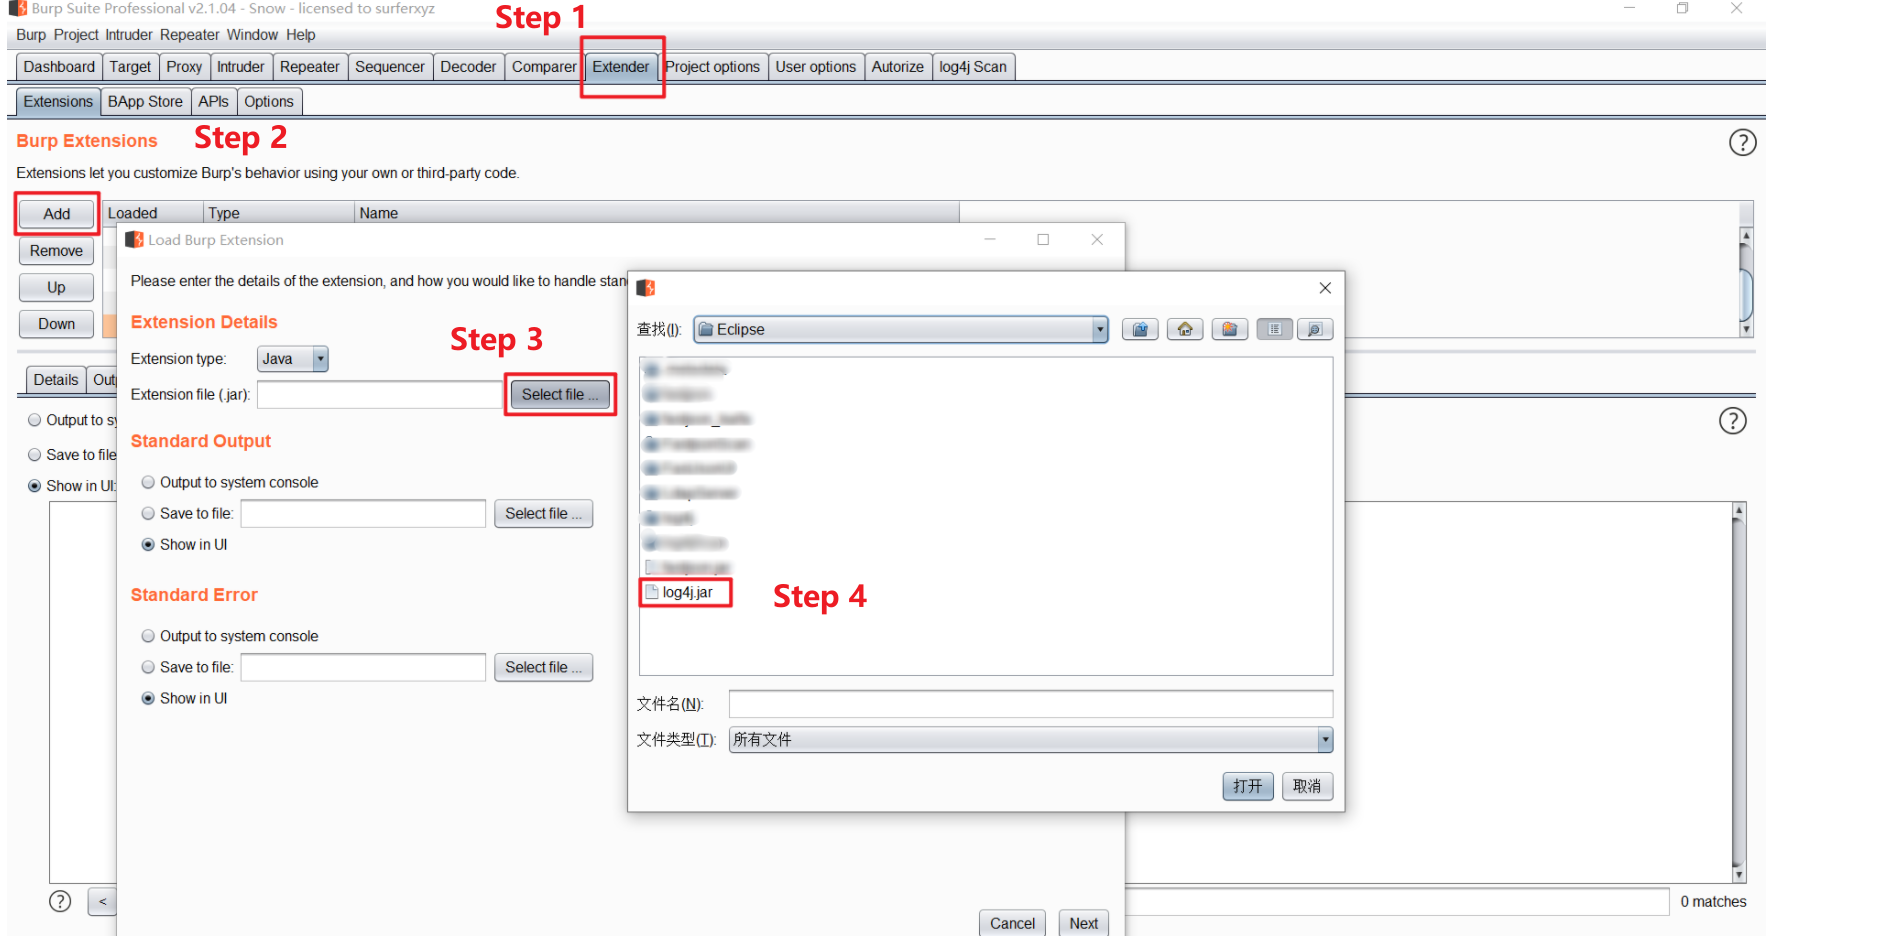 snow0715/log4j-scan-burpsuite
Log4j漏洞(CVE-2021-44228)的Burpsuite检测插件
