CVE-2020-15778-SCP-Command-Injection-Check

This script is a safe and simple tool that helps system users, students, and administrators check if their SCP (Secure Copy) client is vulnerable to…

This script is a safe and simple tool that helps system users, students, and administrators check if their SCP (Secure Copy) client is vulnerable to…

A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…

CVE-2025-0282 is a critical vulnerability found in Ivanti Connect Secure, allowing Remote Command Execution (RCE) through a buffer overflow exploit.

Proof On Concept — Pulse Secure CVE-2021-22893

DO NOT RUN THIS.

Tool to test for existence of CVE-2020-8218

Ivanti Connect Secure, Policy Secure & ZTA Gateways - CVE-2025-0282

TP-Link Archer AXE75 Authenticated Command Injection

PoC for CVE-2025-20265 Cisco Secure FMC Software RADIUS Remote Code Execution Vulnerability

CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…

A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…

Exploit for CVE-2019-11510 targeting Pulse Secure VPN to perform unauthenticated arbitrary file reading and potential credential disclosure.

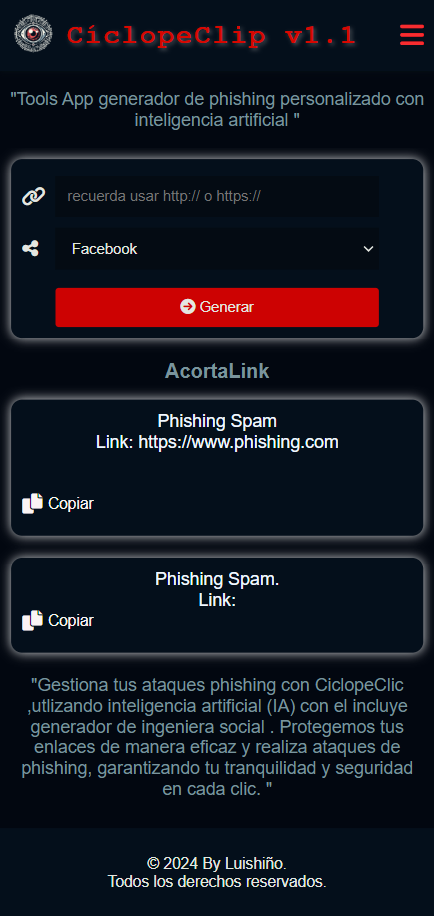
Security awareness training tool for authorized phishing simulations and internal IT audits

Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510

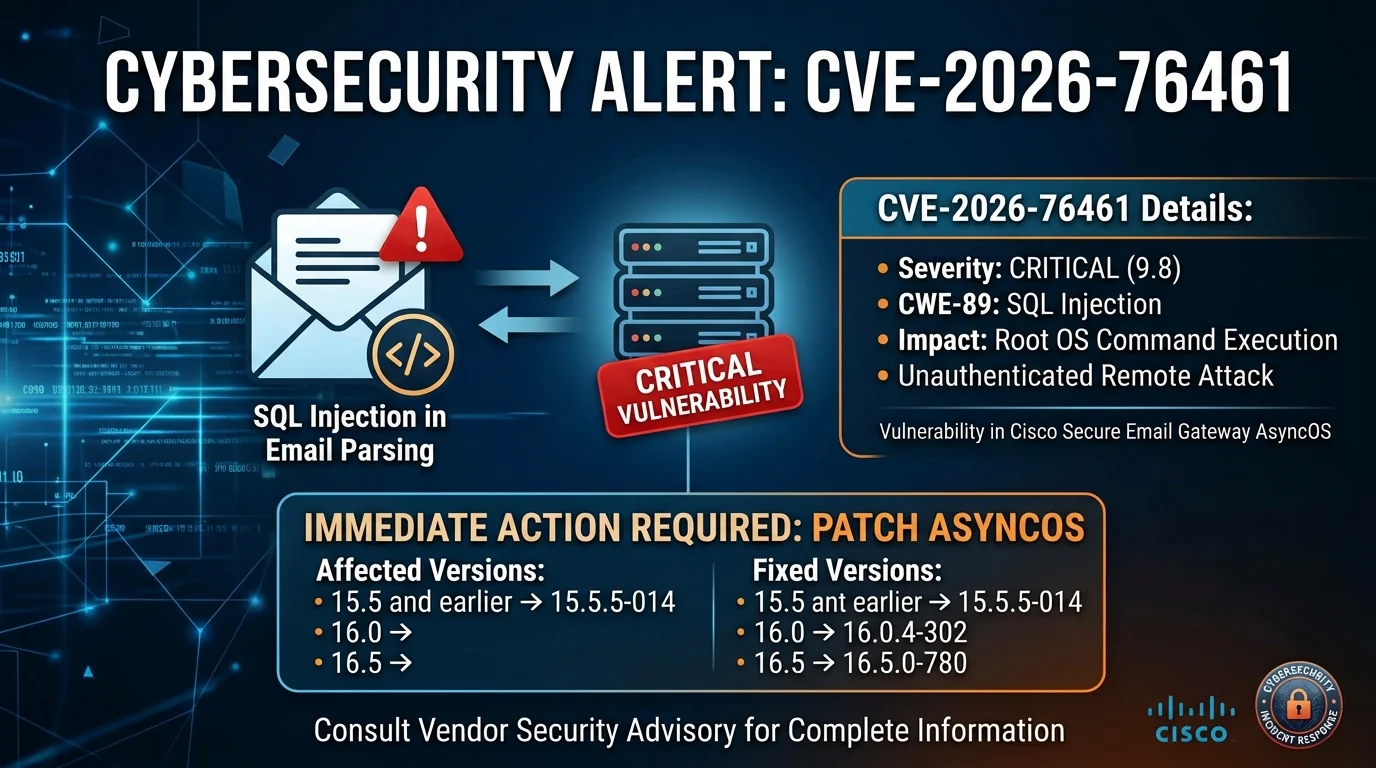
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…

An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…

Patched Adobe Flex SWF files (editor.swf, uploader.swf, uploaderSingle.swf) to fix the CVE-2011-2461 CSRF vulnerability in Magento. Replace…

Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…