
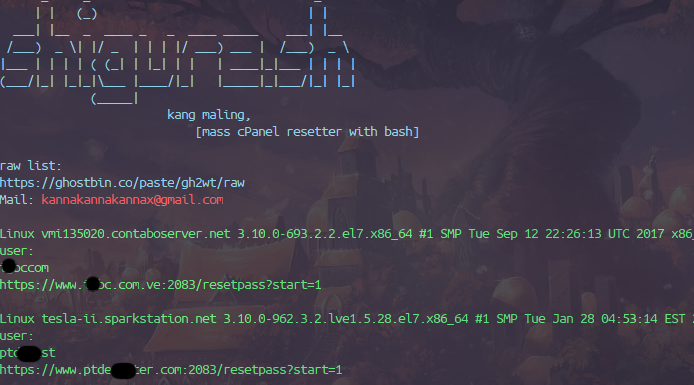
shiguresh
 redsplit/shiguresh
CVE-2004-1769 // Mass cPanel Reset password
exploitationpassword-attacksvulnerability-analysis+1
redsplit/shigureshCVE-2004-1769 // Mass cPanel Reset password
 alewong/webminrce-exp-cve-2019-15107-
Remote Code Execution Vulnerability in Webmin
 0xwhoami35/cve-2023-23752
Authentication bypass exploit for Joomla CVE-2023-23752 that leaks administrator credentials and MySQL configuration from vulnerable versions…
 eqstlab/cve-2026-72898
Unauthenticated blind SQL injection exploit for Metabase, exploiting a raw SQL injection in the password reset endpoint to extract data via…
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 mananispiwpiw/cve-2025-58434-poc
CVE-2025-58434 Proof of Concept
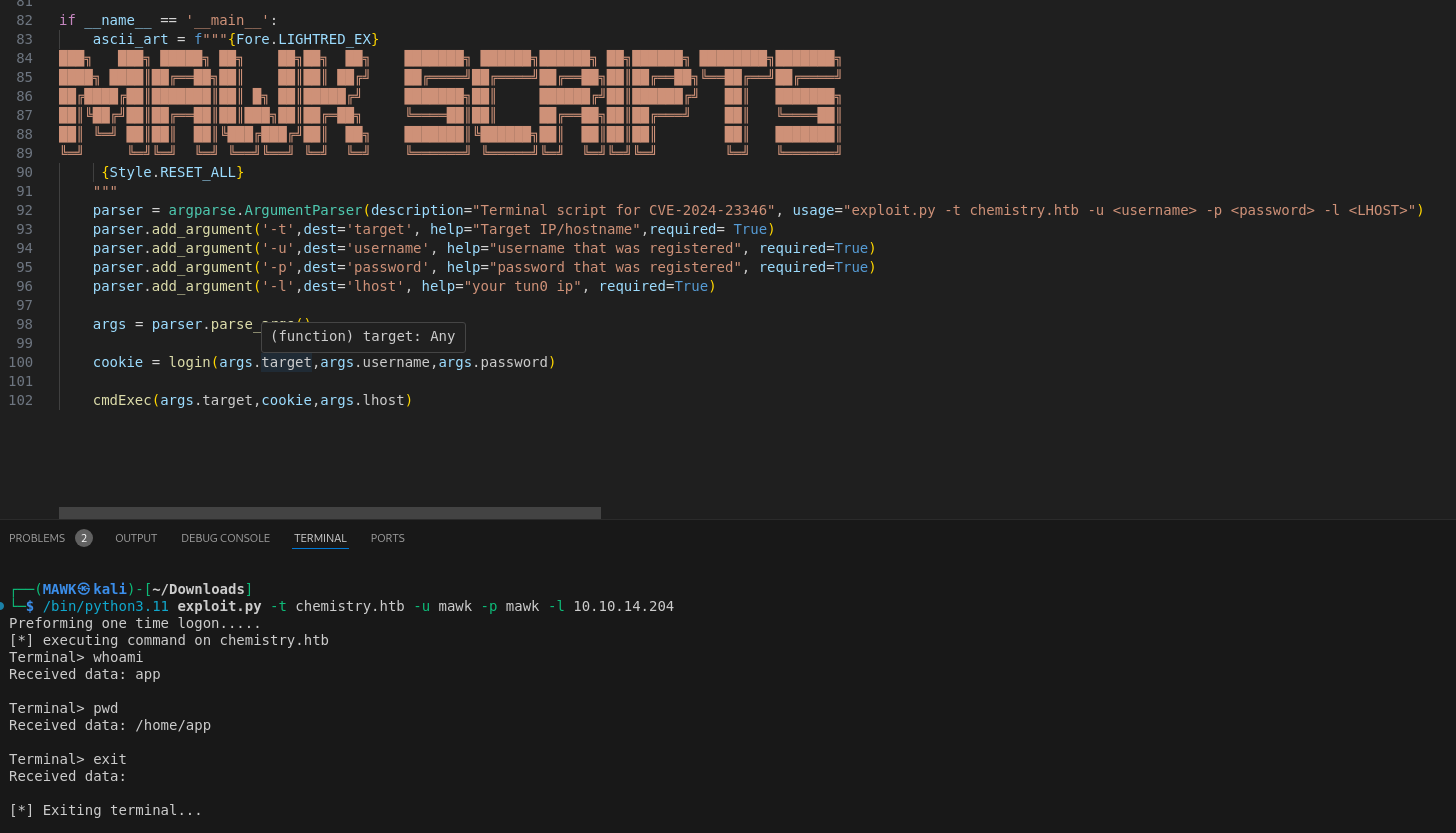 mawk0235/cve-2024-23346
This is an exploit for CVE-2024-23346 that acts as a "terminal" (tested on chemistry.htb)
 vanlam2001/csrf_casdoor
Proof-of-concept CSRF exploit for Casdoor's `/api/set-password` endpoint (CVE-2023-34927), enabling unauthorized password changes via cross-site POST…
 tim-hoekstra/cve-2022-37932
Proof-of-concept exploit for an authentication bypass in HP 1920 Series switches, allowing unauthenticated admin password change via crafted HTTP…
 cyberhawk000/cve-2022-24181
XSS via Host Header injection and Steal Password Reset Token of another user
 enzocipher/cve-2025-25198
Captures password reset tokens from Mailcow Host header injection attacks.
 groppoxx/cve-2025-25198-poc
PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…