burp-alfresco-referer-proxy-cve-2014-9301

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Proof-of-concept exploit for CVE-2024-2054, demonstrating insecure deserialization RCE in Artica-Proxy administrative web application. Includes…

Exploit script for CVE-2025-55182 that deploys a Godzilla memory shell on vulnerable web servers, with support for proxy and encoding options.

Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…

Python-based proof-of-concept exploit for CVE-2021-3019 targeting Lanproxy, enabling remote code execution via directory traversal in the web proxy…

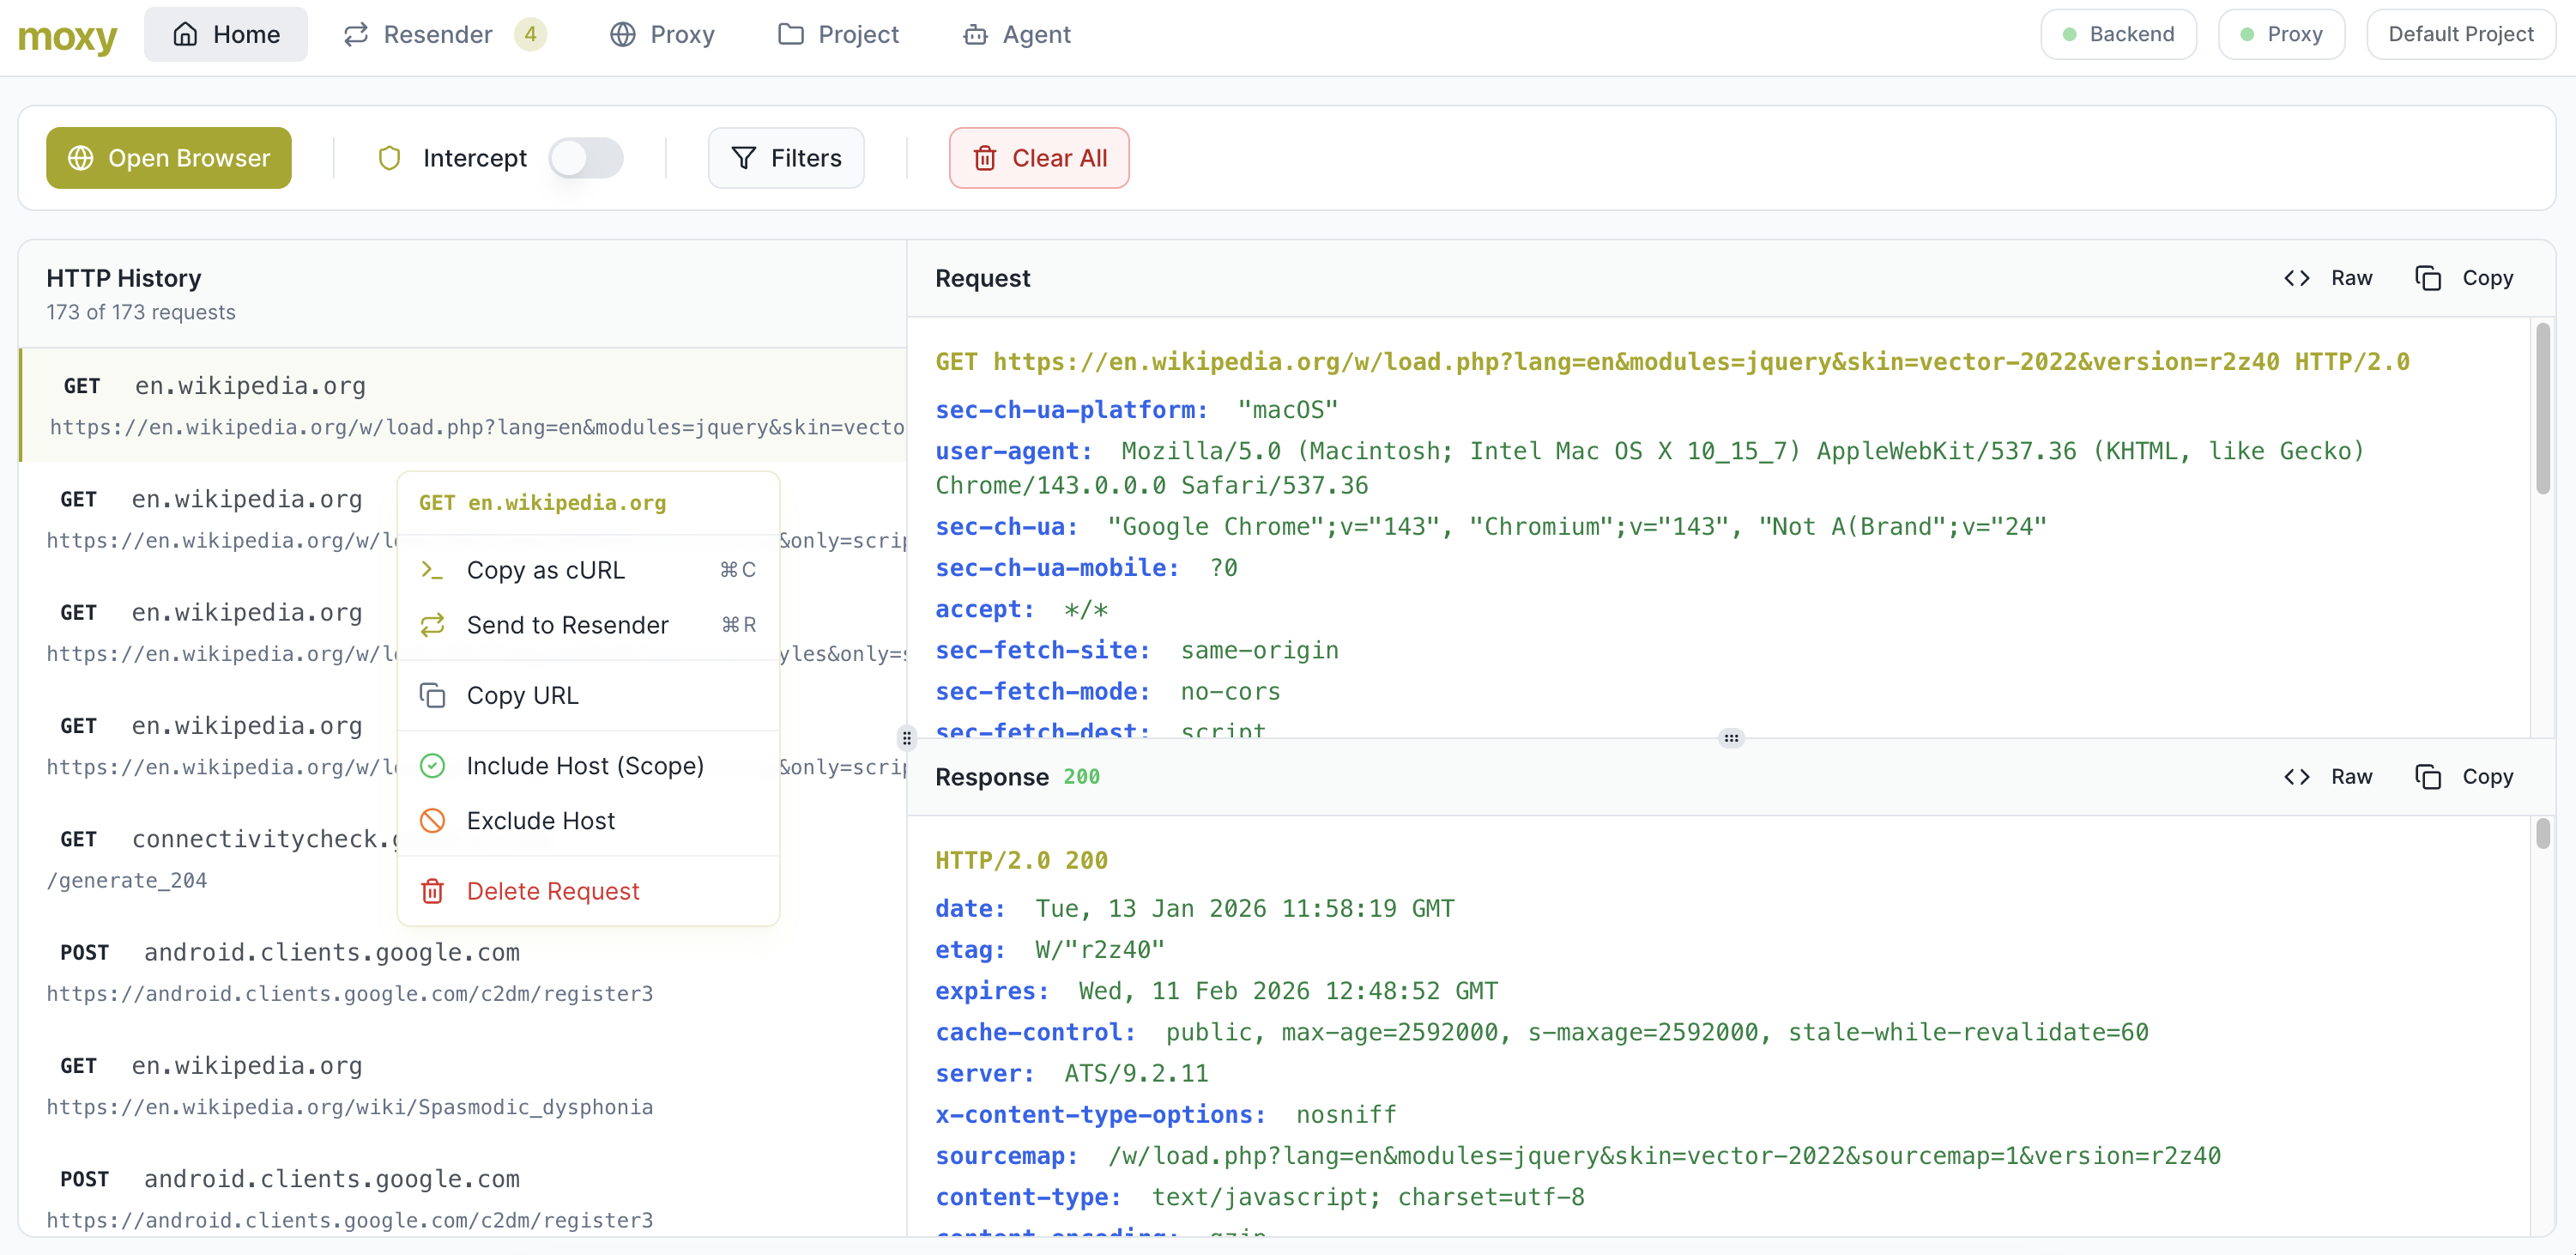
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…

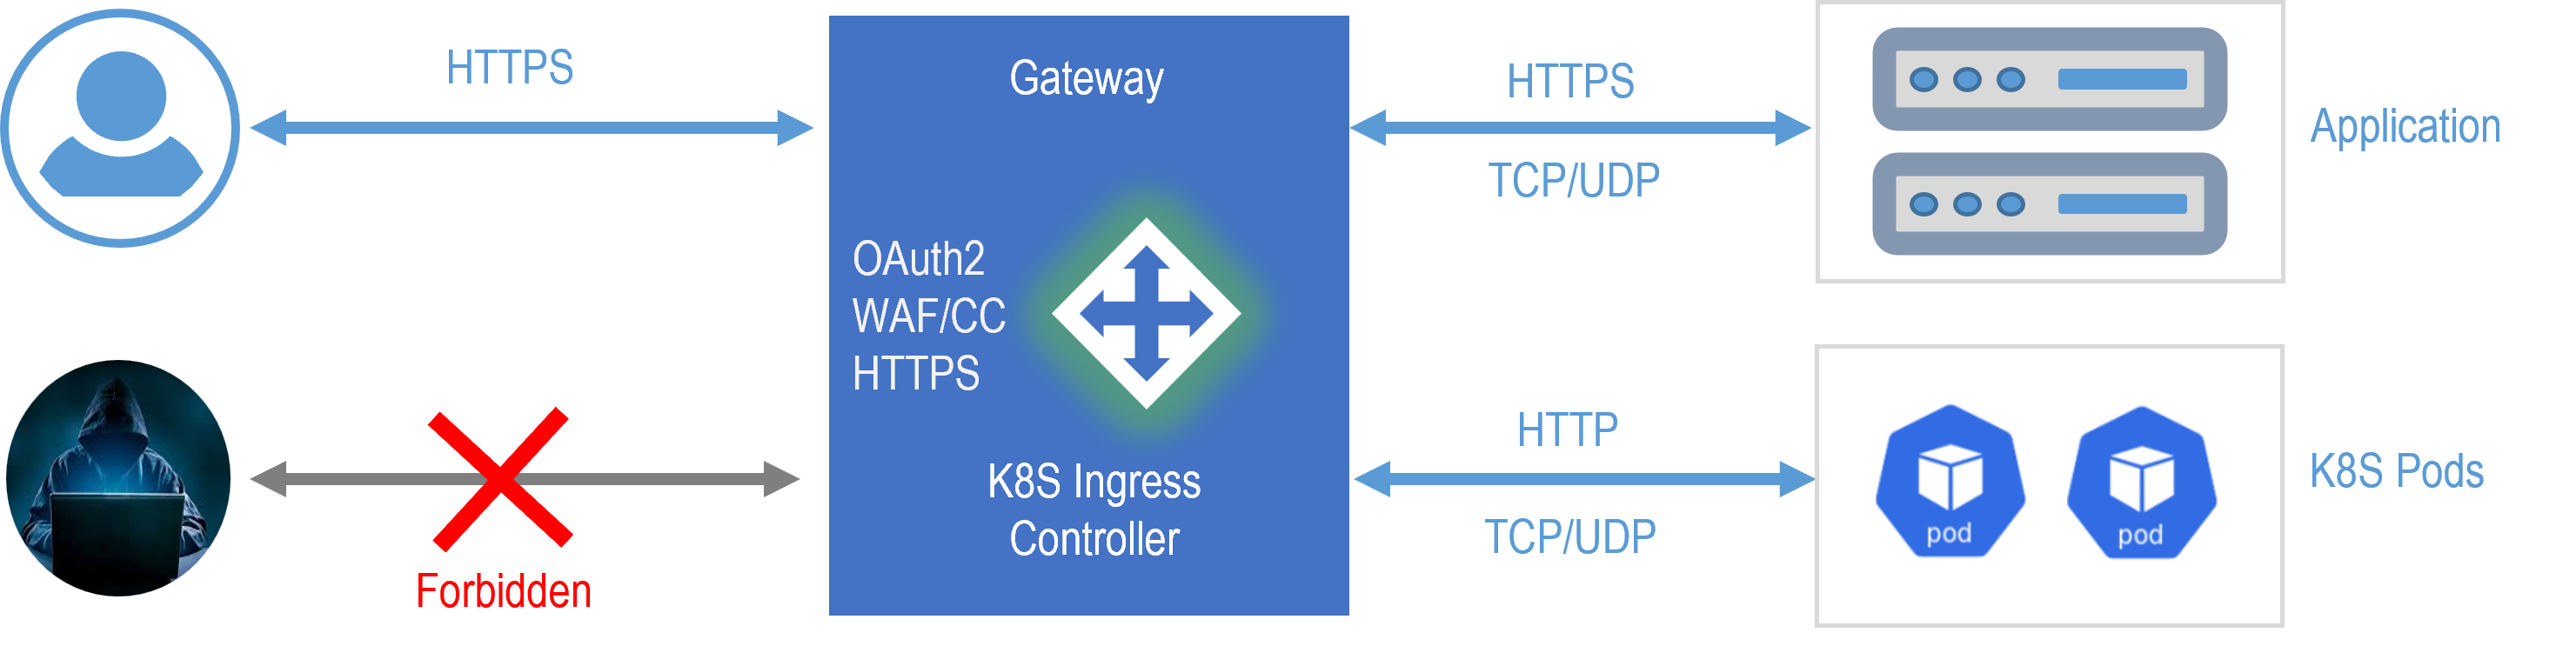
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.

Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)

CVE-2015-3224

Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…

Chrome extension and Shodan scanner for detecting and demonstrating RCE vulnerabilities in React Server Components (RSC) and Next.js applications,…

TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…