

JS-Tap
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
483
hoodoer/js-tapJavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 richflexpix/cpanel-pwn
cPanel/WHM CVE-2026-41940 CRLF injection auth bypass exploit
 epinna/weevely3
Weaponized web shell
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)
 iamnewbiez/cve-2021-44228
Deliberately vulnerable Apache Solr application (CVE-2021-44228) for practicing Log4Shell exploitation via User-Agent, POST, and admin endpoints.…
 sacx-7/cve-2025-50867
Proof-of-concept for a time-based blind SQL injection vulnerability in the takeassessment2.php endpoint of CloudClassroom-PHP-Project 1.0,…
 redteampentesting/cve-2020-13935
Exploit for WebSocket Vulnerability in Apache Tomcat
 aabbcc19191/cve-2020-13935
Exploit for Apache Tomcat WebSocket vulnerability CVE-2020-13935, allowing testing of WebSocket endpoints for denial-of-service vulnerability.
 esistferry/cve-2022-24992
Proof-of-concept for CVE-2022-24992, a path traversal vulnerability in QRCDR's QR-Code generator script, with technical write-up and exploitation…
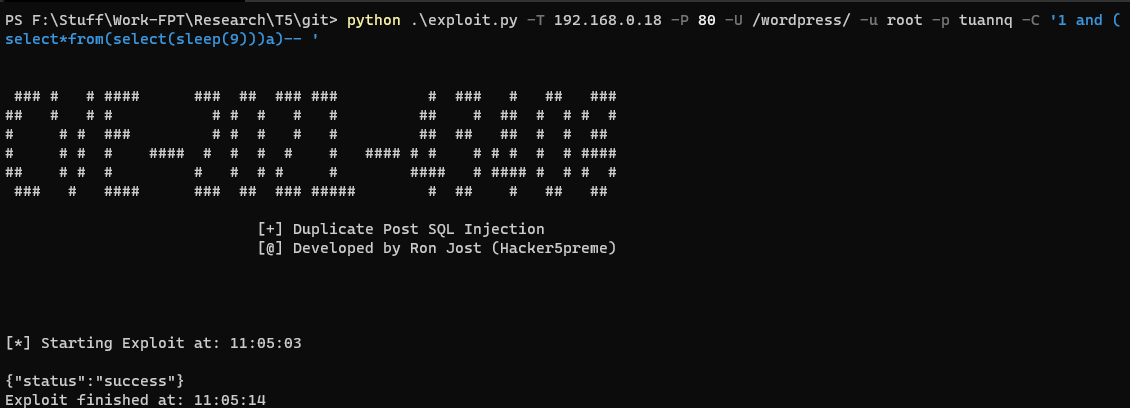 tuannq2299/cve-2021-43408
Technical analysis and proof-of-concept exploit for CVE-2021-43408, a SQL injection vulnerability in the WordPress Duplicate Post plugin version…
 lp008/cve-2020-13942
Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.
 jax7sec/cve-2017-9841
Batch scanner and exploitation script for CVE-2017-9841, a PHPUnit remote code execution vulnerability triggered via HTTP POST requests with PHP…
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 feartheploto/gitlab-cve-2023-7028
Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
 kswzzl/cve-2016-3861
my extended take on Mark Brand's CVE 2016-3861 libutils bug
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…