
phpggc
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
exploitationexploit-frameworkspayload-generation+1
3.9k
ambionics/phpggcPHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
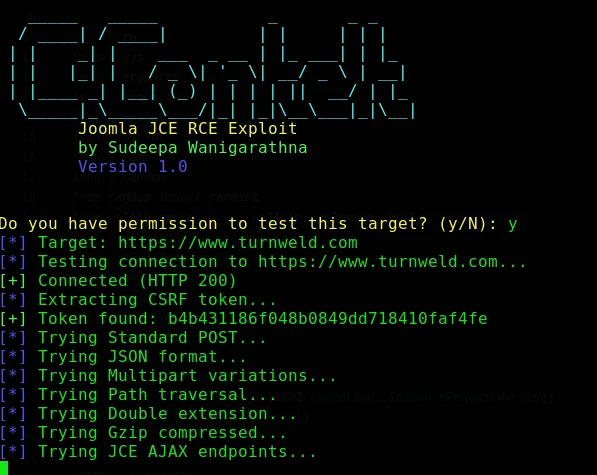 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 assetnote/react2shell-scanner
High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 malayke/next.js-rsc-rce-scanner-cve-2025-66478
A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.

 kingsabri/godofwar
GodOfWar - Malicious Java WAR builder with built-in payloads
 anonkryptiquz/nextsploit
NextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
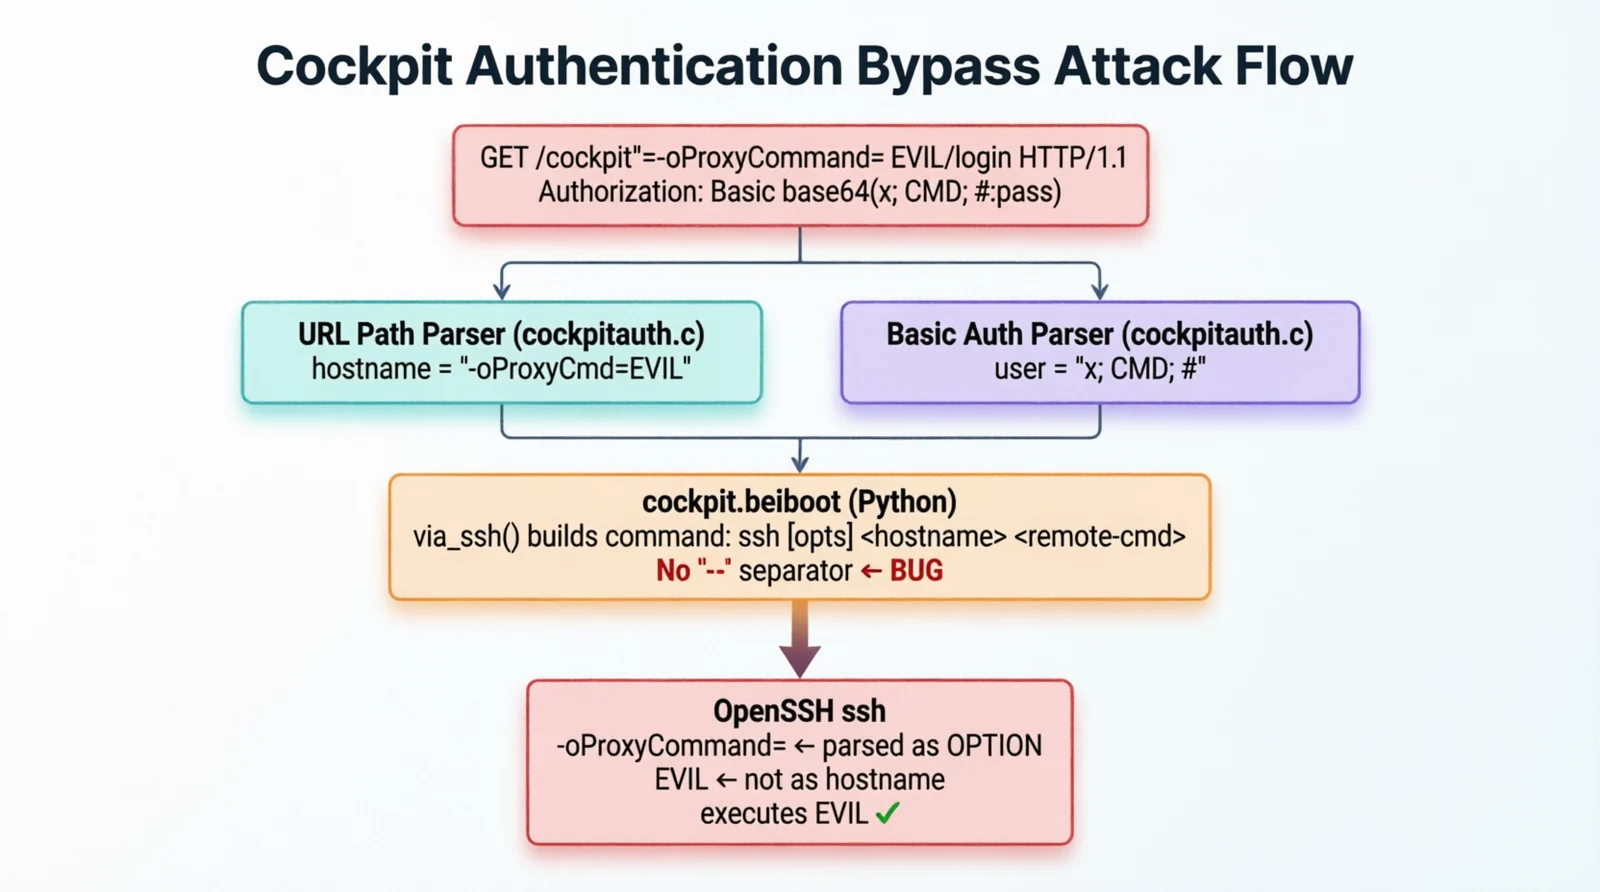 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 pysectools/cve-2026-3629
WordPress Privilege Escalation Checker
 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc
 0xl0k1/cve-2012-1823
PHP CGI Argument Injection.
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 iqzer0/vulnknox
A Go-based wrapper for the KNOXSS API to automate XSS vulnerability testing.
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…