
proxylogscan
 dwisiswant0/proxylogscan
A fast tool to mass scan for a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as…
exploitationinformation-gatheringpenetration-testing+3
166
dwisiswant0/proxylogscanA fast tool to mass scan for a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 haotiku/cve-2021-26855-exploit-exchange
Automated scanner and exploit tool for CVE-2021-26855 targeting Microsoft Exchange servers, enabling remote code execution on vulnerable instances…
 soltanali0/cve-2022-41082
CVE-2022-41082-poc
 exfil0/cve-2025-53770
A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 synacktiv/cve-2024-43468
Exploit for CVE-2024-43468: unauthenticated SQL injection in Microsoft Configuration Manager Management Points, enabling arbitrary SQL execution and…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 alt3kx/cve-2021-26855_poc
Proof-of-concept exploit for CVE-2021-26855, demonstrating SSRF in Microsoft Exchange Server to access backend services and extract user information.
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
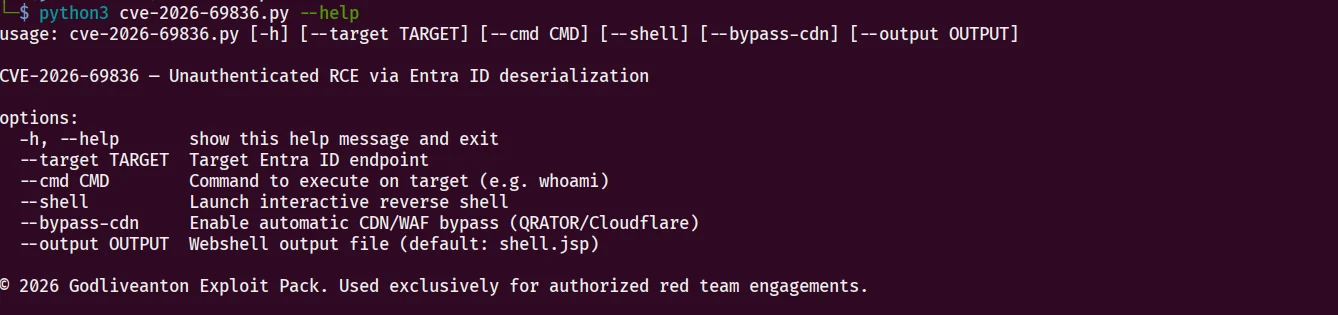 sentinel-aidefense/cve-2026-69836-exp
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization
 homjxi0e/cve-2017-8641_chakra_js_globalobject
There is a classic heap overflow when eval a string which large enough in Chakra! This issue can be reproduced steadly in uptodate Edge in Win10 WIP.…
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 shytangerine/cve-2021-26855
Proof-of-concept exploit for CVE-2021-26855 (Microsoft Exchange Server SSRF) demonstrating SSRF to RCE chain with crafted HTTP requests to /ecp/x.png.
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
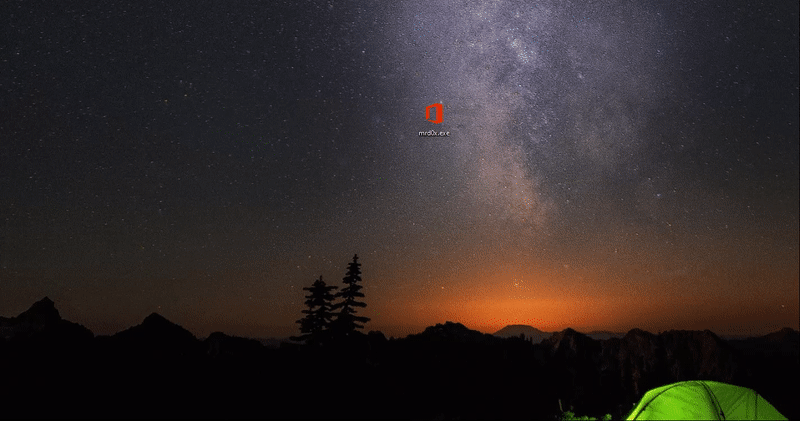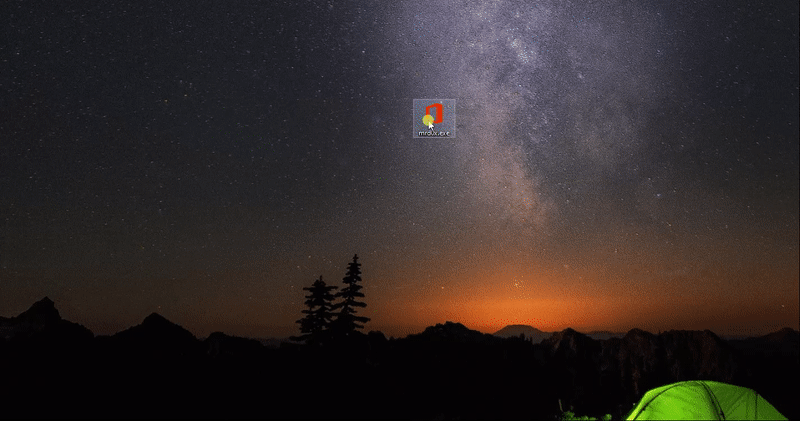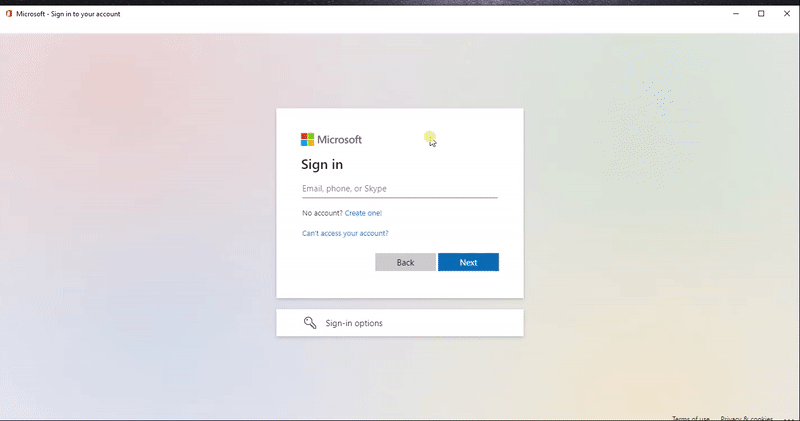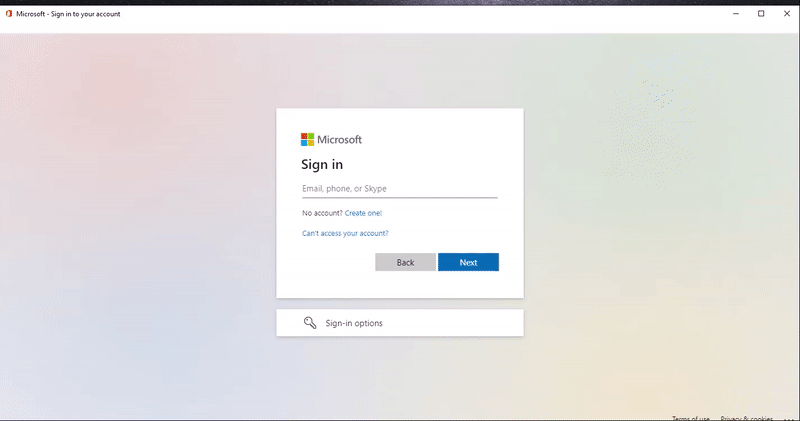 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
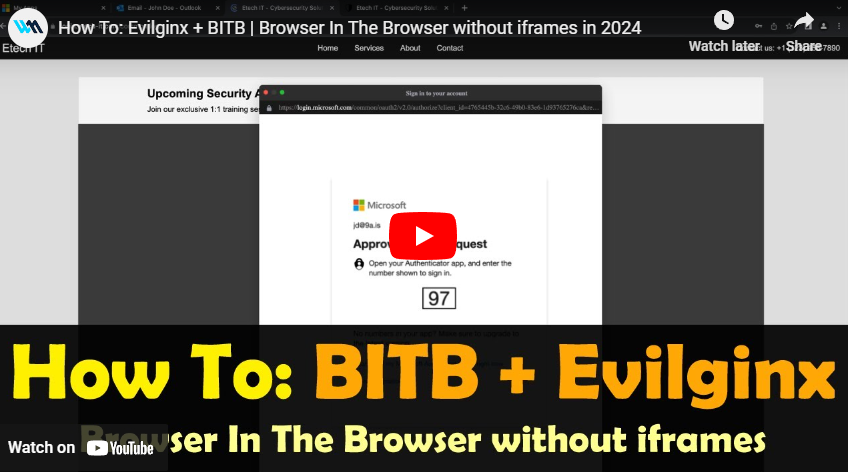 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
 evilashz/exchangessrftorceexploit
Exploit chain for CVE-2021-26855 (SSRF) and CVE-2021-27065 (RCE) targeting Microsoft Exchange servers, enabling remote code execution via ProxyLogon…