
PhEmail
 dionach/phemail
PhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test
email-harvestinginformation-gatheringosint+4
349
dionach/phemailPhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test
 h4k6/cve-2023-2982-poc
WordPress社交登录和注册(Discord,Google,Twitter,LinkedIn)<=7.6.4-绕过身份验证
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 mr-xn/cve-2021-26855-d
Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…
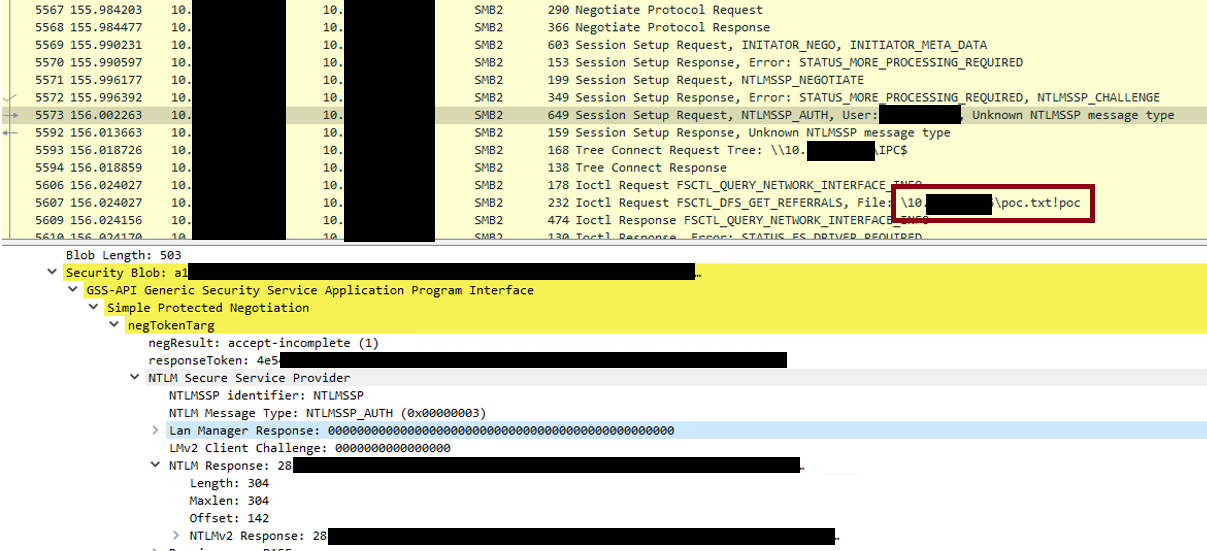 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
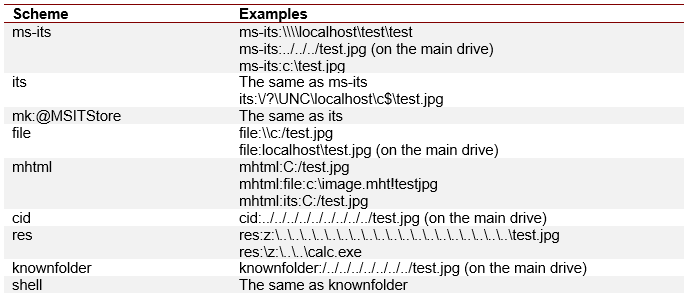 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 0xdims/cve-2019-16759
This tools will extracts and dumps Email + SMTP from vBulletin database server
 romain-deperne/cve-2026-33715
Proof-of-concept exploit for unauthenticated SSRF and open email relay in Chamilo LMS via install.ajax.php, allowing internal network probing and…
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 rootxsushant/cve-2023-5561-poc-updated
Updated POC for Unauth Post Author Email Disclosures WordPress CVE-2023-5561
 kernel364/cve-2024-2876
Proof-of-concept exploit for a critical SQL injection vulnerability in WordPress Email Subscribers plugin. Includes exploitation details, HTTP…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 networksecure/cve-2020-14065
Exploit for CVE-2020-14065: unlimited file upload vulnerability in Icewarp Email Server 12.3.0.1, enabling remote code execution via crafted upload…
 dthkhang/cve-2023-5561-poc
PoC exploit for CVE-2023-5561 that enumerates WordPress user email addresses via the /wp-json/wp/v2/users API endpoint. For authorized security…