
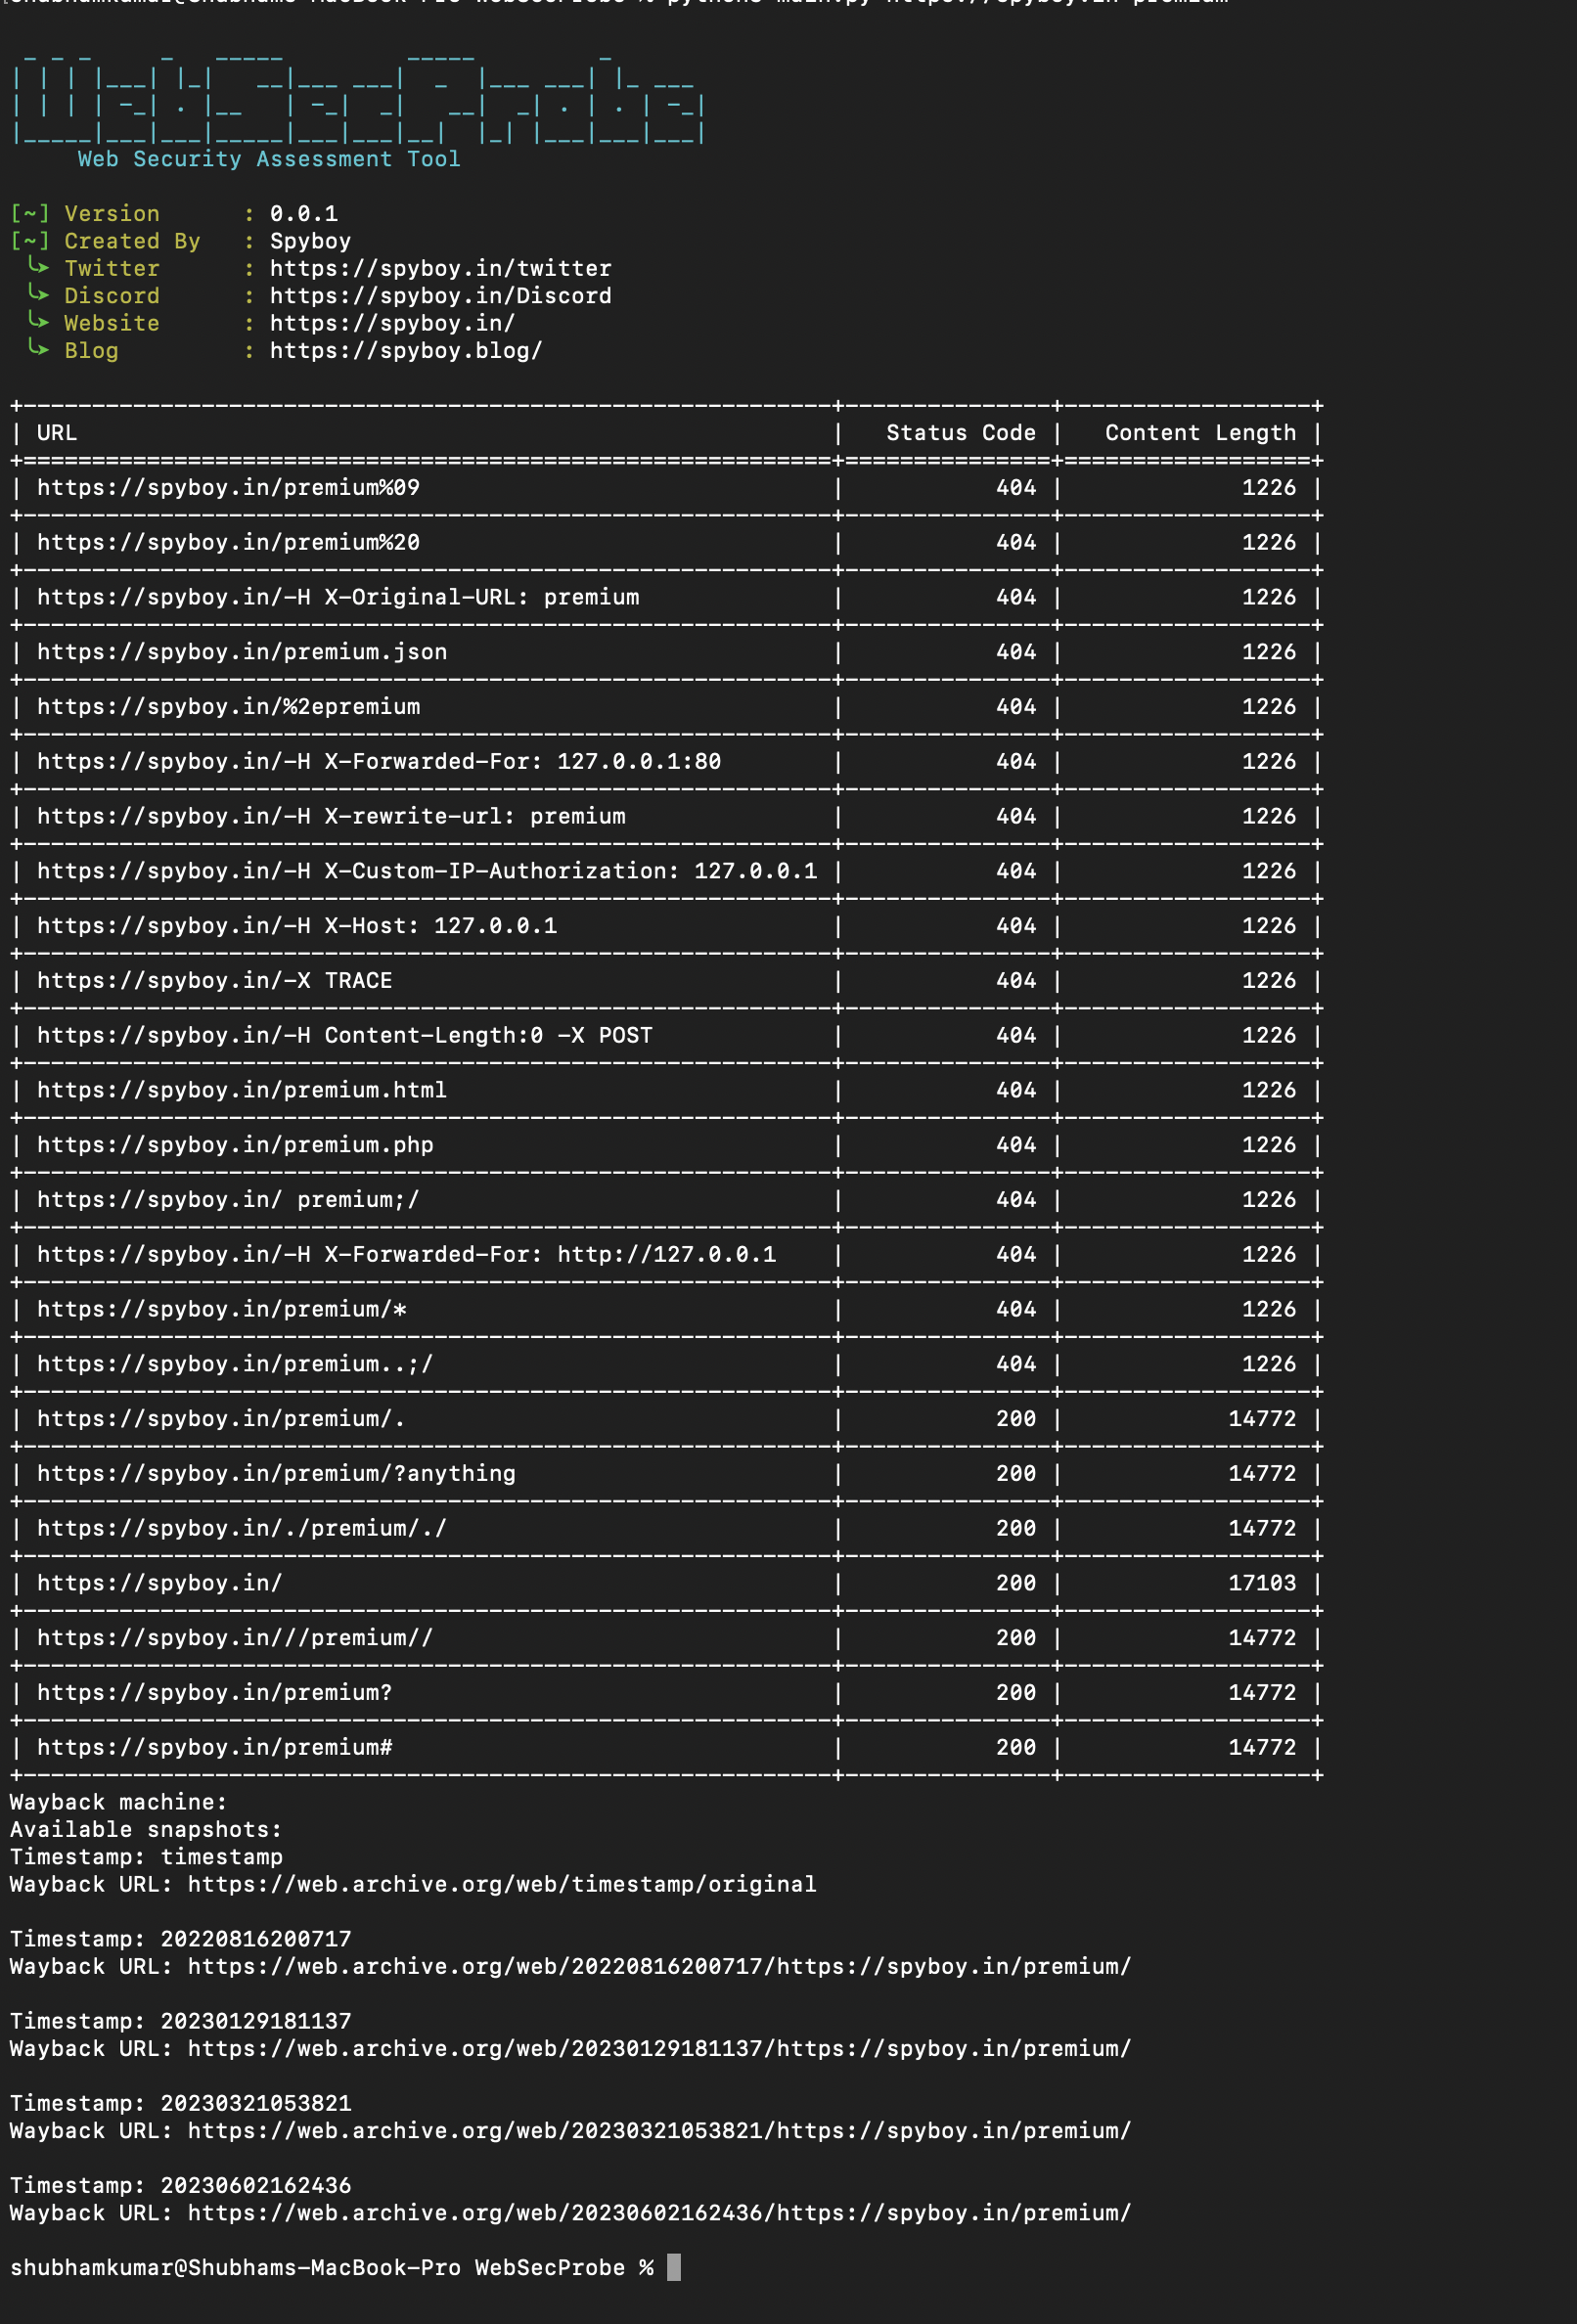
WebSecProbe
 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
misconfigurationpenetration-testingvulnerability-scanners+2
185
spyboy-productions/websecprobeSecurity testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 abdulahadthecyber-pixel/aidor
Bash-based automated IDOR vulnerability scanner that detects insecure direct object references by enumerating numerical parameters and analyzing HTTP…
 d4vinci/pyflooder
A http flood python script that could stop a normal website in 10s
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 ternopil-te-te-t4p/cryptoquant-key-gen
Patcher utility that bypasses CryptoQuant premium tier restrictions to unlock advanced analytics and real-time data access, with a Python GUI for…
 coalfire-research/doozer
Password cracking utility
 ikkisoft/parrotng
Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.
 jpiechowka/zip-shotgun
Utility script to test zip file upload functionality (and possible extraction of zip files) for vulnerabilities (aka Zip Slip)
 u238/grafana-cve-2018-15727
a small utility to generate a cookie in order to exploit a grafana vulnerability (CVE-2018-15727)
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 gabrielolivra/exploit-medium-cve-2021-41184
Proof-of-concept exploit for CVE-2021-41184, a cross-site scripting (XSS) vulnerability in jQuery UI's .position() utility, targeting version 1.12.1.
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 bcdannyboy/cve-2023-50164
A scanning utility and PoC for CVE-2023-50164
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 kc57/jitbit_helpdesk_auth_bypass
Utility to derive the shared secret on a JitBit Helpdesk install which can be used for authentication bypass (CVE-2017-18486)
 lwzsoviet/cve-2021-3281
Proof-of-concept for CVE-2021-3281: directory traversal vulnerability in Django's TarArchive utility via crafted tar files, with Python tarfile…
 anilkashyap01/binary-exploitation-and-kernel-escalation
Secured root-level access by identifying and exploiting misconfigurations and outdated software. Buffer overflow vulnerability in an outdated version…